
 Uniswap

 Android
 iOS
dApp Permissions
- User confirmation before processing requests8.7 / 8.7Description
Requires user confirmation before processing requests from dApps for specific RPC methods.
-
The wallet requires user confirmation for all supported privileged endpoints (eth_signTypedData, personal_sign, eth_sendTransaction) and returns an unsupported-method error for the other tested endpoints, ensuring no request was executed without confirmation.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot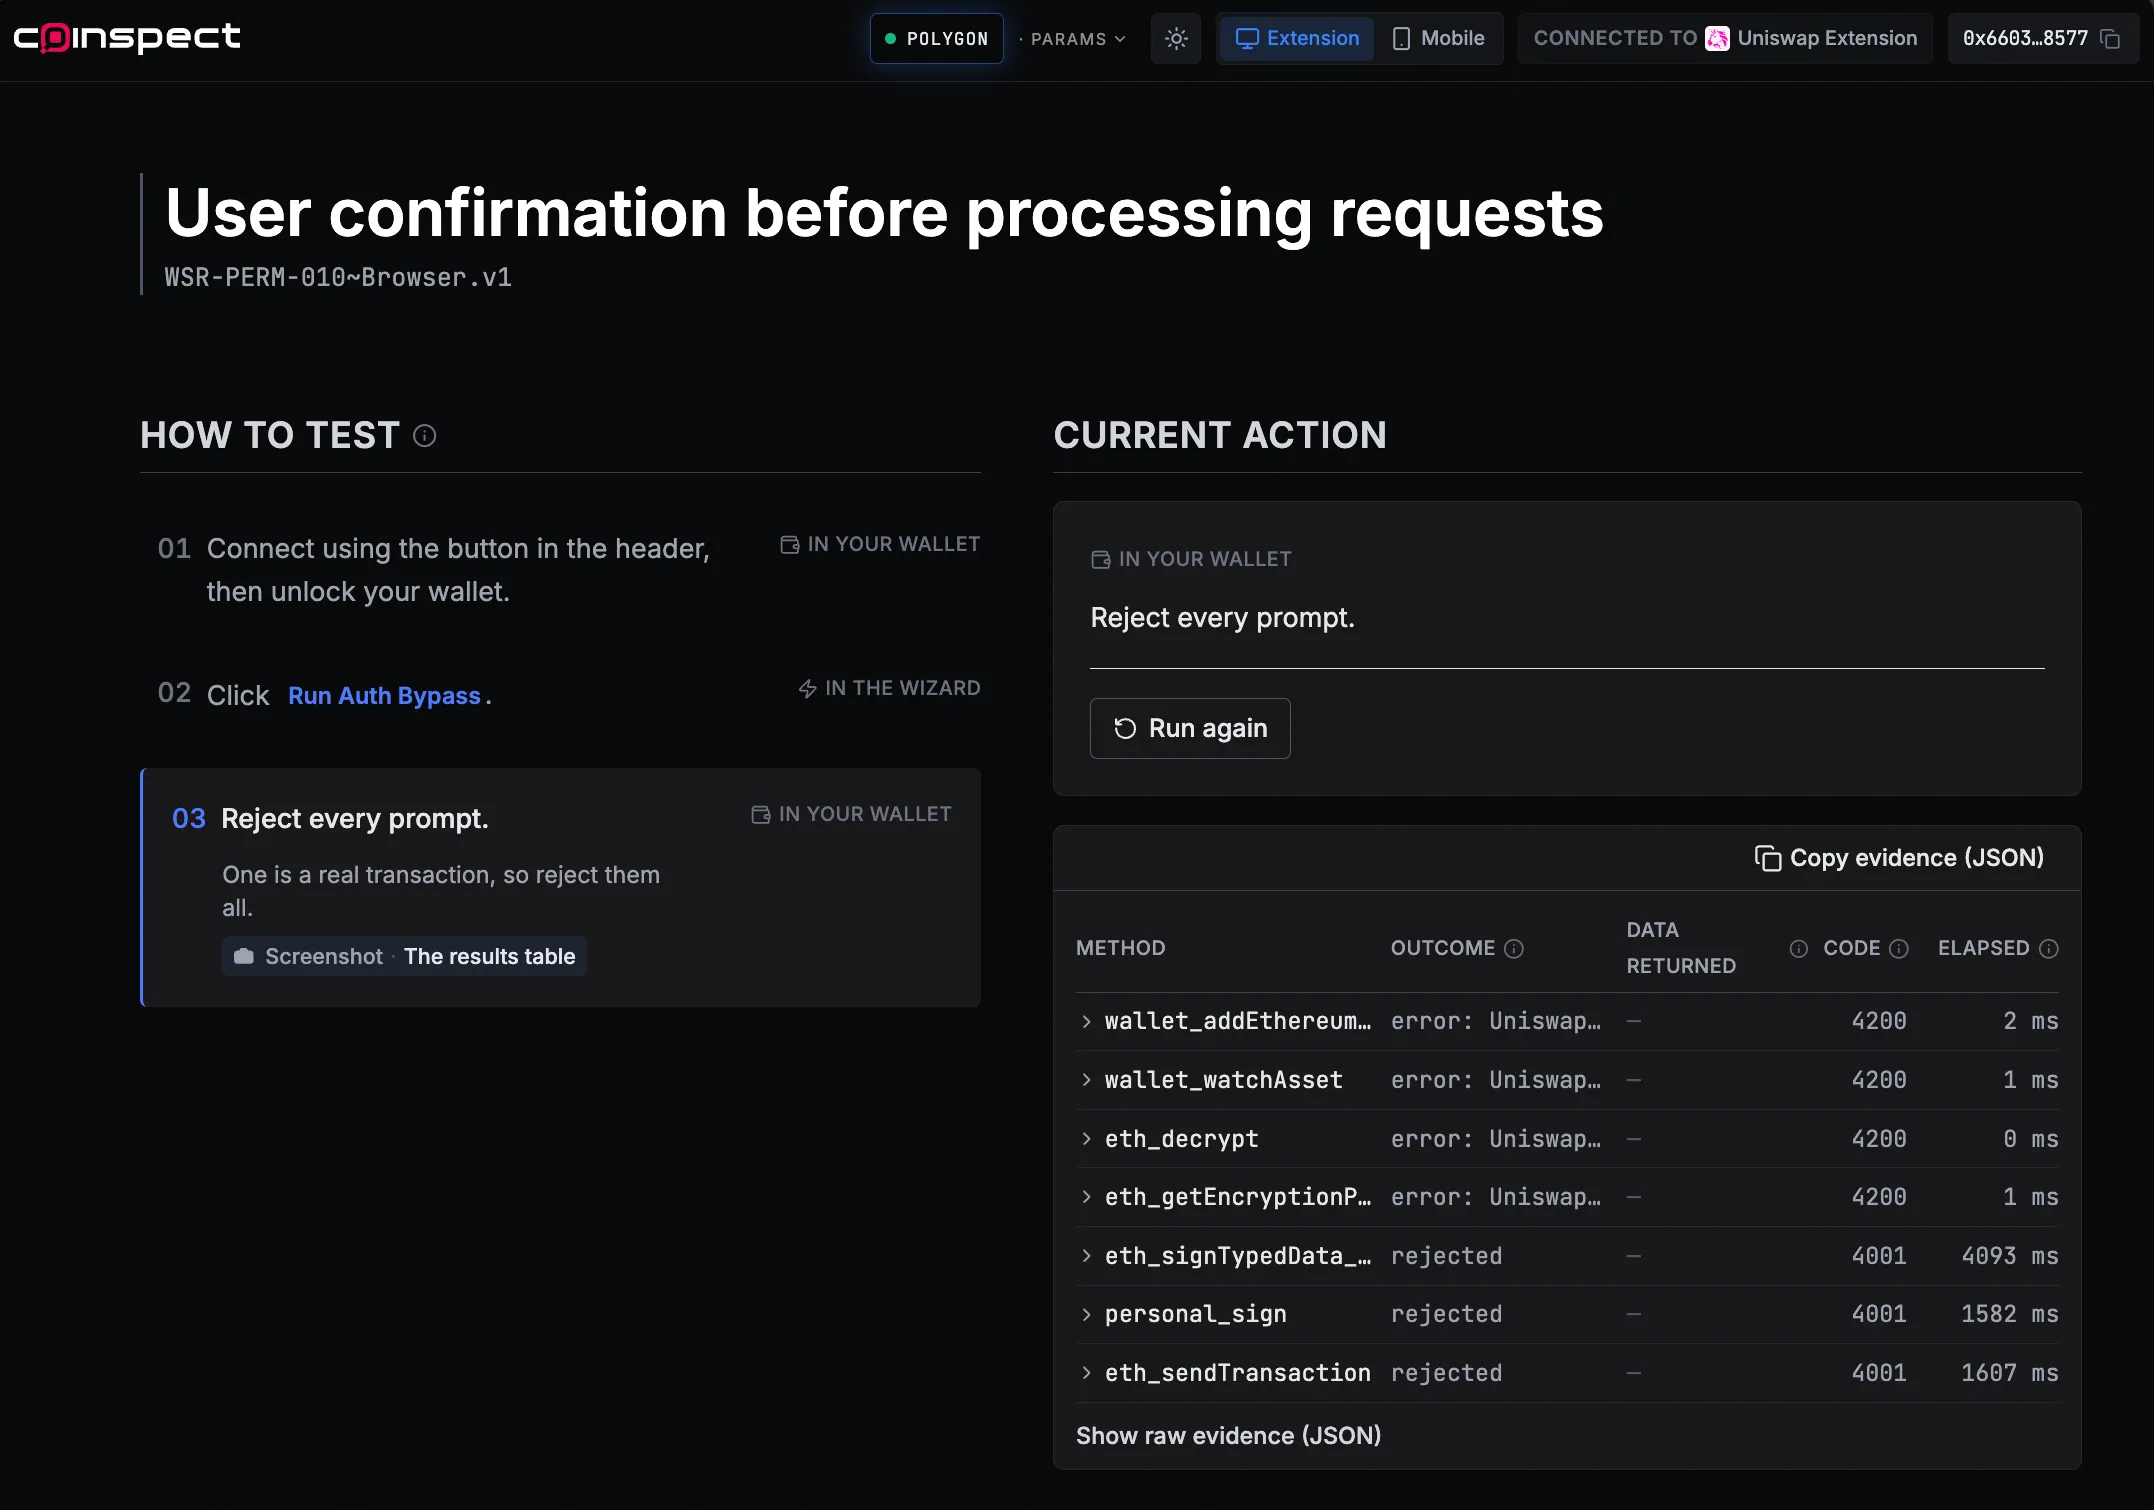 Last updated on Sep 3, 2026Report an issue with this check
-
- User consent for dApp access7.7 / 7.7Description
Requires user approval before granting dApp access to specific RPC methods.
-
The wallet rejected every privileged RPC method (eth_accounts, eth_decrypt, eth_getEncryptionPublicKey, eth_signTypedData, personal_sign, eth_sendTransaction) with an error and returned no data, confirming that dApp access requires explicit user approval.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot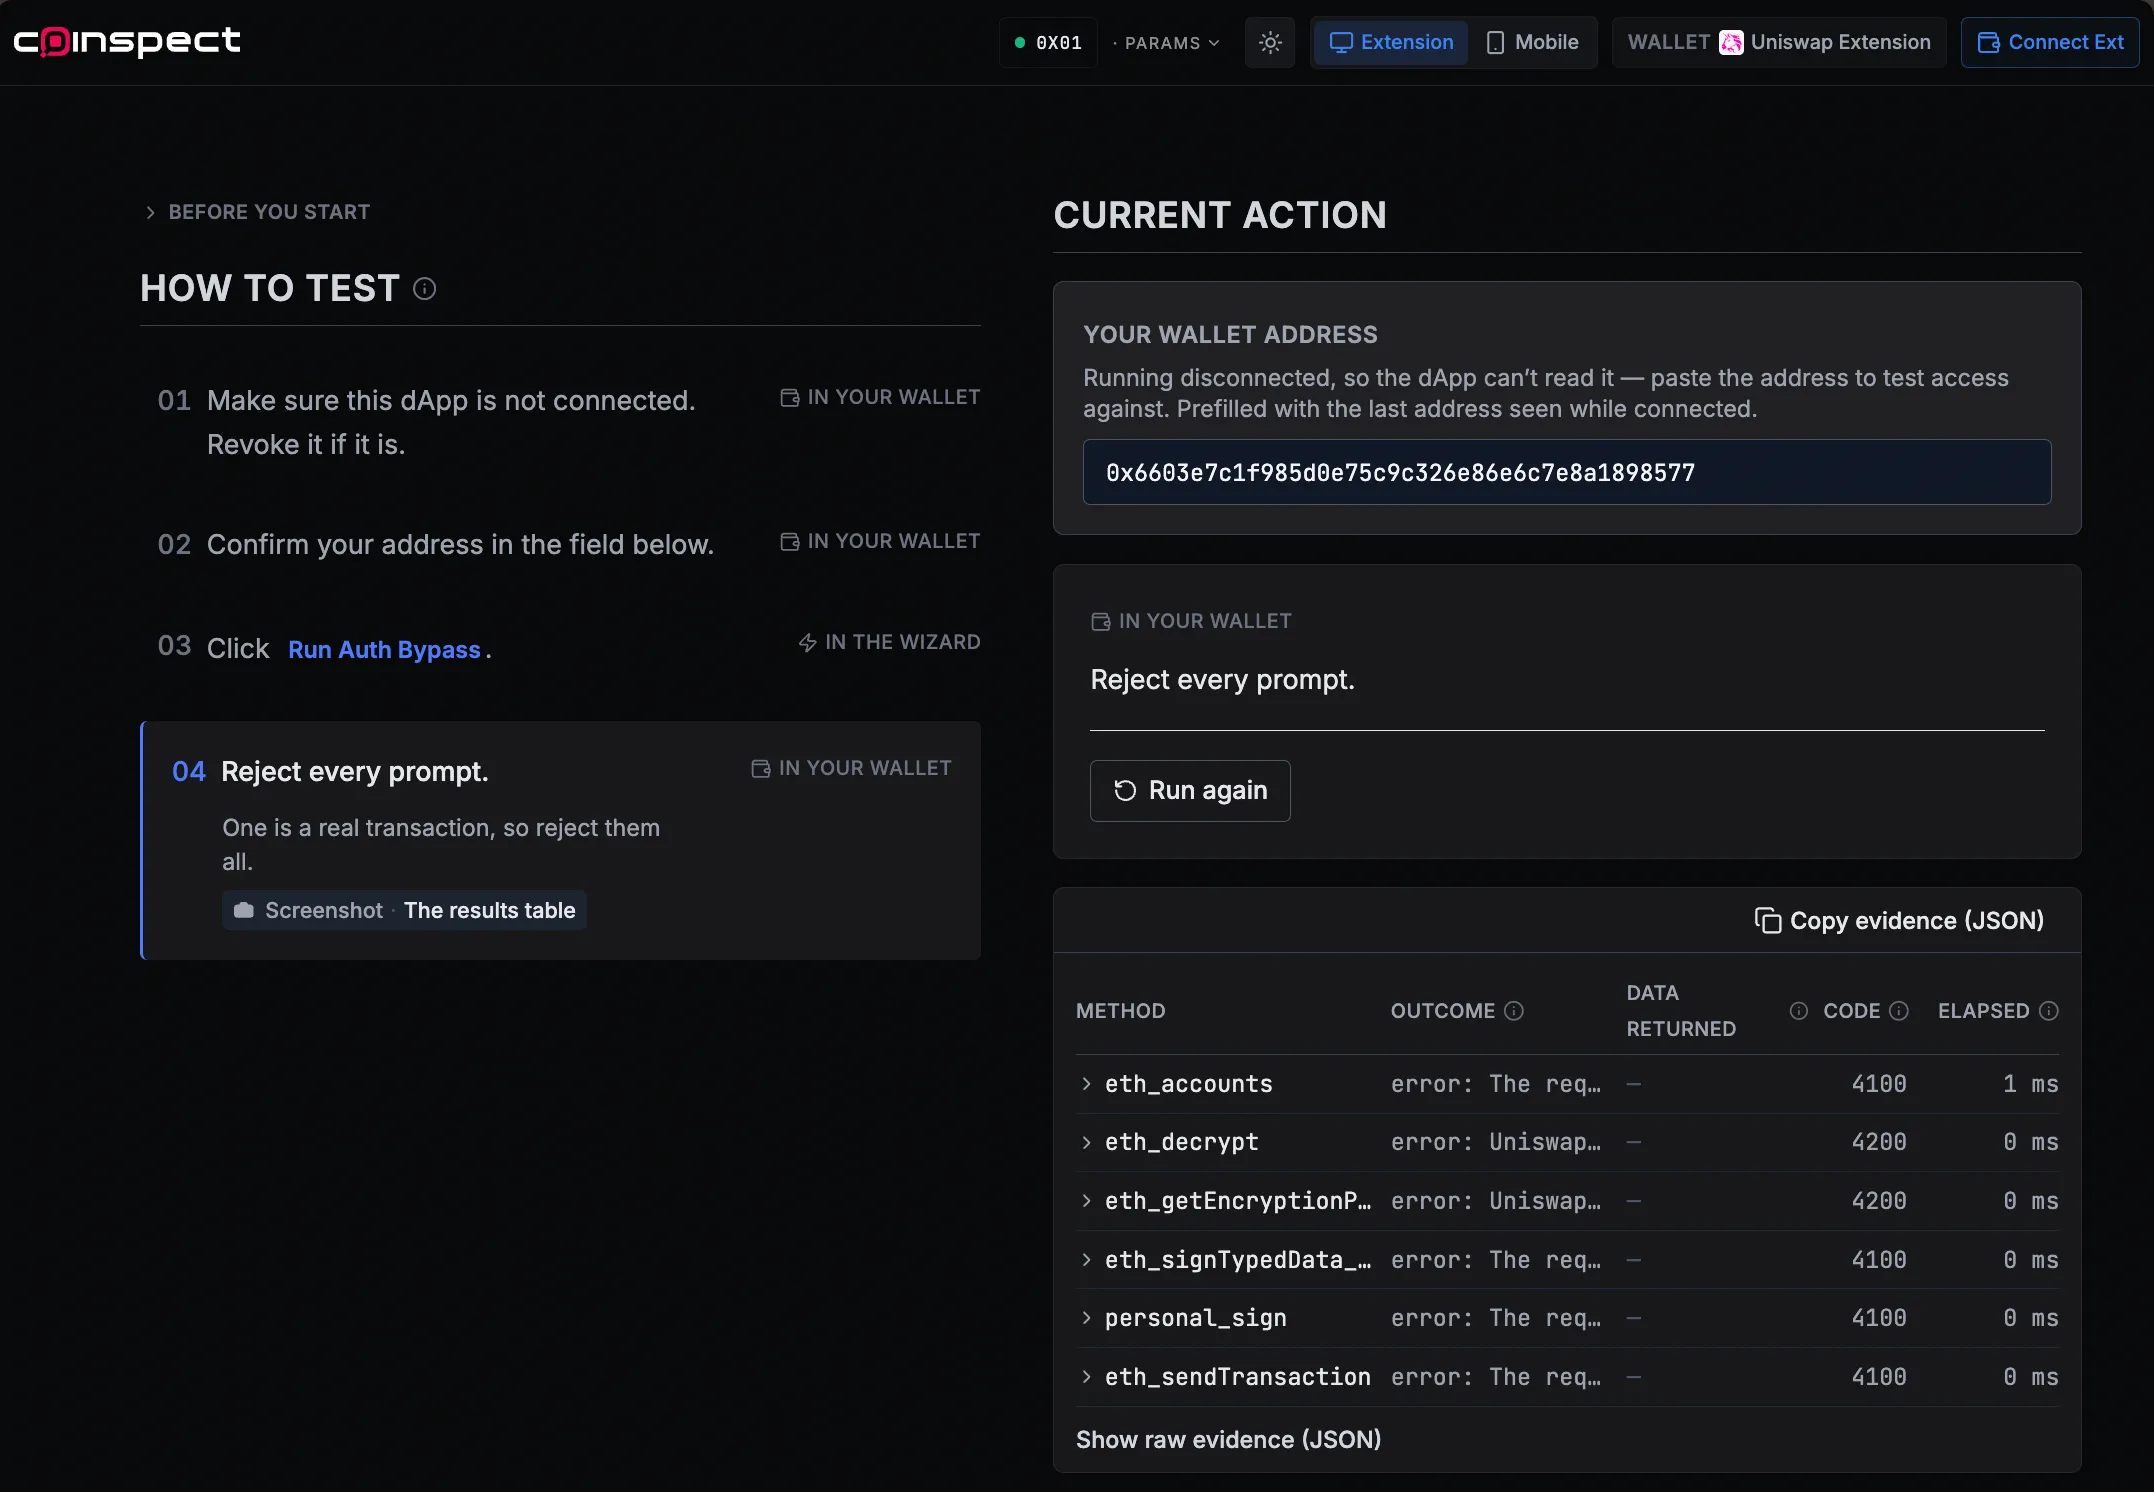 Last updated on Sep 3, 2026Report an issue with this check
-
- Wallet unlock before requests5.6 / 5.6Description
Requires users to unlock it before processing dApp requests when in a locked state.
-
The wallet requires the user to unlock before processing any dApp request; all tested methods (wallet_addEthereumChain, wallet_watchAsset, eth_decrypt, eth_getEncryptionPublicKey, eth_signTypedData, personal_sign, eth_sendTransaction) were rejected or received no response while locked, with no data returned.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot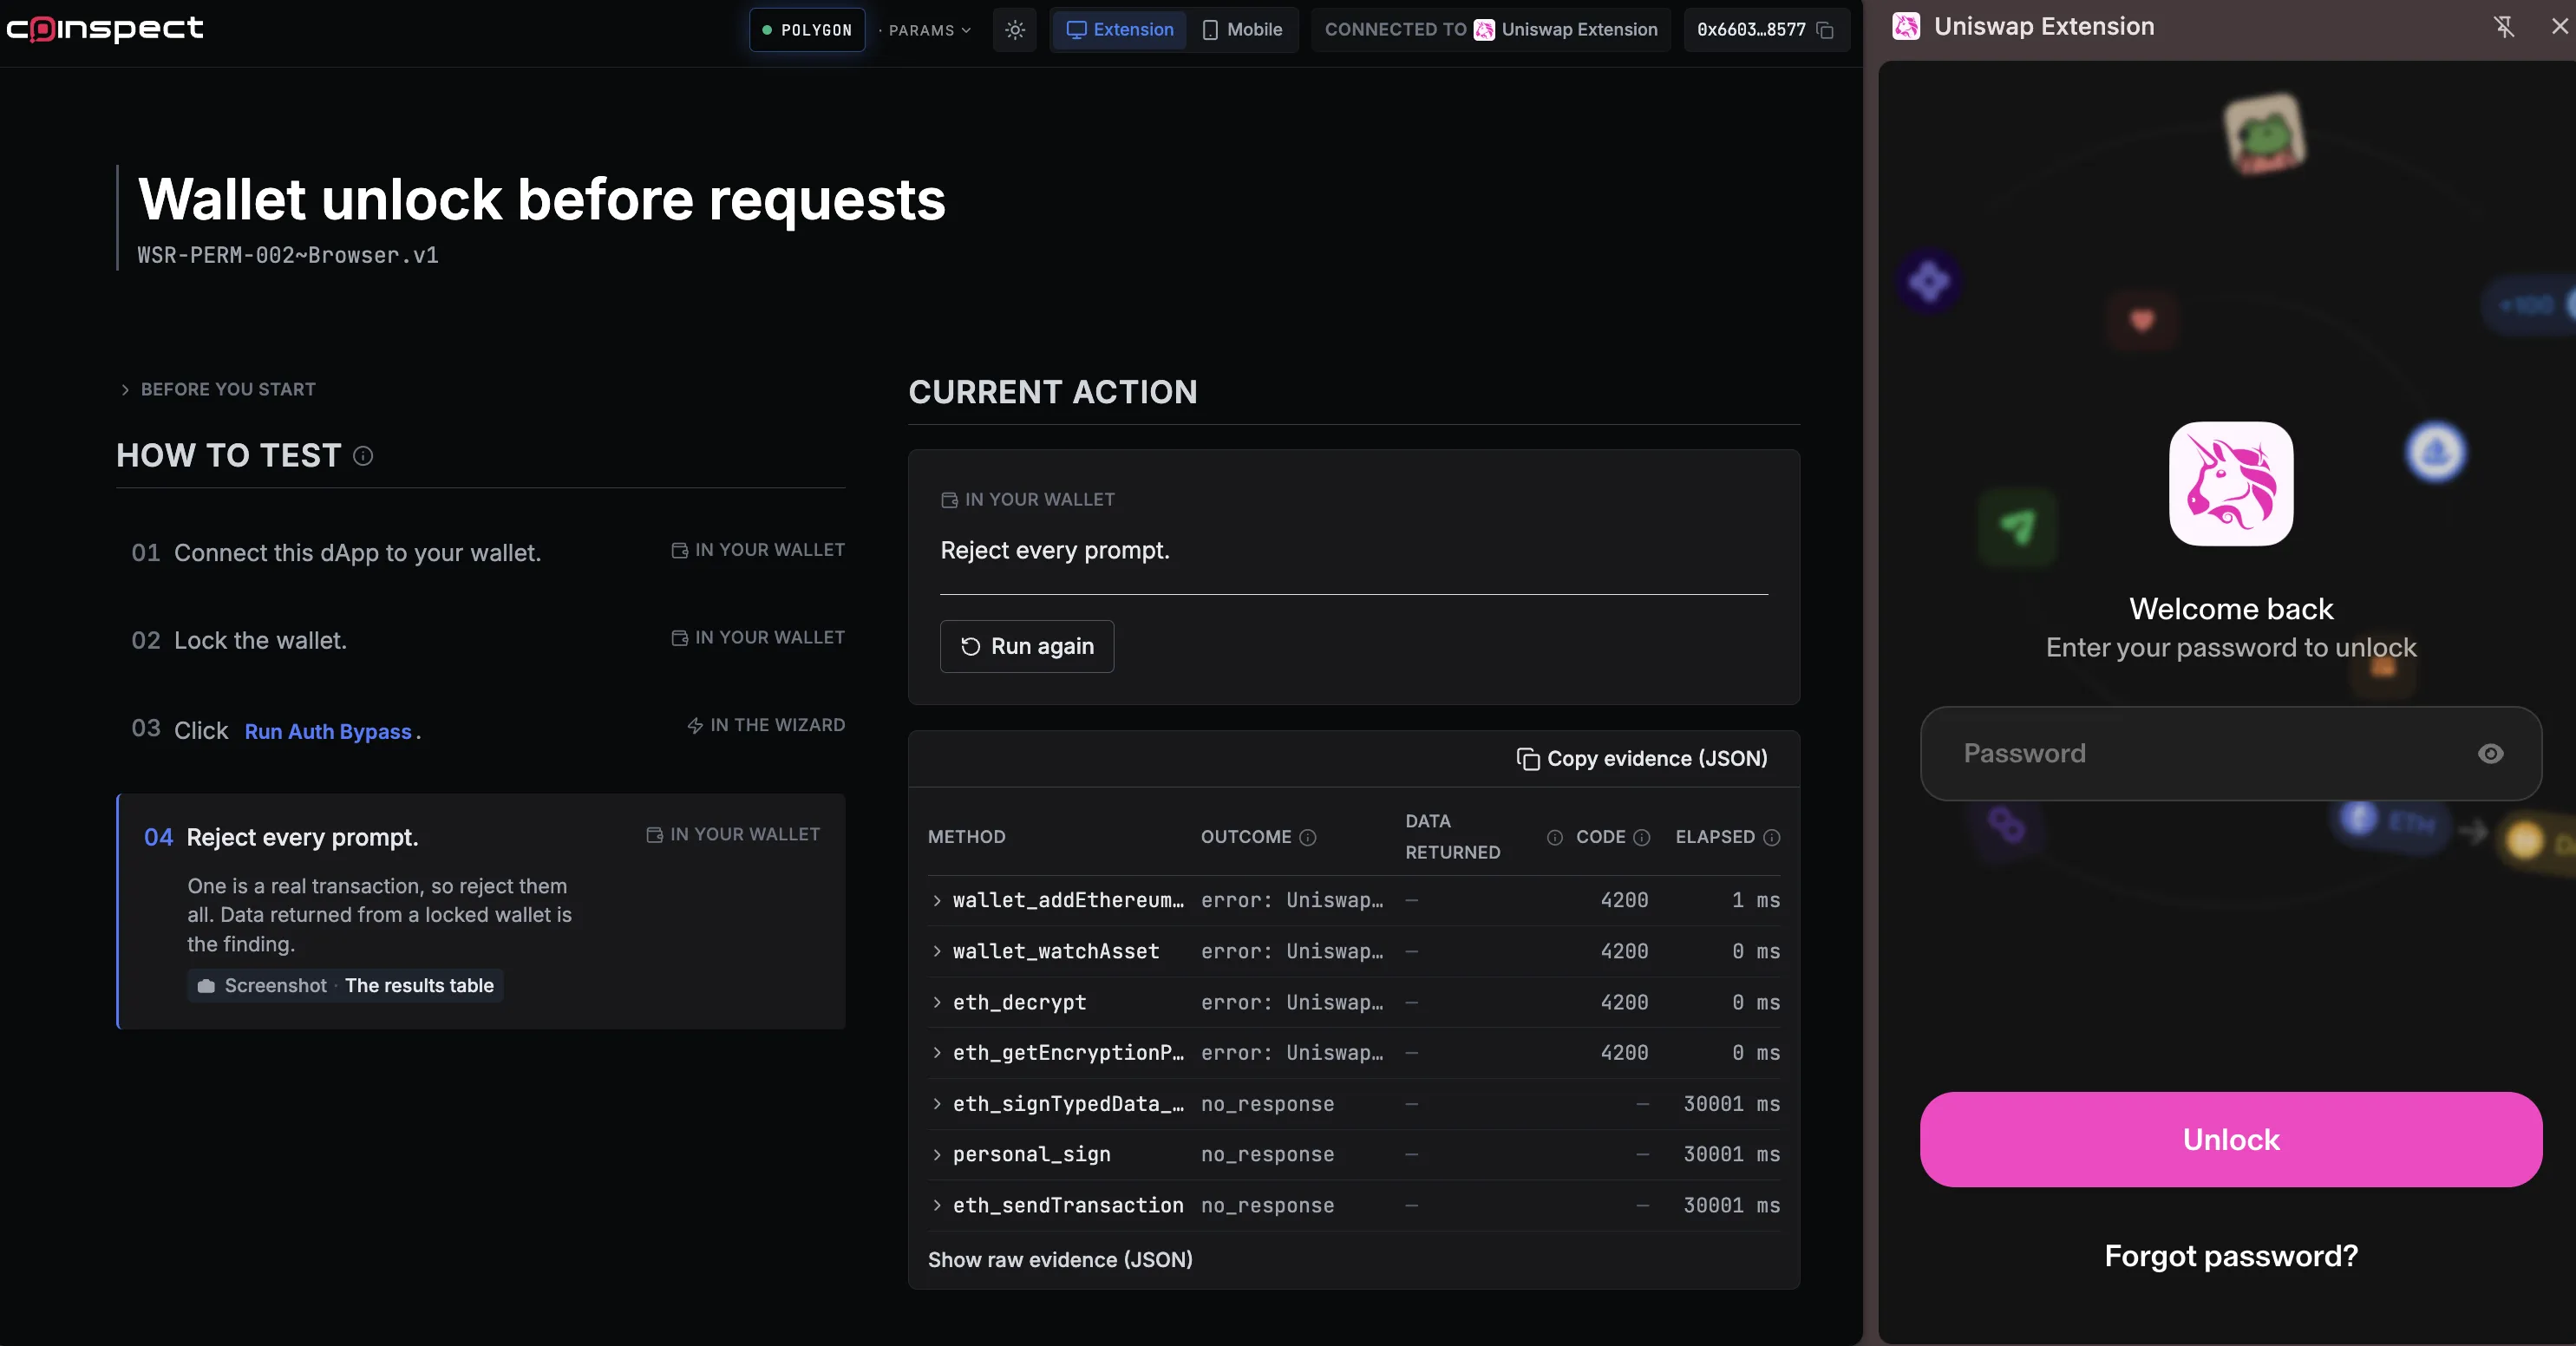 Last updated on Sep 3, 2026Report an issue with this check
-
- Mismatching EIP-712 chainId detection3.5 / 3.5Description
Alerts users or rejects signing EIP-712 messages with a mismatched chain ID.
-
The wallet displays an error message "Chain ID on message does not match the chain ID set on the extension", when attempting to sign an EIP-712 object with a chainId different from the wallet's active network.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot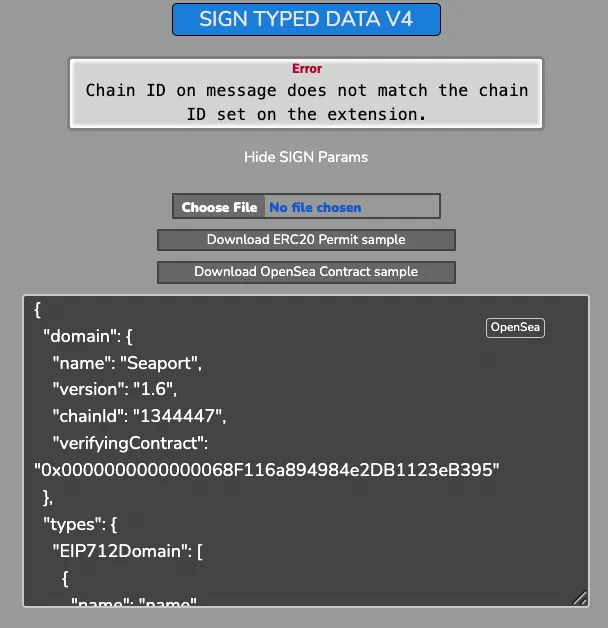 Last updated on Sep 3, 2026Report an issue with this check
-
- eth_sign method disabled3.3 / 3.3Description
Restricts the use of the deprecated and insecure eth_sign method by default.
-
The wallet rejects `eth_sign` requests as expected, returning an error message that it does not support `eth_sign` because it is deprecated.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot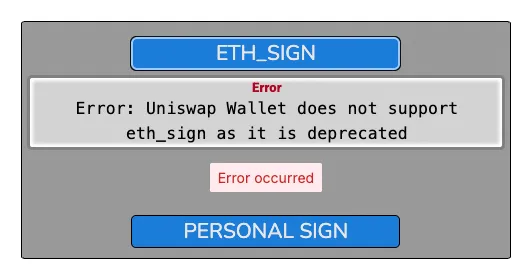 Last updated on Sep 3, 2026Report an issue with this check
-
- Mismatching SIWE domain detection0.0 / 1.9Description
Warns users when the domain in a Sign-In with Ethereum (EIP-4361) message does not match the requesting dApp's origin.
-
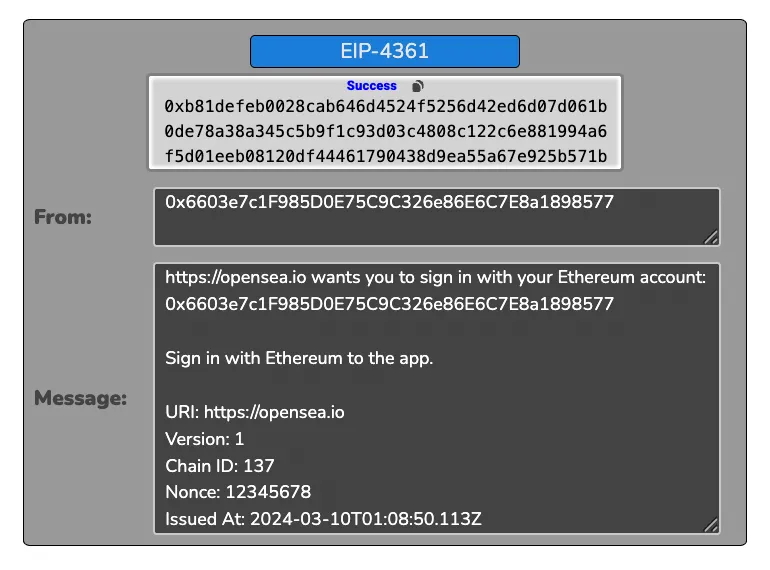
The wallet does not display a warning or block the signing request when the dApp origin differs from the domain specified in the SIWE object.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots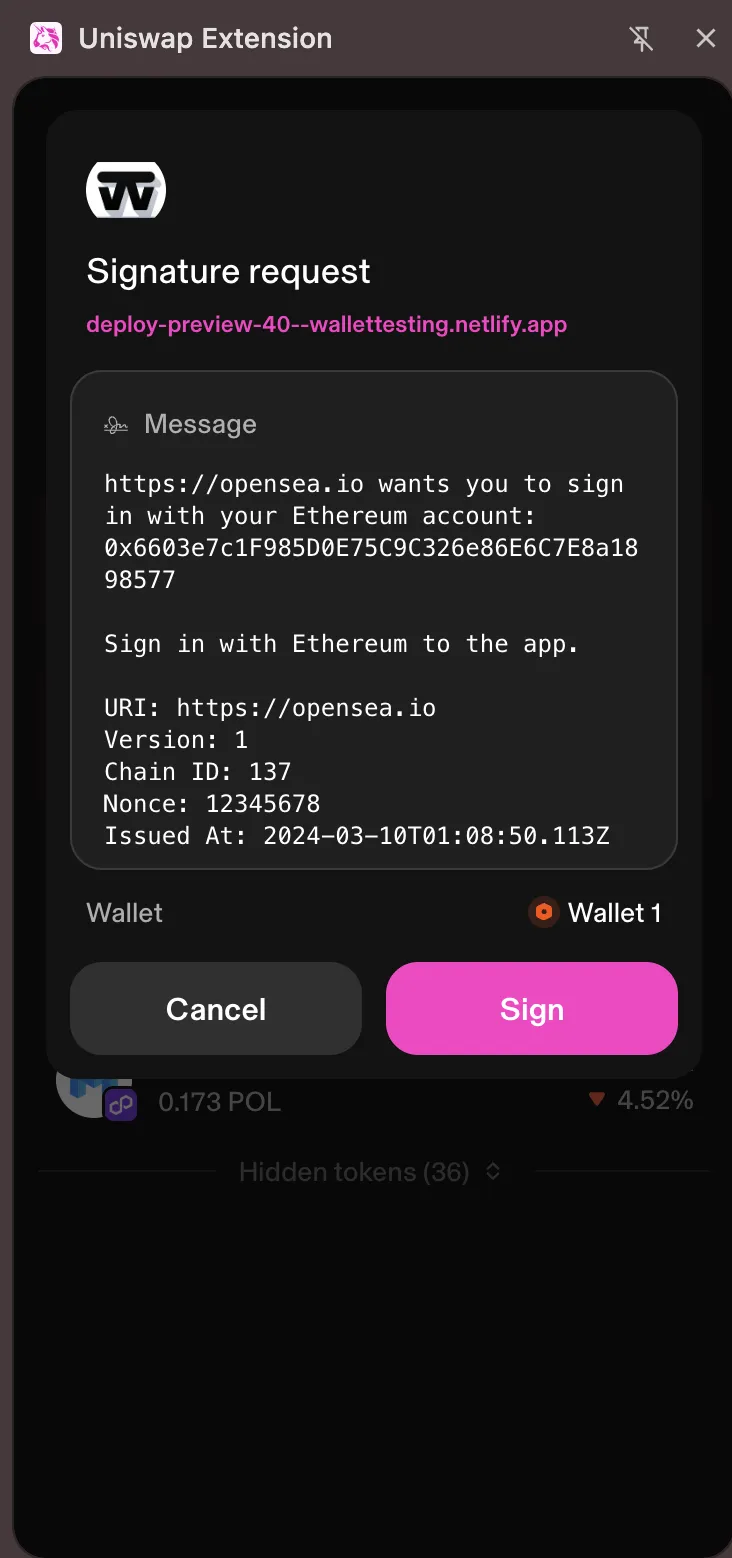
 Last updated on Sep 3, 2026Report an issue with this check
-
- Token approval management0.0 / 1.6Description
Allows users to view and revoke token approvals.
-
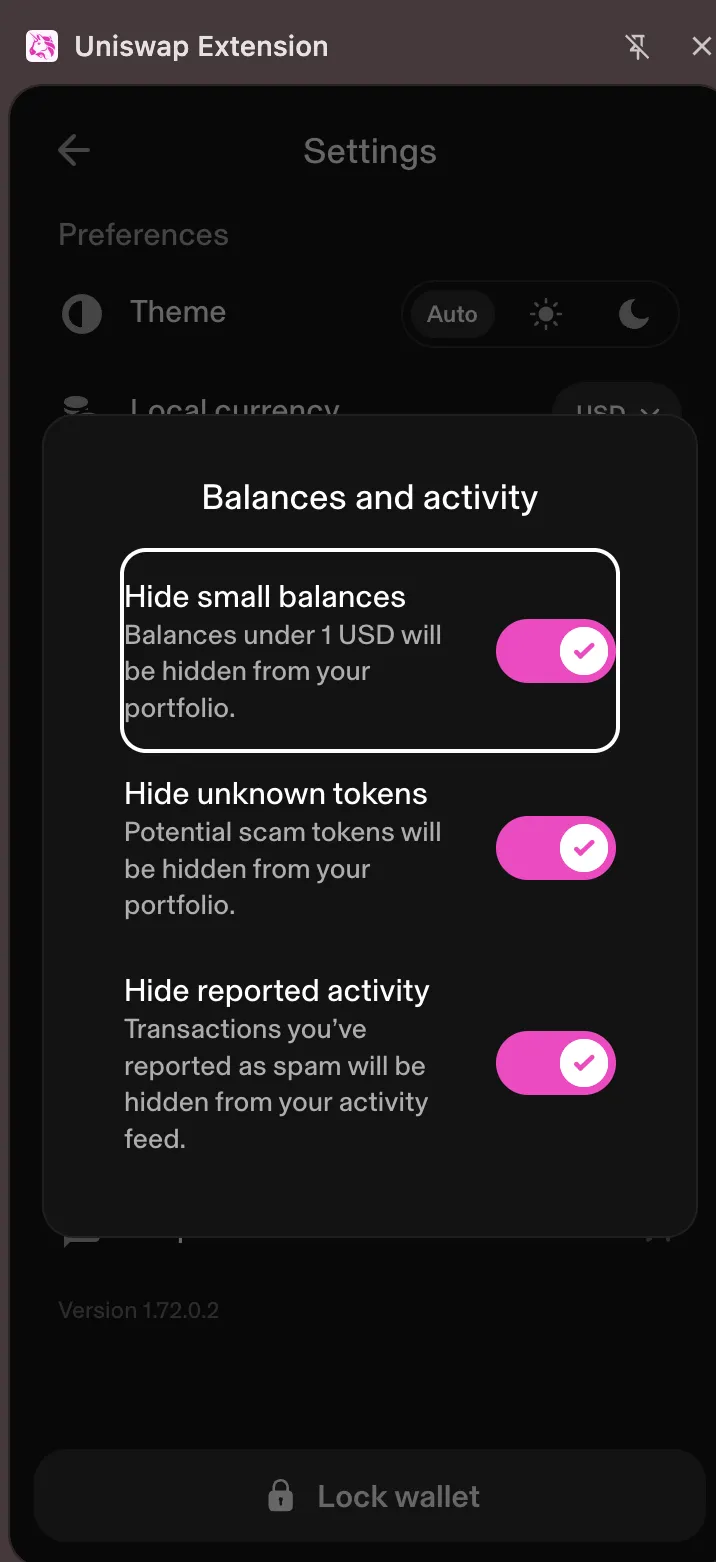
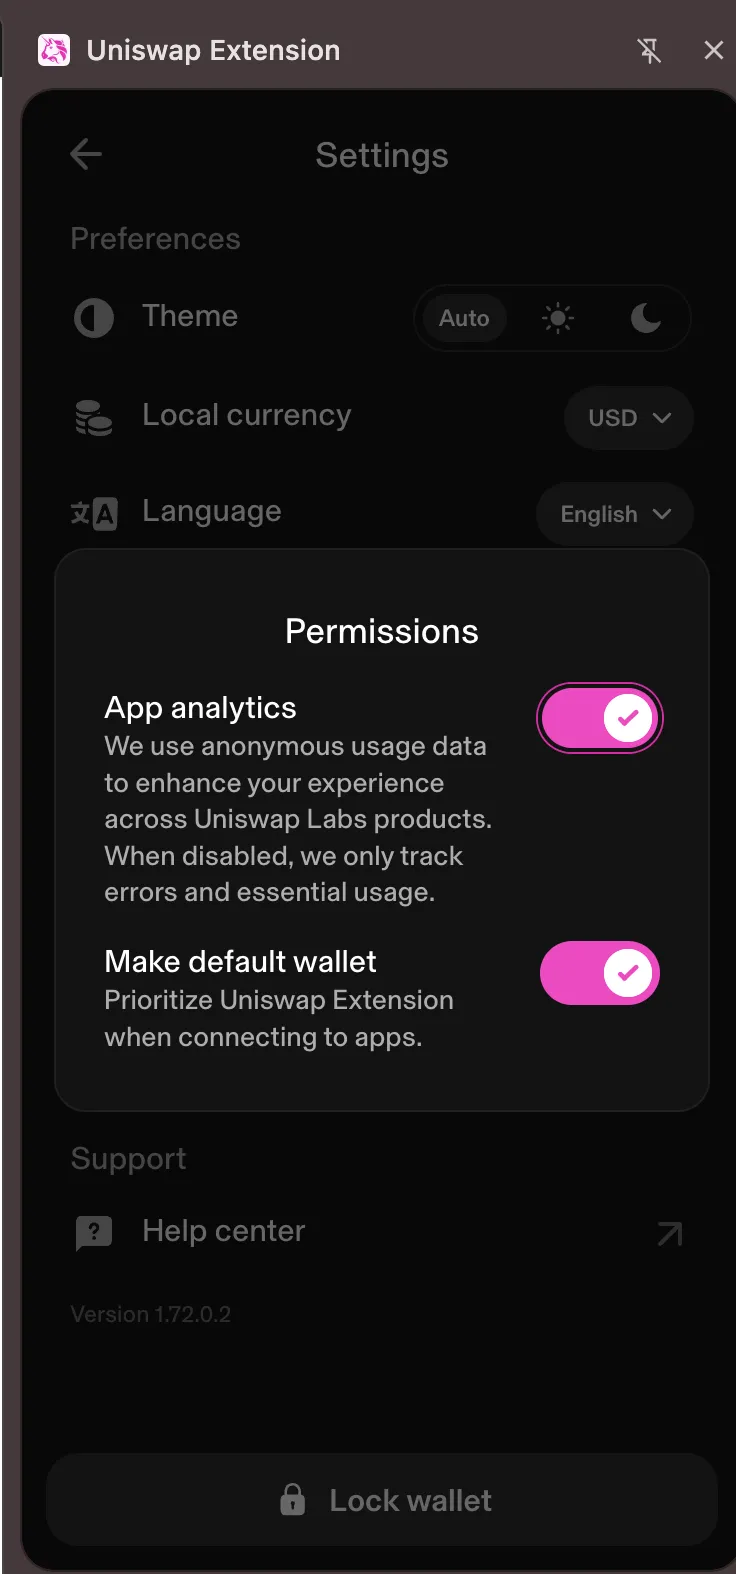
The wallet does not allow users to revoke token approvals through its own built-in revocation system or links to external dApps.
— Verified by Sebastian Camia at Coinspect
Evidence · 3 screenshots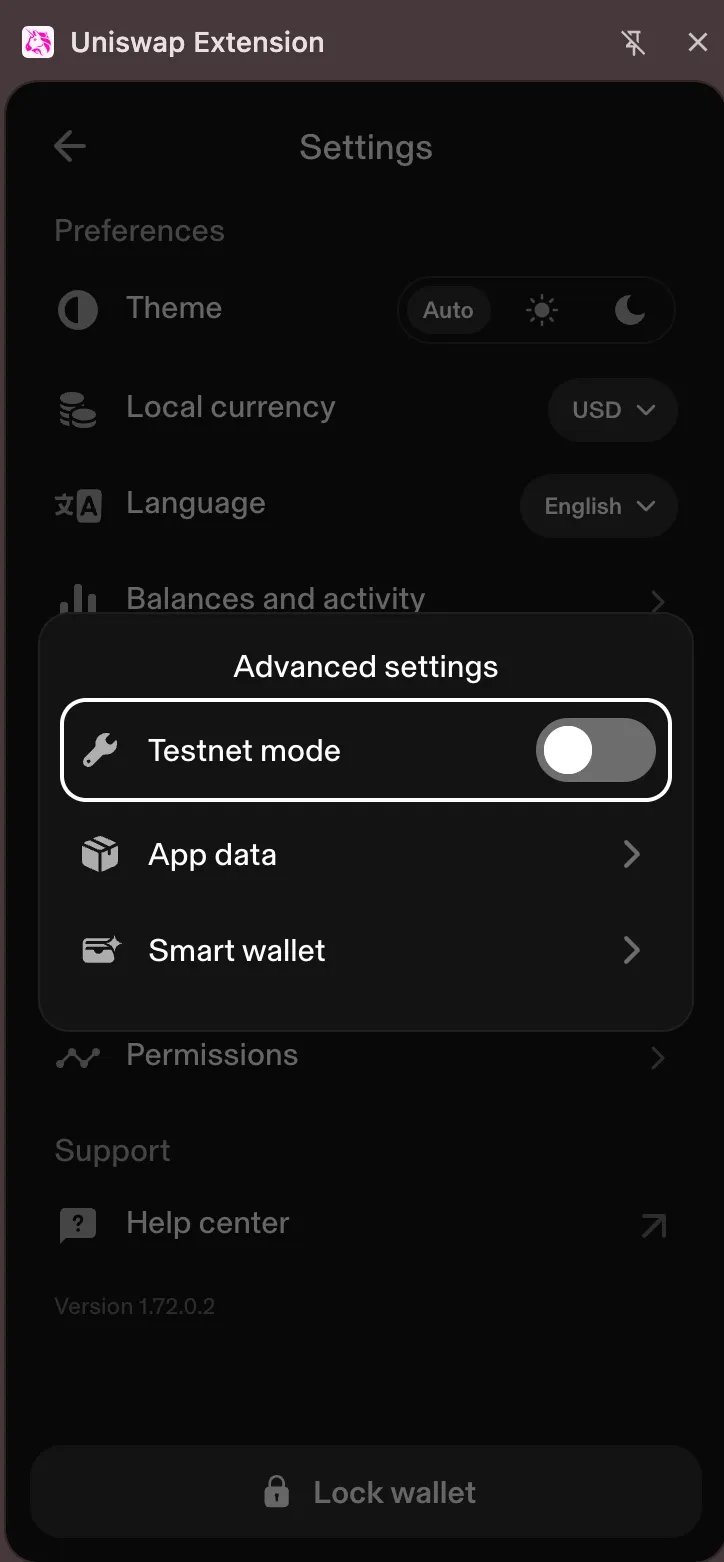
 Last updated on Sep 3, 2026Report an issue with this check
-
- Connected dApp management1.5 / 1.5Description
Allows users to list and revoke connected dApps.
-
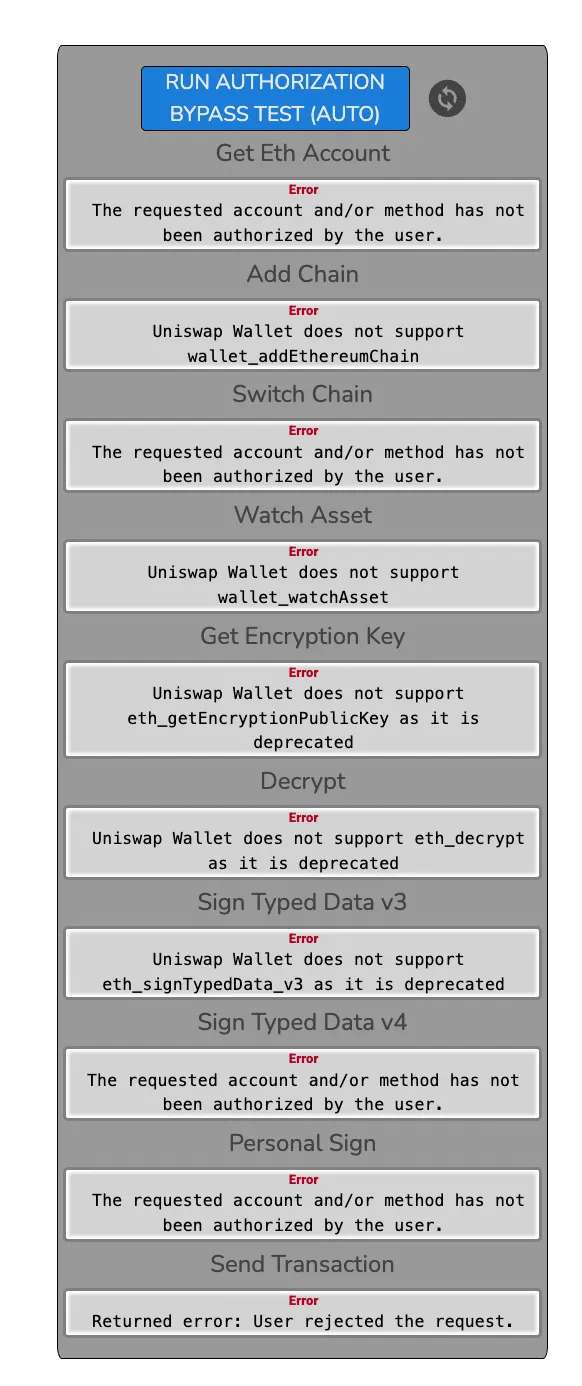
The wallet lists the connected dApps and after disconnecting a dApp, the RPC requests from it are rejected.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots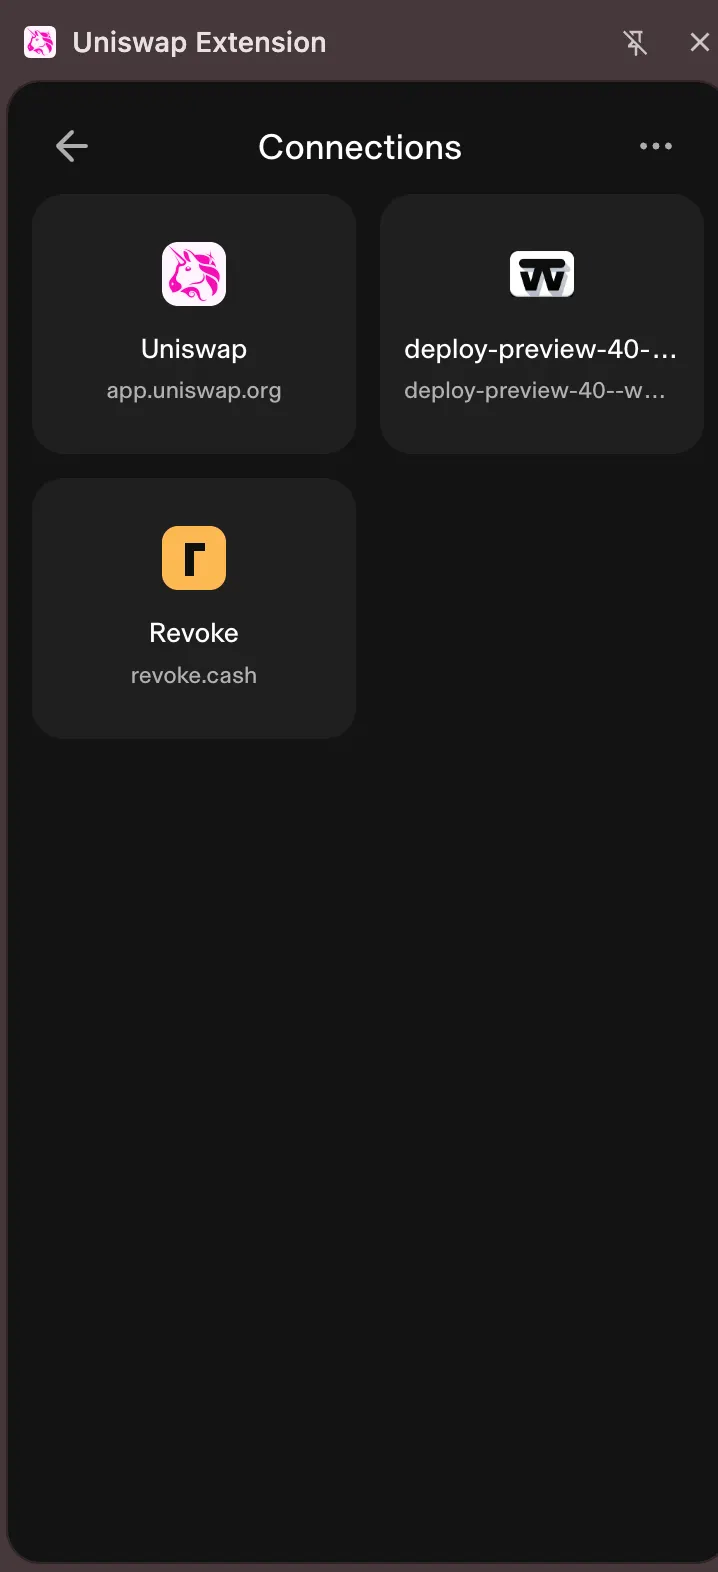
 Last updated on Sep 3, 2026Report an issue with this check
-
- User confirmation before switching chains0.0 / 1.2Description
Requires user confirmation before switching the active chain.
-
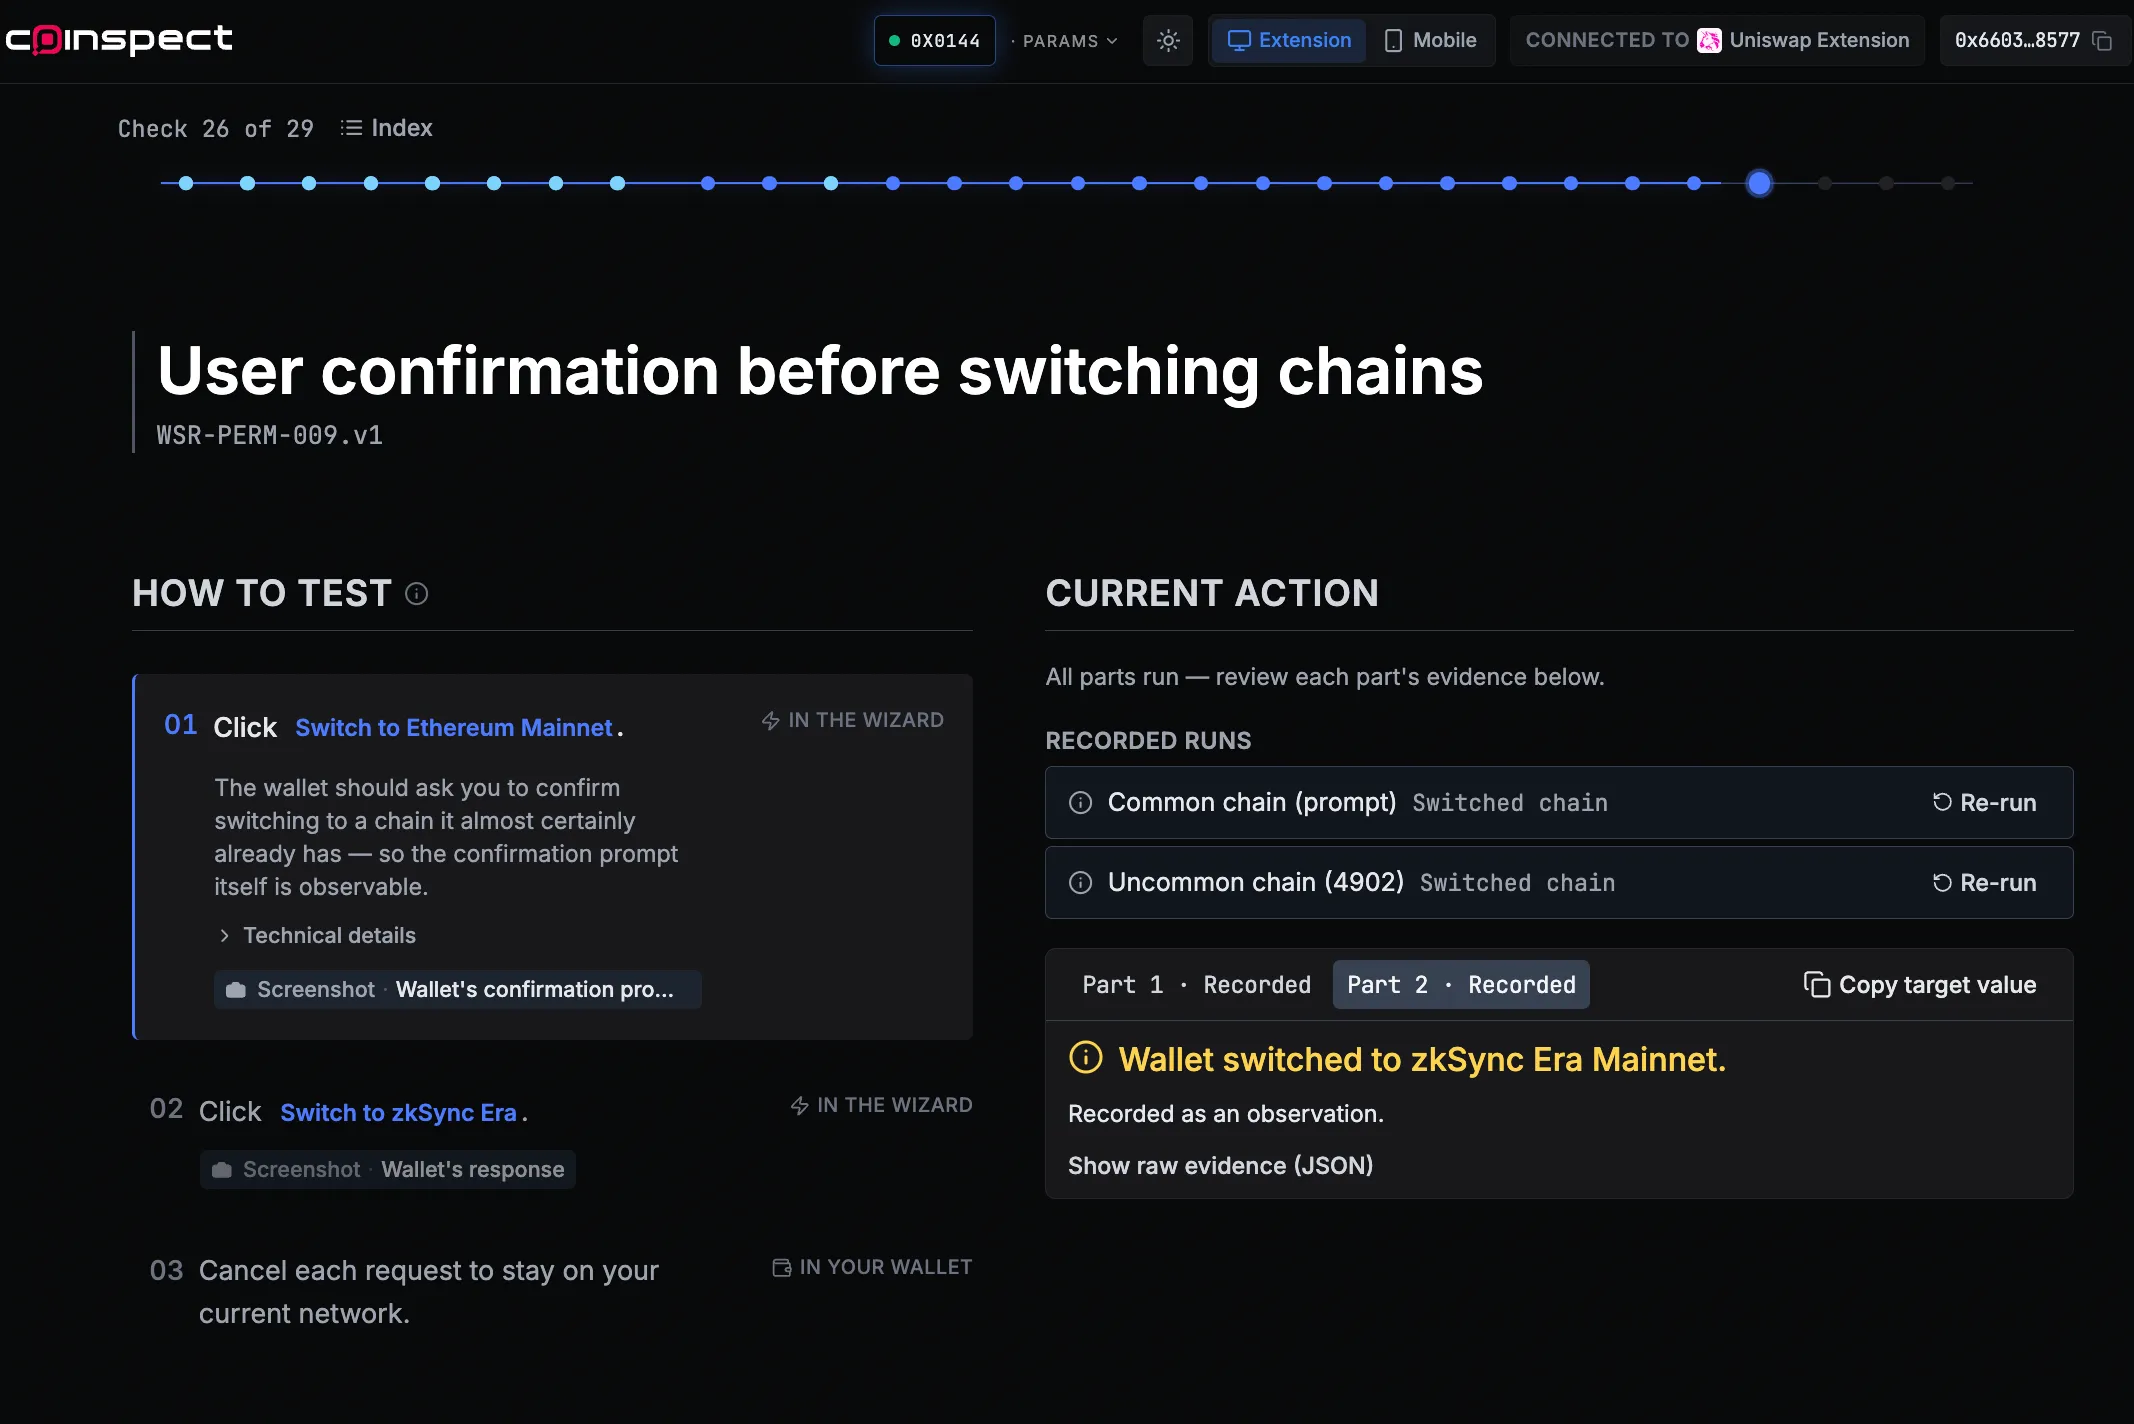
The wallet switched to Ethereum Mainnet and zkSync Era Mainnet without displaying a confirmation prompt, allowing chain switches without user confirmation.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots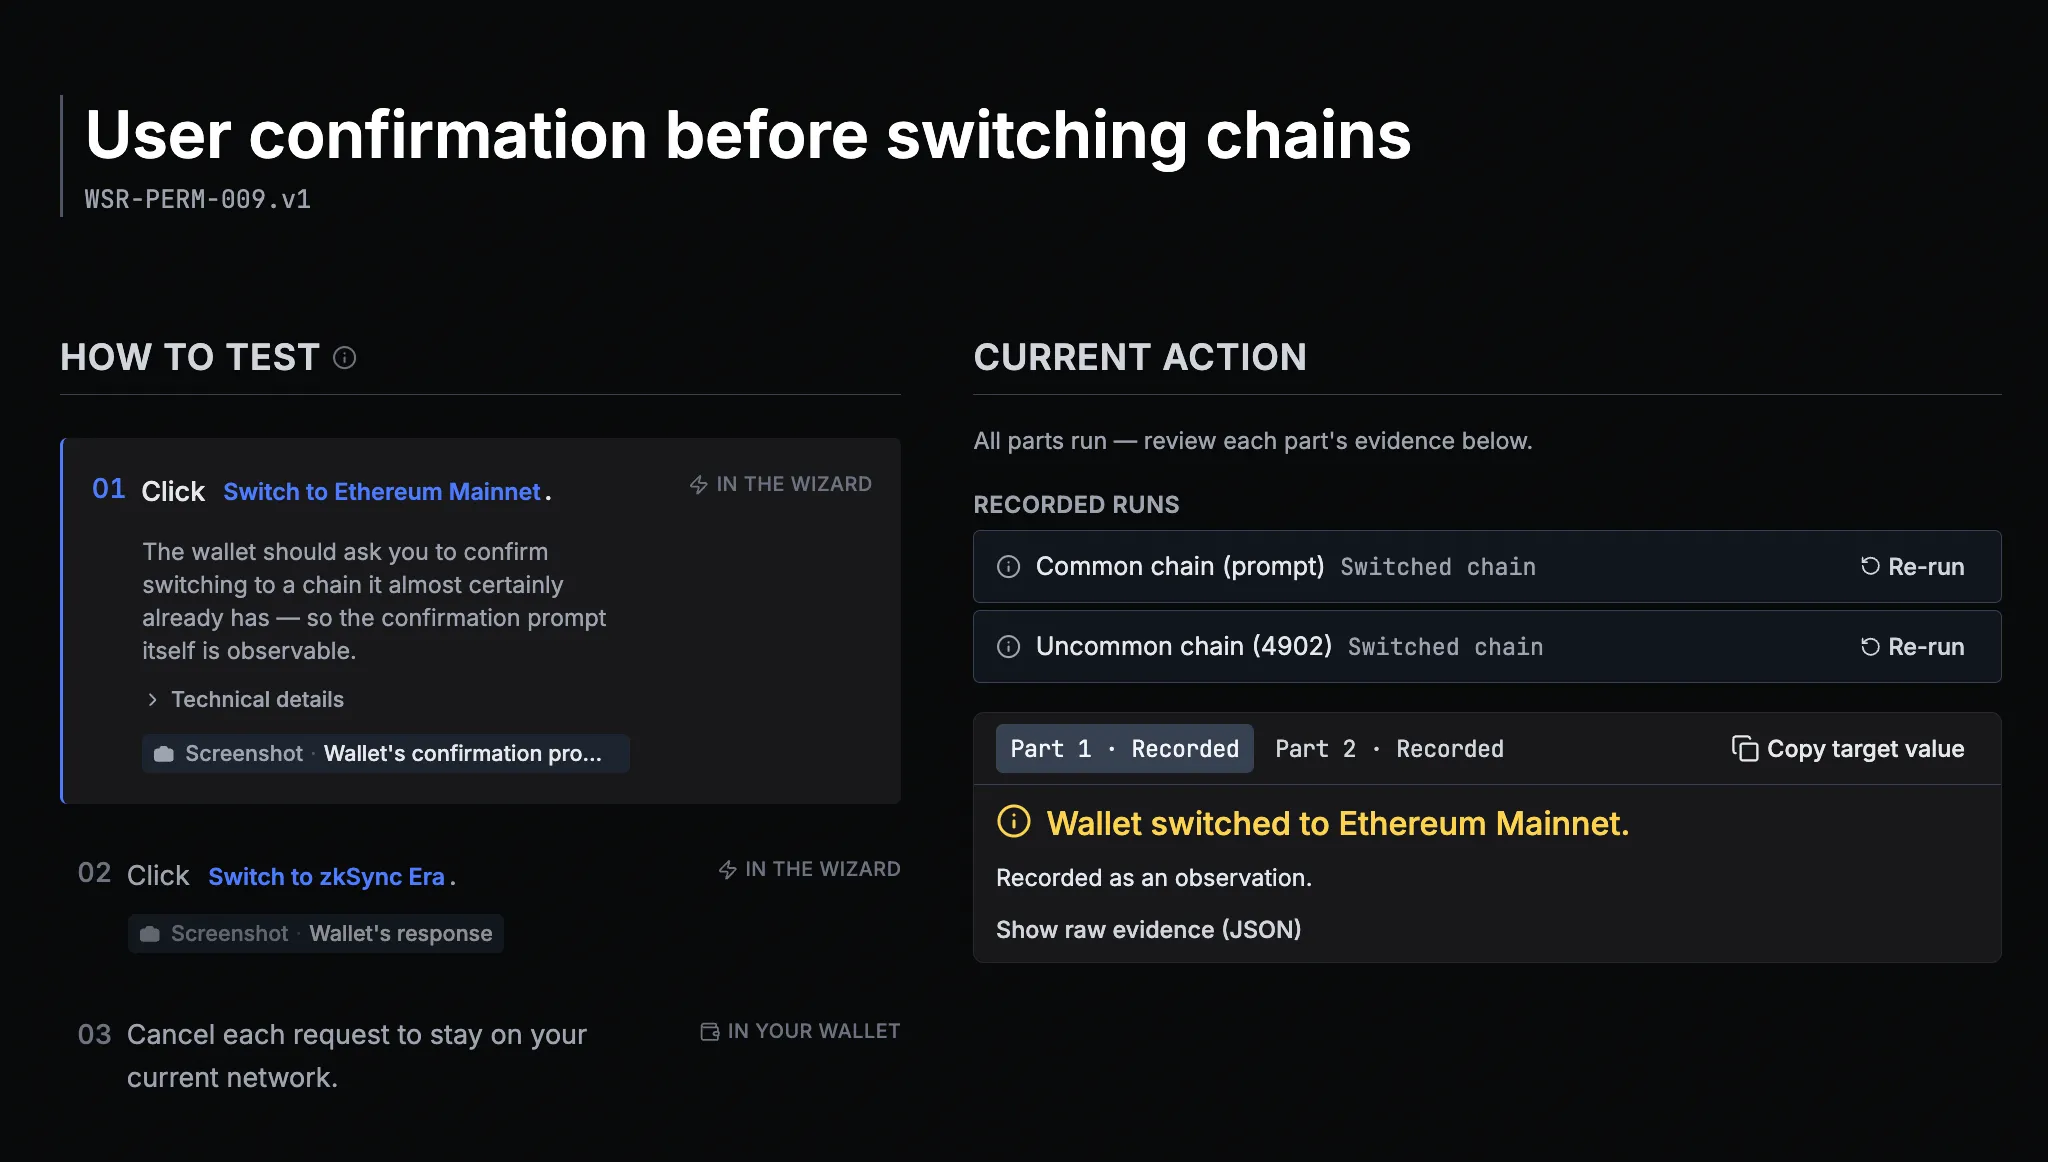
 Last updated on Sep 3, 2026Report an issue with this check
-
Intent Verification
- Transaction simulation6.7 / 6.7Description
Previews the expected outcome by simulating the request execution on the blockchain before signing.
-
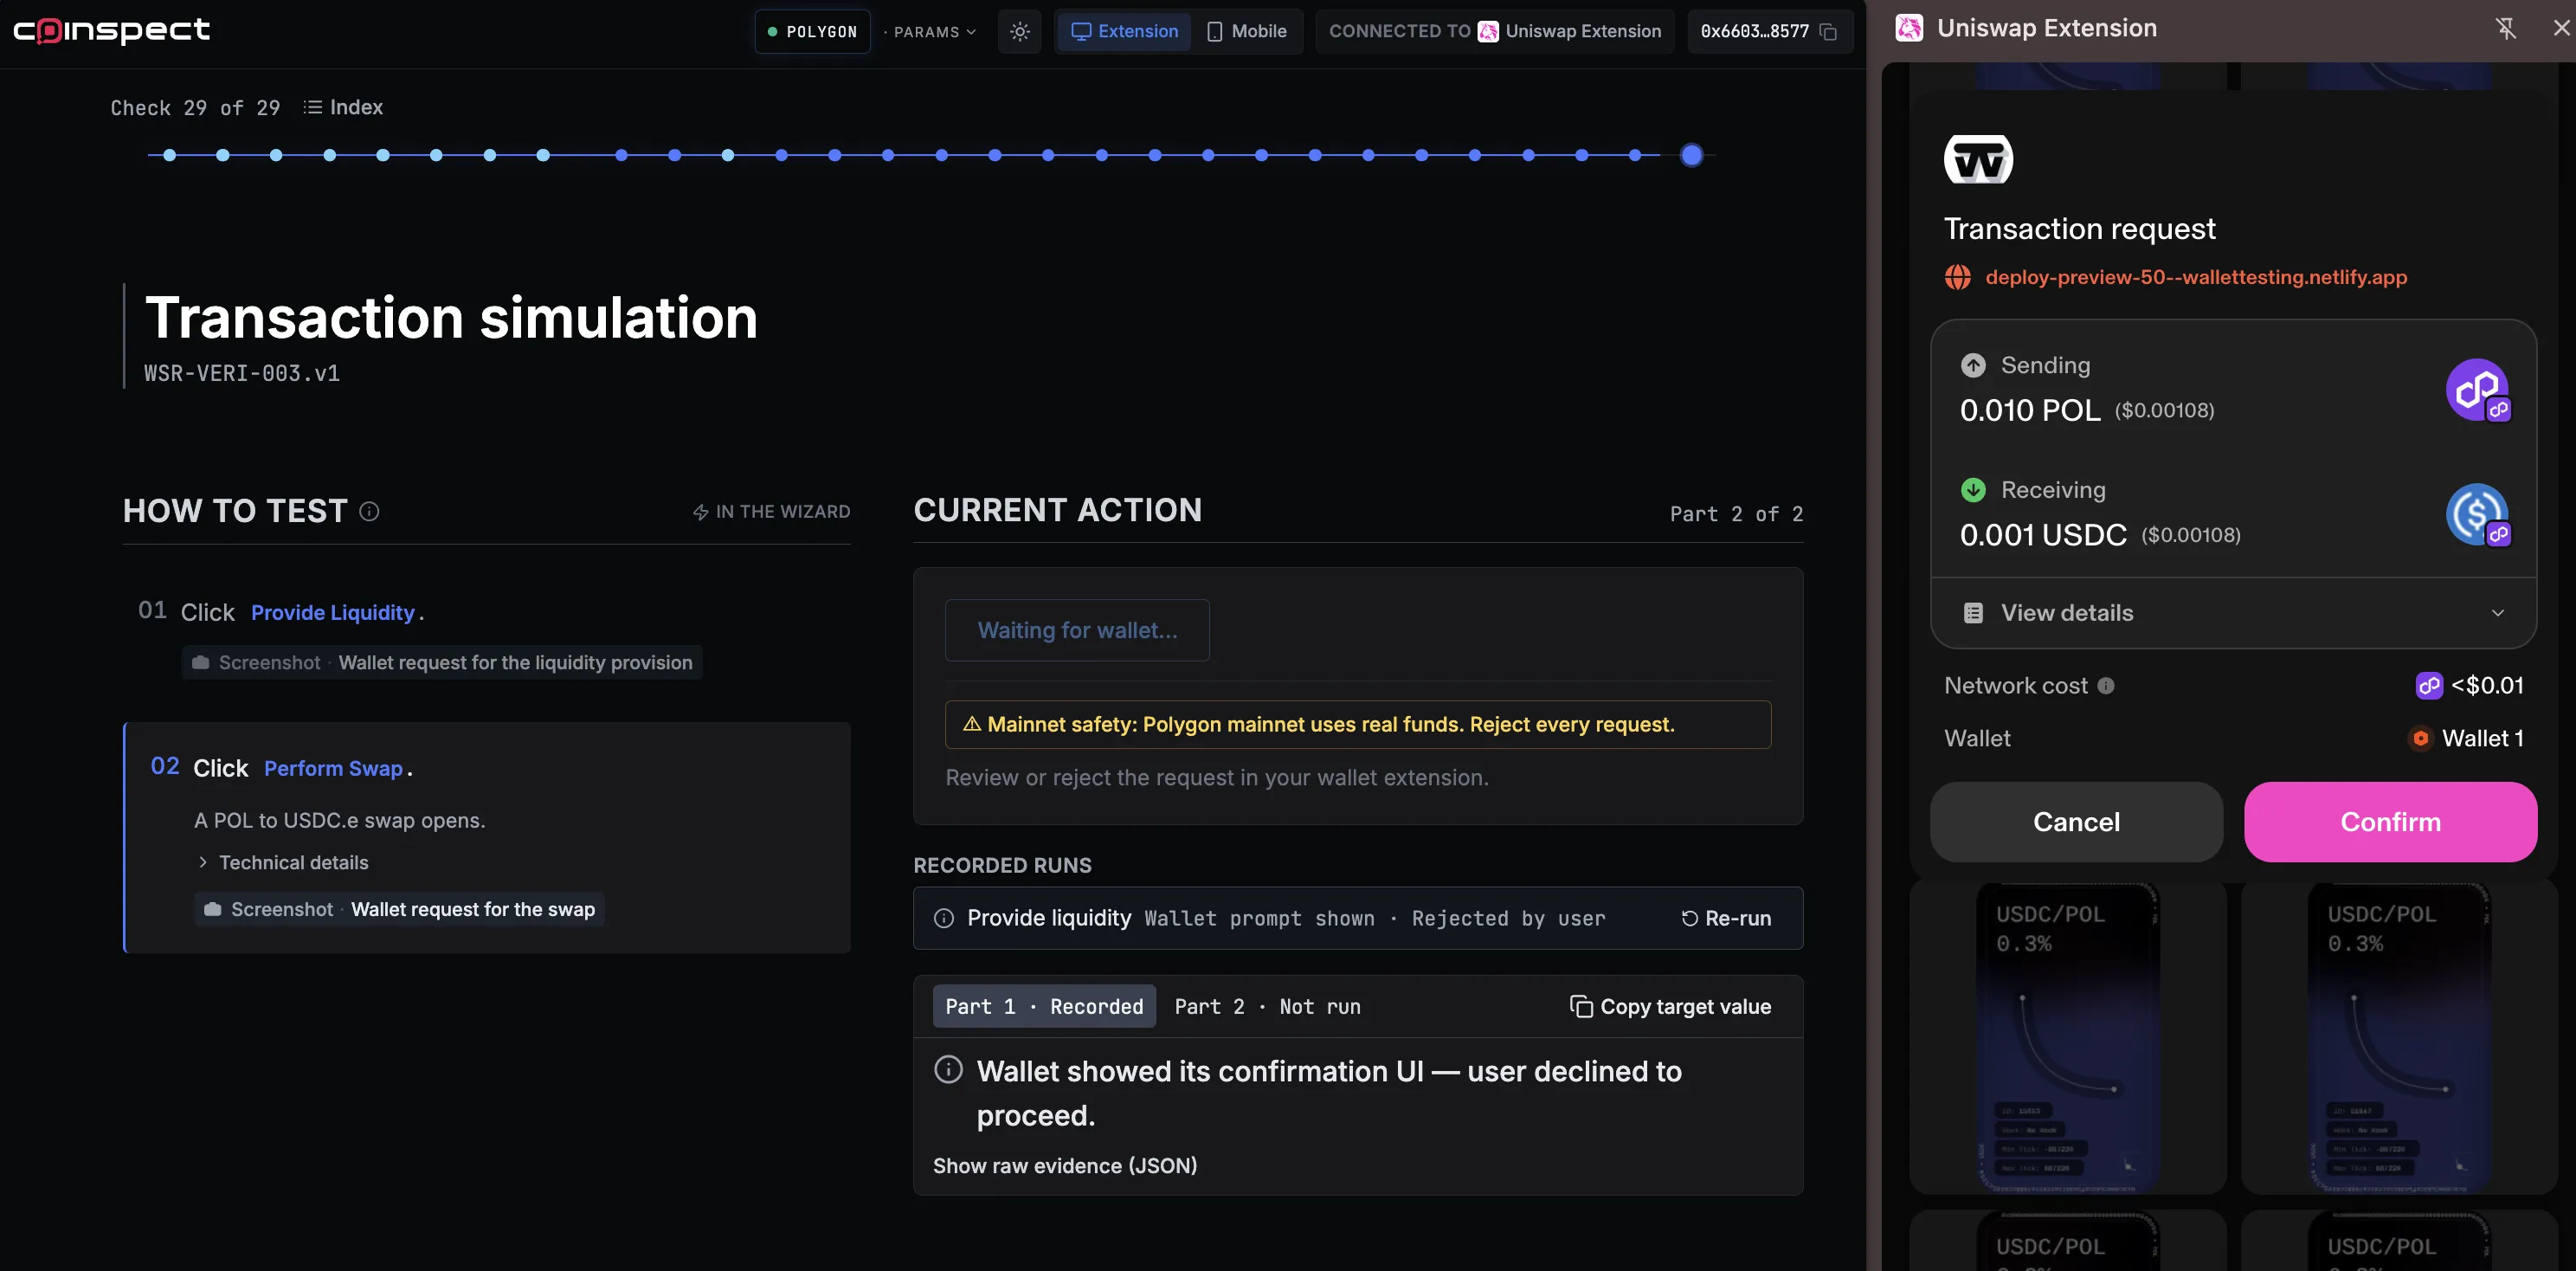
The wallet displays the expected transaction effects for both liquidity provision (sending POL, receiving UNI-V3-POS) and swap (sending POL, receiving USDC) before signing.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots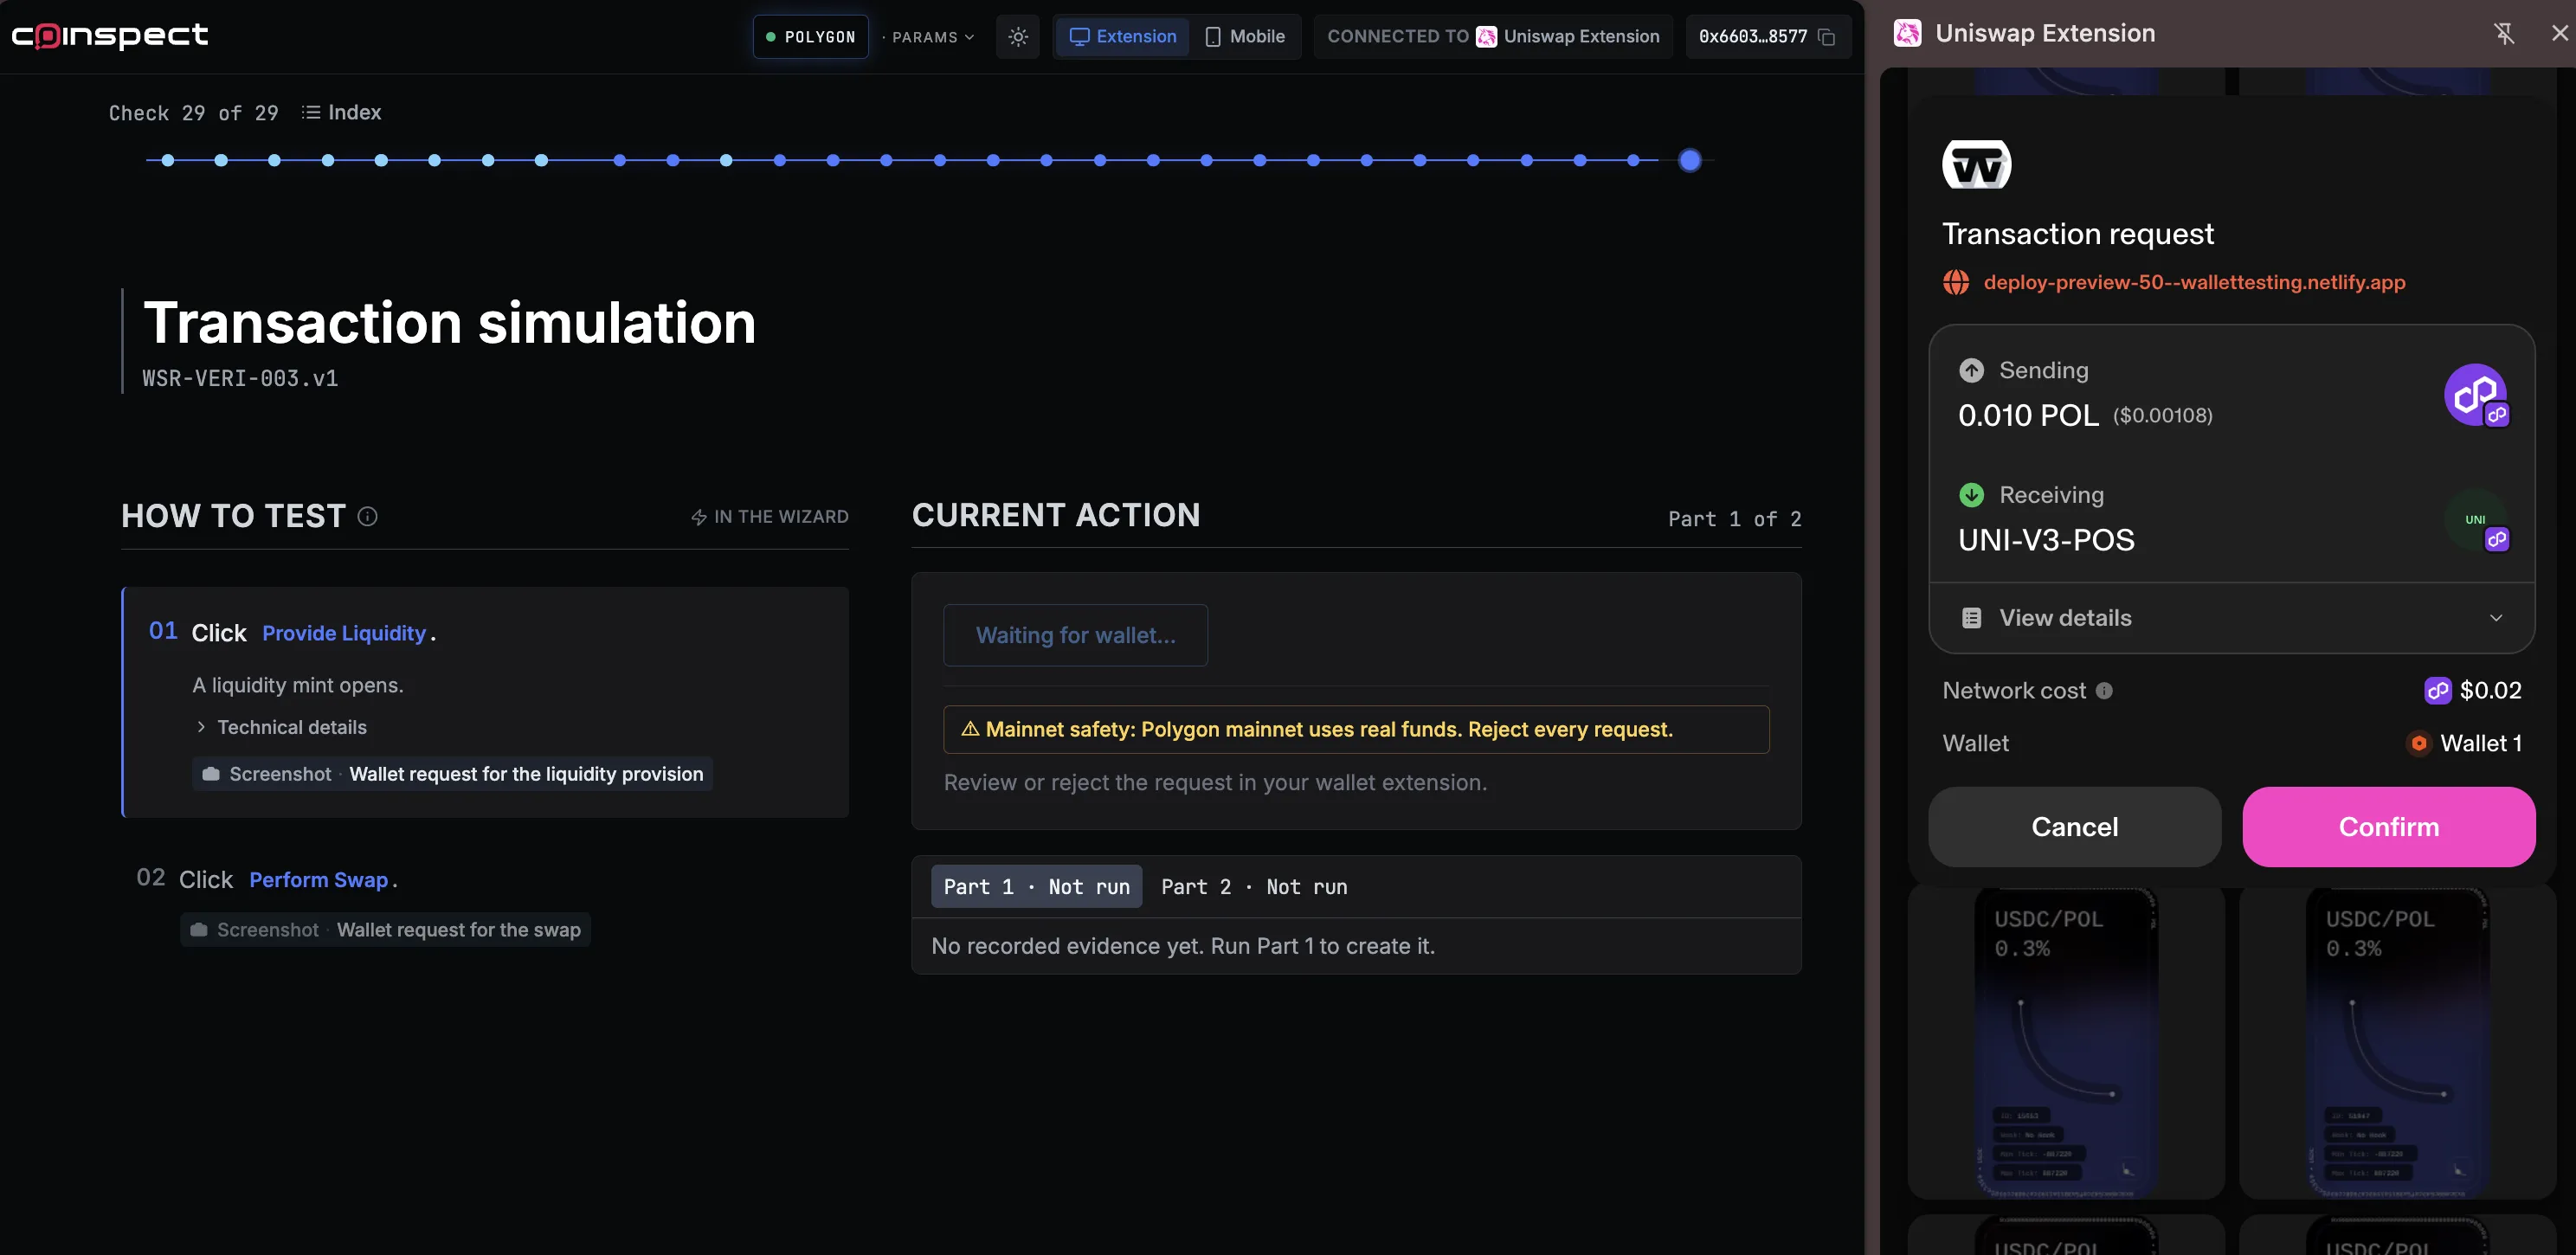
 Last updated on Sep 3, 2026Report an issue with this check
-
- Clear token approval dialog0.0 / 6.7Description
Clearly displays all the key details for ERC-20 Approve requests.
-
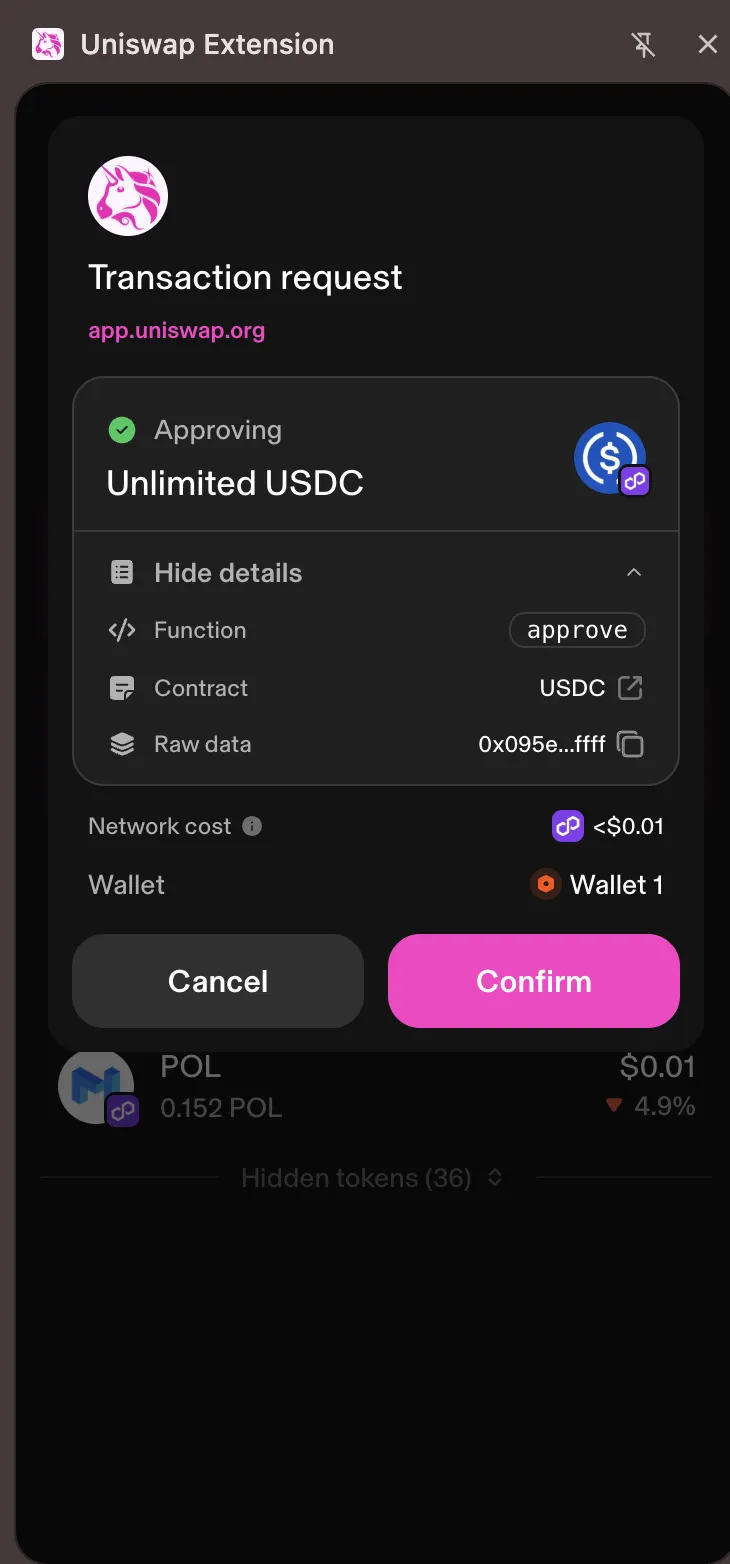
The wallet clearly displays the token (USDC) and the approved amount (unlimited), but not the spender (Uniswap).
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots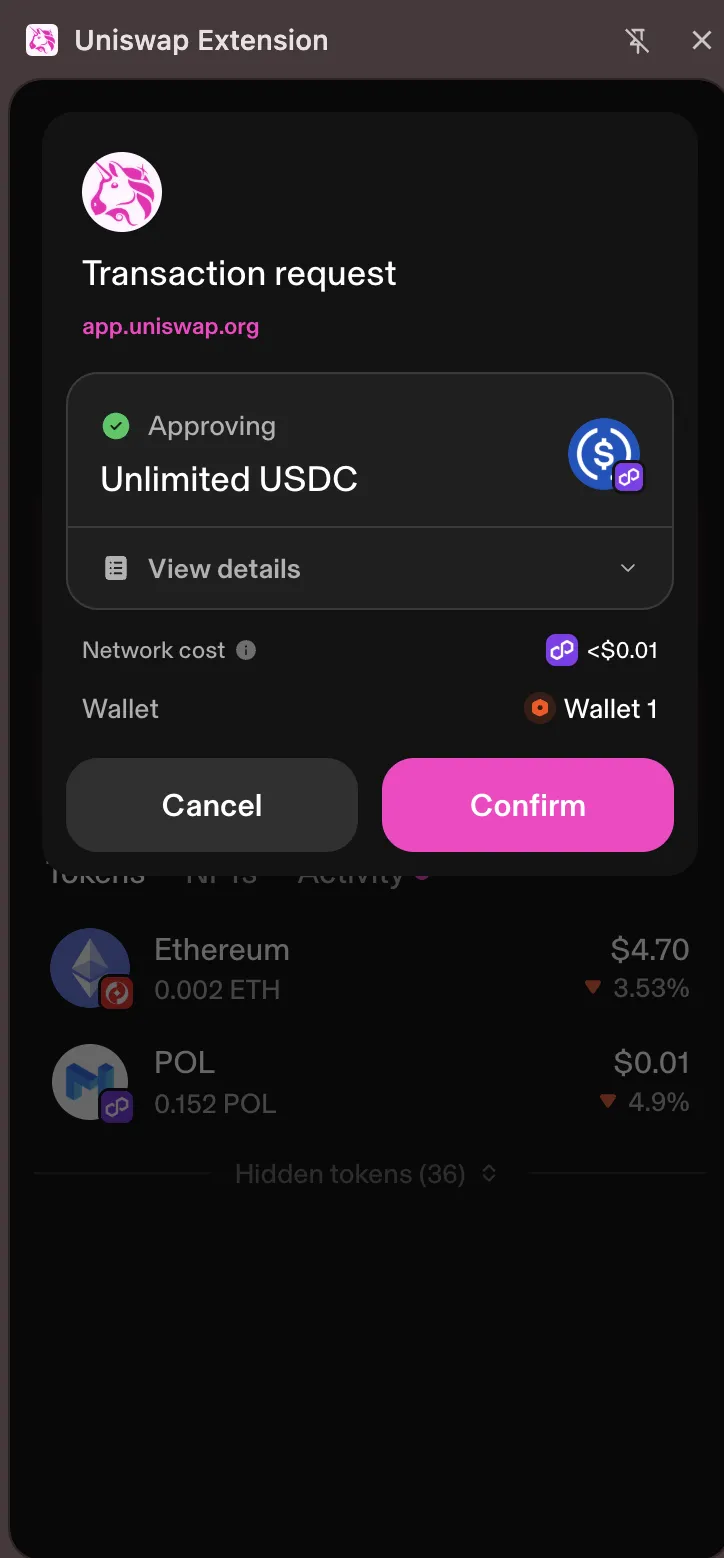
 Last updated on Sep 3, 2026Report an issue with this check
-
- Clear message signing dialog3.8 / 3.8Description
Clearly displays all message signature request details without truncating or hiding information.
-
The data is scrollable in personal_sign and eth_signTypedData (EIP-712) signature requests, and the verifyingContract parameter is also displayed.
— Verified by Sebastian Camia at Coinspect
Evidence · 3 screenshots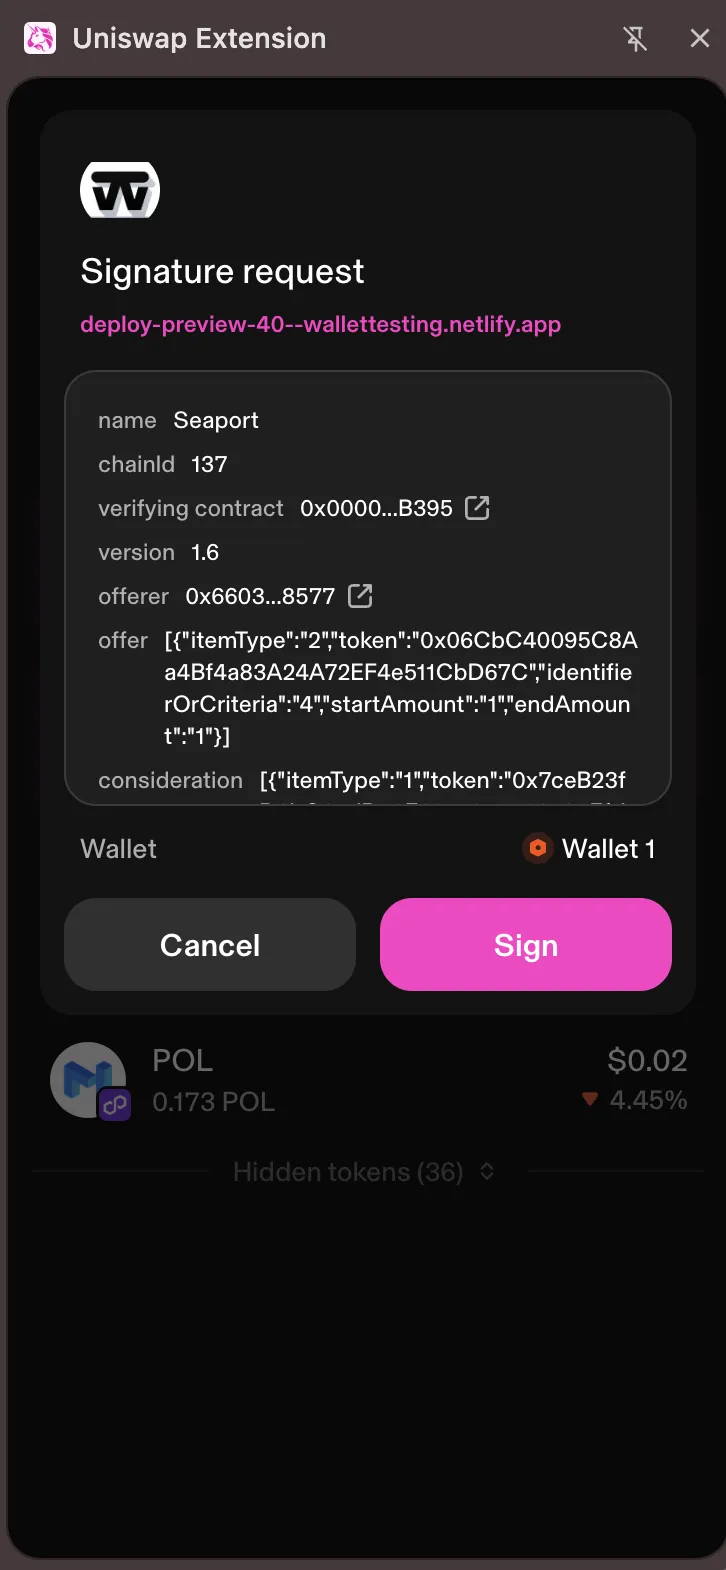
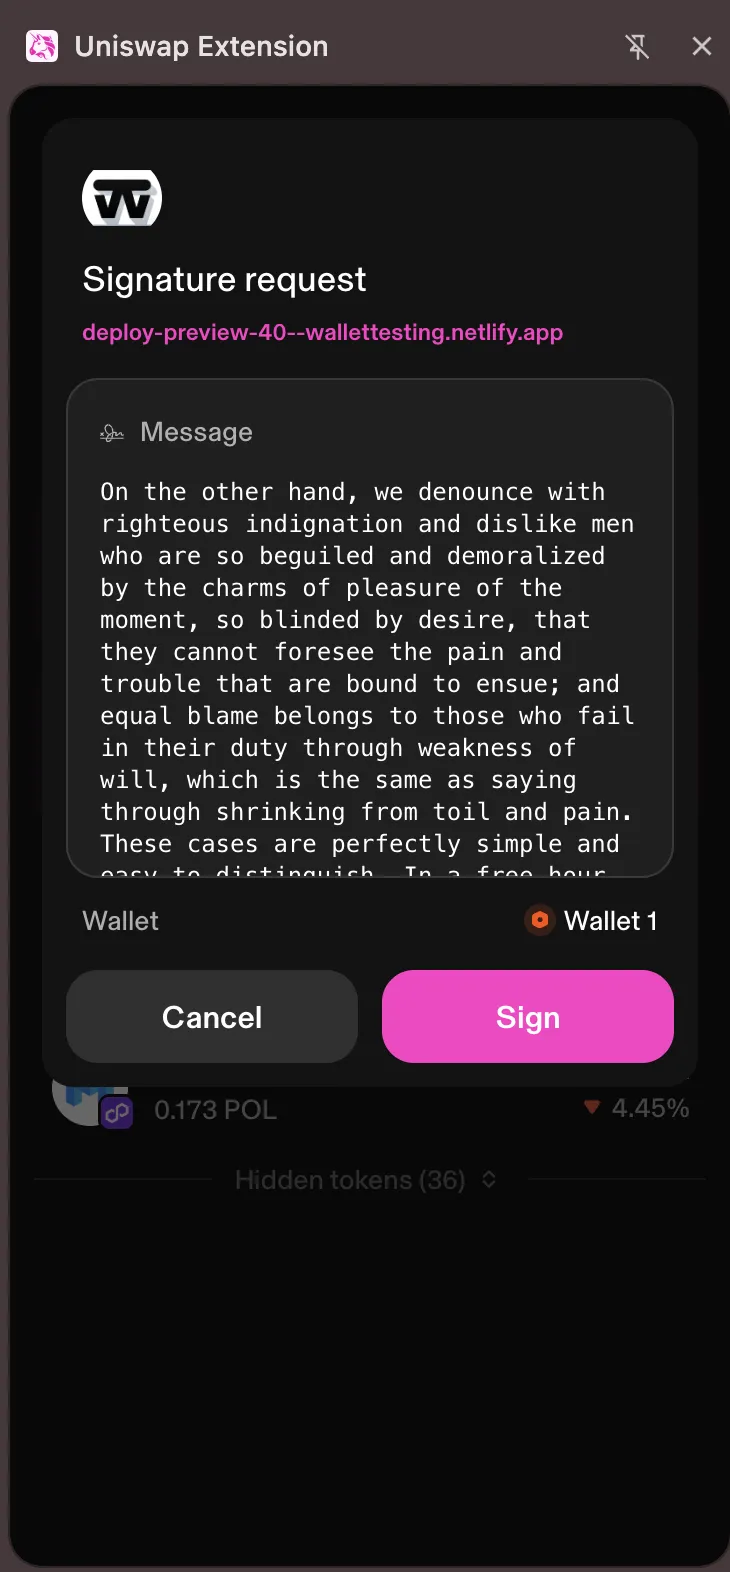
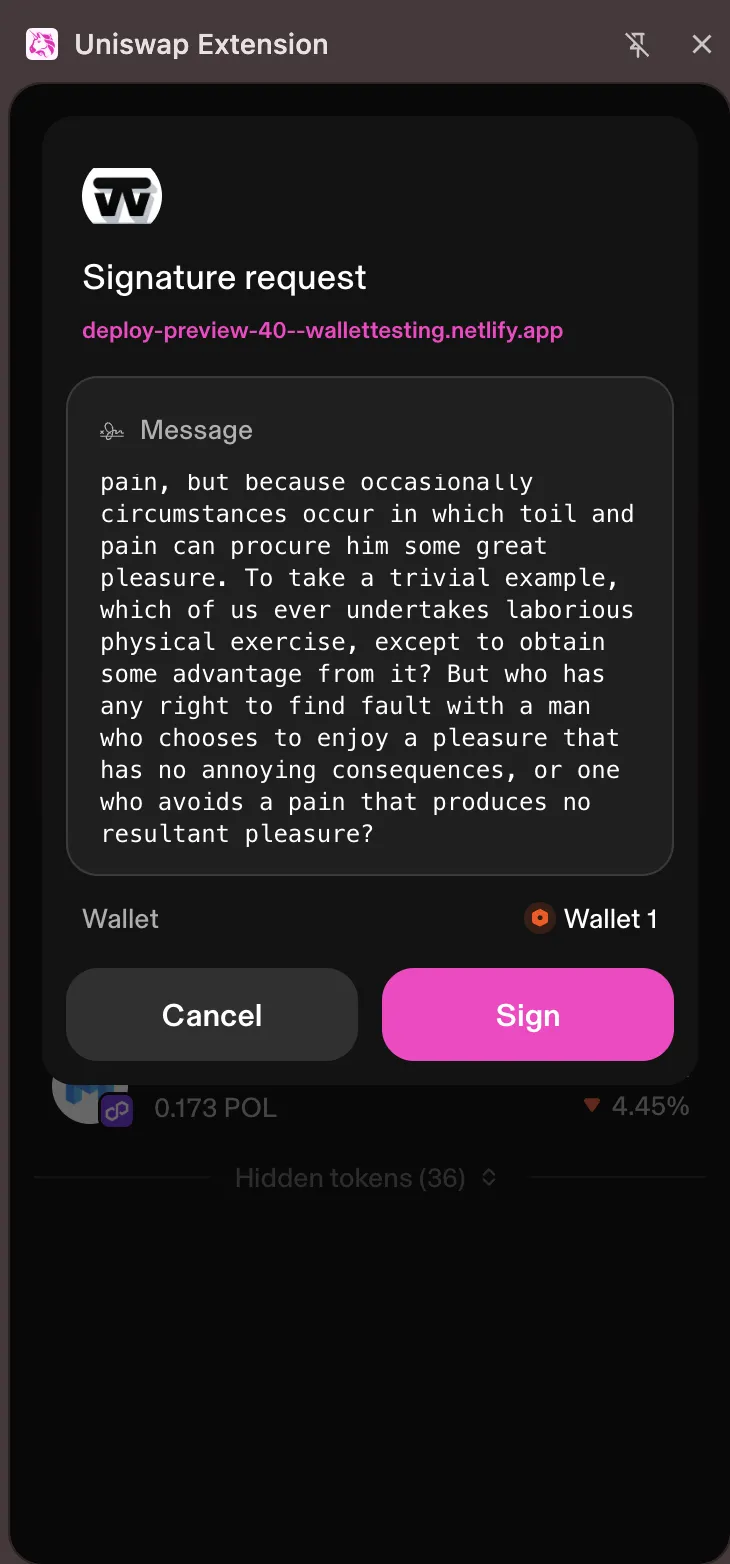 Last updated on Sep 3, 2026Report an issue with this check
-
- EIP-712 message parsing0.0 / 2.4Description
Displays human-readable details for EIP-712 signature requests from well-known protocols.
-
The Seaport EIP-712 signature request is rendered as raw JSON, rather than structured, human-readable details.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot Last updated on Sep 3, 2026Report an issue with this check -
- Invalid address checksum detection2.2 / 2.2Description
Warns users when they input addresses with invalid EIP-55 checksums.
-
The wallet does not allow the manual transaction to proceed because the checksum is invalid. When attempting via the dApp, the transaction cannot be processed, likely due to the same issue.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots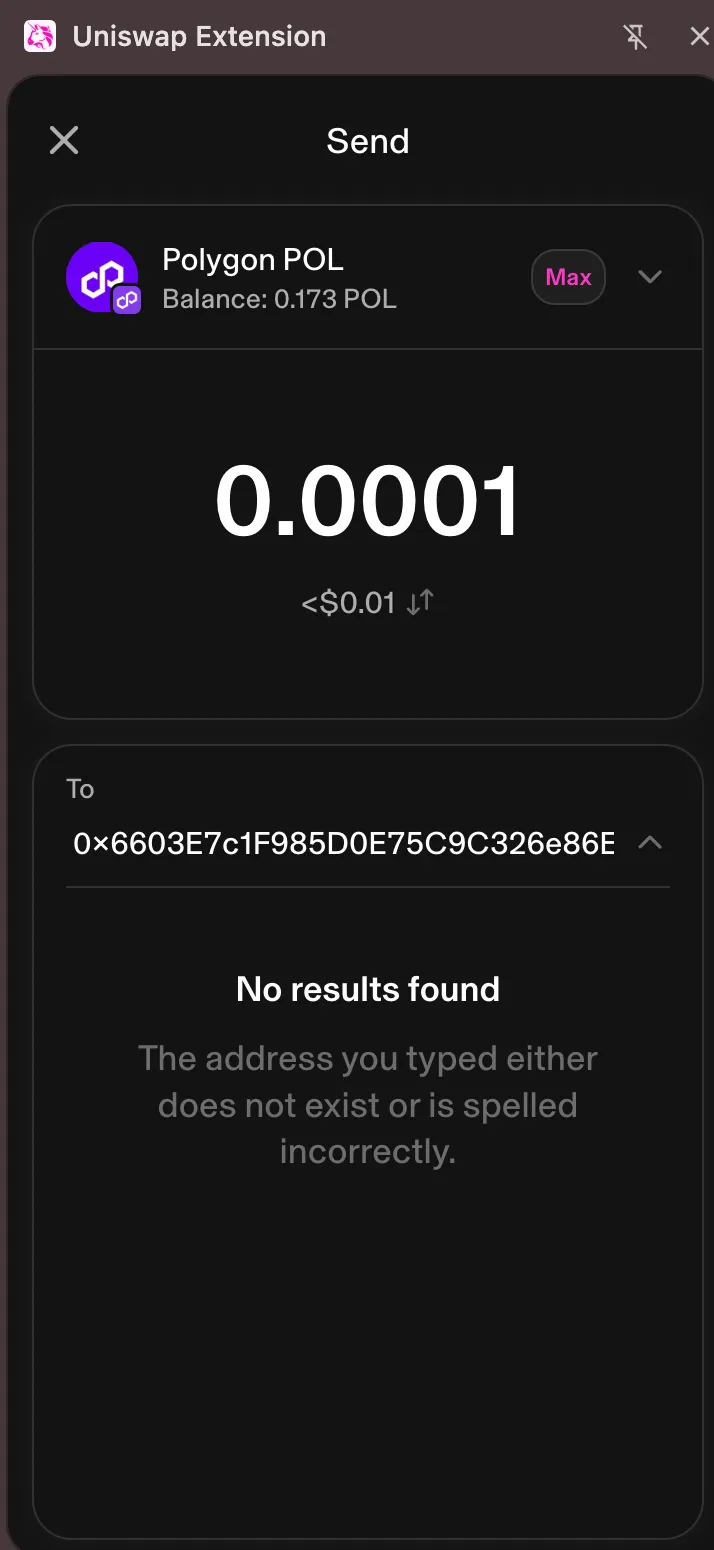
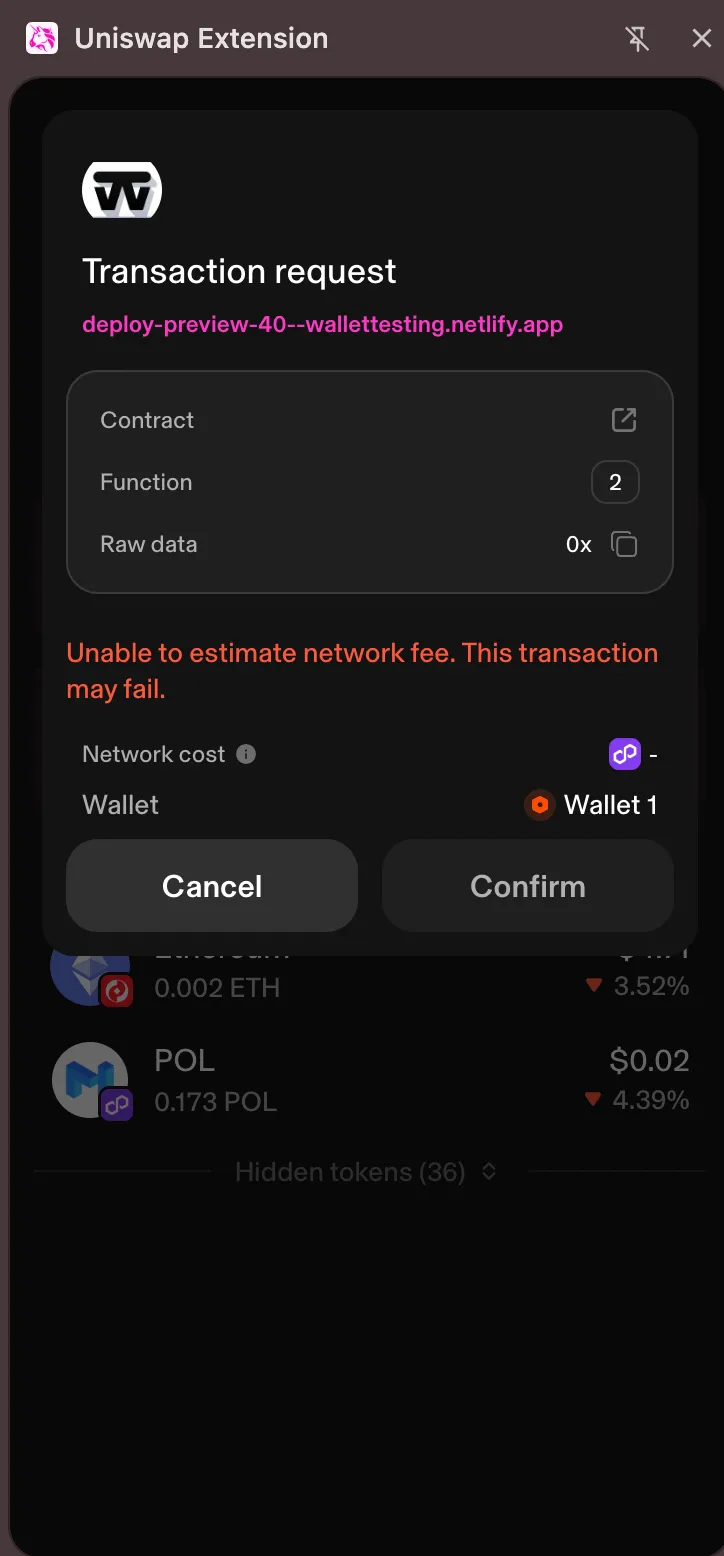 Last updated on Sep 3, 2026Report an issue with this check
-
- Mandatory message review0.0 / 2.1Description
Requires users to review all the details before signing a message.
-
The sign button is enabled before scrolling to the end of the message, failing the acceptance criteria.
— Verified by Sebastian Camia at Coinspect
Evidence · 3 screenshots Last updated on Sep 3, 2026Report an issue with this check -
- Links to blockchain explorers1.2 / 1.2Description
Provides clickable links to block explorers for at least one key blockchain identifier.
-
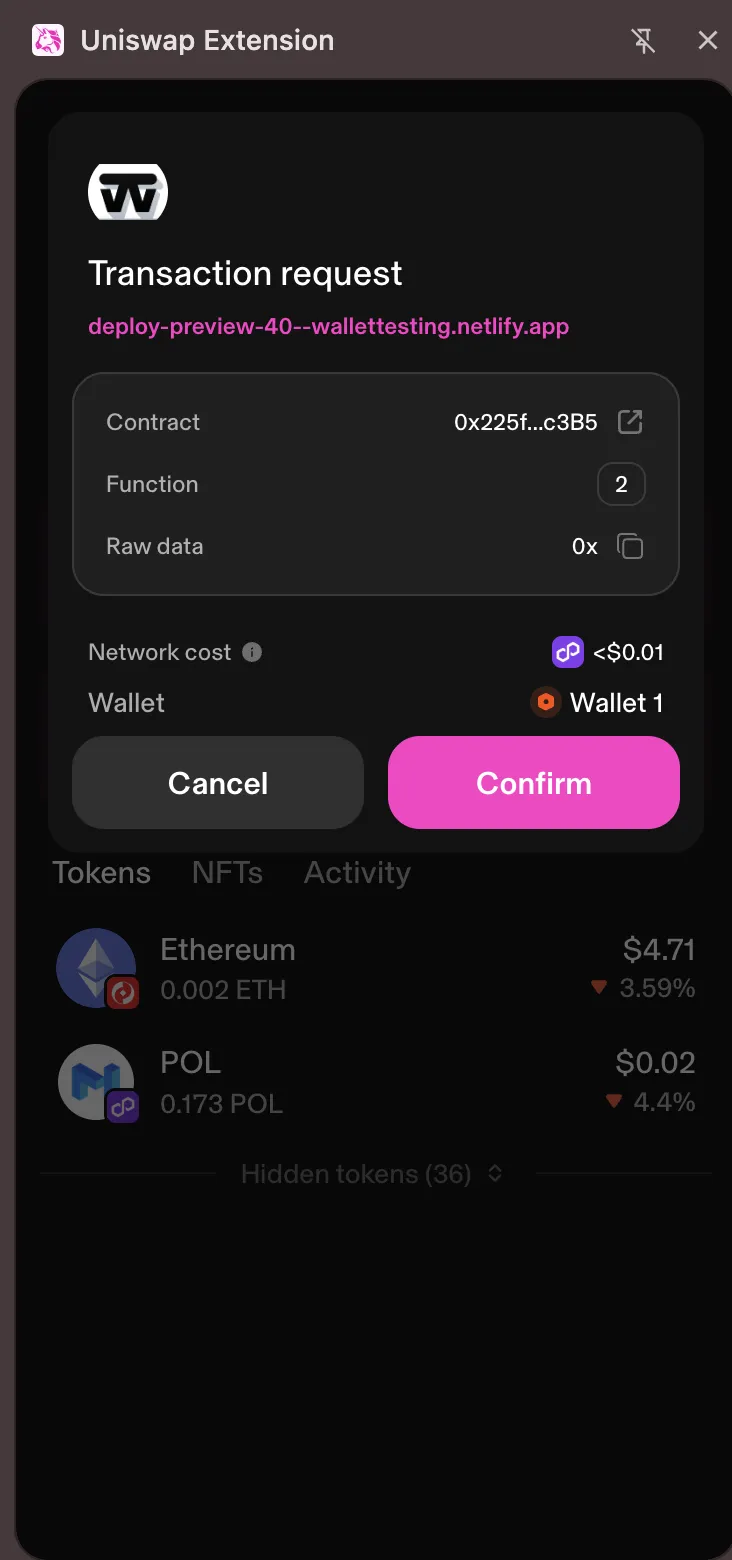
The address, transaction, and contract address are clickable links that redirect to the block explorer in both transaction history and send transaction screens.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots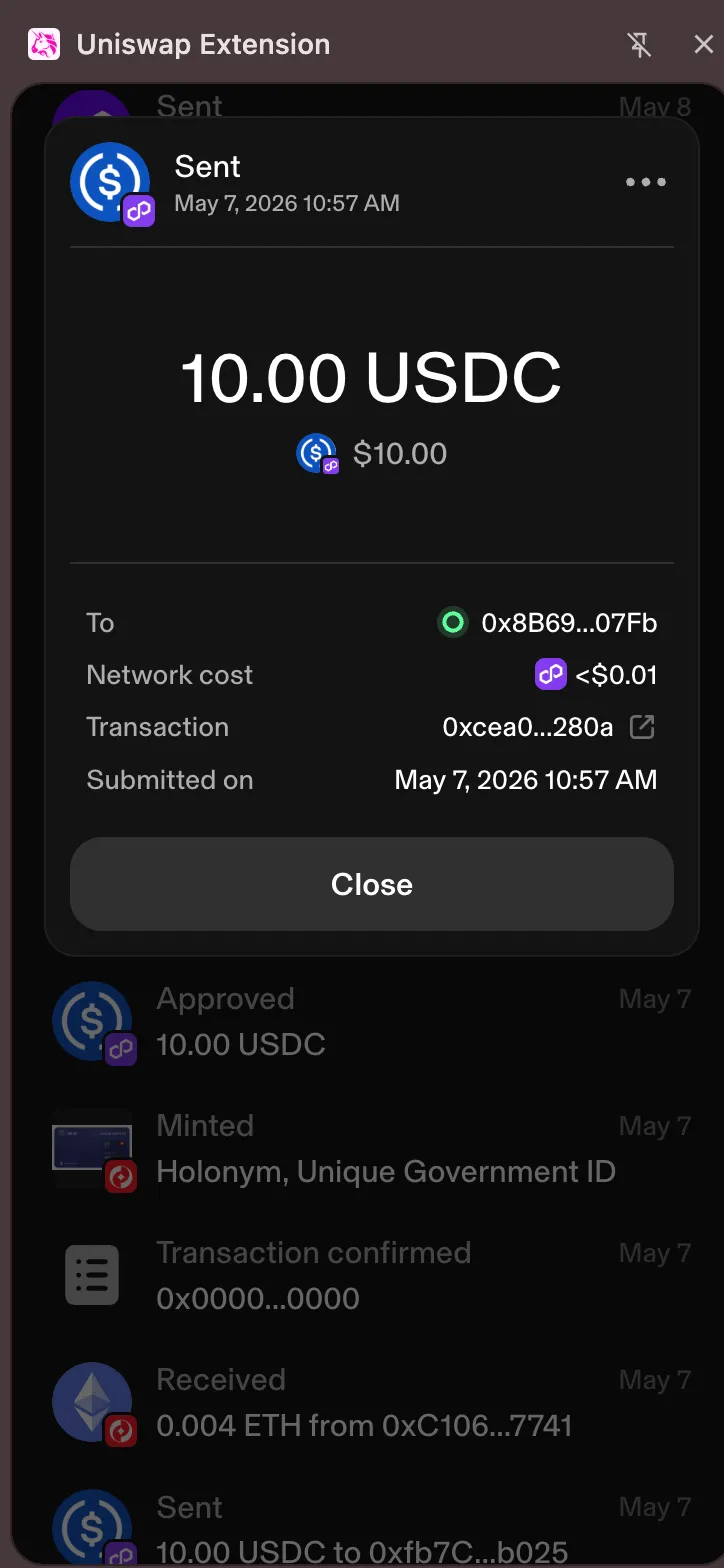
 Last updated on Sep 3, 2026Report an issue with this check
-
Physical Access
- Seed phrase access control6.6 / 6.6Description
Requires authentication to access seed phrases or private keys.
-
The wallet requires password authentication before displaying the recovery phrase.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot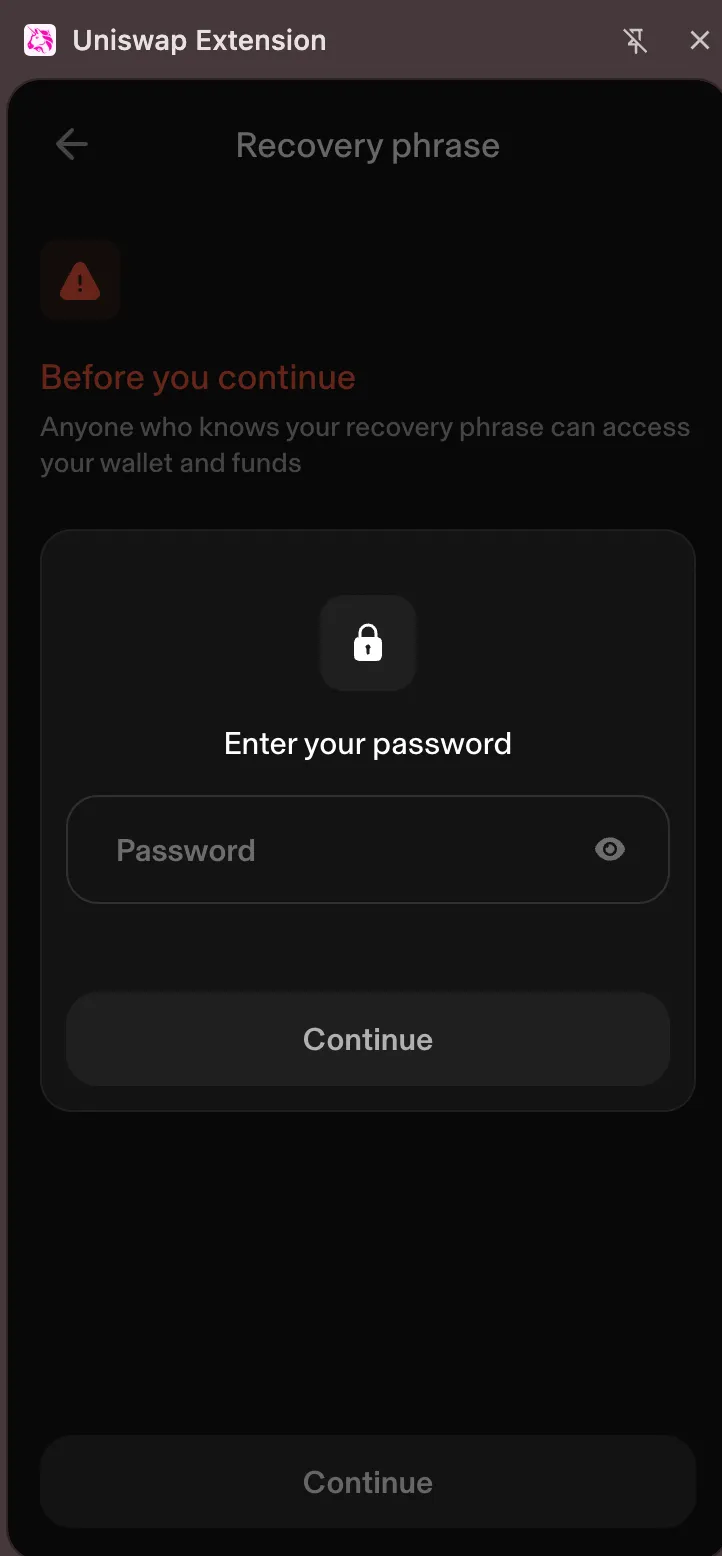 Last updated on Sep 3, 2026Report an issue with this check
-
- Manual wallet lock3.4 / 3.4Description
Allows users to lock it manually.
-
The screenshot shows a 'Lock wallet' button at the bottom of the settings page.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot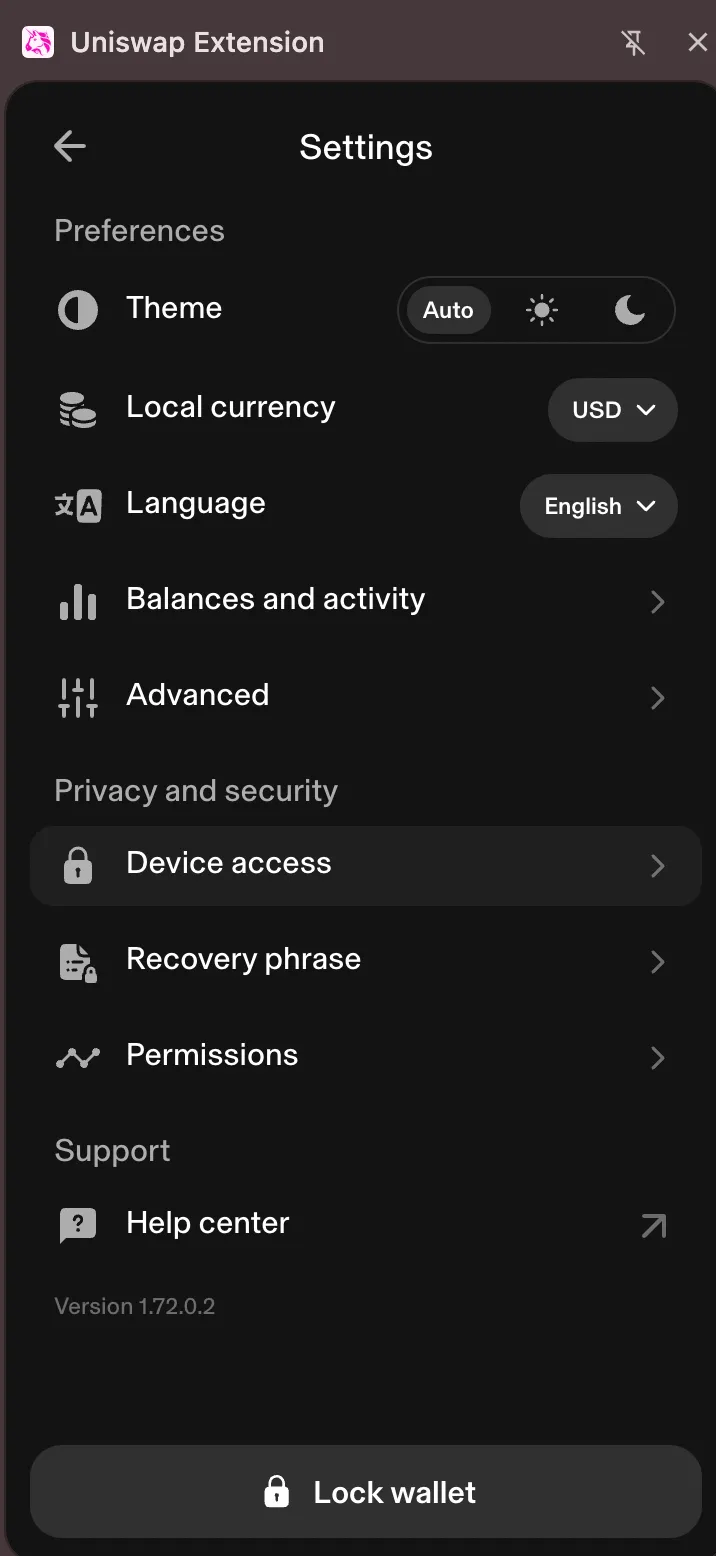 Last updated on Sep 3, 2026Report an issue with this check
-
- Automatic wallet lock0.0 / 3.4Description
Verifies wallet auto-locks on inactivity.
-
The default auto-lock timeout is 30 minutes, which does not meet the acceptance criteria of auto-locking within 20 minutes.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot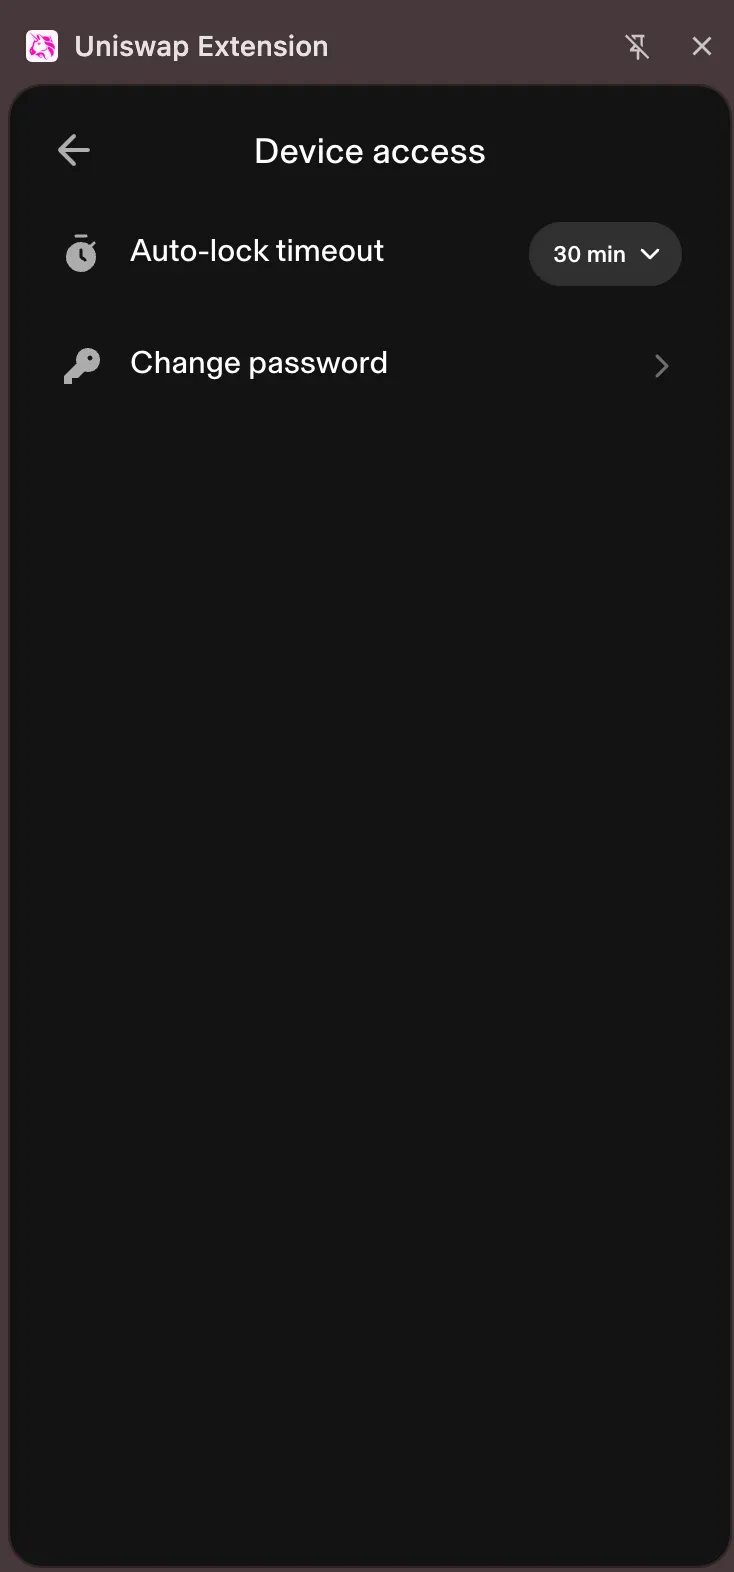 Last updated on Sep 3, 2026Report an issue with this check
-
- Robust Authentication3.2 / 3.2Description
Uses strong authentication, such as resistance to trivial or commonly-used passwords.
-
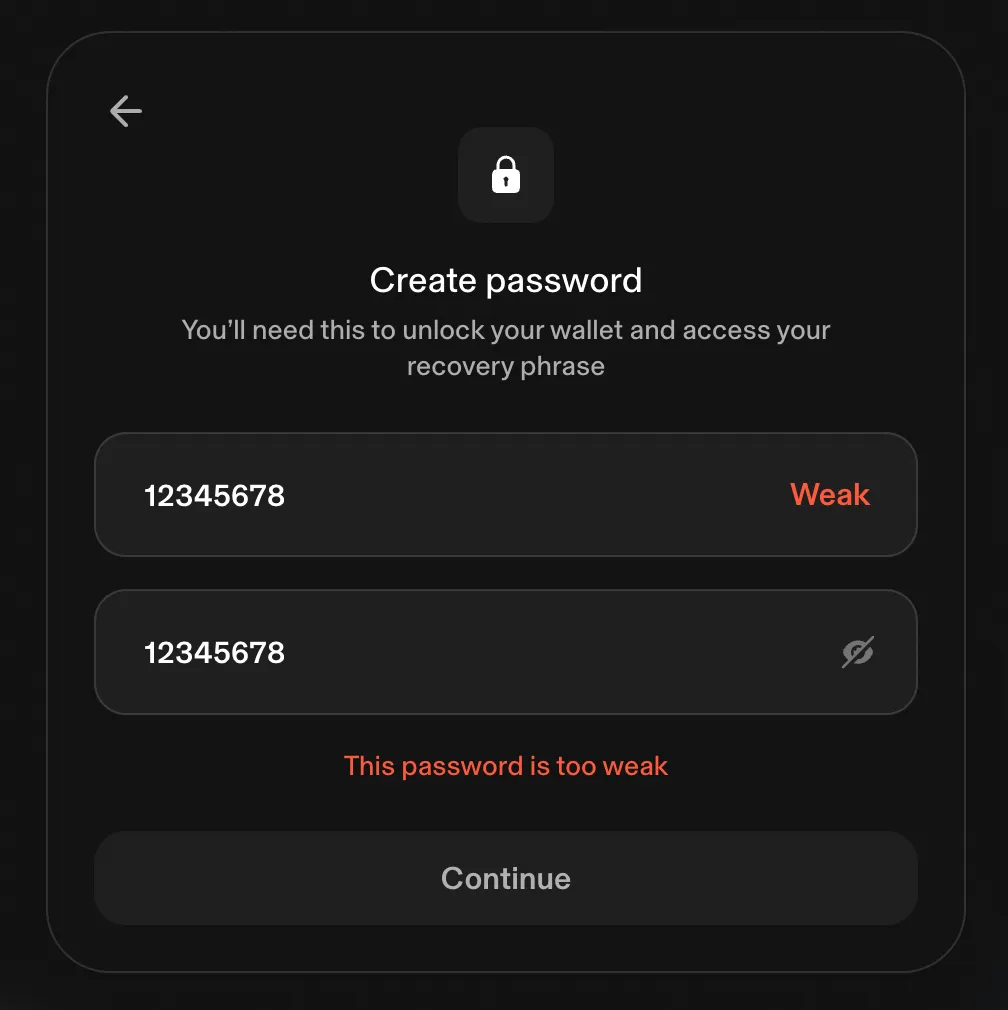
The password validation correctly rejects trivial passwords that are at least 8 characters long. The validation message is "This password is too weak".
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots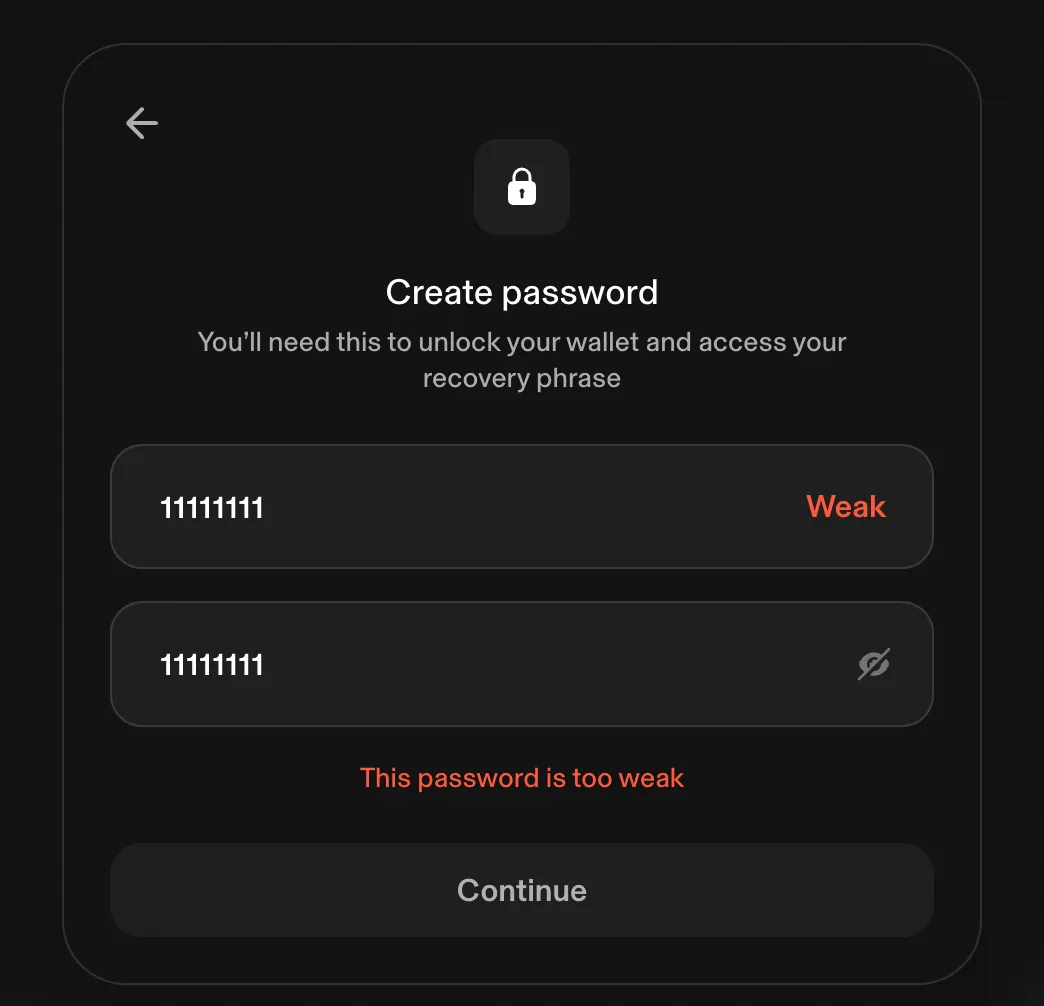
 Last updated on Sep 3, 2026Report an issue with this check
-
- Seed phrase access warning1.8 / 1.8Description
Warns users of the risk before allowing access to seed phrases or private keys.
-
The risks of sharing the recovery phrase are communicated clearly on the screen, including not sharing it, viewing it in private, and not entering it on any websites.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot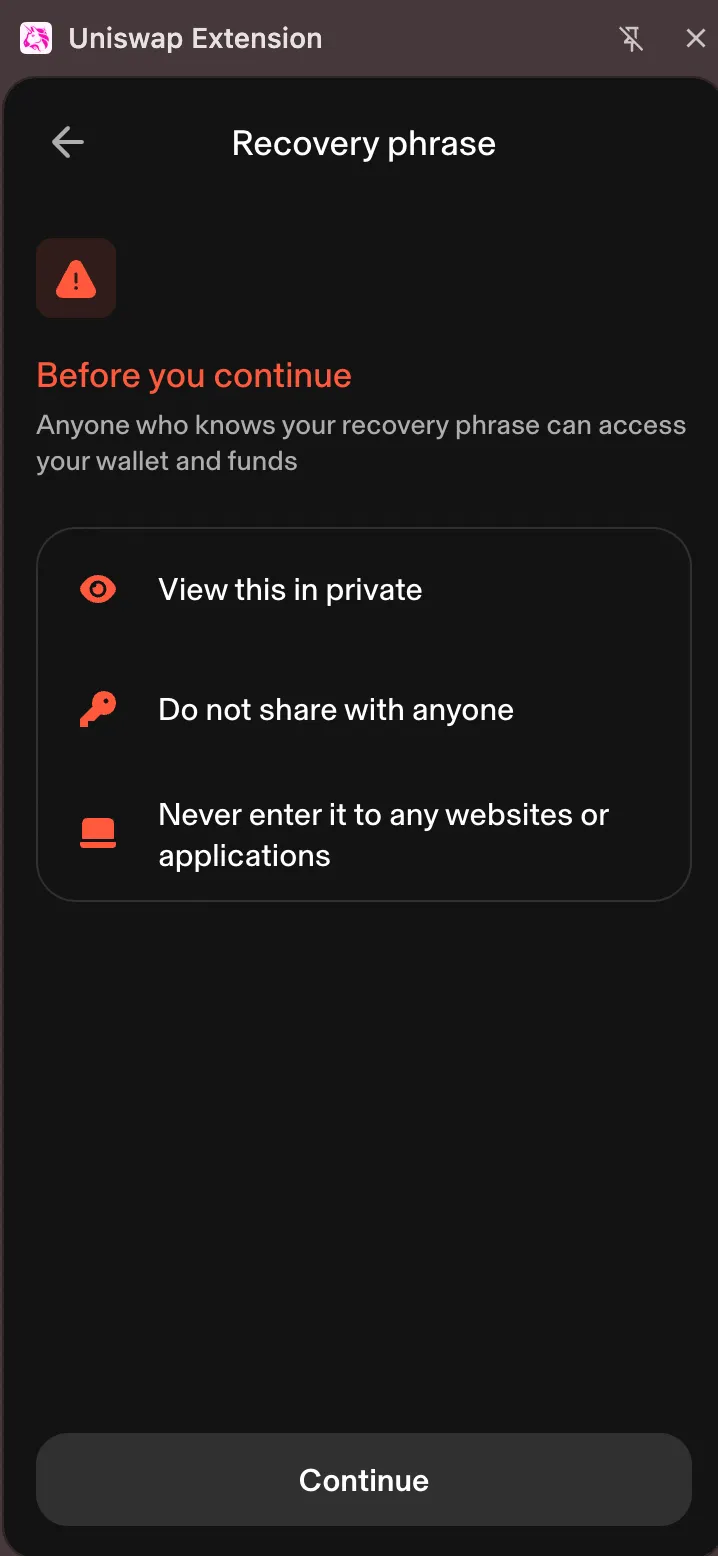 Last updated on Sep 3, 2026Report an issue with this check
-
- Clipboard seed phrase leak prevention0.0 / 1.8Description
Limits exposure of secrets by restricting or warning on copying seed phrases or taking screenshots.
-
The seed phrase was able to be copied with no time limit, warning about risks, or prevention of copying.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot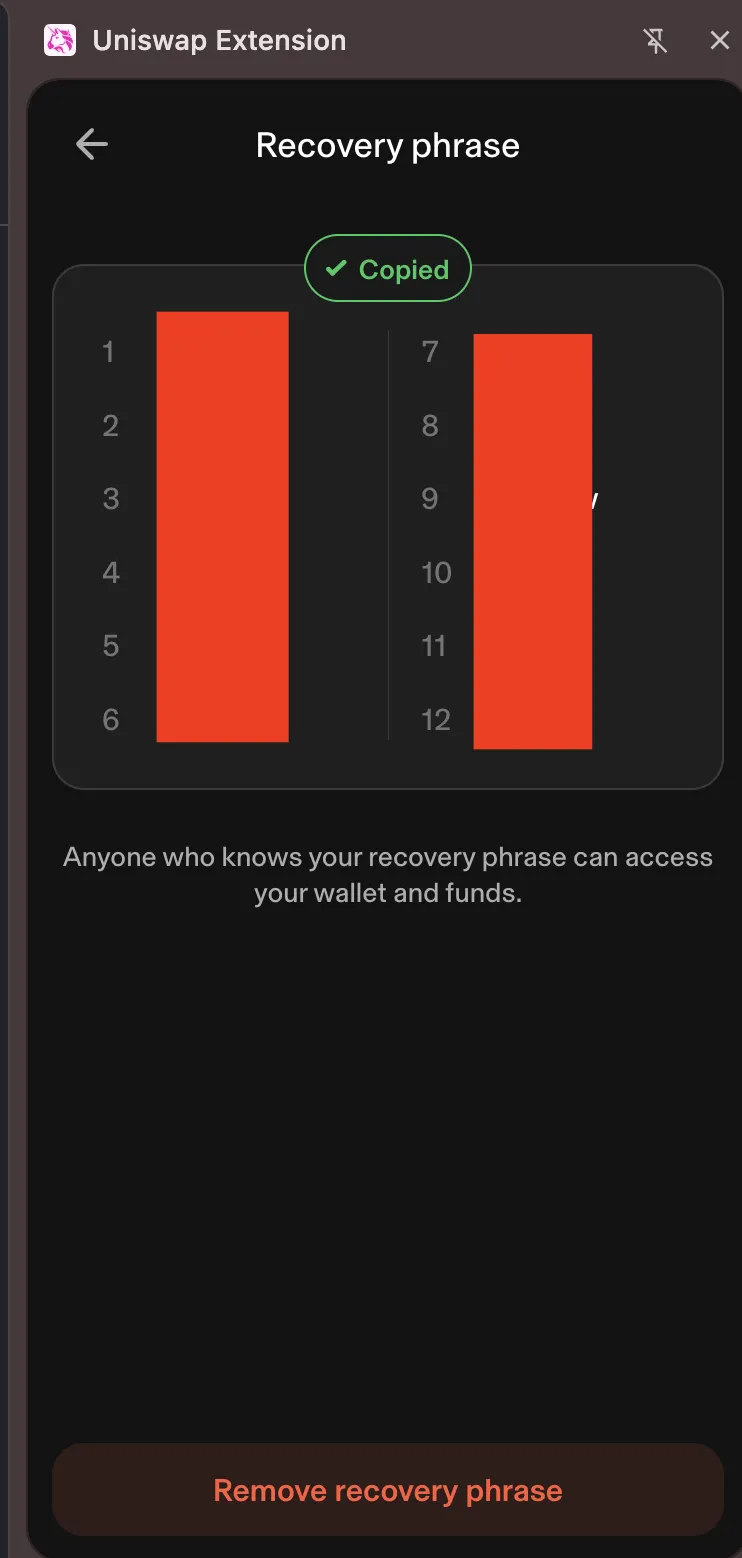 Last updated on Sep 3, 2026Report an issue with this check
-
Threat Prevention
- Malicious and poisoned address detection2.5 / 5.1Description
Prevents or alerts users about interactions with a known malicious address or a lookalike (poisoned) address.
-
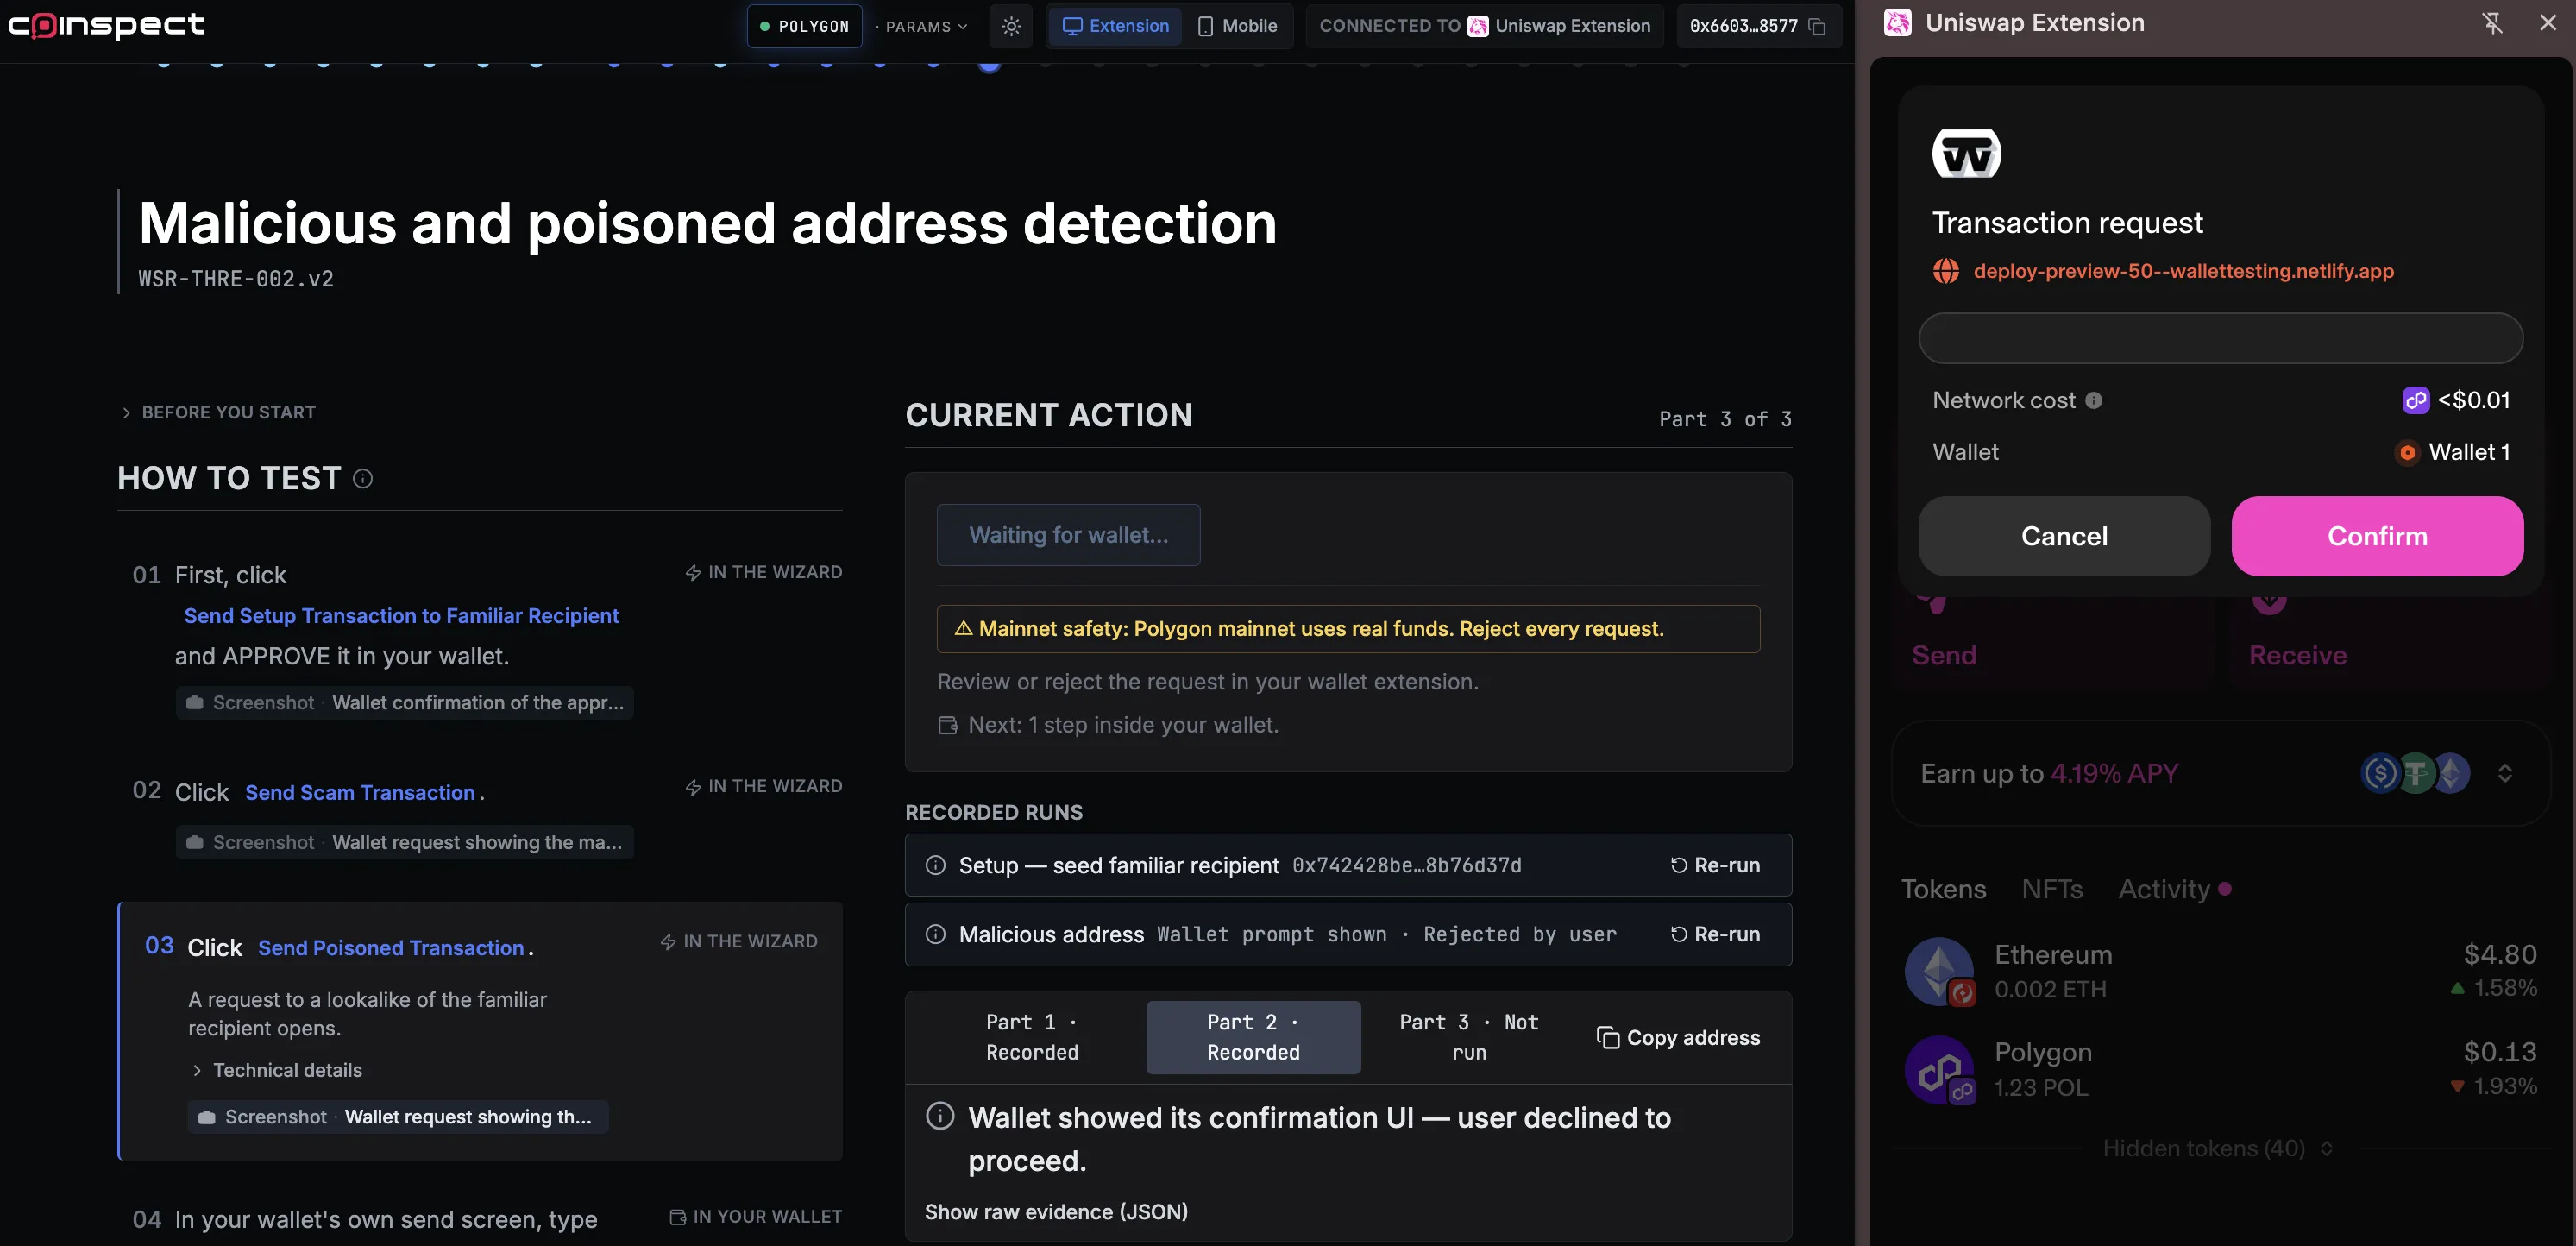
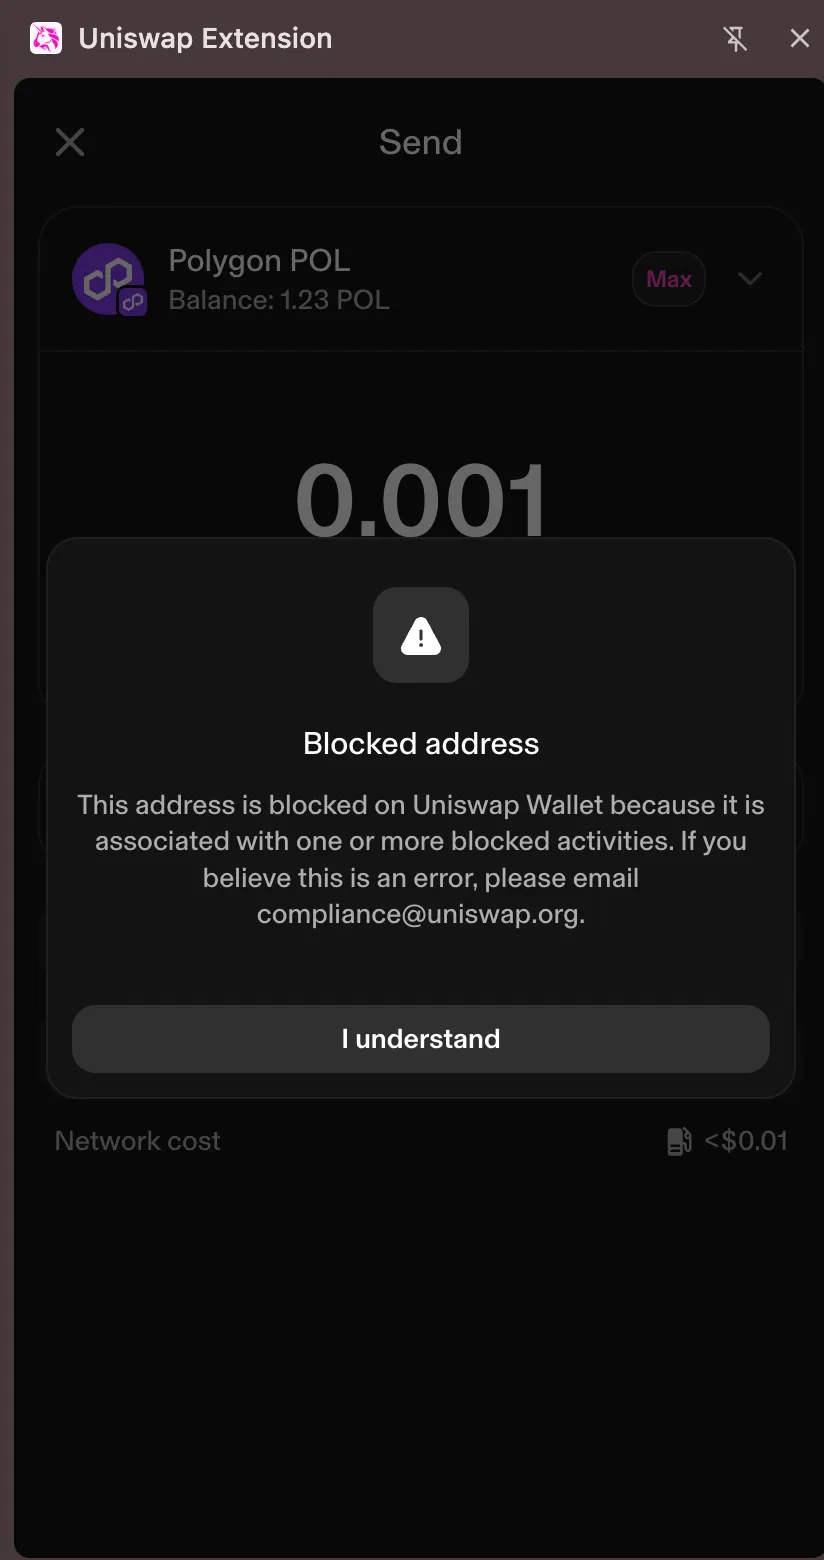
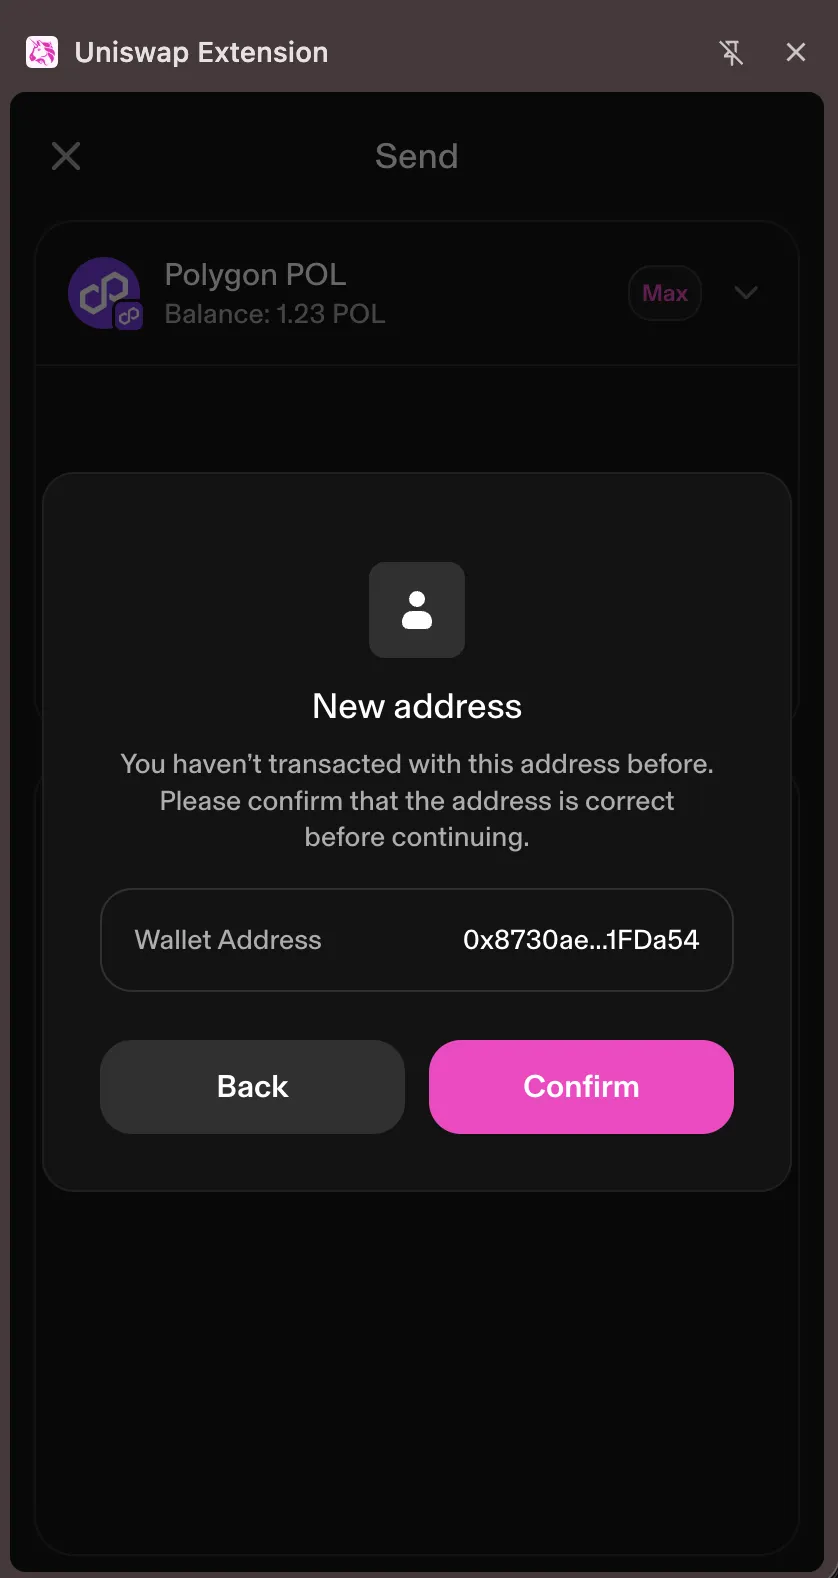
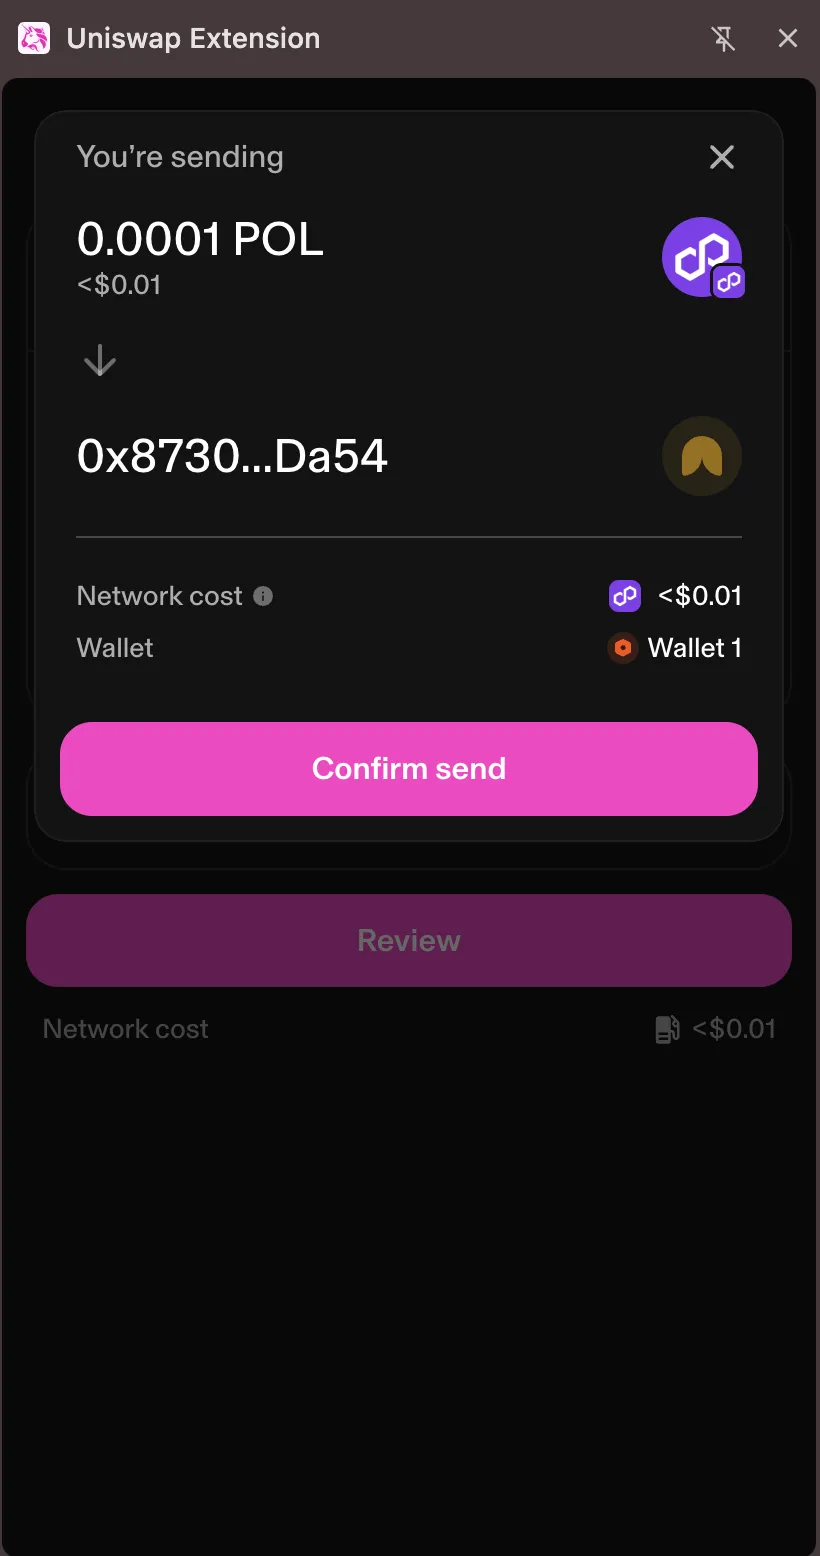
The wallet blocks/warns for the known malicious address (0x742428be...8b76d37d) on both manual and dApp entry, and warns with a generic 'New address' warning for the lookalike address (0x8730ae...1FDa54) on manual entry, but it does not warn for the lookalike address when supplied by a dApp.
— Verified by Sebastian Camia at Coinspect
Evidence · 5 screenshots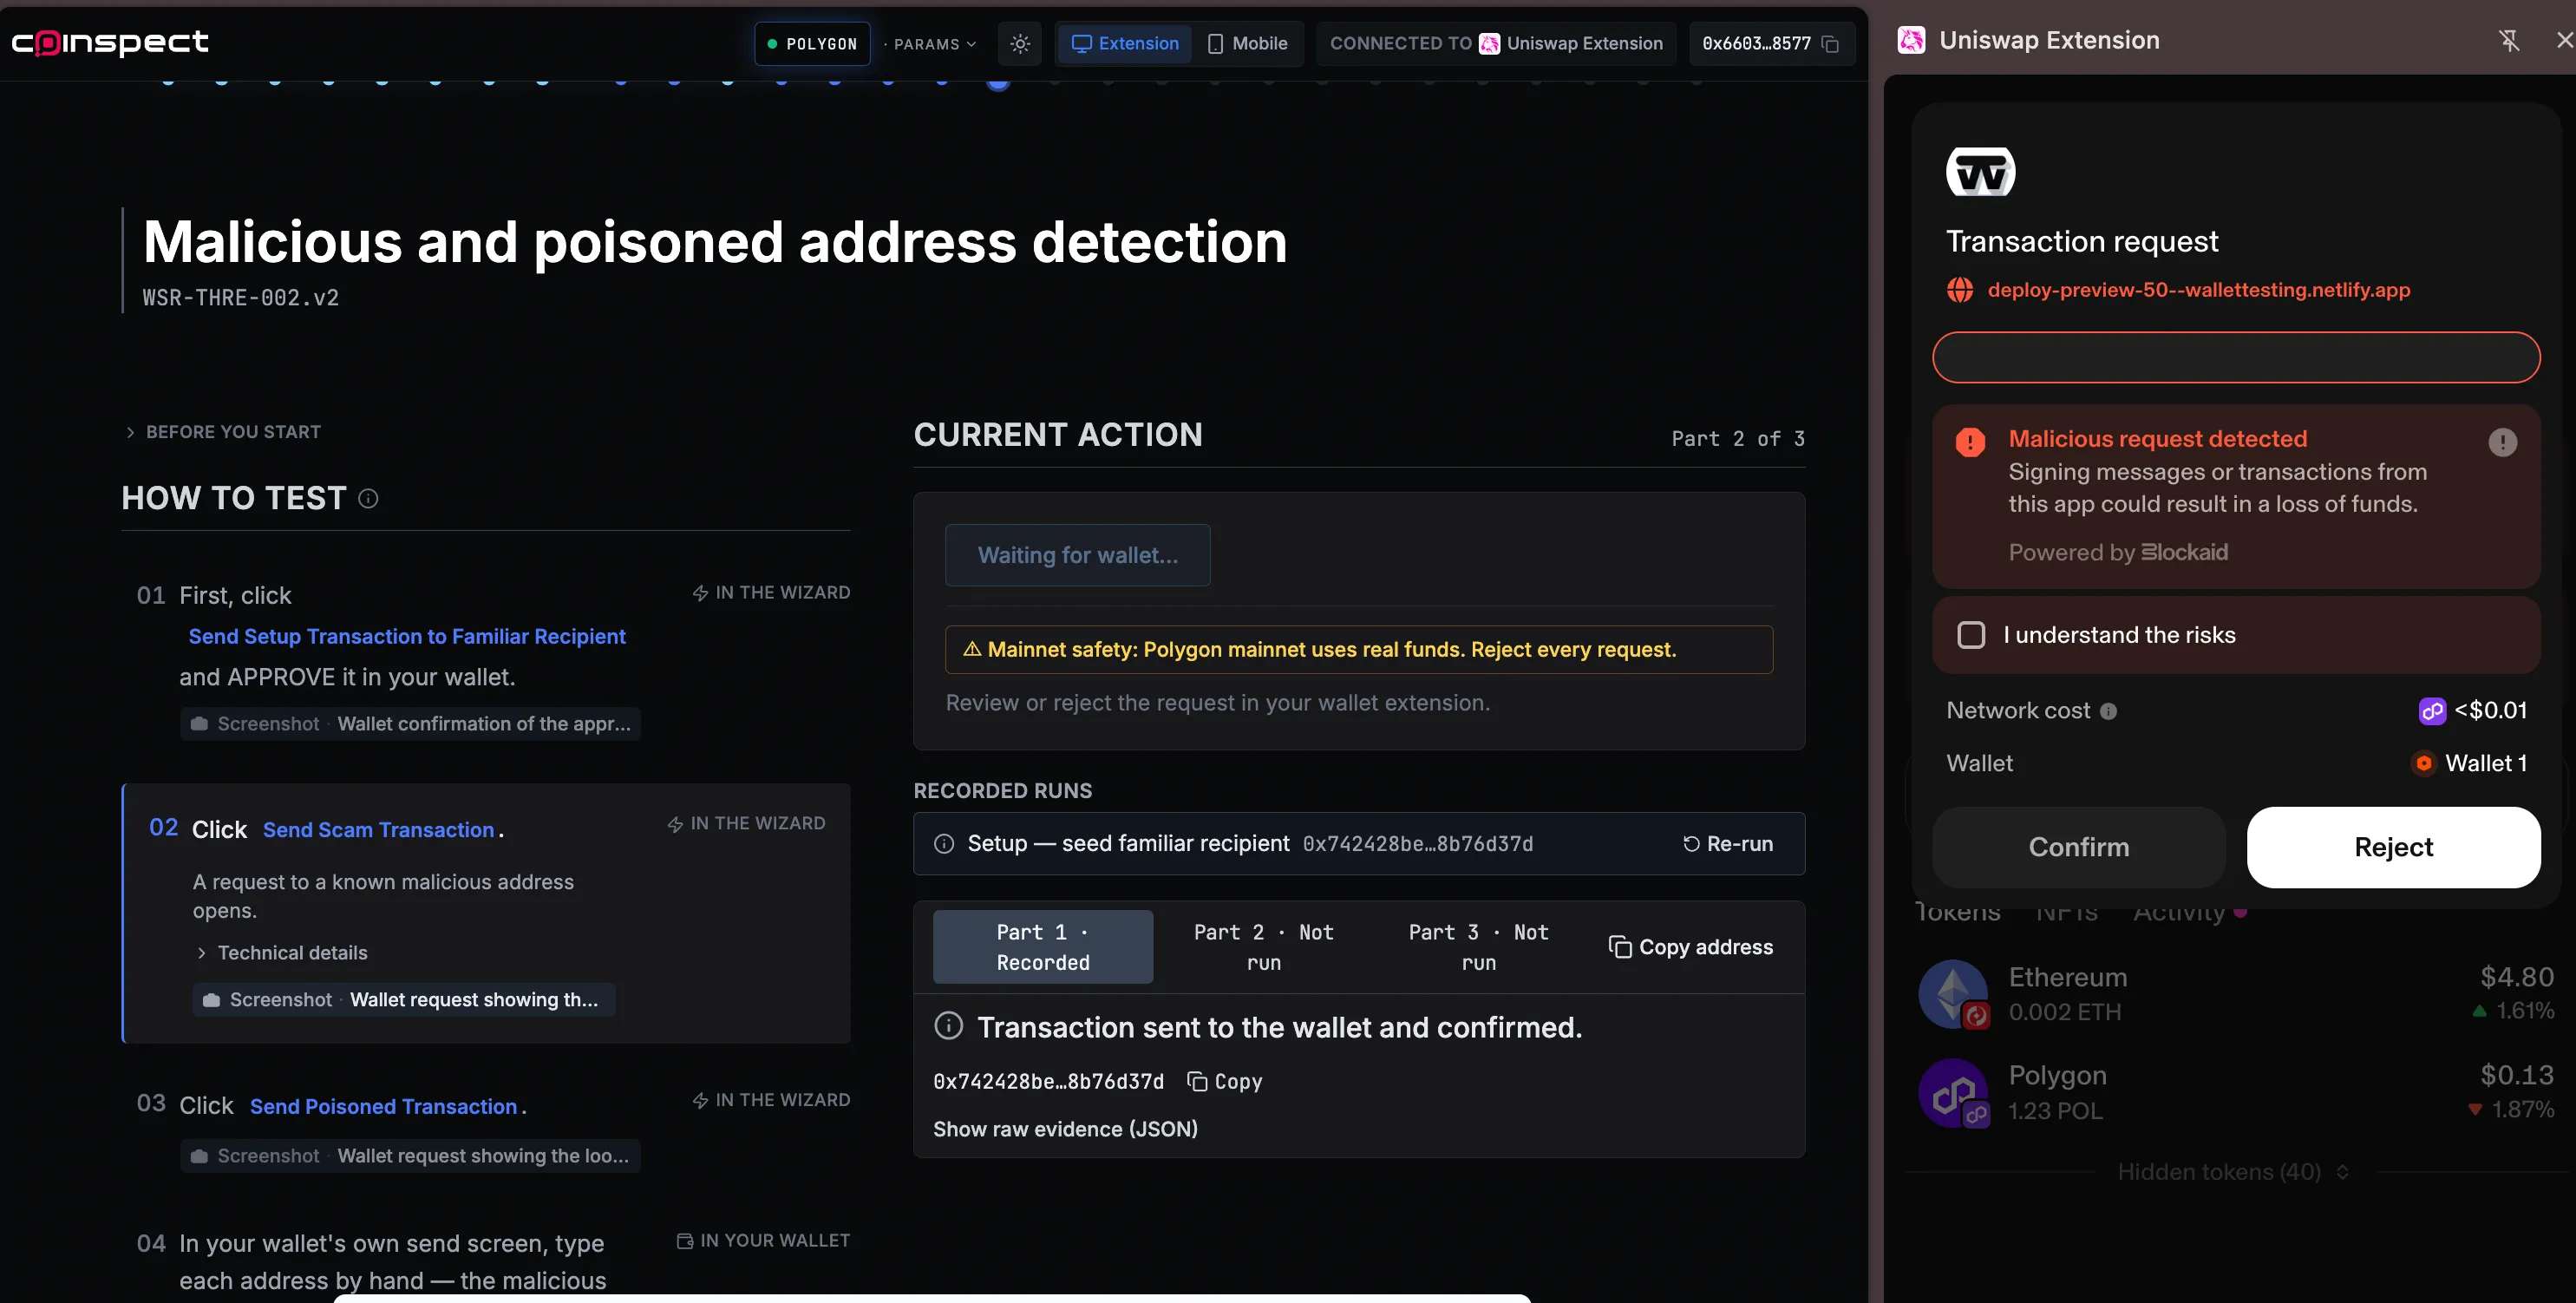
 Last updated on Sep 3, 2026Report an issue with this check
-
- Phishing dApp detection5.1 / 5.1Description
Prevents or alerts users about interactions with a known malicious URL.
-
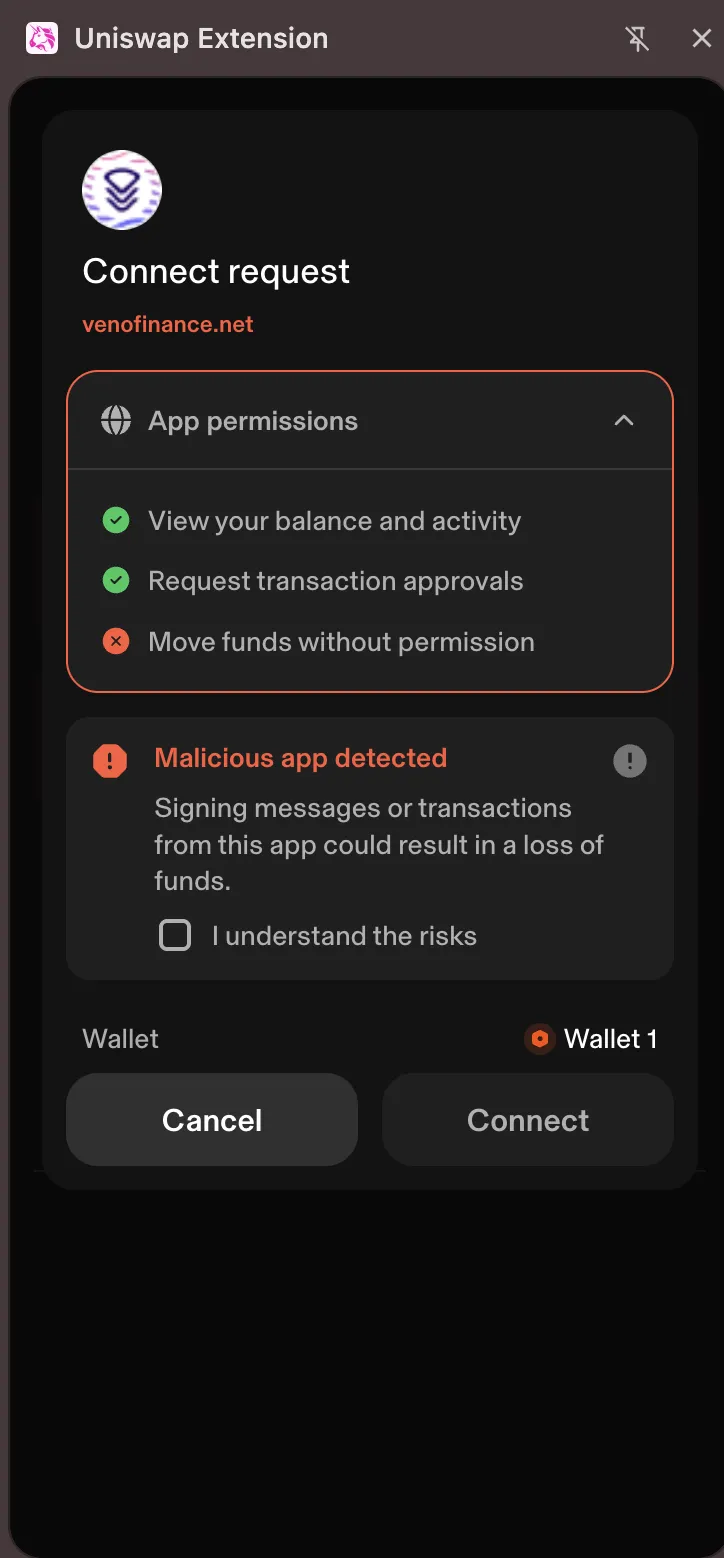
The wallet warns the user about malicious apps, as expected. Hyperliqidrop.com and venofinance.net are detected as malicious apps.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots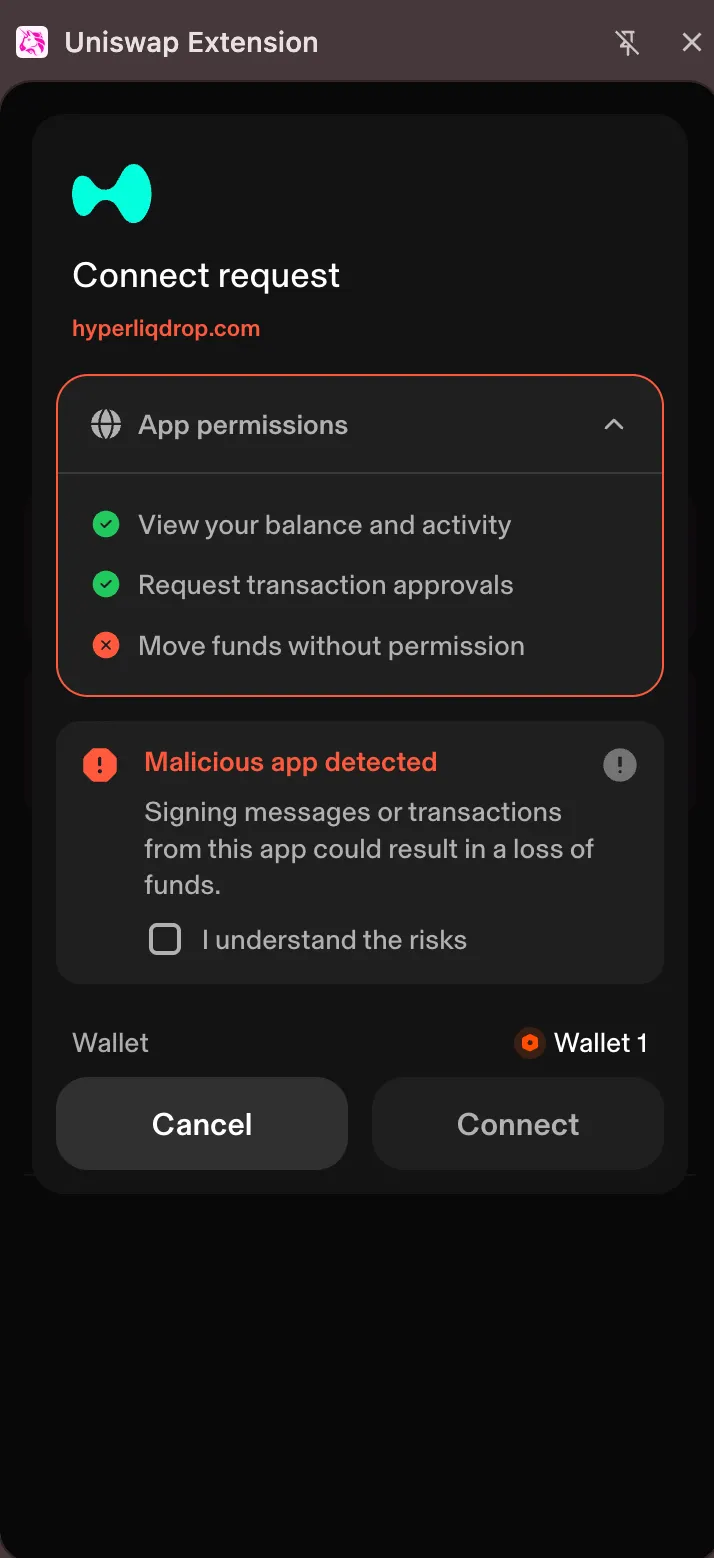
 Last updated on Sep 3, 2026Report an issue with this check
-
- Trusted dApp detection0.0 / 3.3Description
Informs users when interacting with a trusted dApp URL.
-
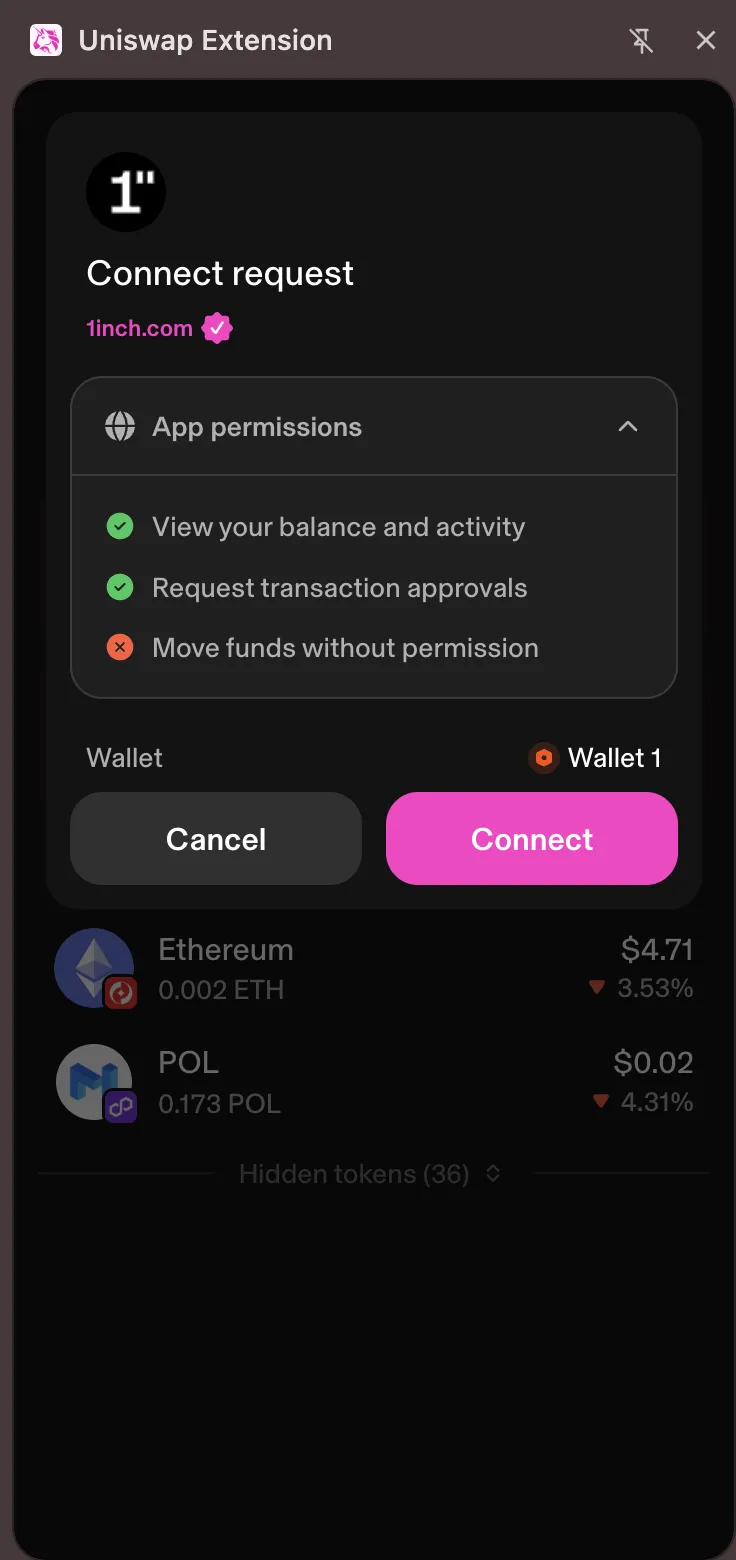
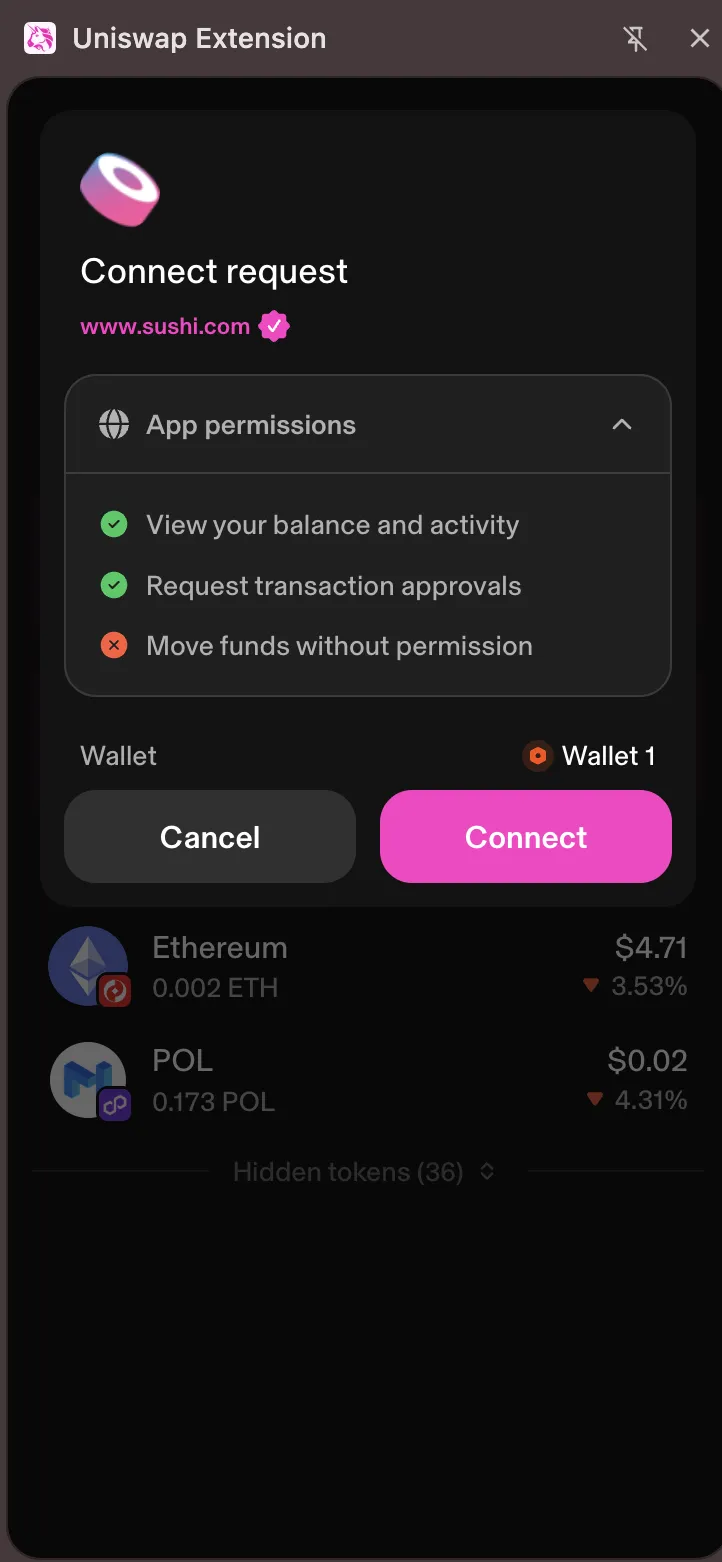
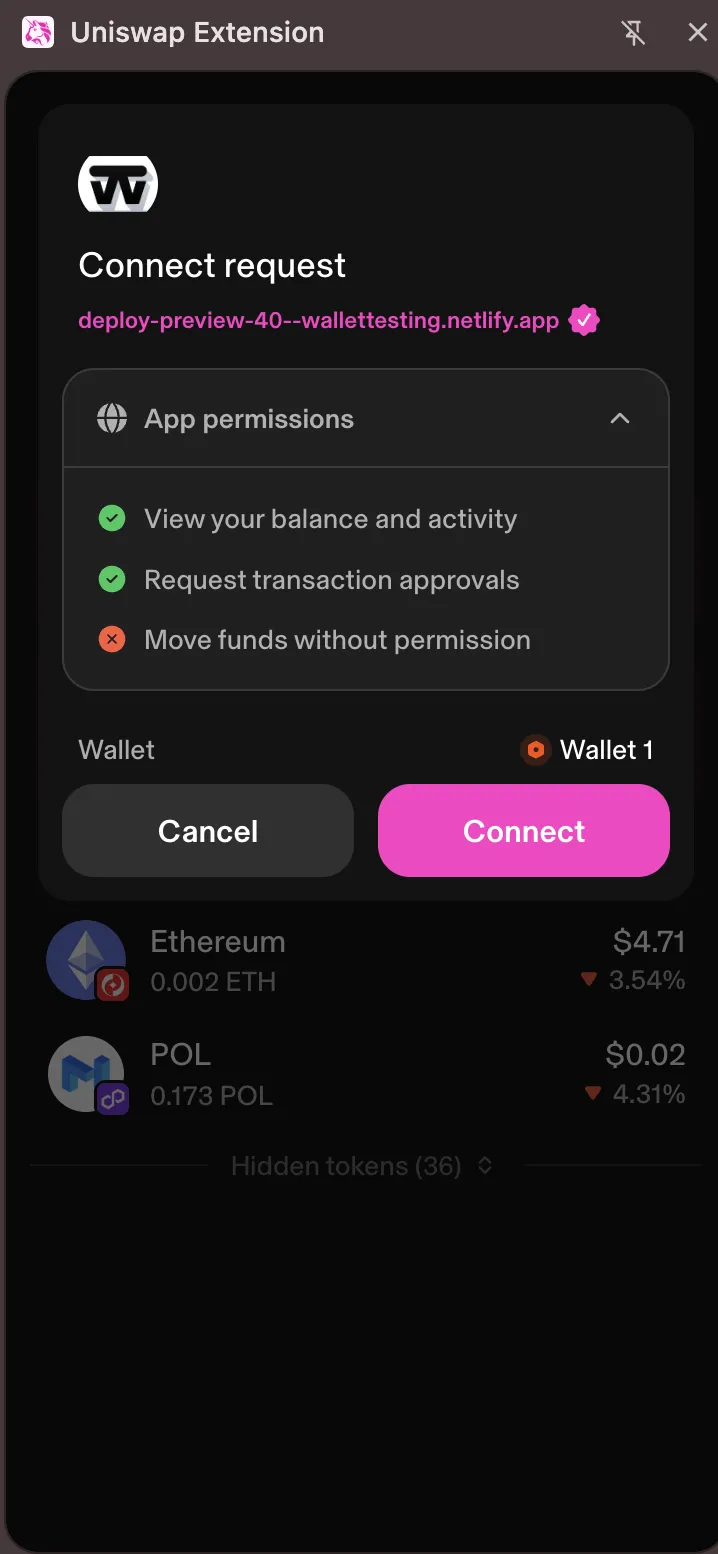
Unknown dApps also have a checkmark, so verified dApps are not clearly distinguished from unknown ones.
— Verified by Sebastian Camia at Coinspect
Evidence · 4 screenshots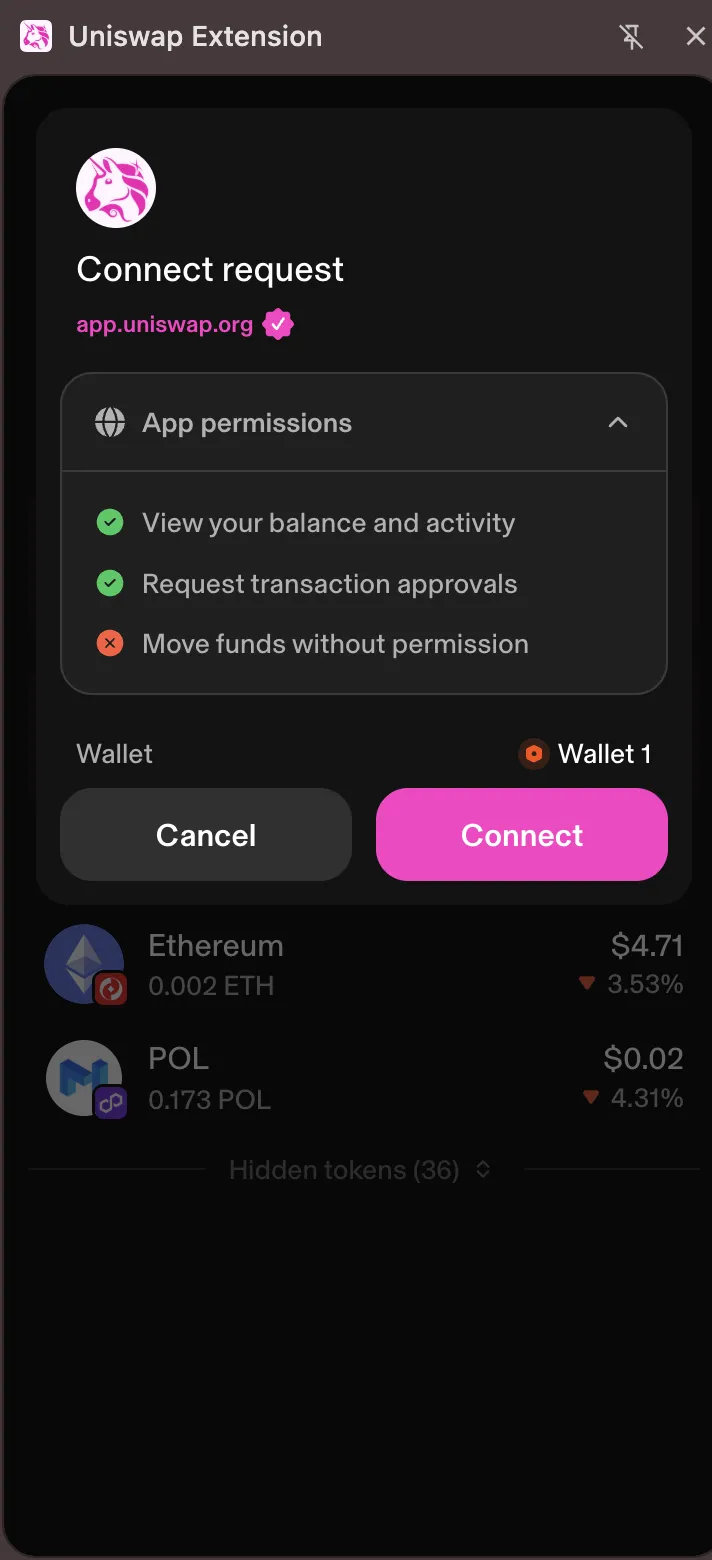
 Last updated on Sep 3, 2026Report an issue with this check
-
- Unknown address detection2.8 / 2.8Description
Warns users when interacting with an unknown address.
-
The wallet warns about the new address when the transaction is done manually. However, it does not do so when the transaction comes from a dApp.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots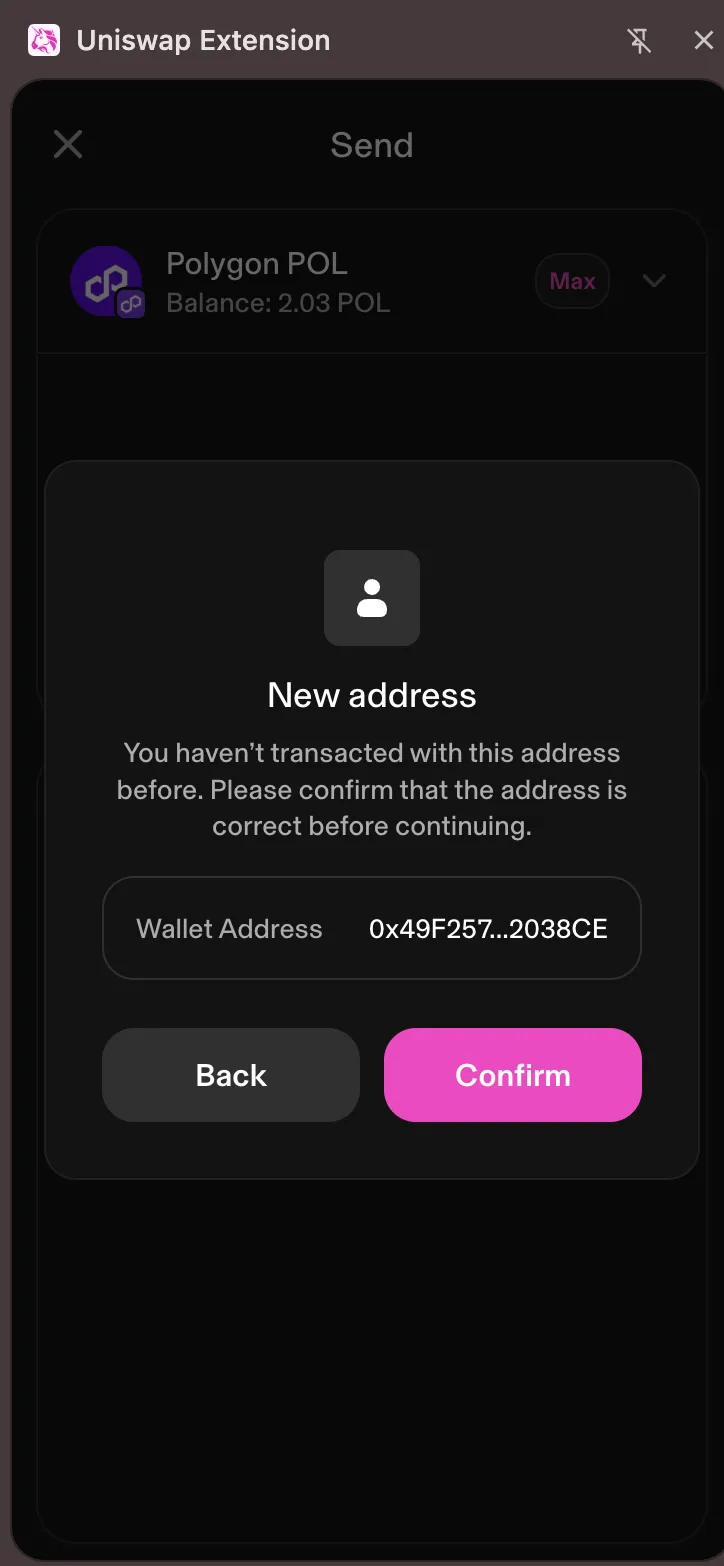 Last updated on Sep 3, 2026Report an issue with this check
-
- Full dApp URL display1.5 / 1.5Description
Clearly displays the full dApp URL in the connection prompt.
-
The full dApp origin URL is displayed without truncation in the connection dialog.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot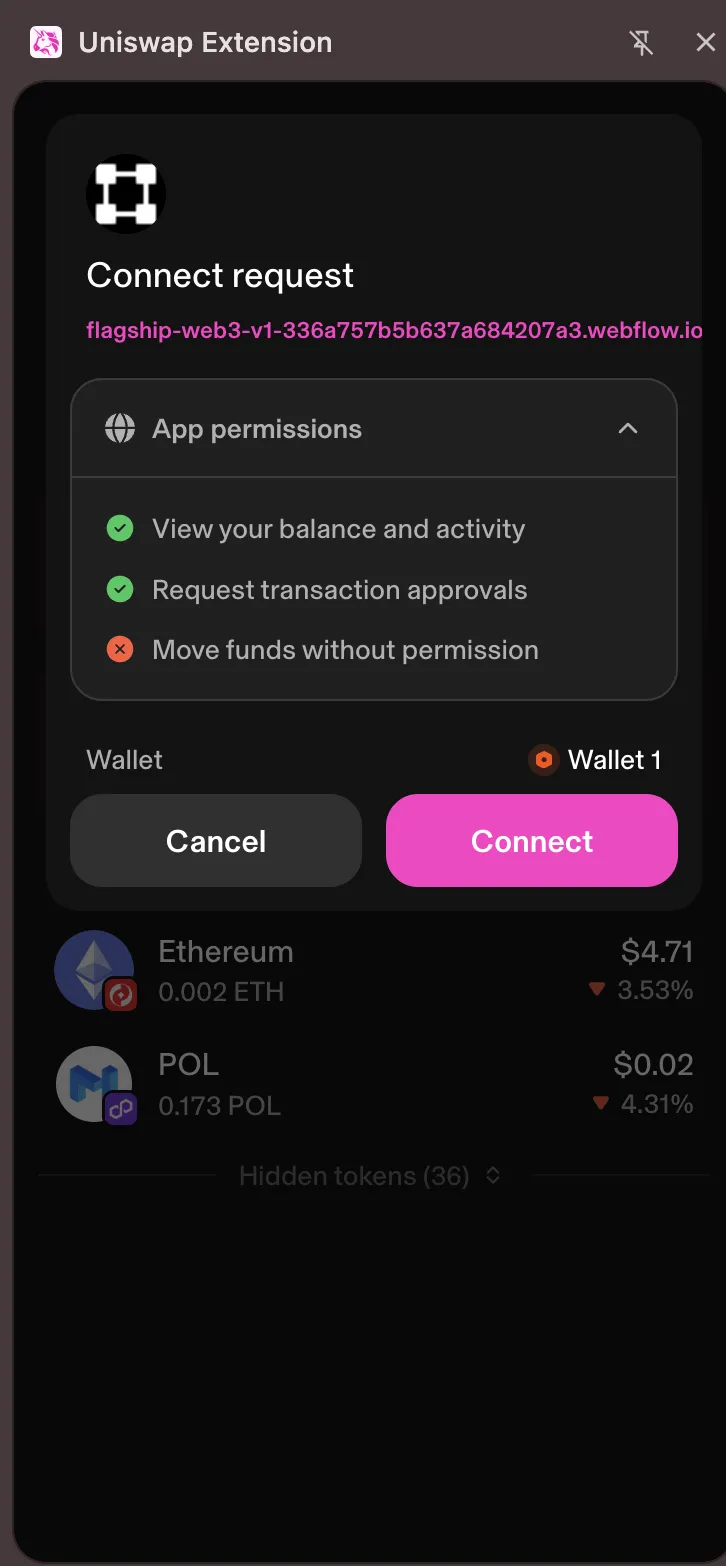 Last updated on Sep 3, 2026Report an issue with this check
-
- Malicious or spam token filtering1.3 / 1.3Description
Hides malicious tokens and NFTs by default.
-
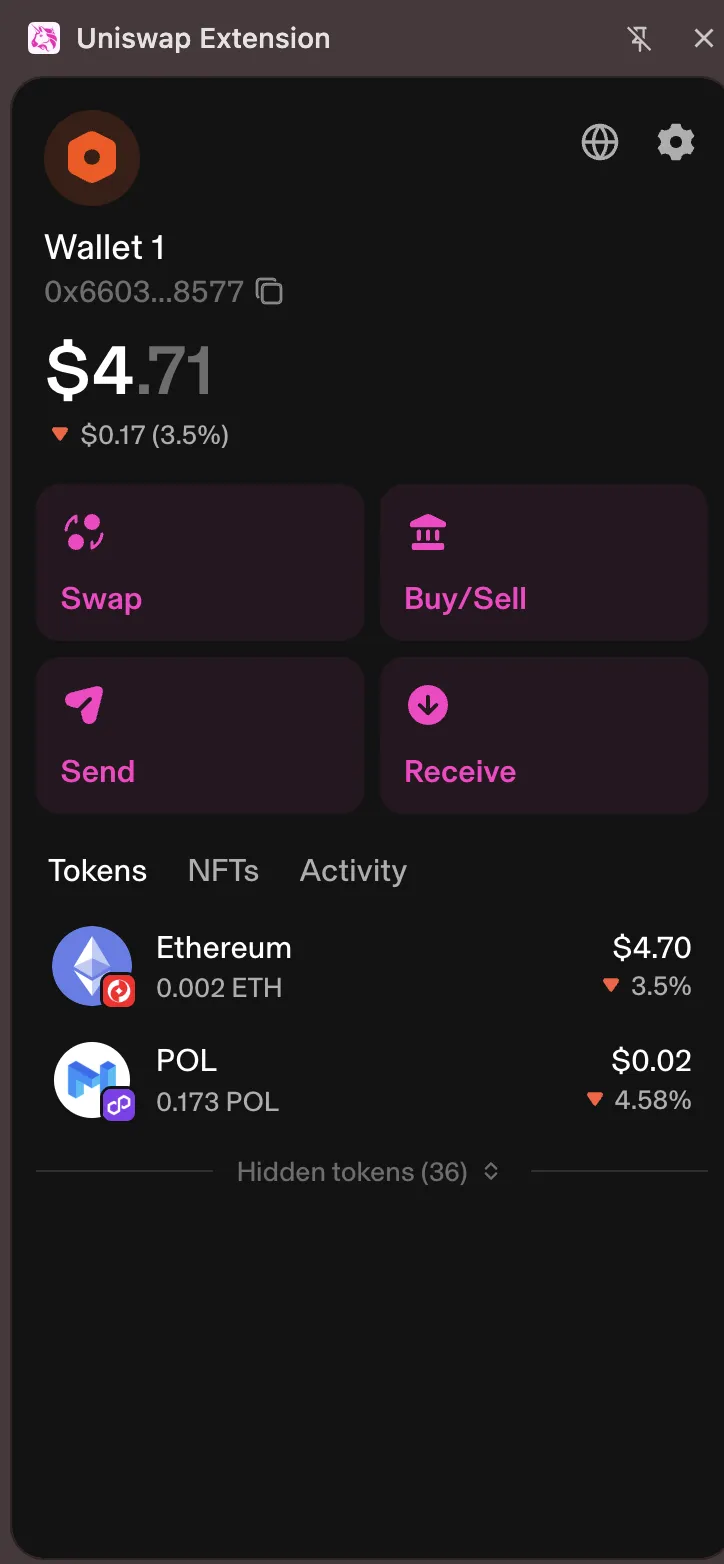
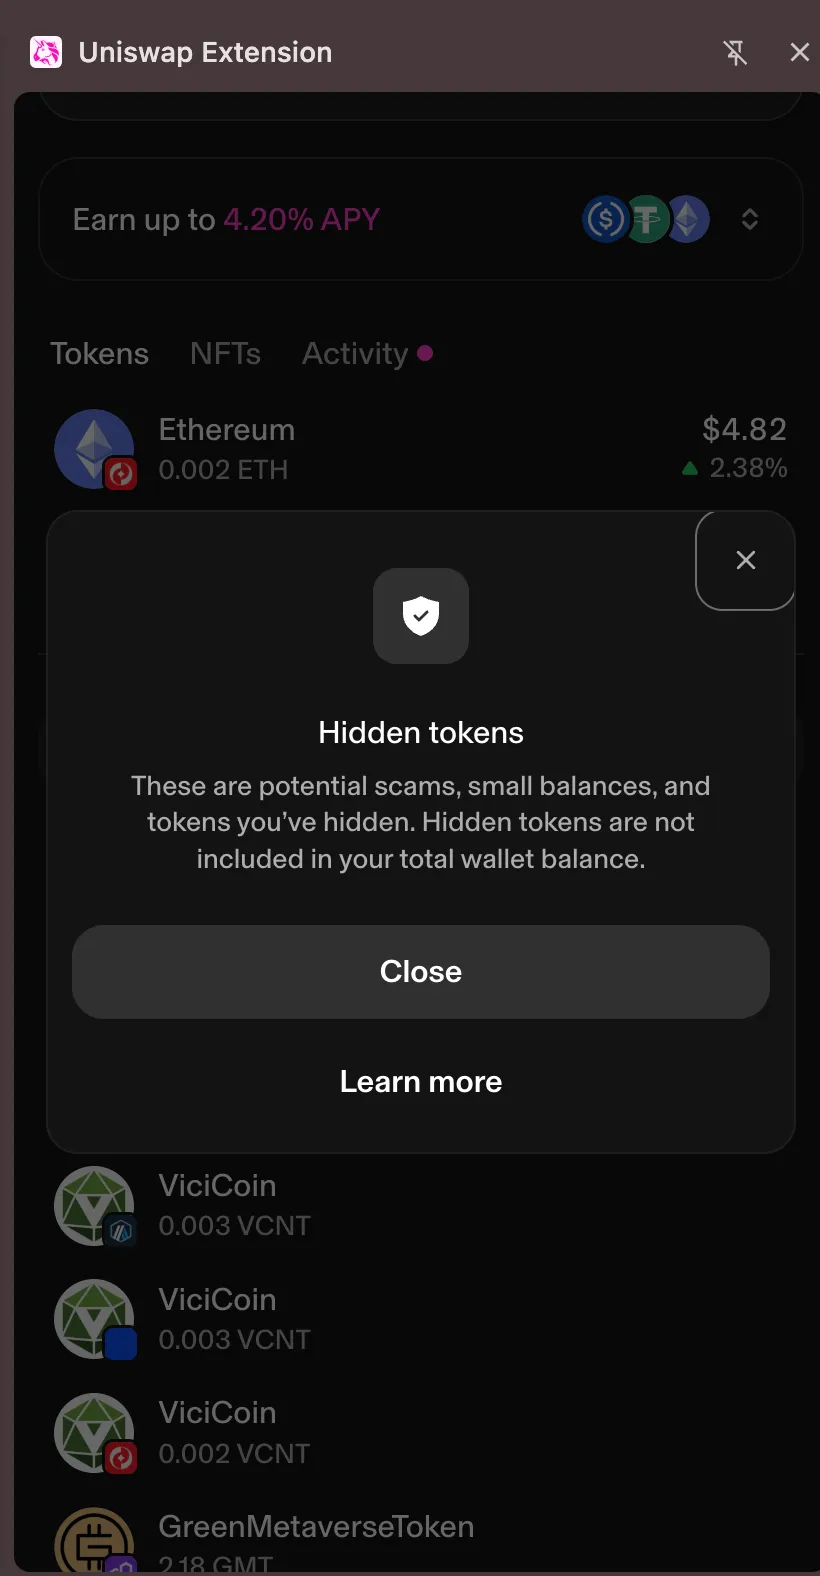
Spam tokens and NFTs are hidden by default as indicated by the "Hidden tokens" section.
— Verified by Sebastian Camia at Coinspect
Evidence · 3 screenshots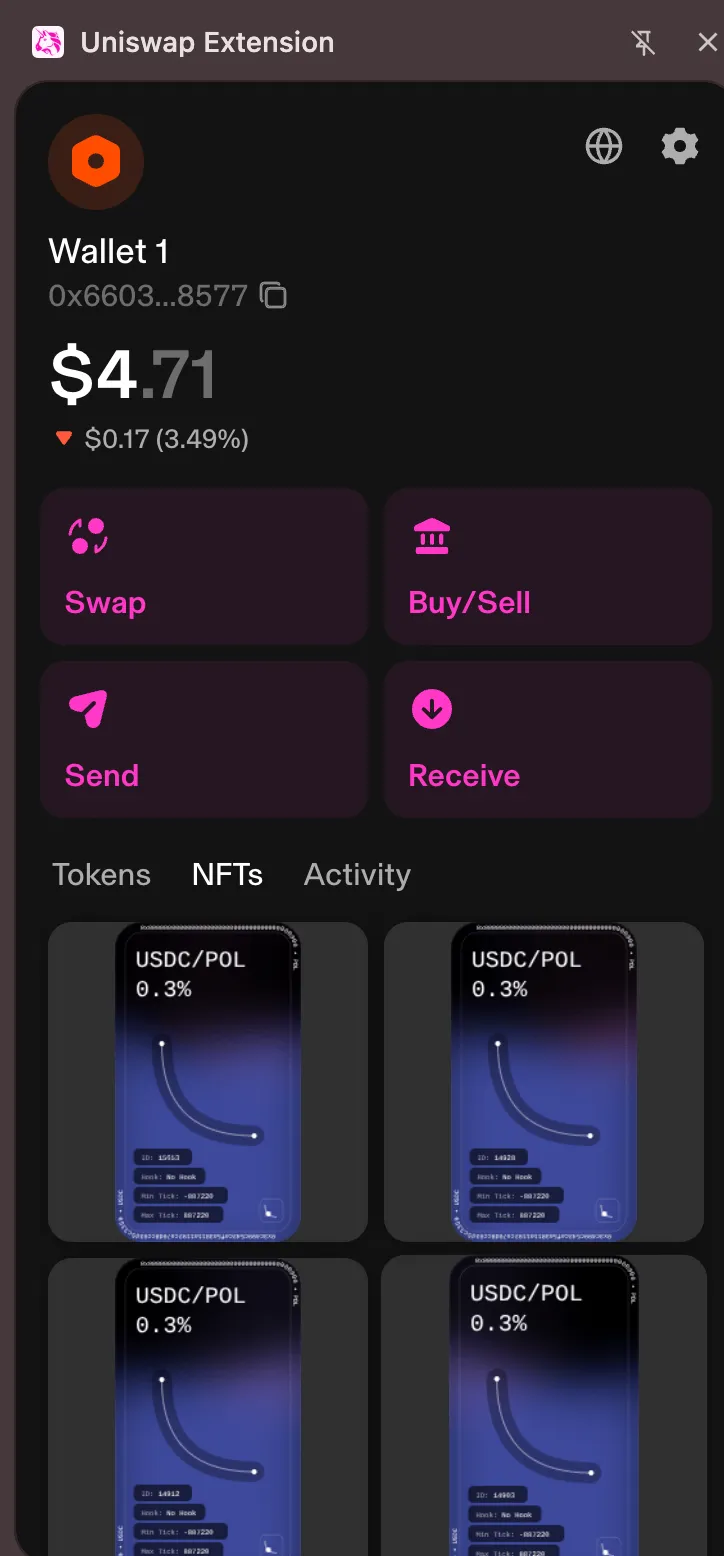
 Last updated on Sep 3, 2026Report an issue with this check
-
- dApp access disclosure dialog1.0 / 1.0Description
Discloses the dApp's read access to the user's account and its ability to request signatures on connection.
-
The connection dialog clearly states that the dApp will be able to "View your balance and activity" and "Request transaction approvals", which matches the acceptance criteria.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot Last updated on Sep 3, 2026Report an issue with this check -
This ranking is for informational purposes only. It should not be relied on to provide legal, tax, financial, investment, or other types of advice. Coinspect does not guarantee or warrant the accuracy, completeness, timeliness, suitability, or validity of the information provided and will not be responsible for any claim attributable to reliance on errors, omissions, or other inaccuracies of any part of such information.