
 Brave

Brave
- Chrome
- v1.84.141
66.4
dApp Permissions
- User confirmation before processing requests8.7 / 8.7Description
Requires user confirmation before processing requests from dApps for specific RPC methods.
-
The wallet requires user confirmation for all the RPC endpoints.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot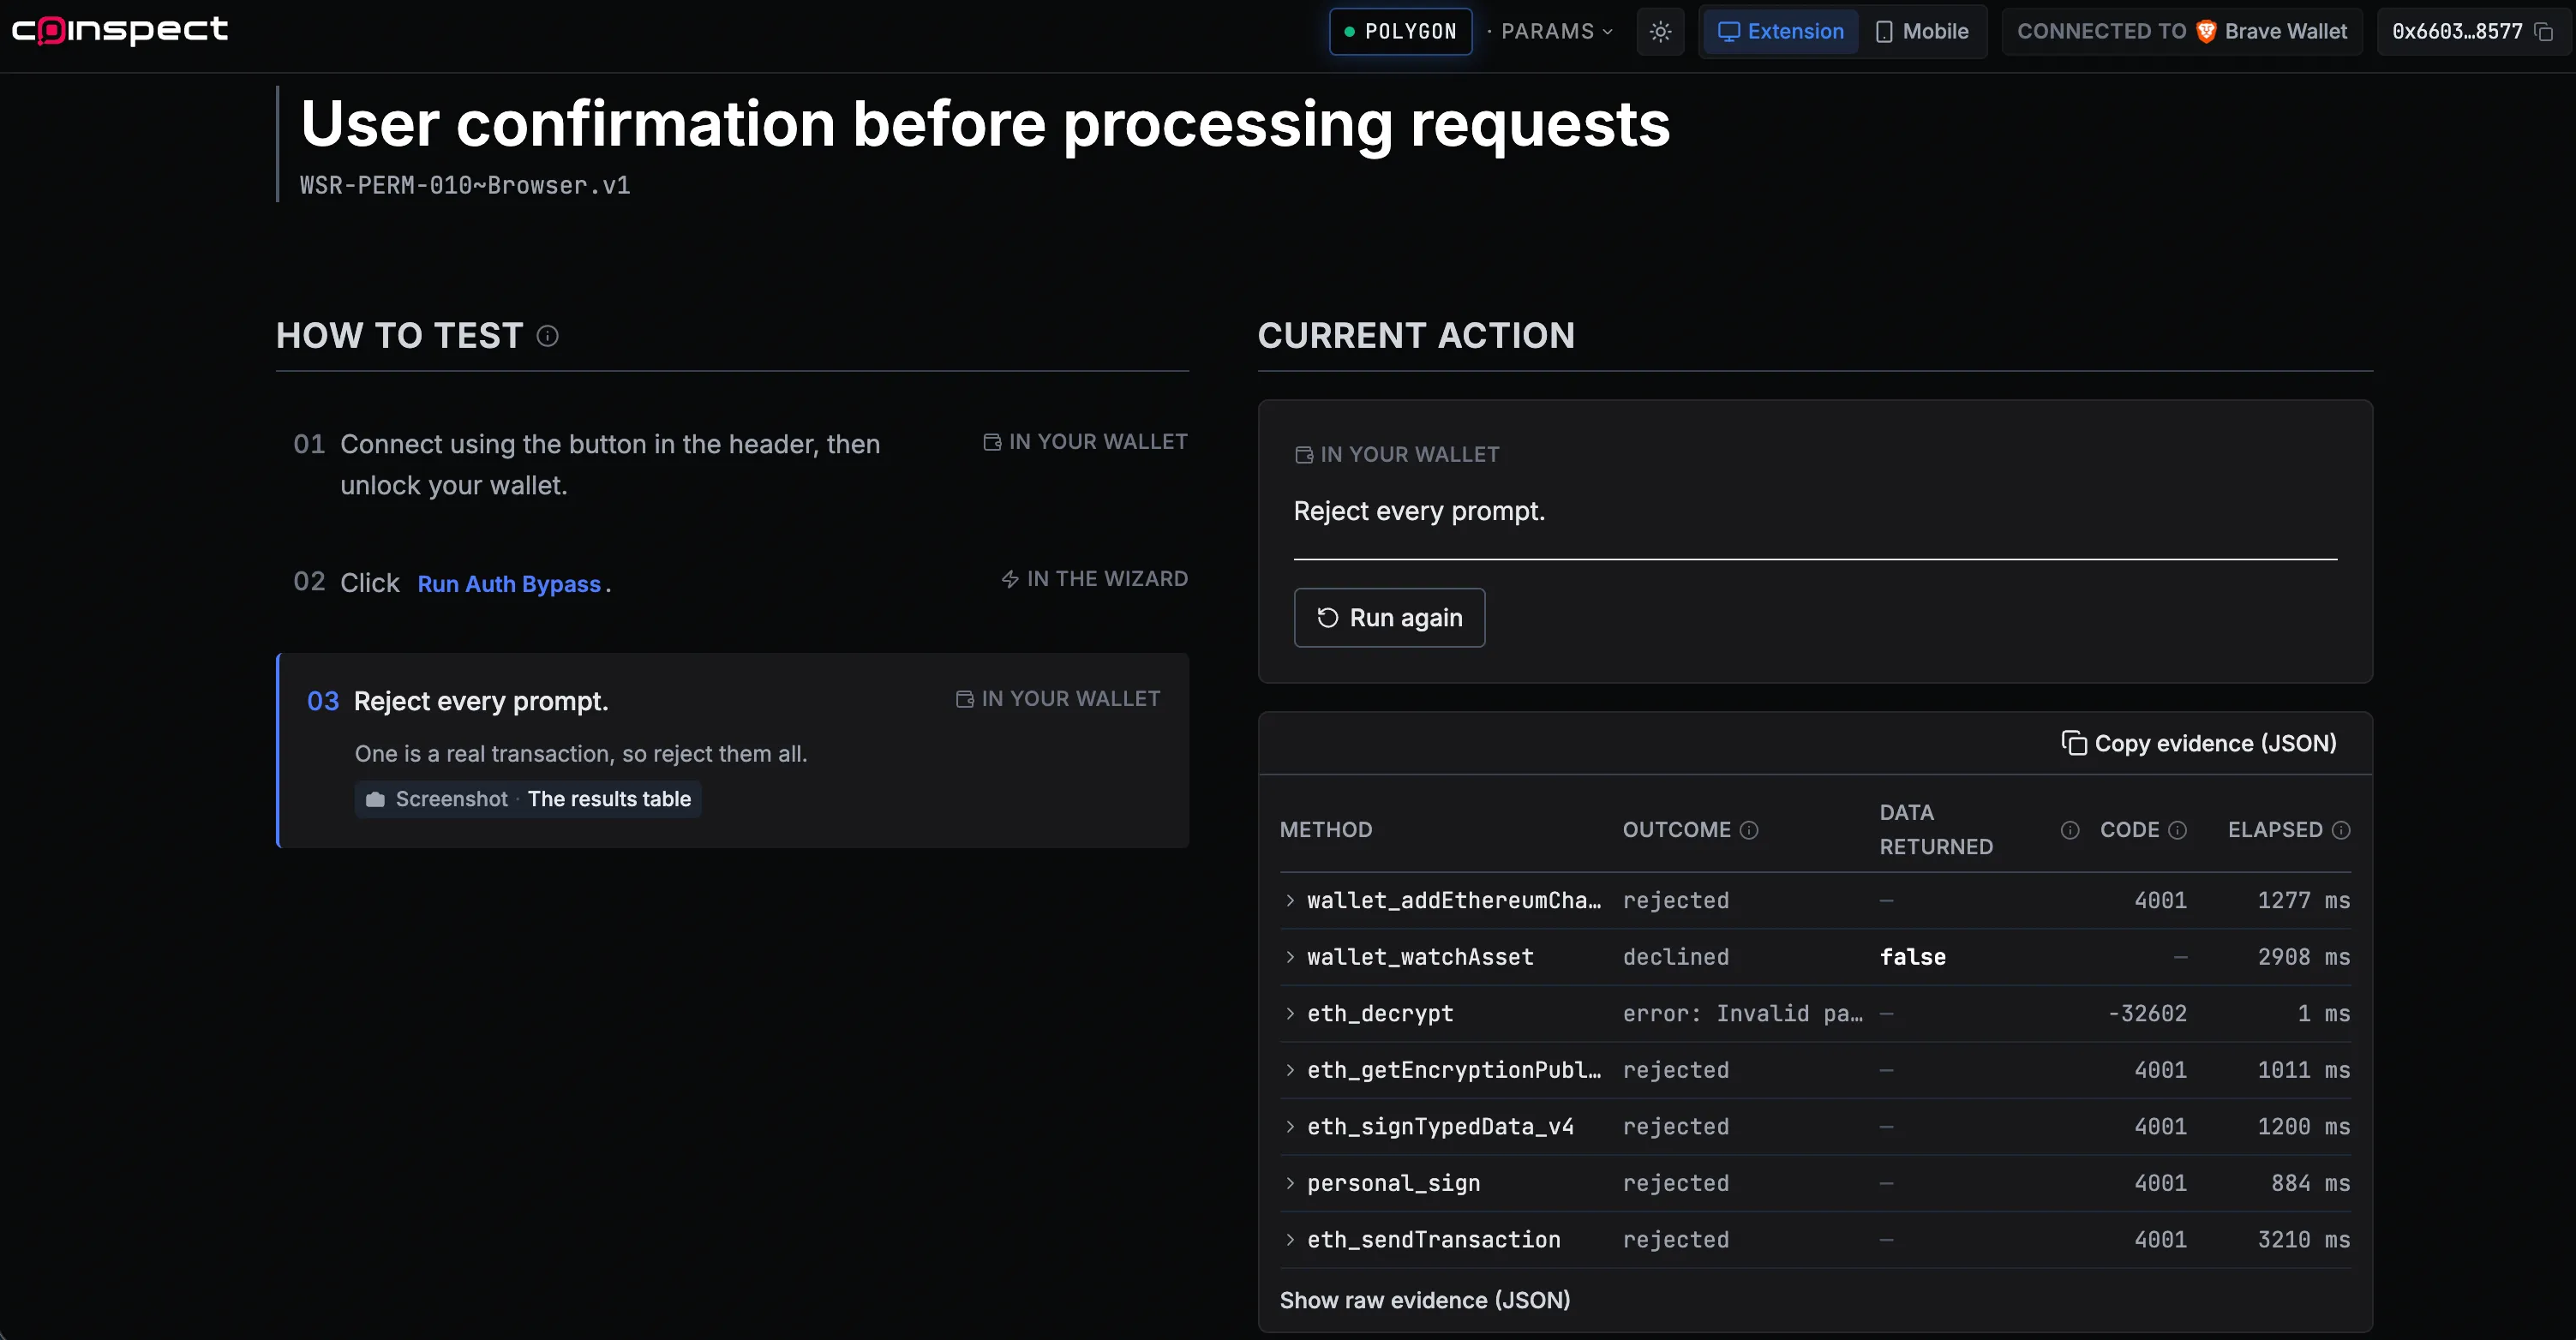 Last updated on Sep 3, 2026Report an issue with this check
-
- User consent for dApp access7.7 / 7.7Description
Requires user approval before granting dApp access to specific RPC methods.
-
The wallet rejects all dApp requests to privileged RPC methods with an unauthorized error (code 4100) when the wallet is not connected, and no account information is leaked; eth_accounts returns an empty array.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot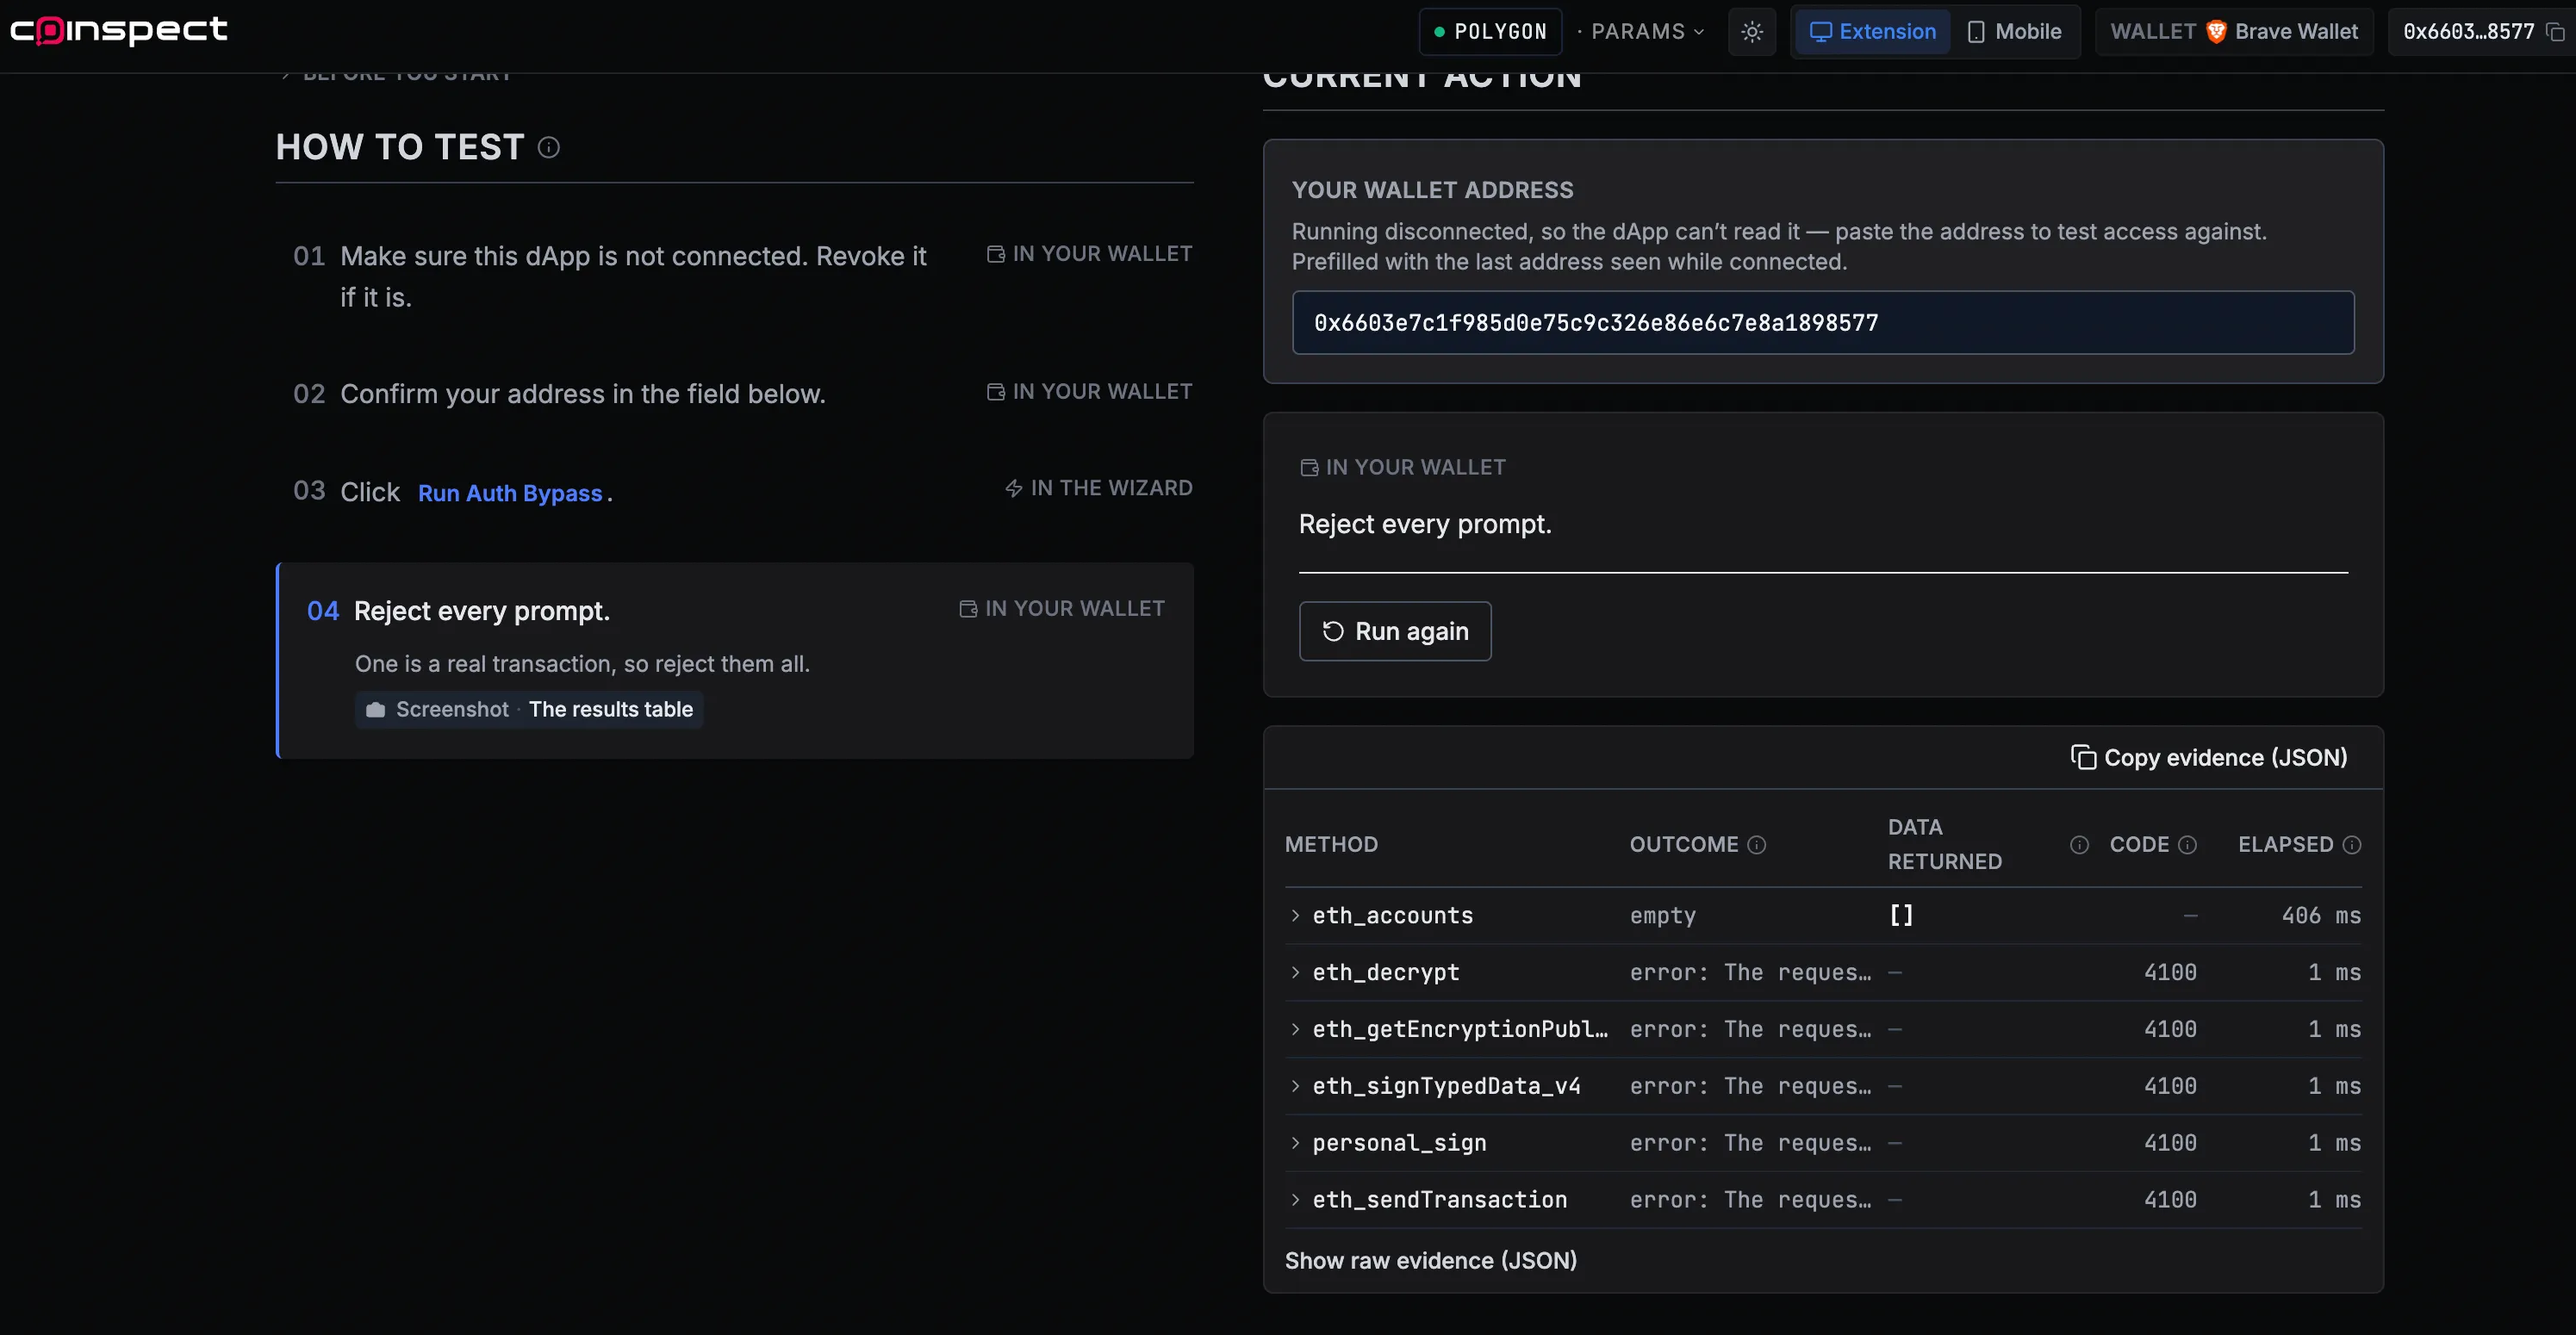 Last updated on Sep 3, 2026Report an issue with this check
-
- Wallet unlock before requests5.6 / 5.6Description
Requires users to unlock it before processing dApp requests when in a locked state.
-
The wallet did not process any of the six RPC requests while locked: wallet_addEthereumChain and wallet_watchAsset returned no response, and eth_decrypt, eth_getEncryptionPublicKey, eth_signTypedData_v4, personal_sign, and eth_sendTransaction all returned error code 4100 (unauthorized). No sensitive data was returned.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot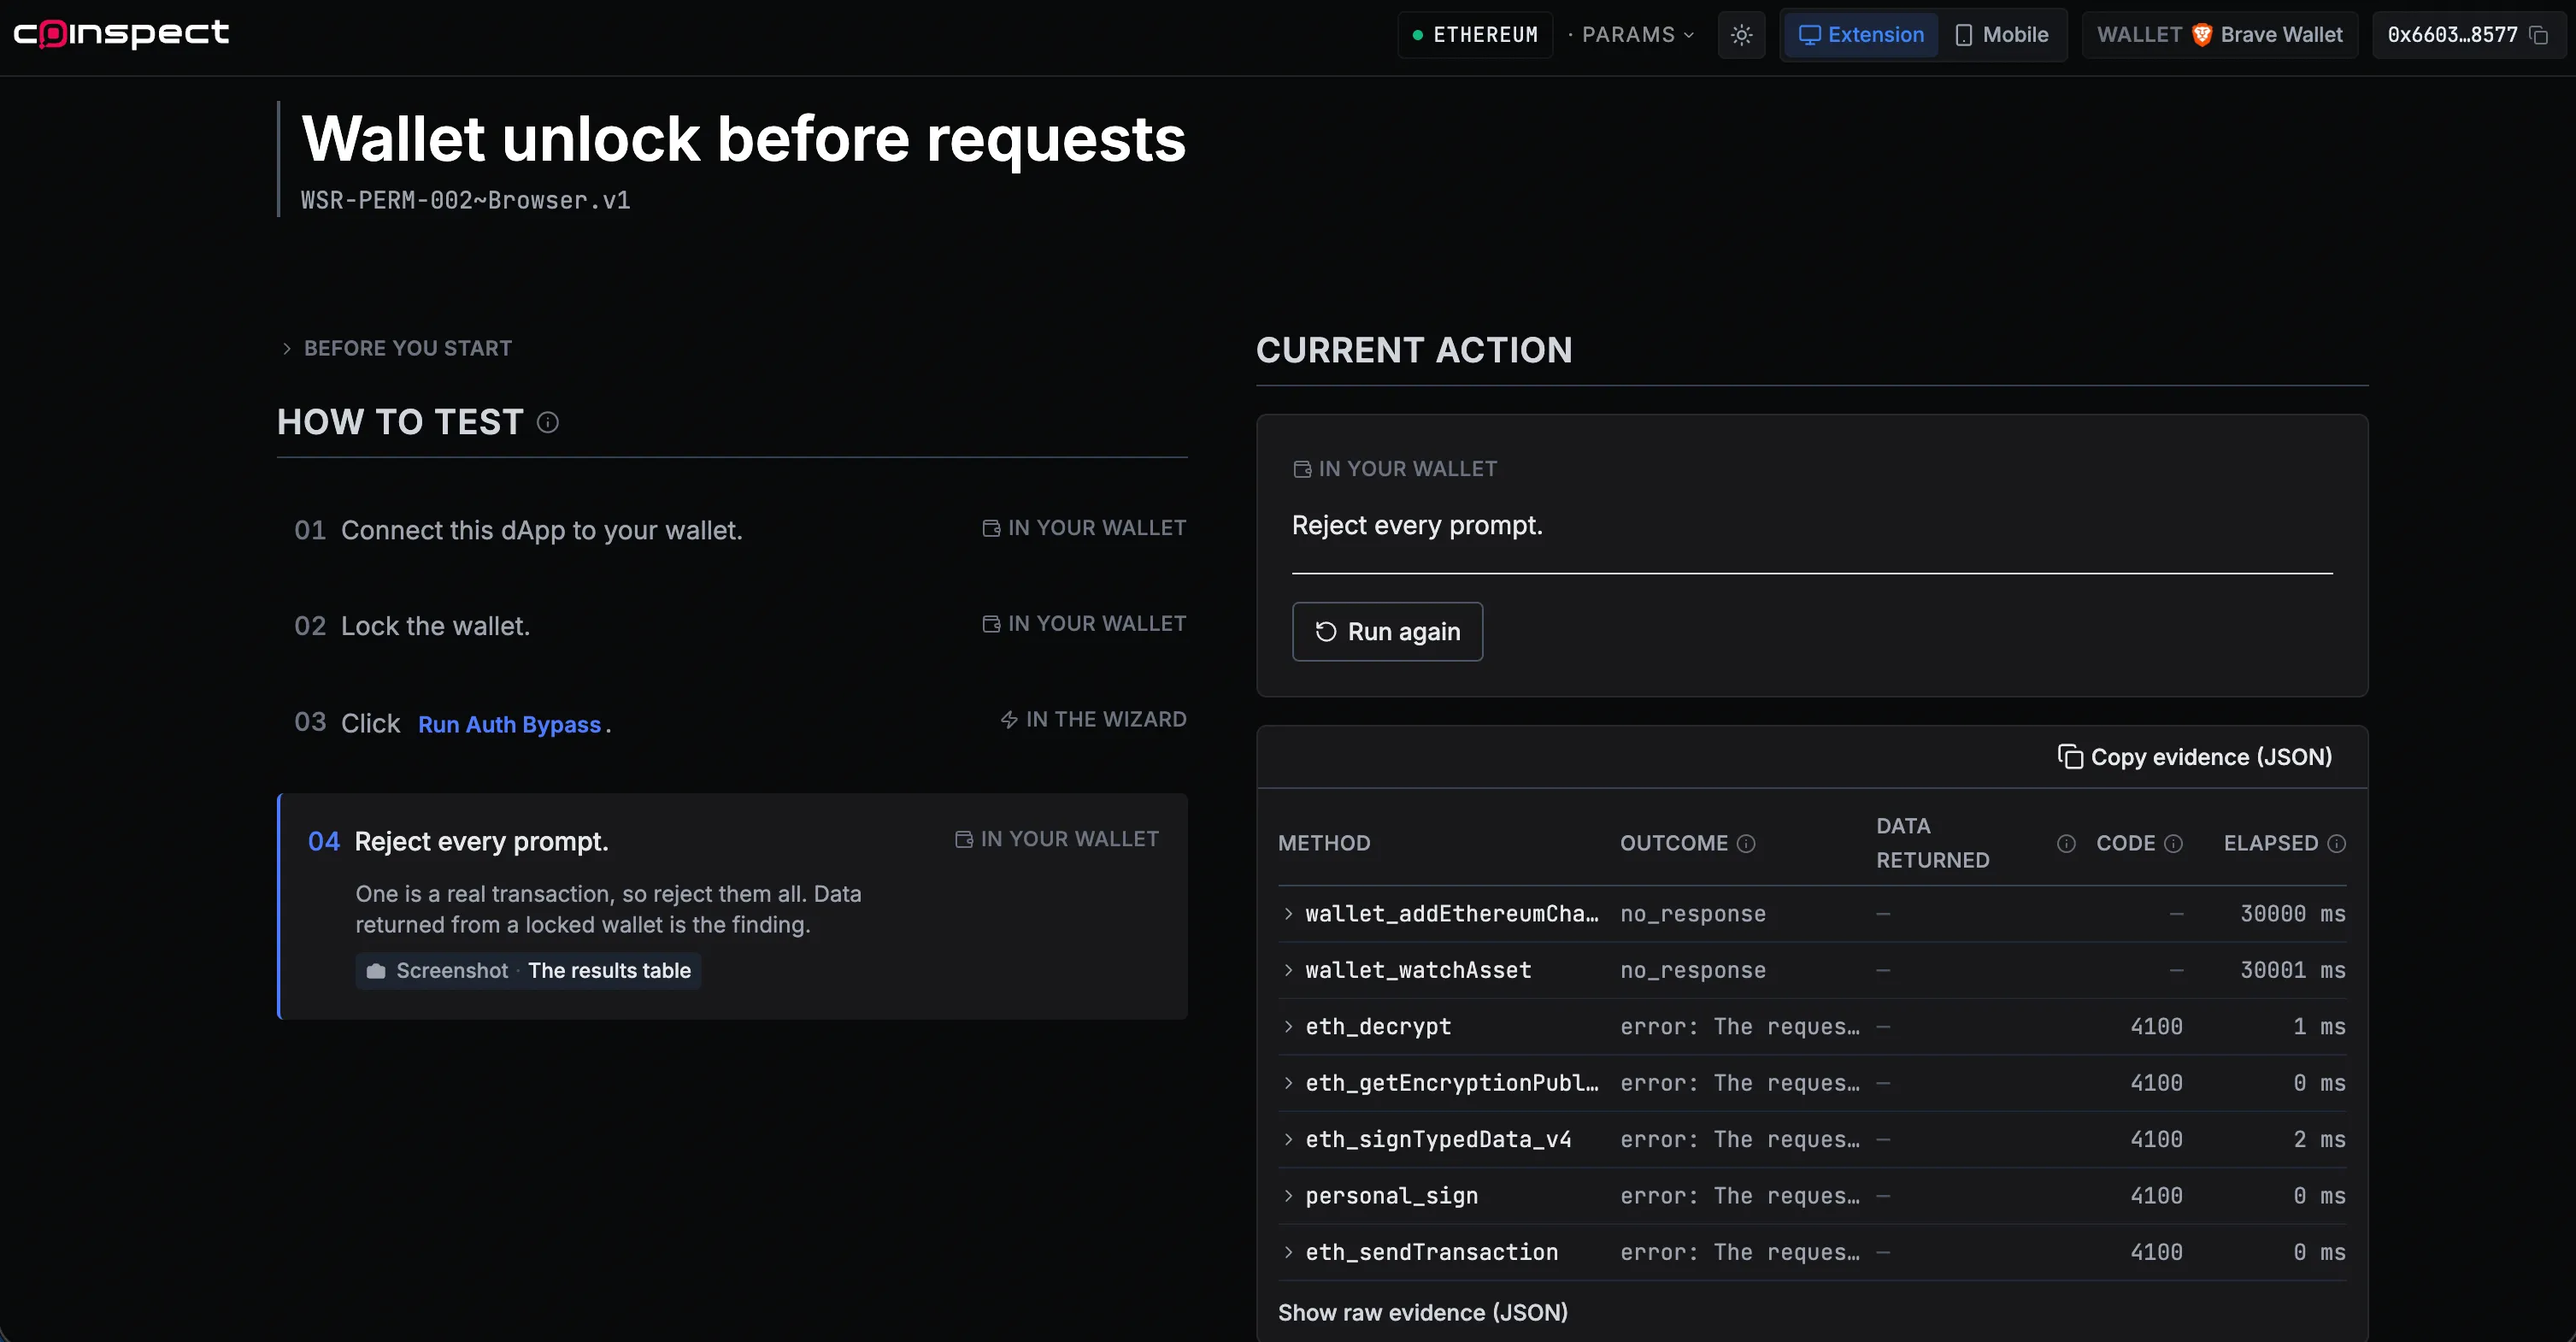 Last updated on Sep 3, 2026Report an issue with this check
-
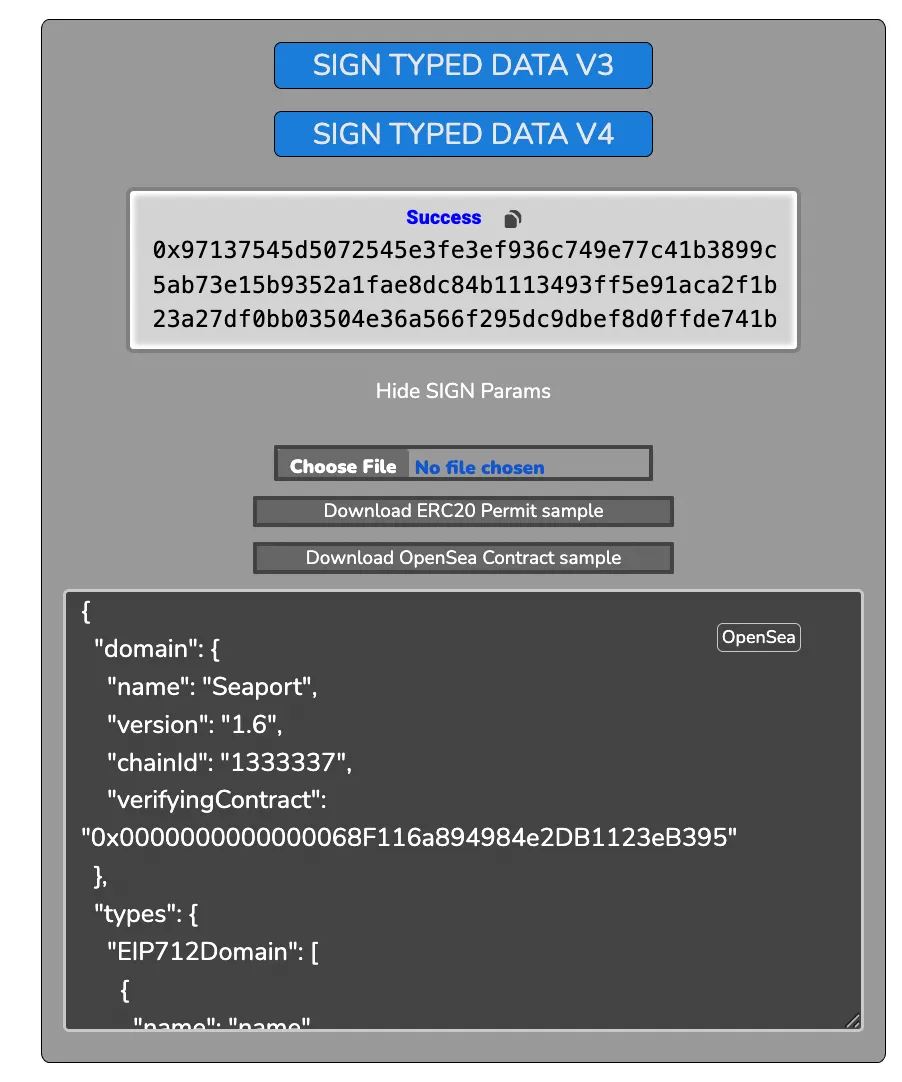
- Mismatching EIP-712 chainId detection0.0 / 3.5Description
Alerts users or rejects signing EIP-712 messages with a mismatched chain ID.
-
The wallet signed the EIP-712 object even though the chainId was different from the active network, without displaying a warning or rejecting the request.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots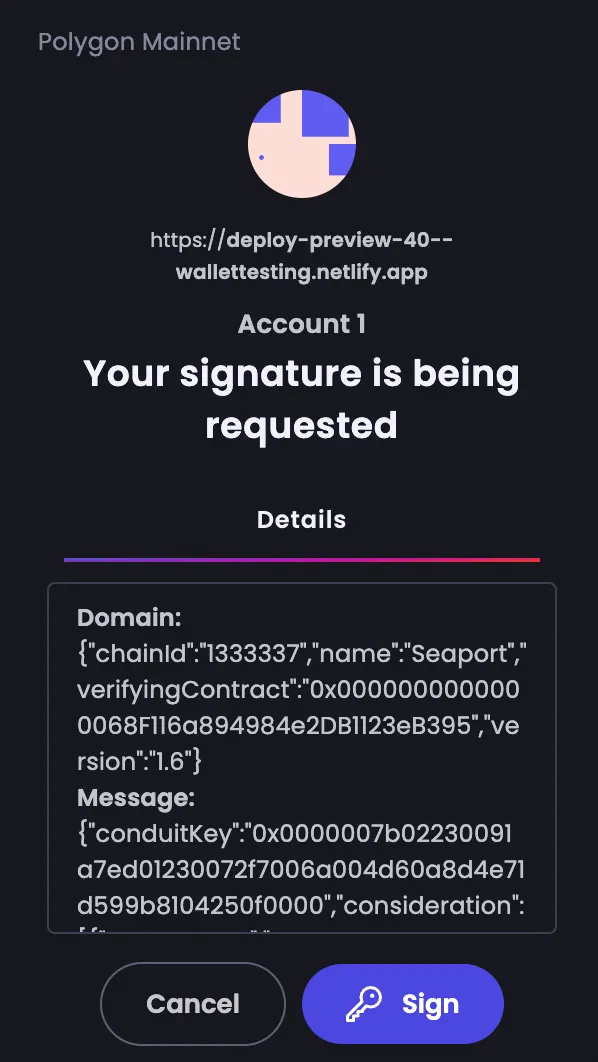
 Last updated on Sep 3, 2026Report an issue with this check
-
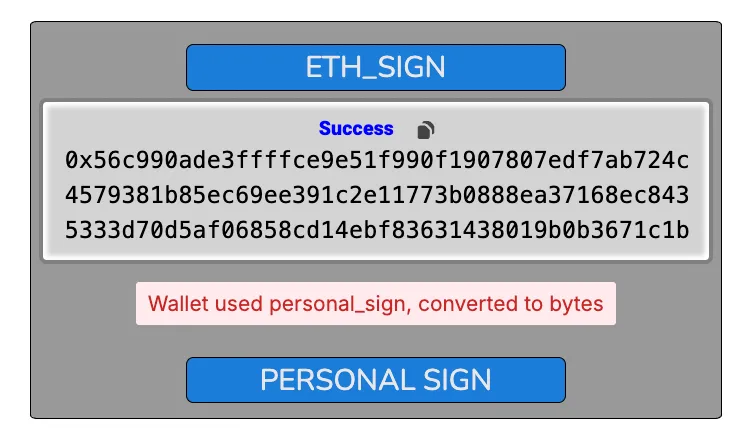
- eth_sign method disabled3.3 / 3.3Description
Restricts the use of the deprecated and insecure eth_sign method by default.
-
The wallet redirected the `eth_sign` request to `personal_sign`, and indicated that the wallet used personal_sign, converted to bytes.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots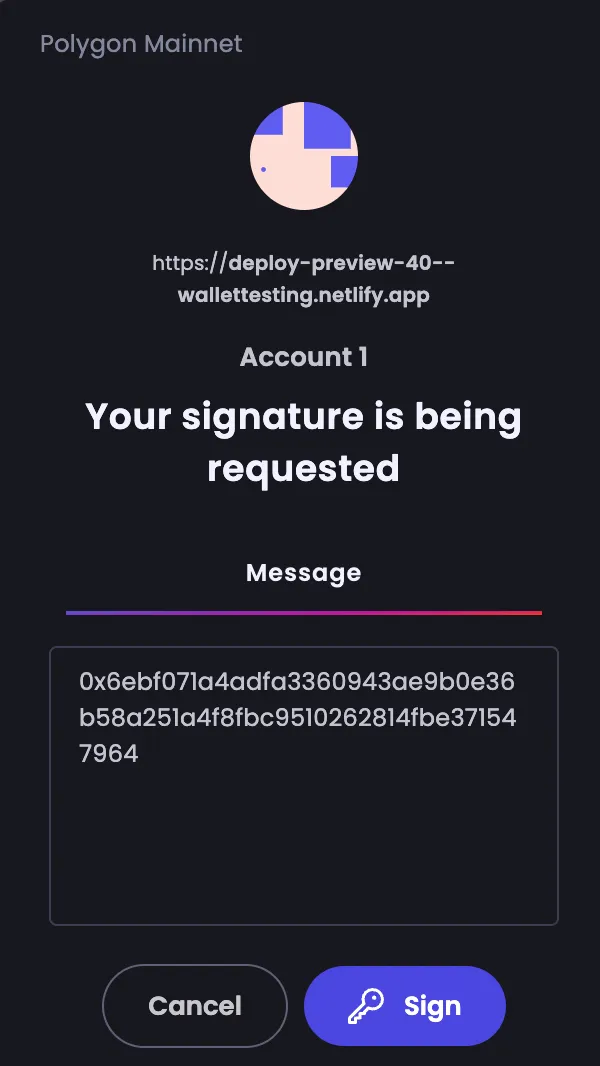
 Last updated on Sep 3, 2026Report an issue with this check
-
- Mismatching SIWE domain detection1.9 / 1.9Description
Warns users when the domain in a Sign-In with Ethereum (EIP-4361) message does not match the requesting dApp's origin.
-
The wallet detected the domain mismatch between the dApp and the SIWE object and blocked the signing request.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot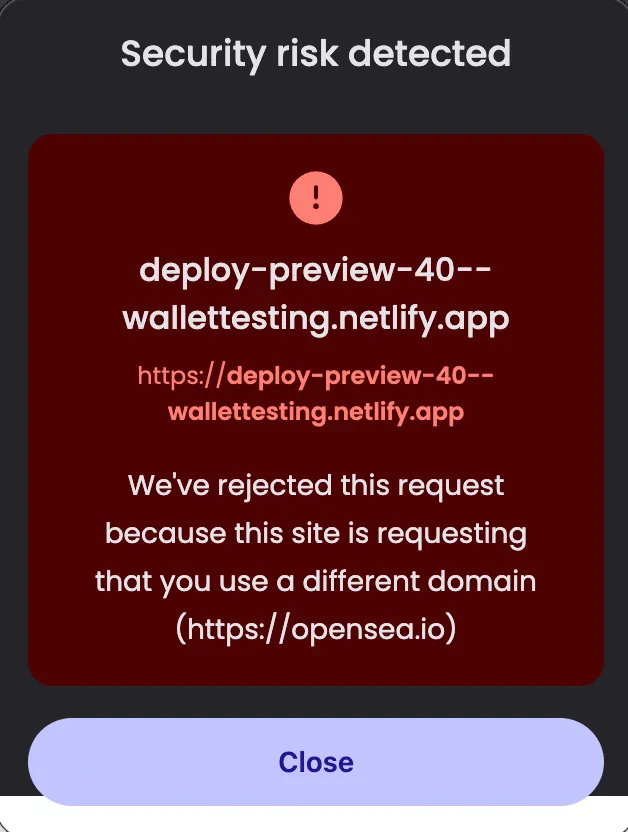 Last updated on Sep 3, 2026Report an issue with this check
-
- Token approval management0.0 / 1.6Description
Allows users to view and revoke token approvals.
-
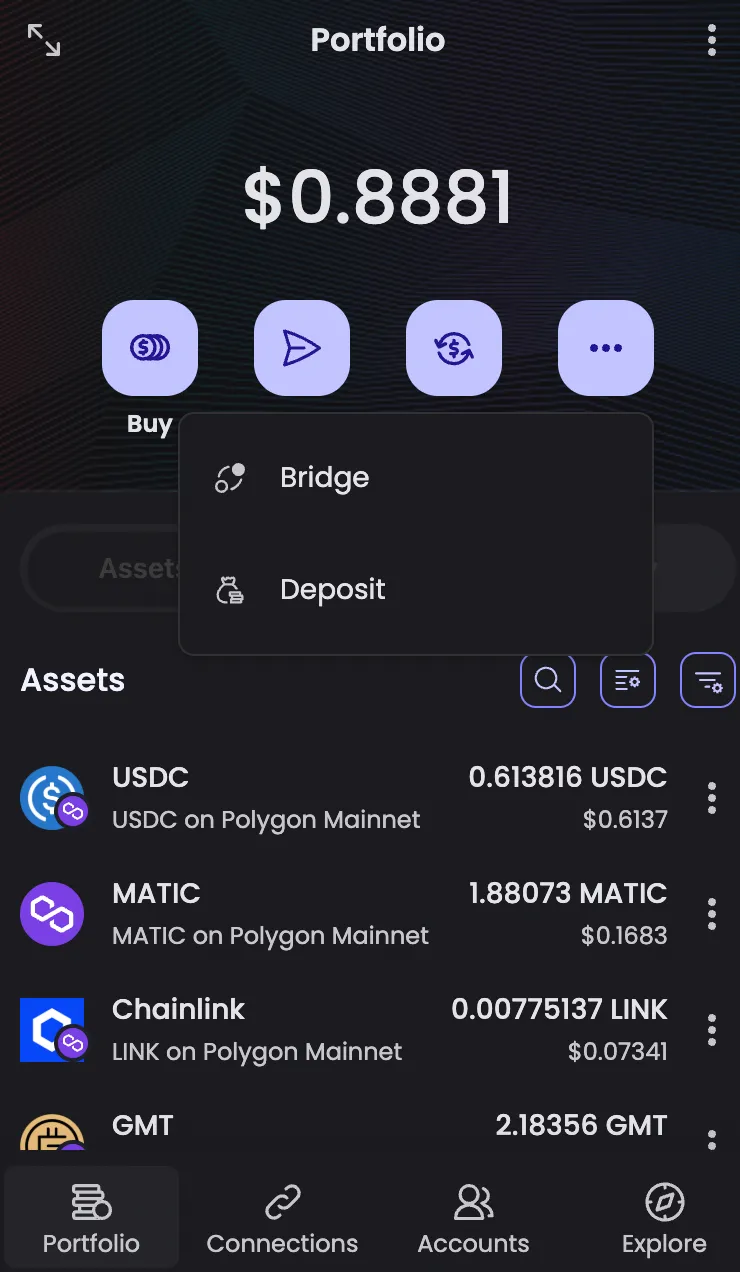
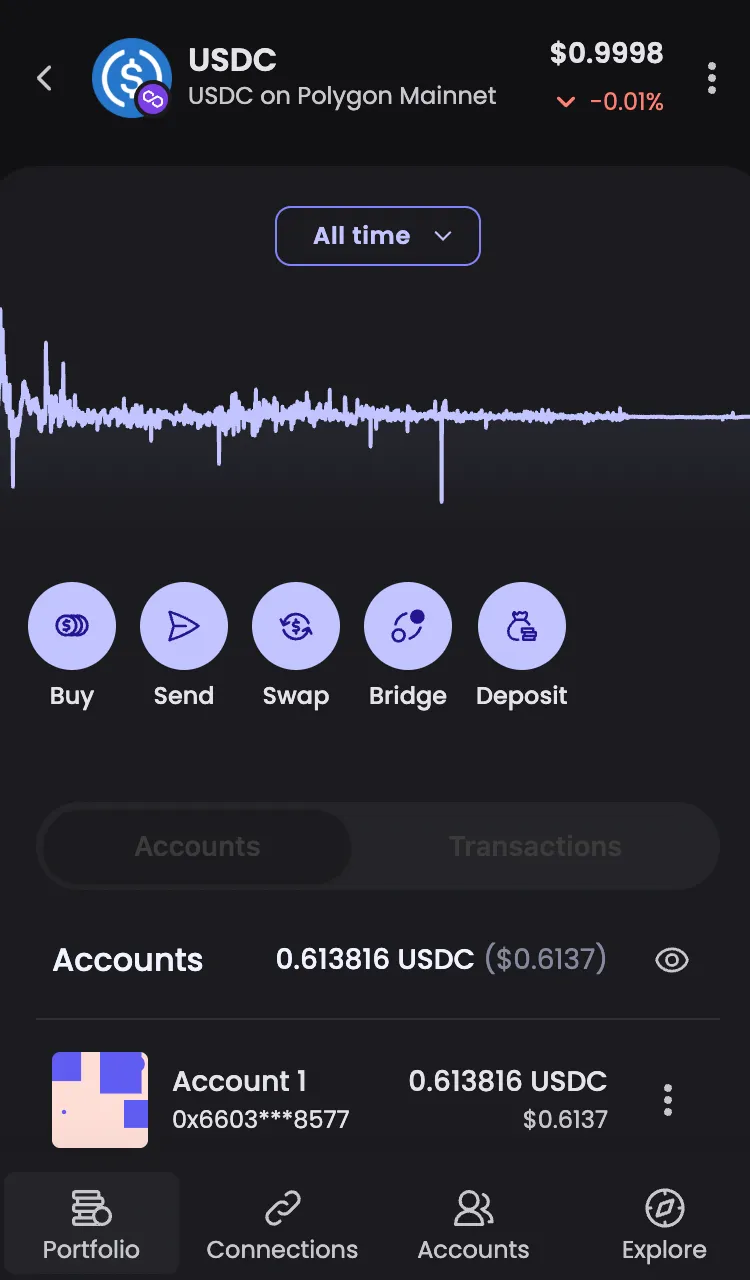
The wallet does not offer the ability to list and revoke token approvals, via in-app functionality or links to external dApps.
— Verified by Sebastian Camia at Coinspect
Evidence · 3 screenshots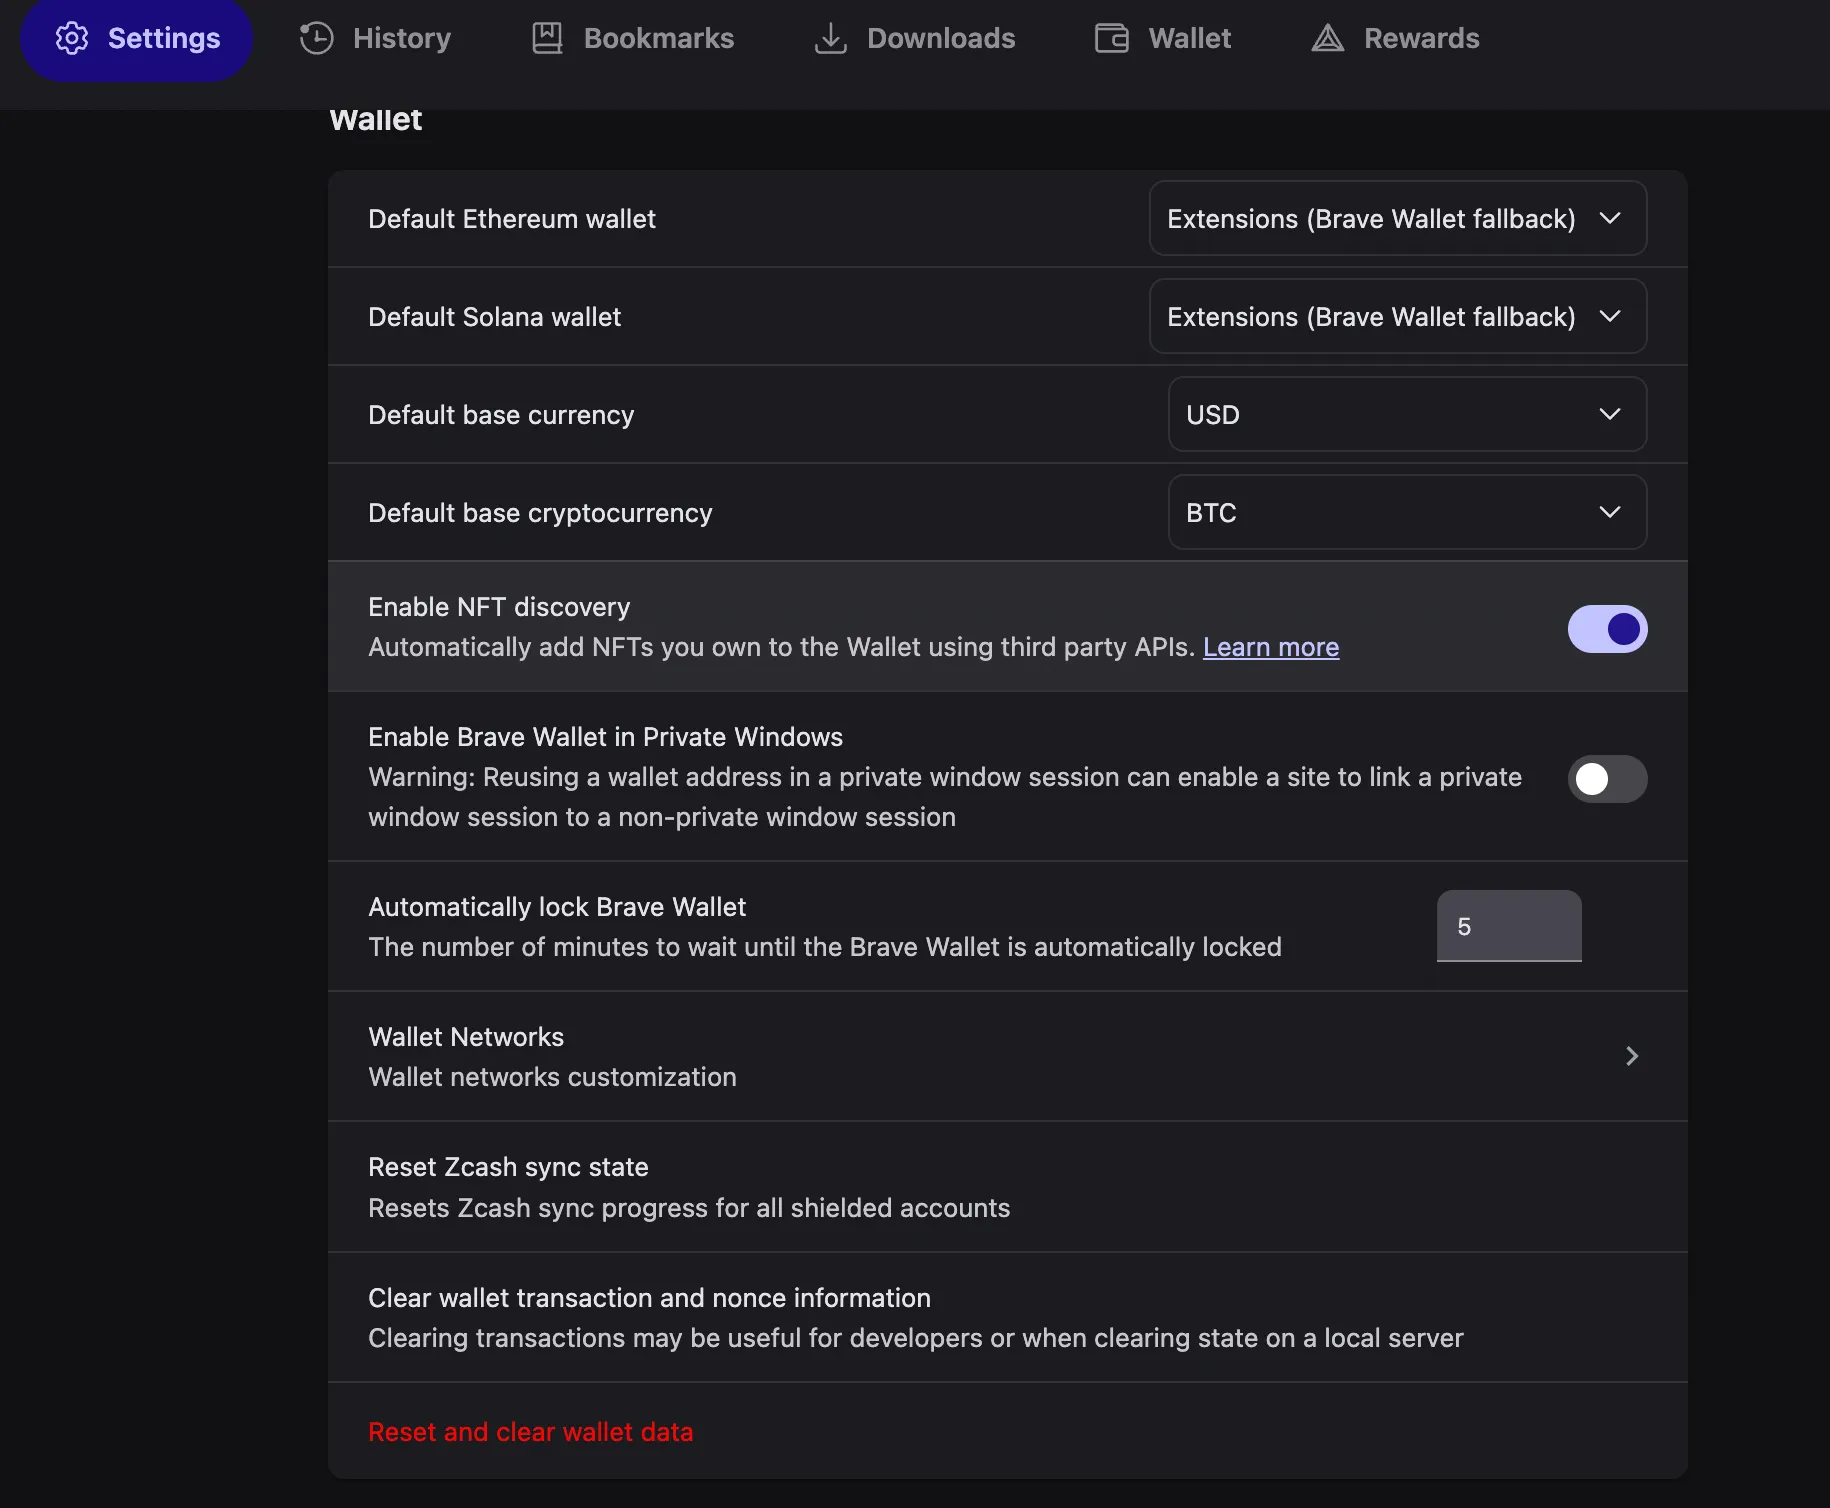
 Last updated on Sep 3, 2026Report an issue with this check
-
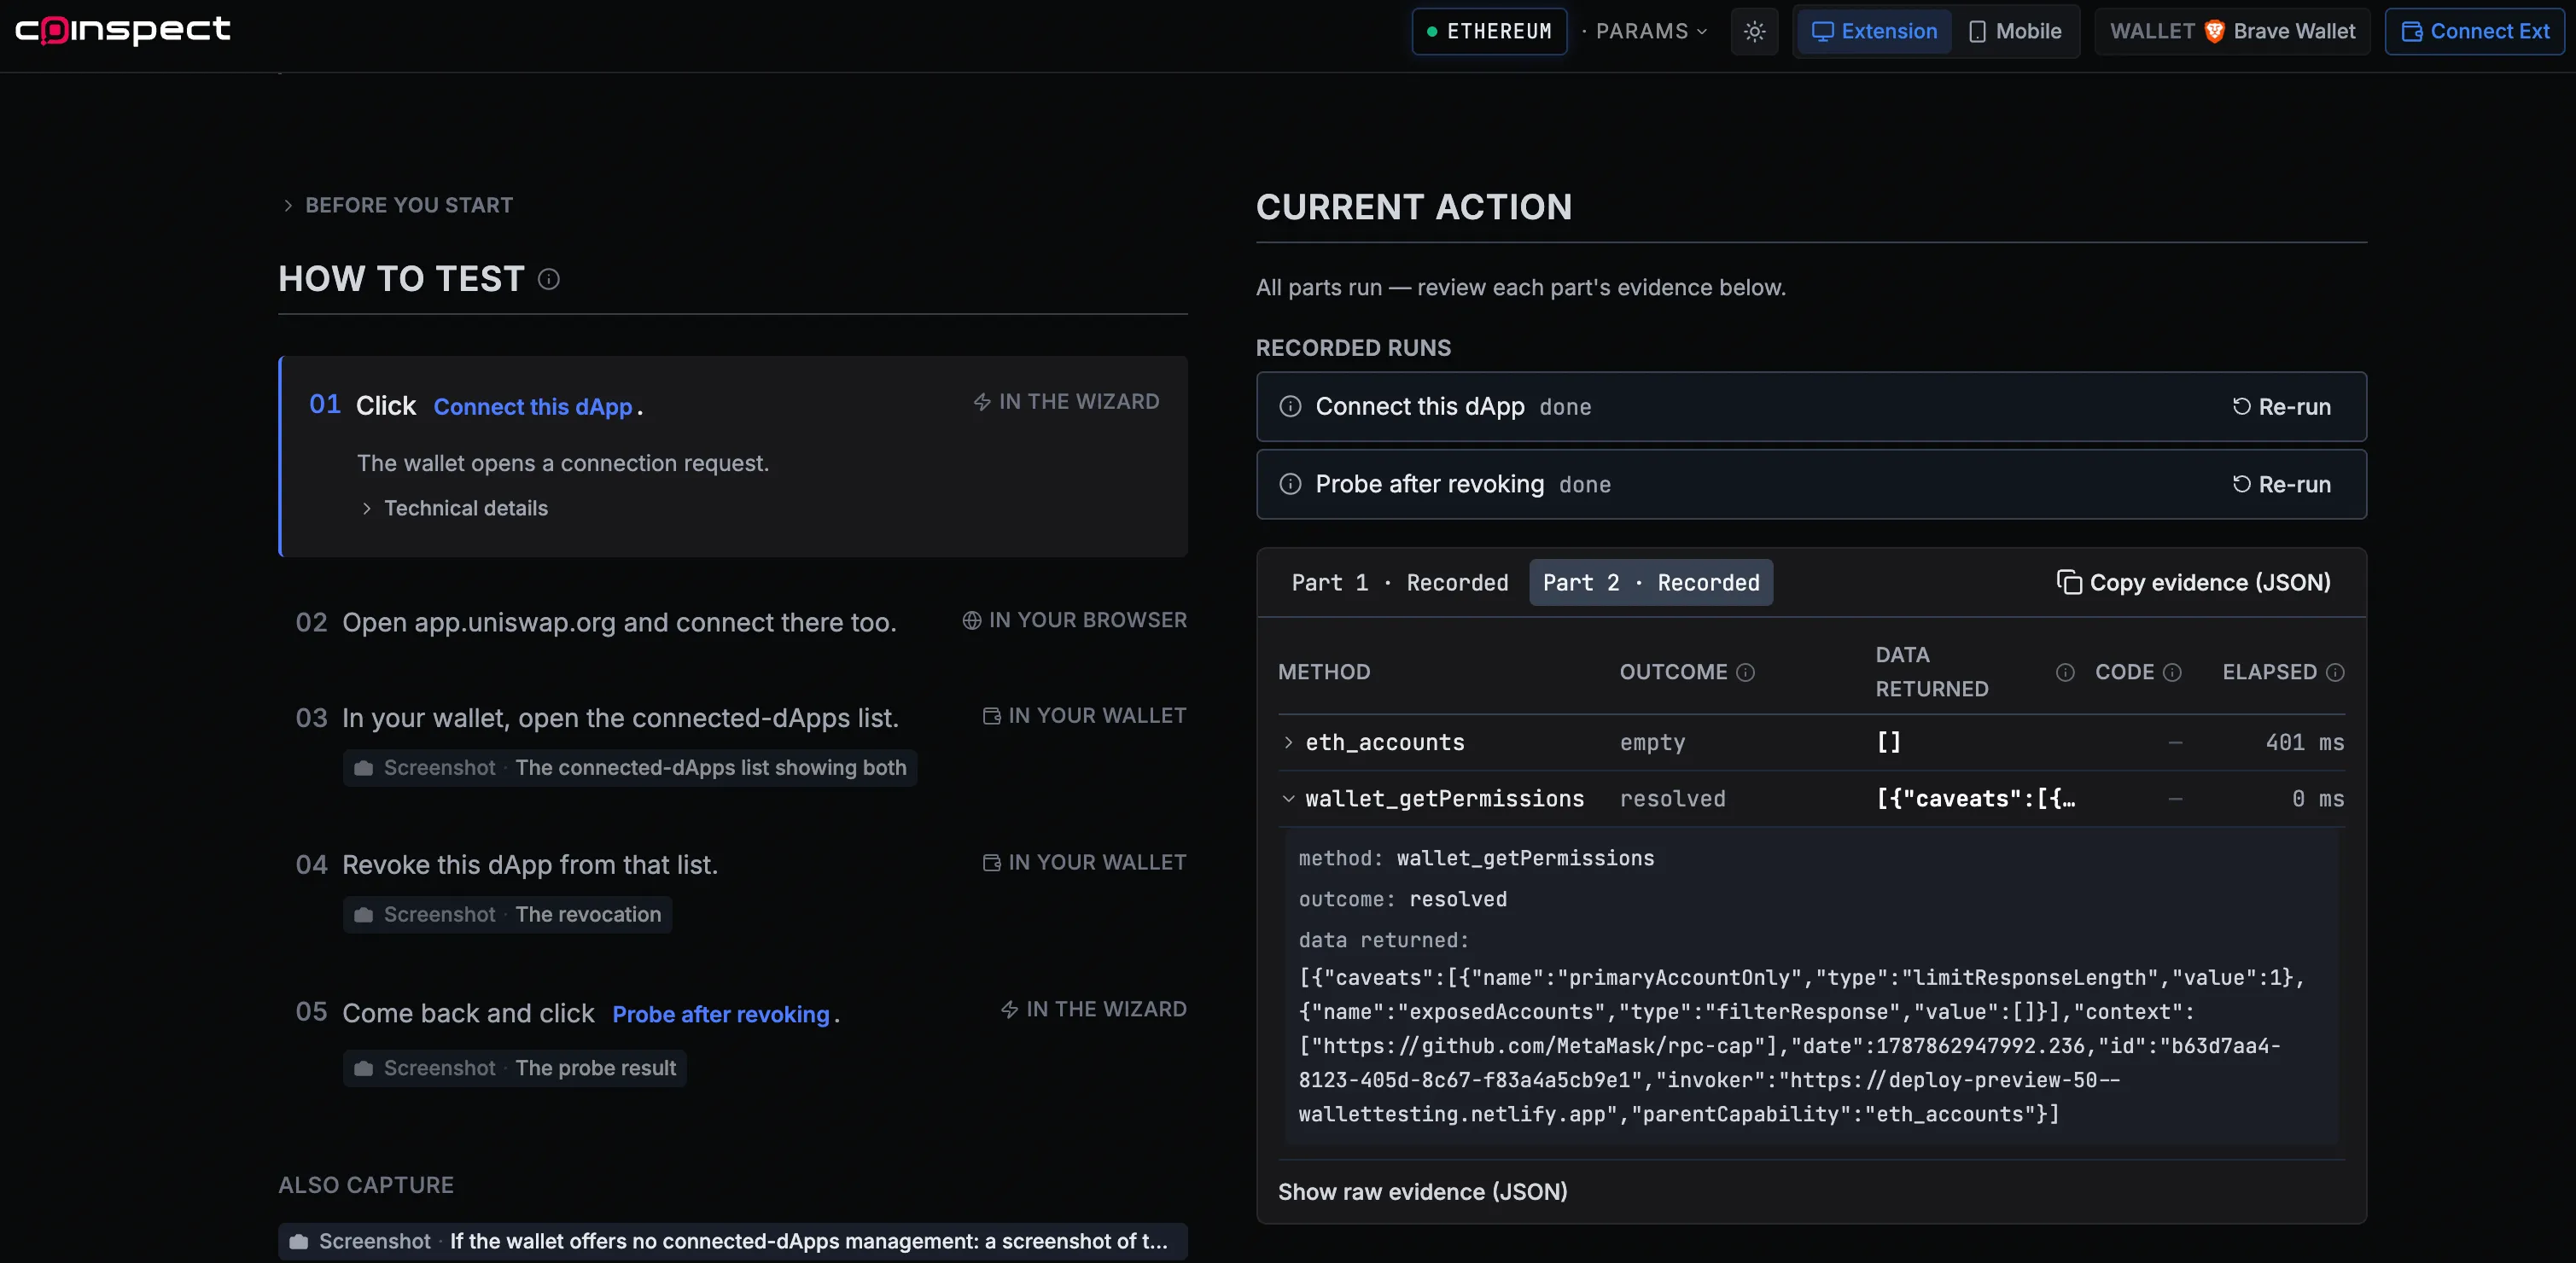
- Connected dApp management1.5 / 1.5Description
Allows users to list and revoke connected dApps.
-
The wallet lists connected dApps and revoking access prevents further RPC requests from the disconnected dApp.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots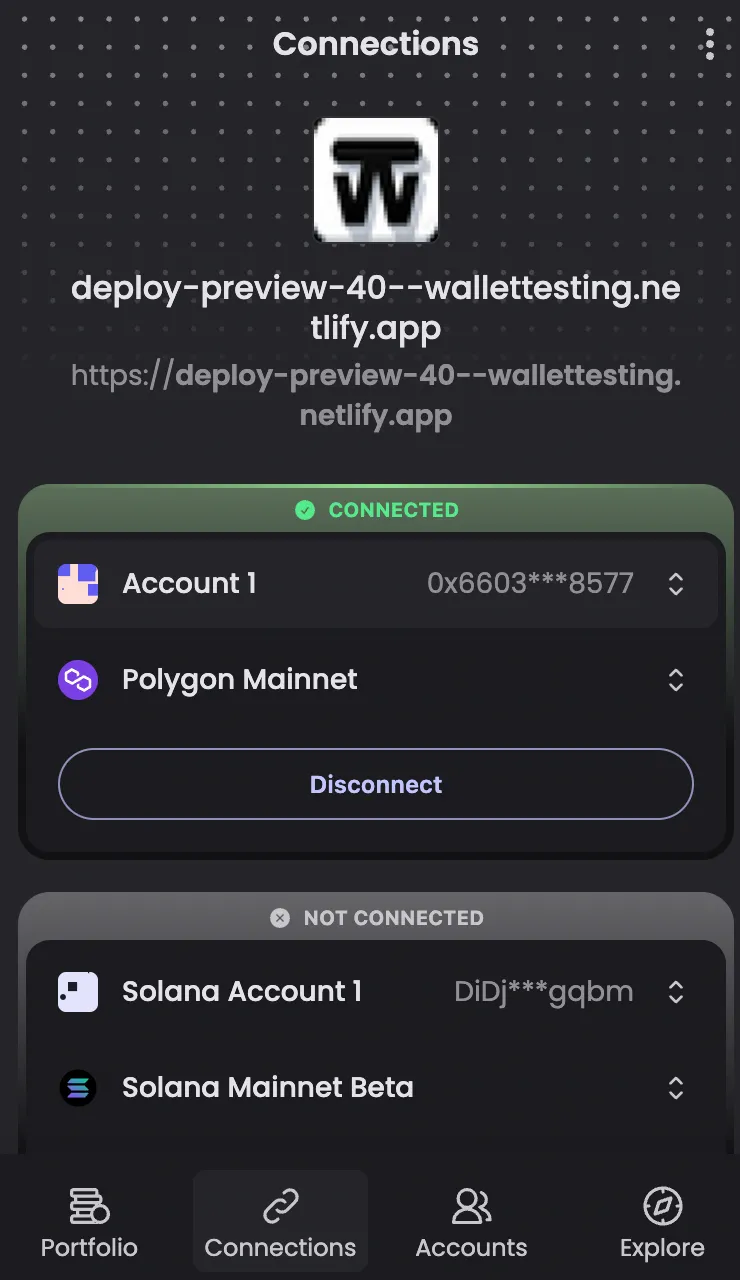
 Last updated on Sep 3, 2026Report an issue with this check
-
- User confirmation before switching chains1.2 / 1.2Description
Requires user confirmation before switching the active chain.
-
The wallet prompts for user confirmation before switching the network, as required.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot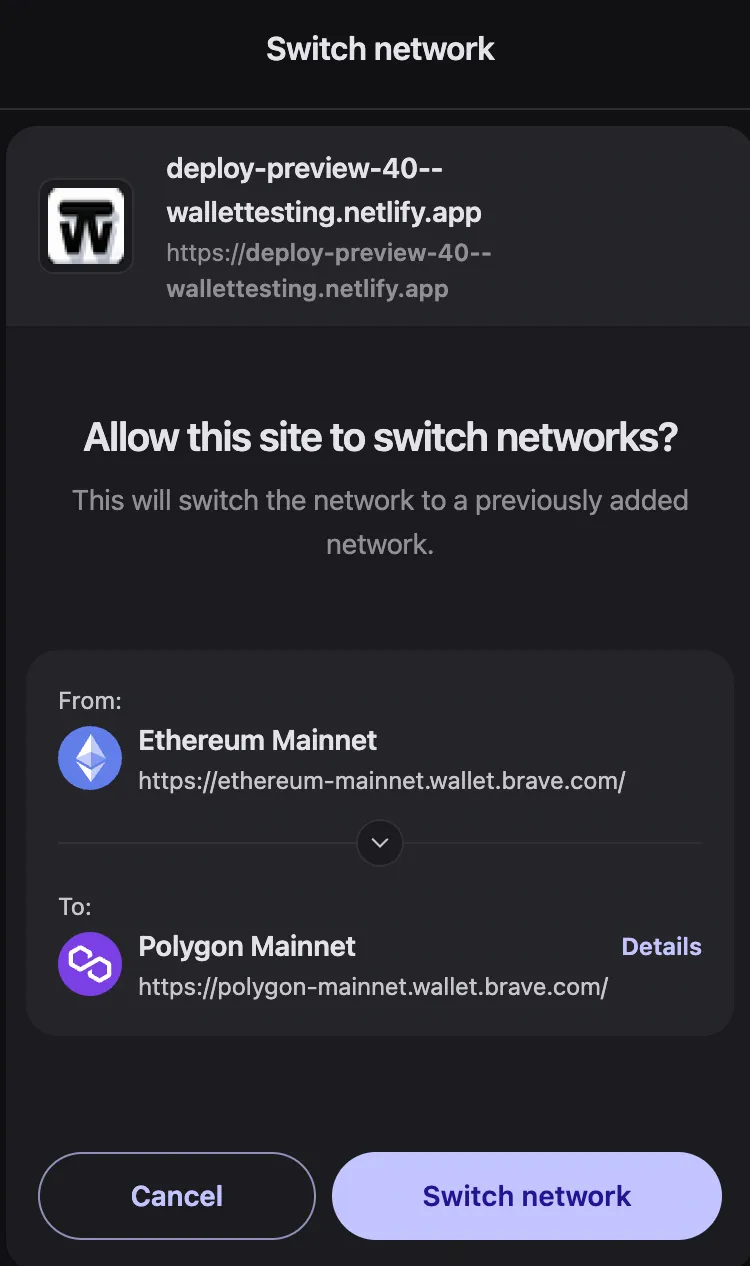 Last updated on Sep 3, 2026Report an issue with this check
-
Intent Verification
- Transaction simulation0.0 / 6.7Description
Previews the expected outcome by simulating the request execution on the blockchain before signing.
-
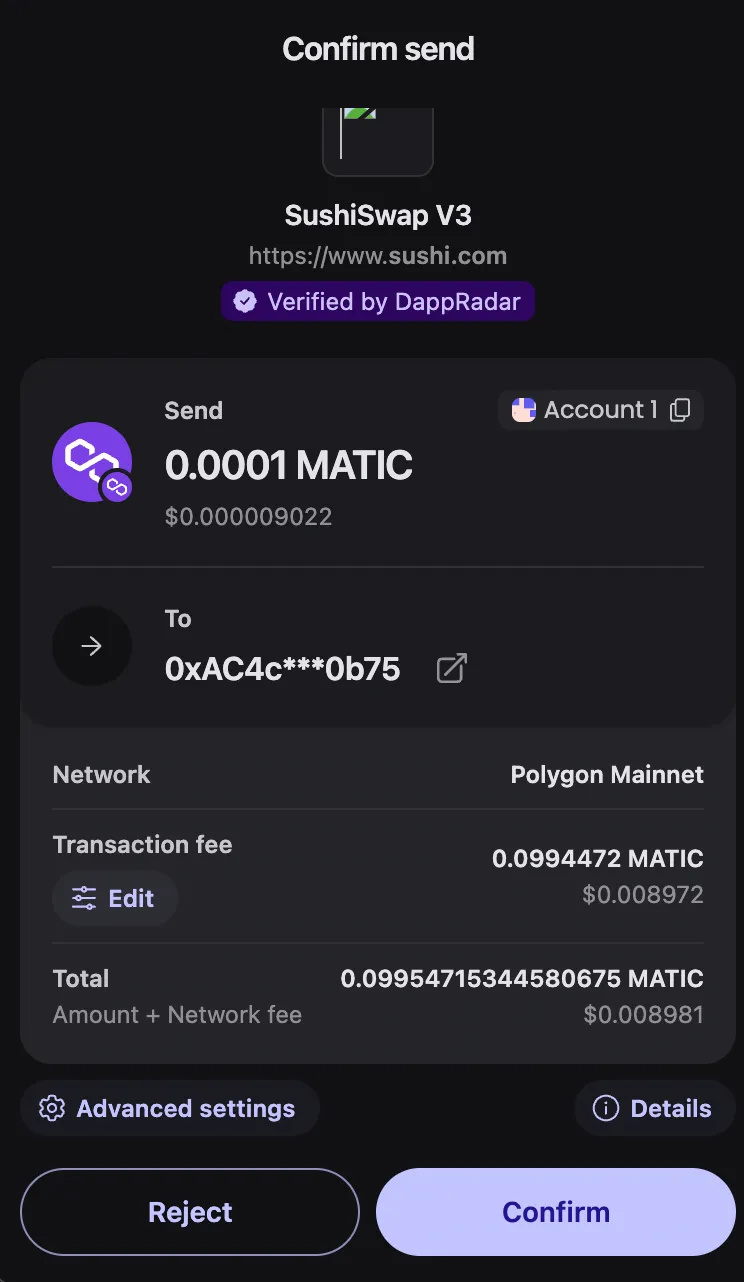
The wallet only shows the amount of MATIC being sent, but do not show the expected outputs from the execution of the transaction before signing.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots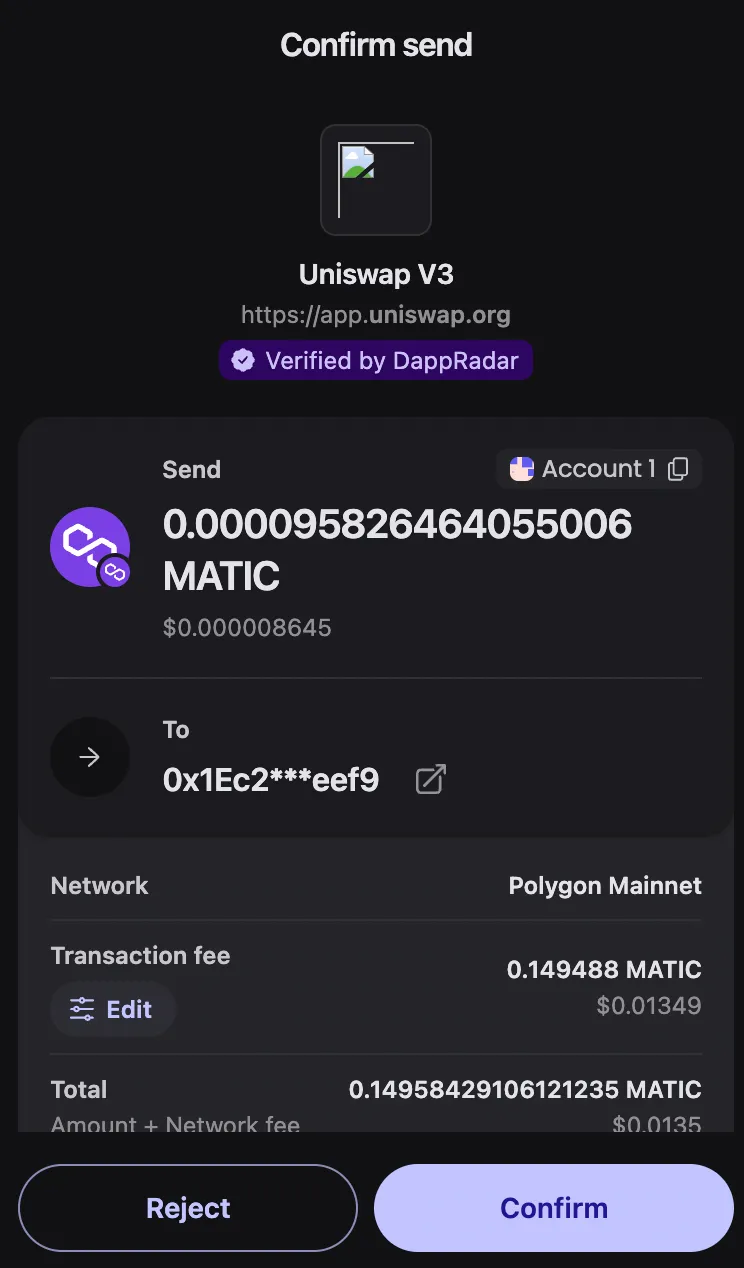
 Last updated on Sep 3, 2026Report an issue with this check
-
- Clear token approval dialog6.7 / 6.7Description
Clearly displays all the key details for ERC-20 Approve requests.
-
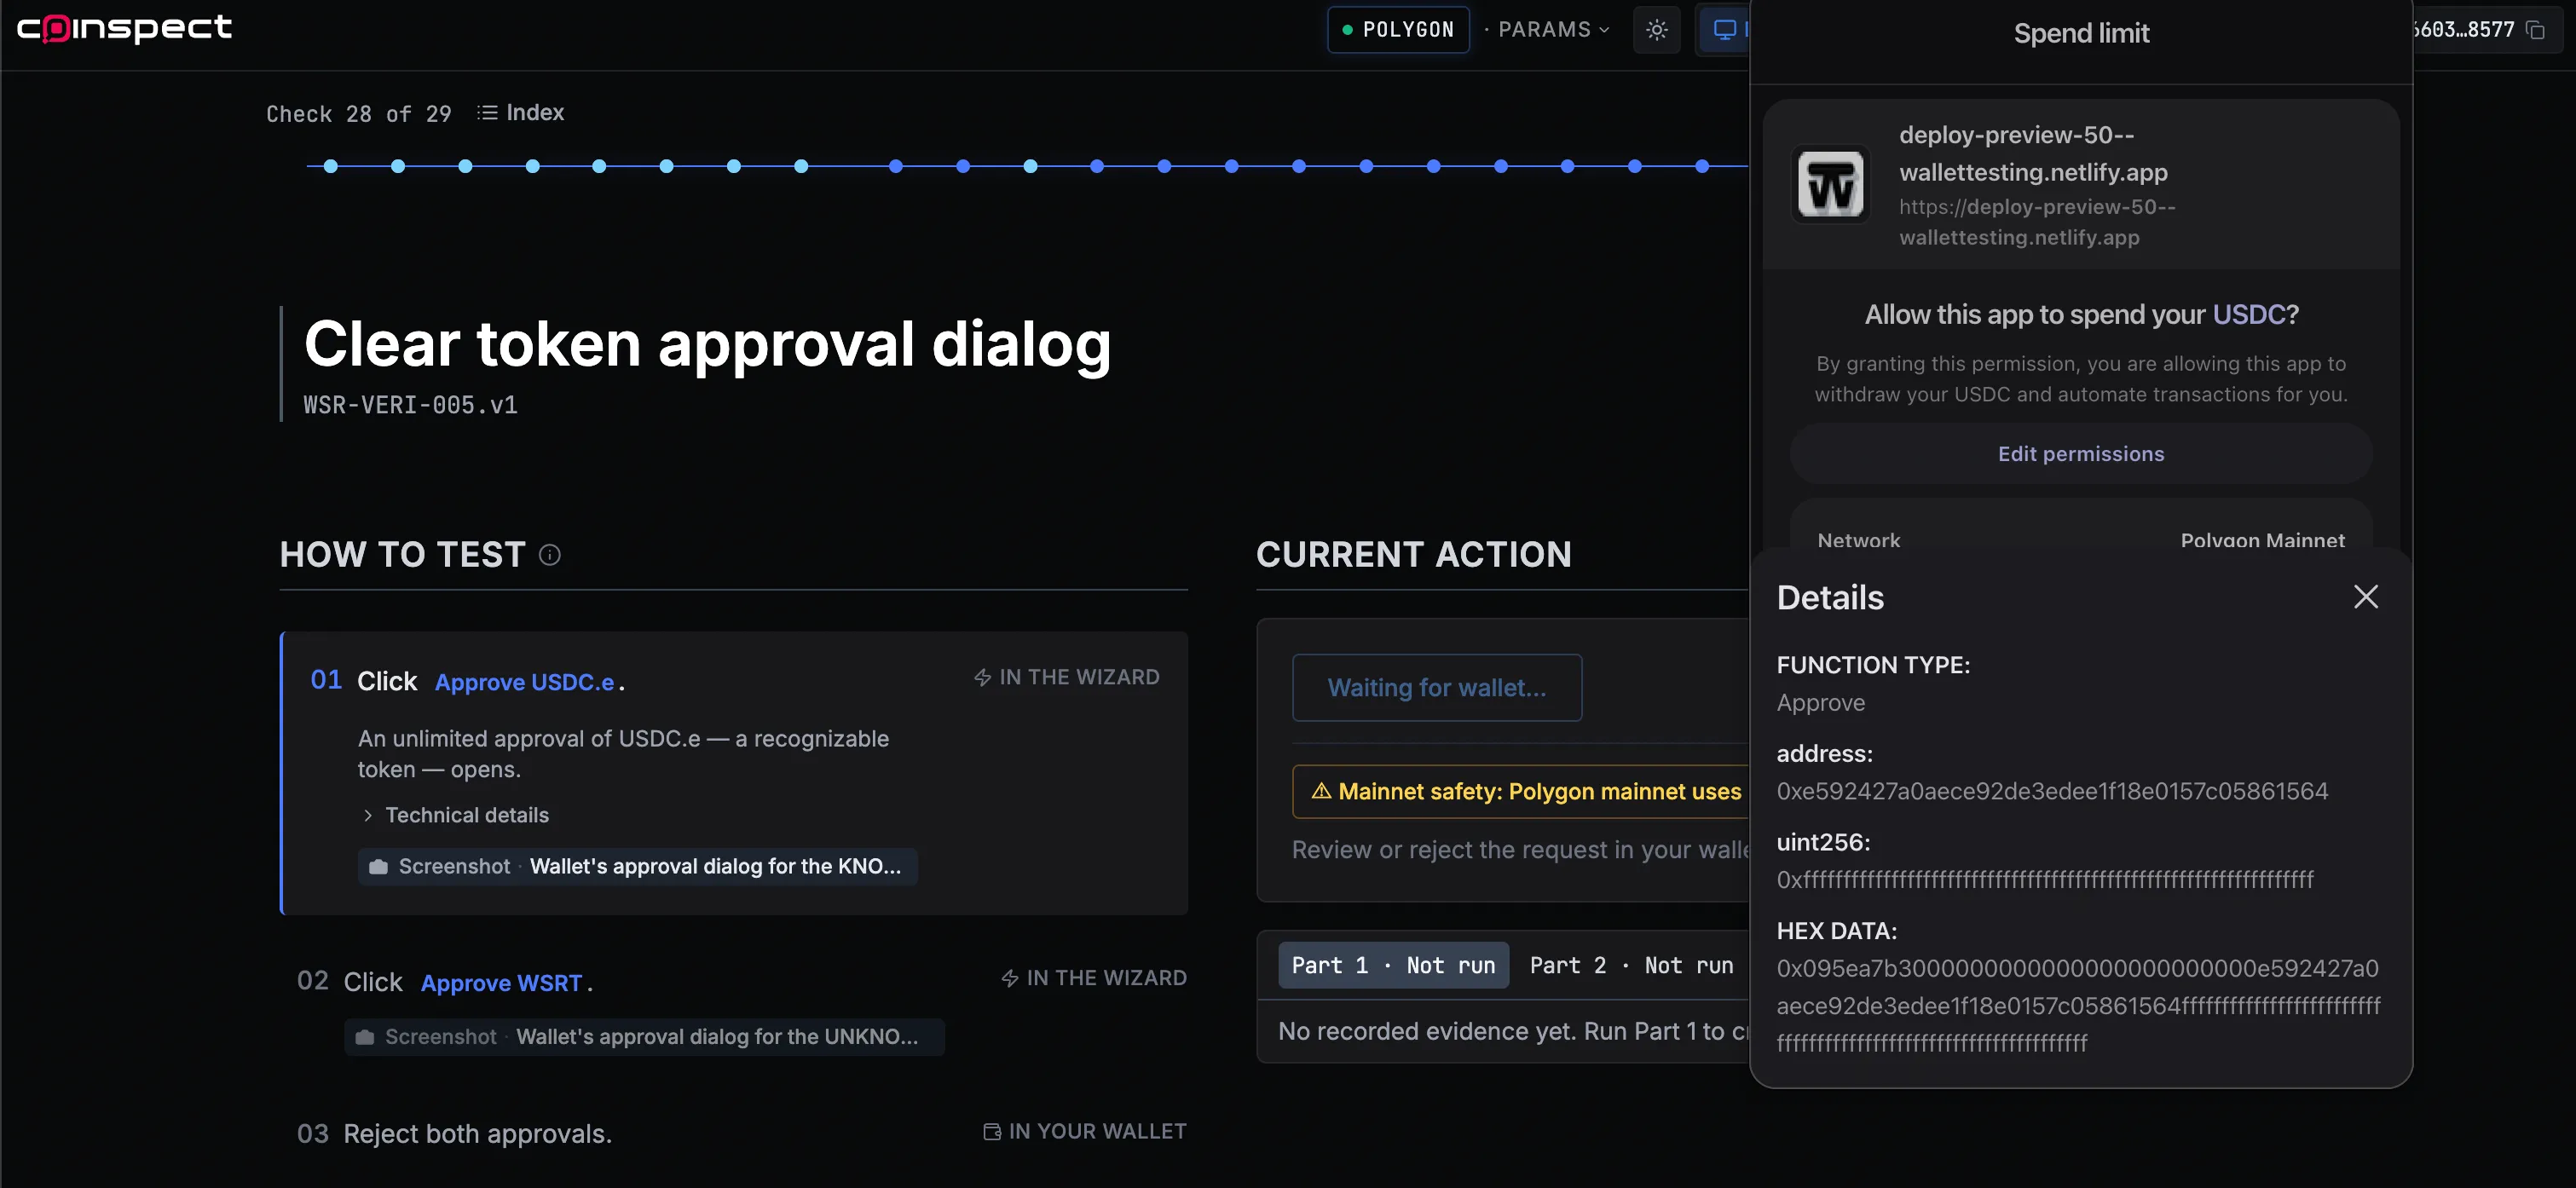
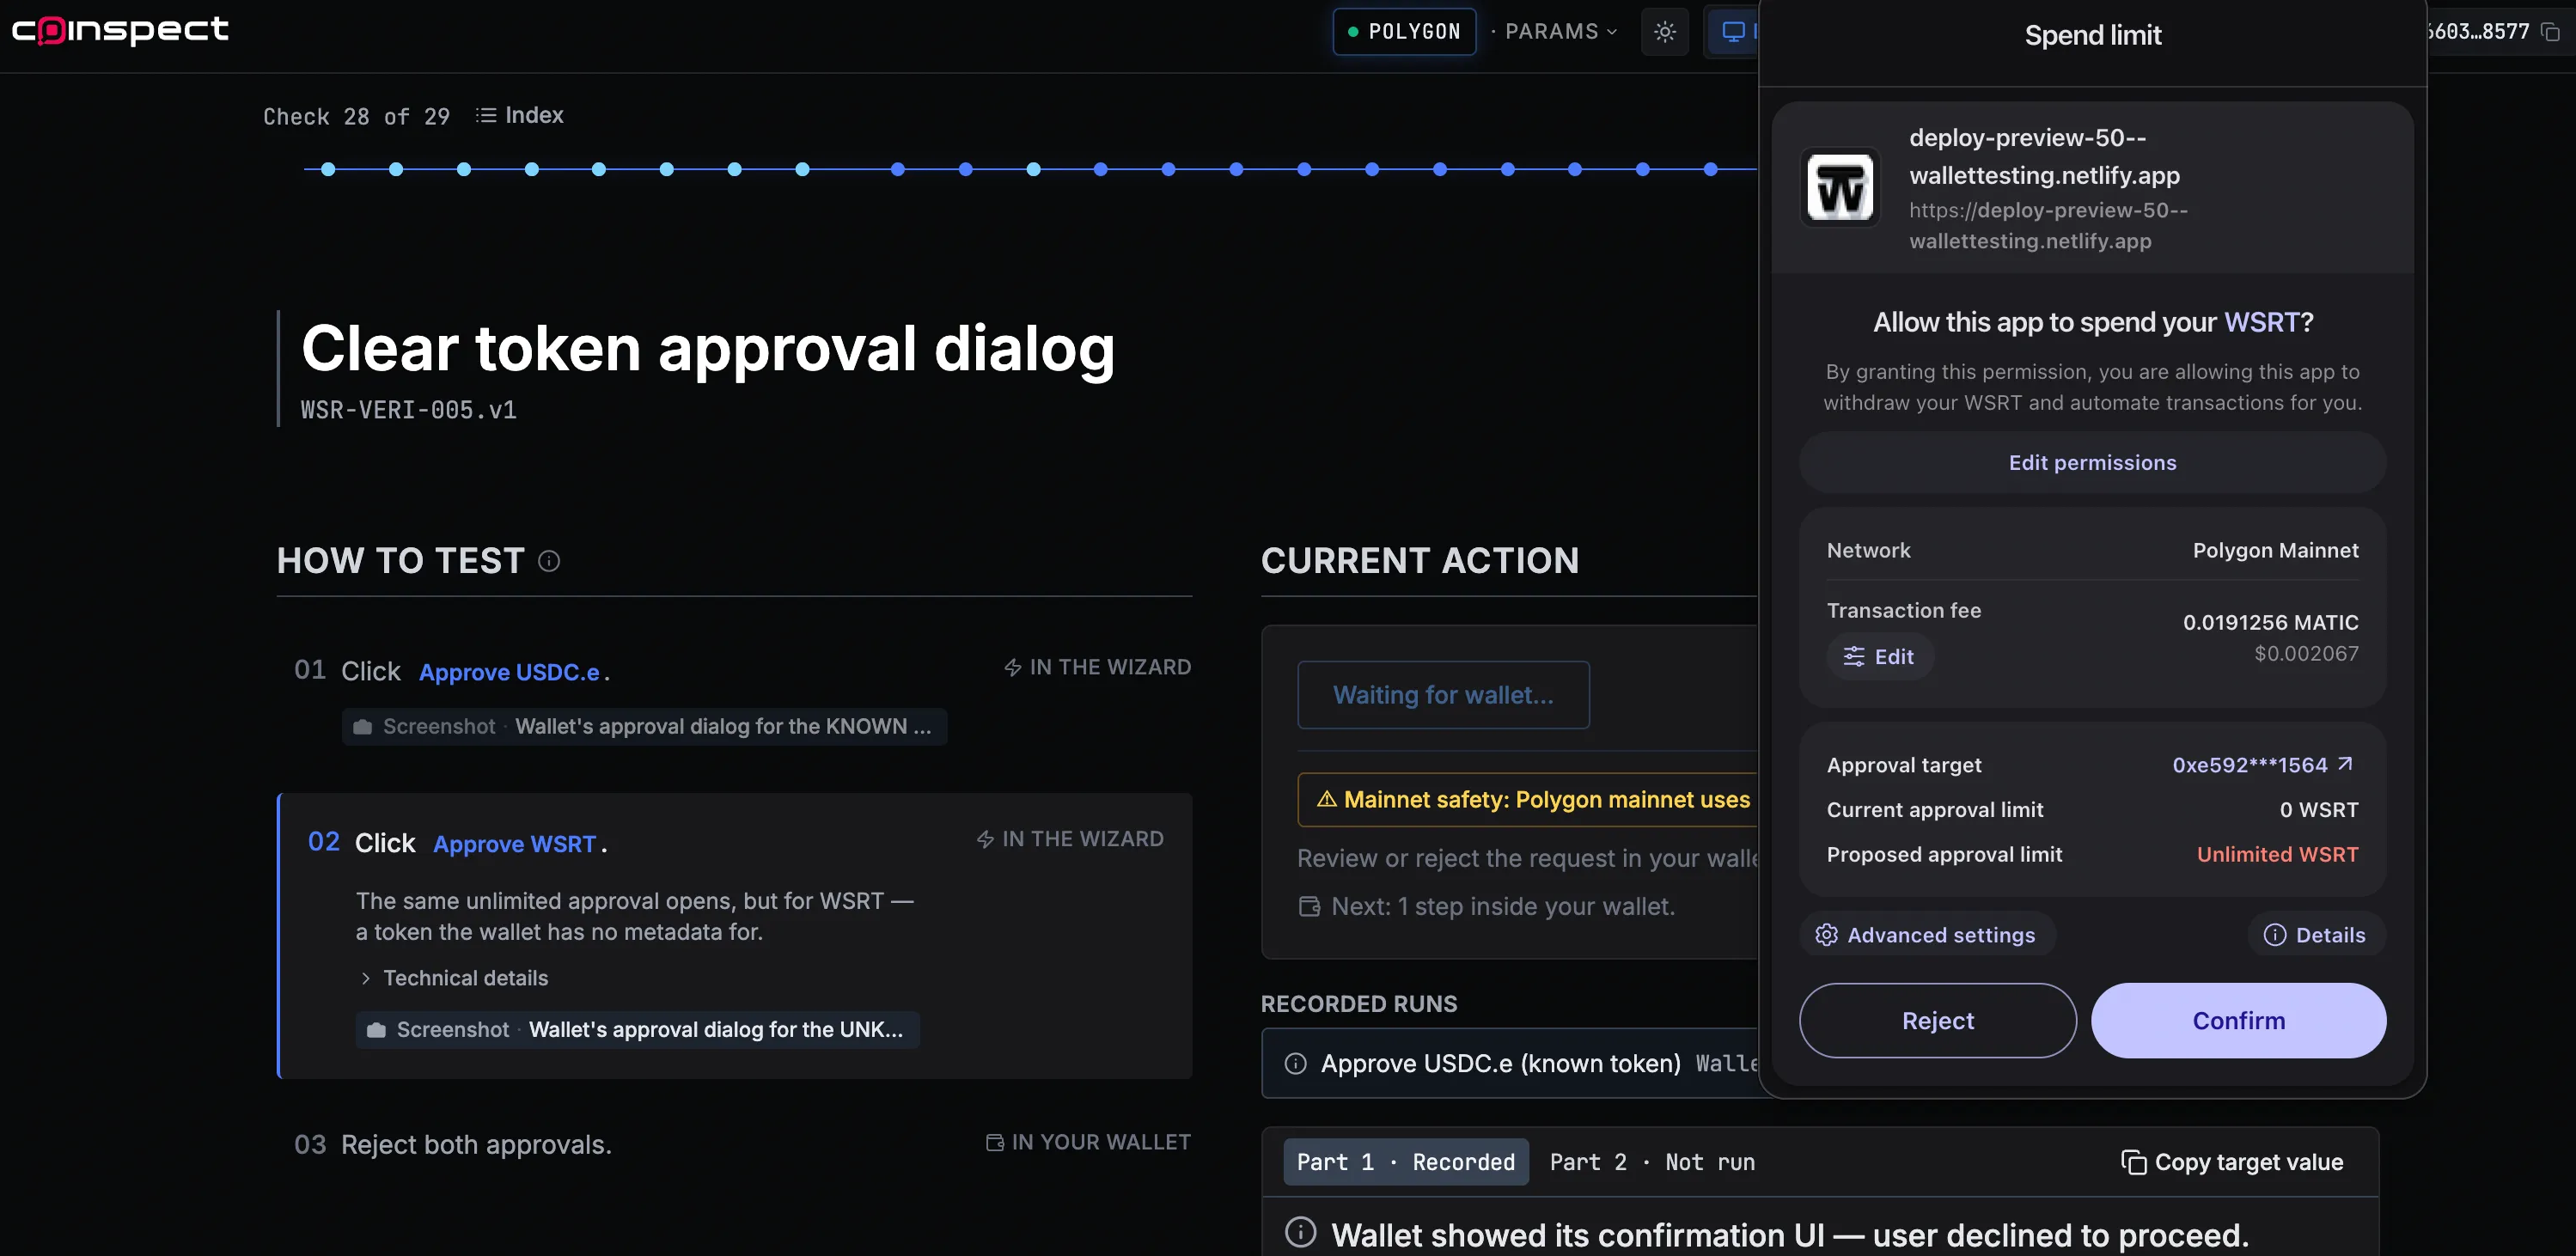
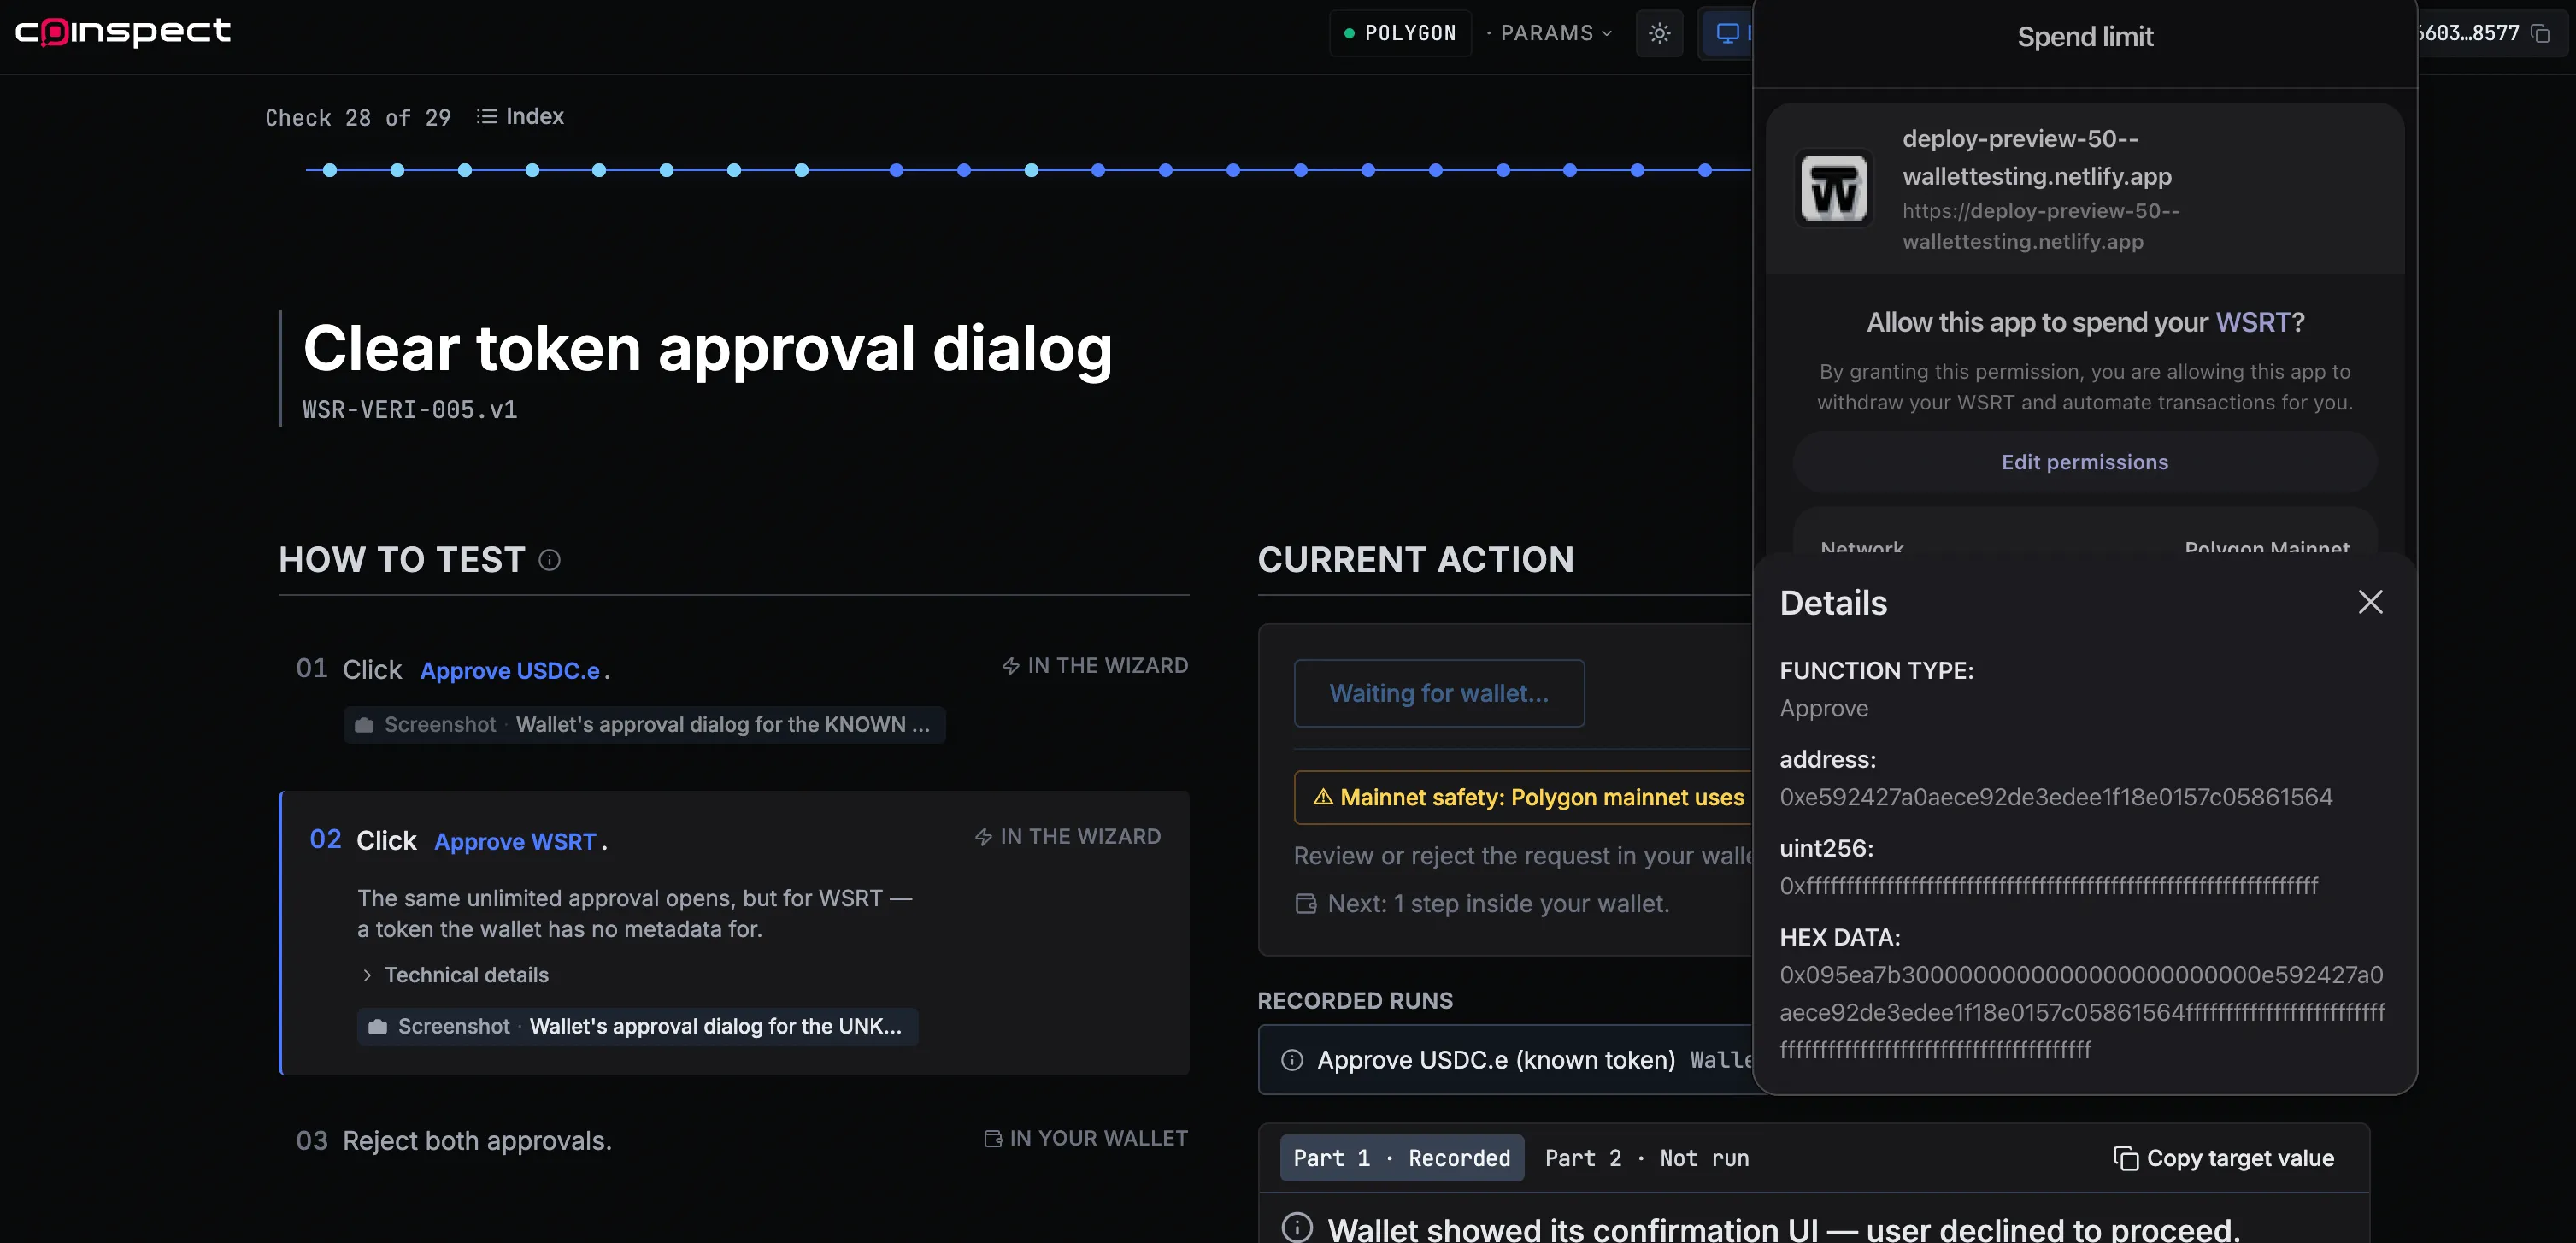
The wallet clearly identifies the approval request and displays the token symbol/address, spender address, and approved amount for both the known token (USDC) and the custom ERC-20 (WSRT).
— Verified by Sebastian Camia at Coinspect
Evidence · 4 screenshots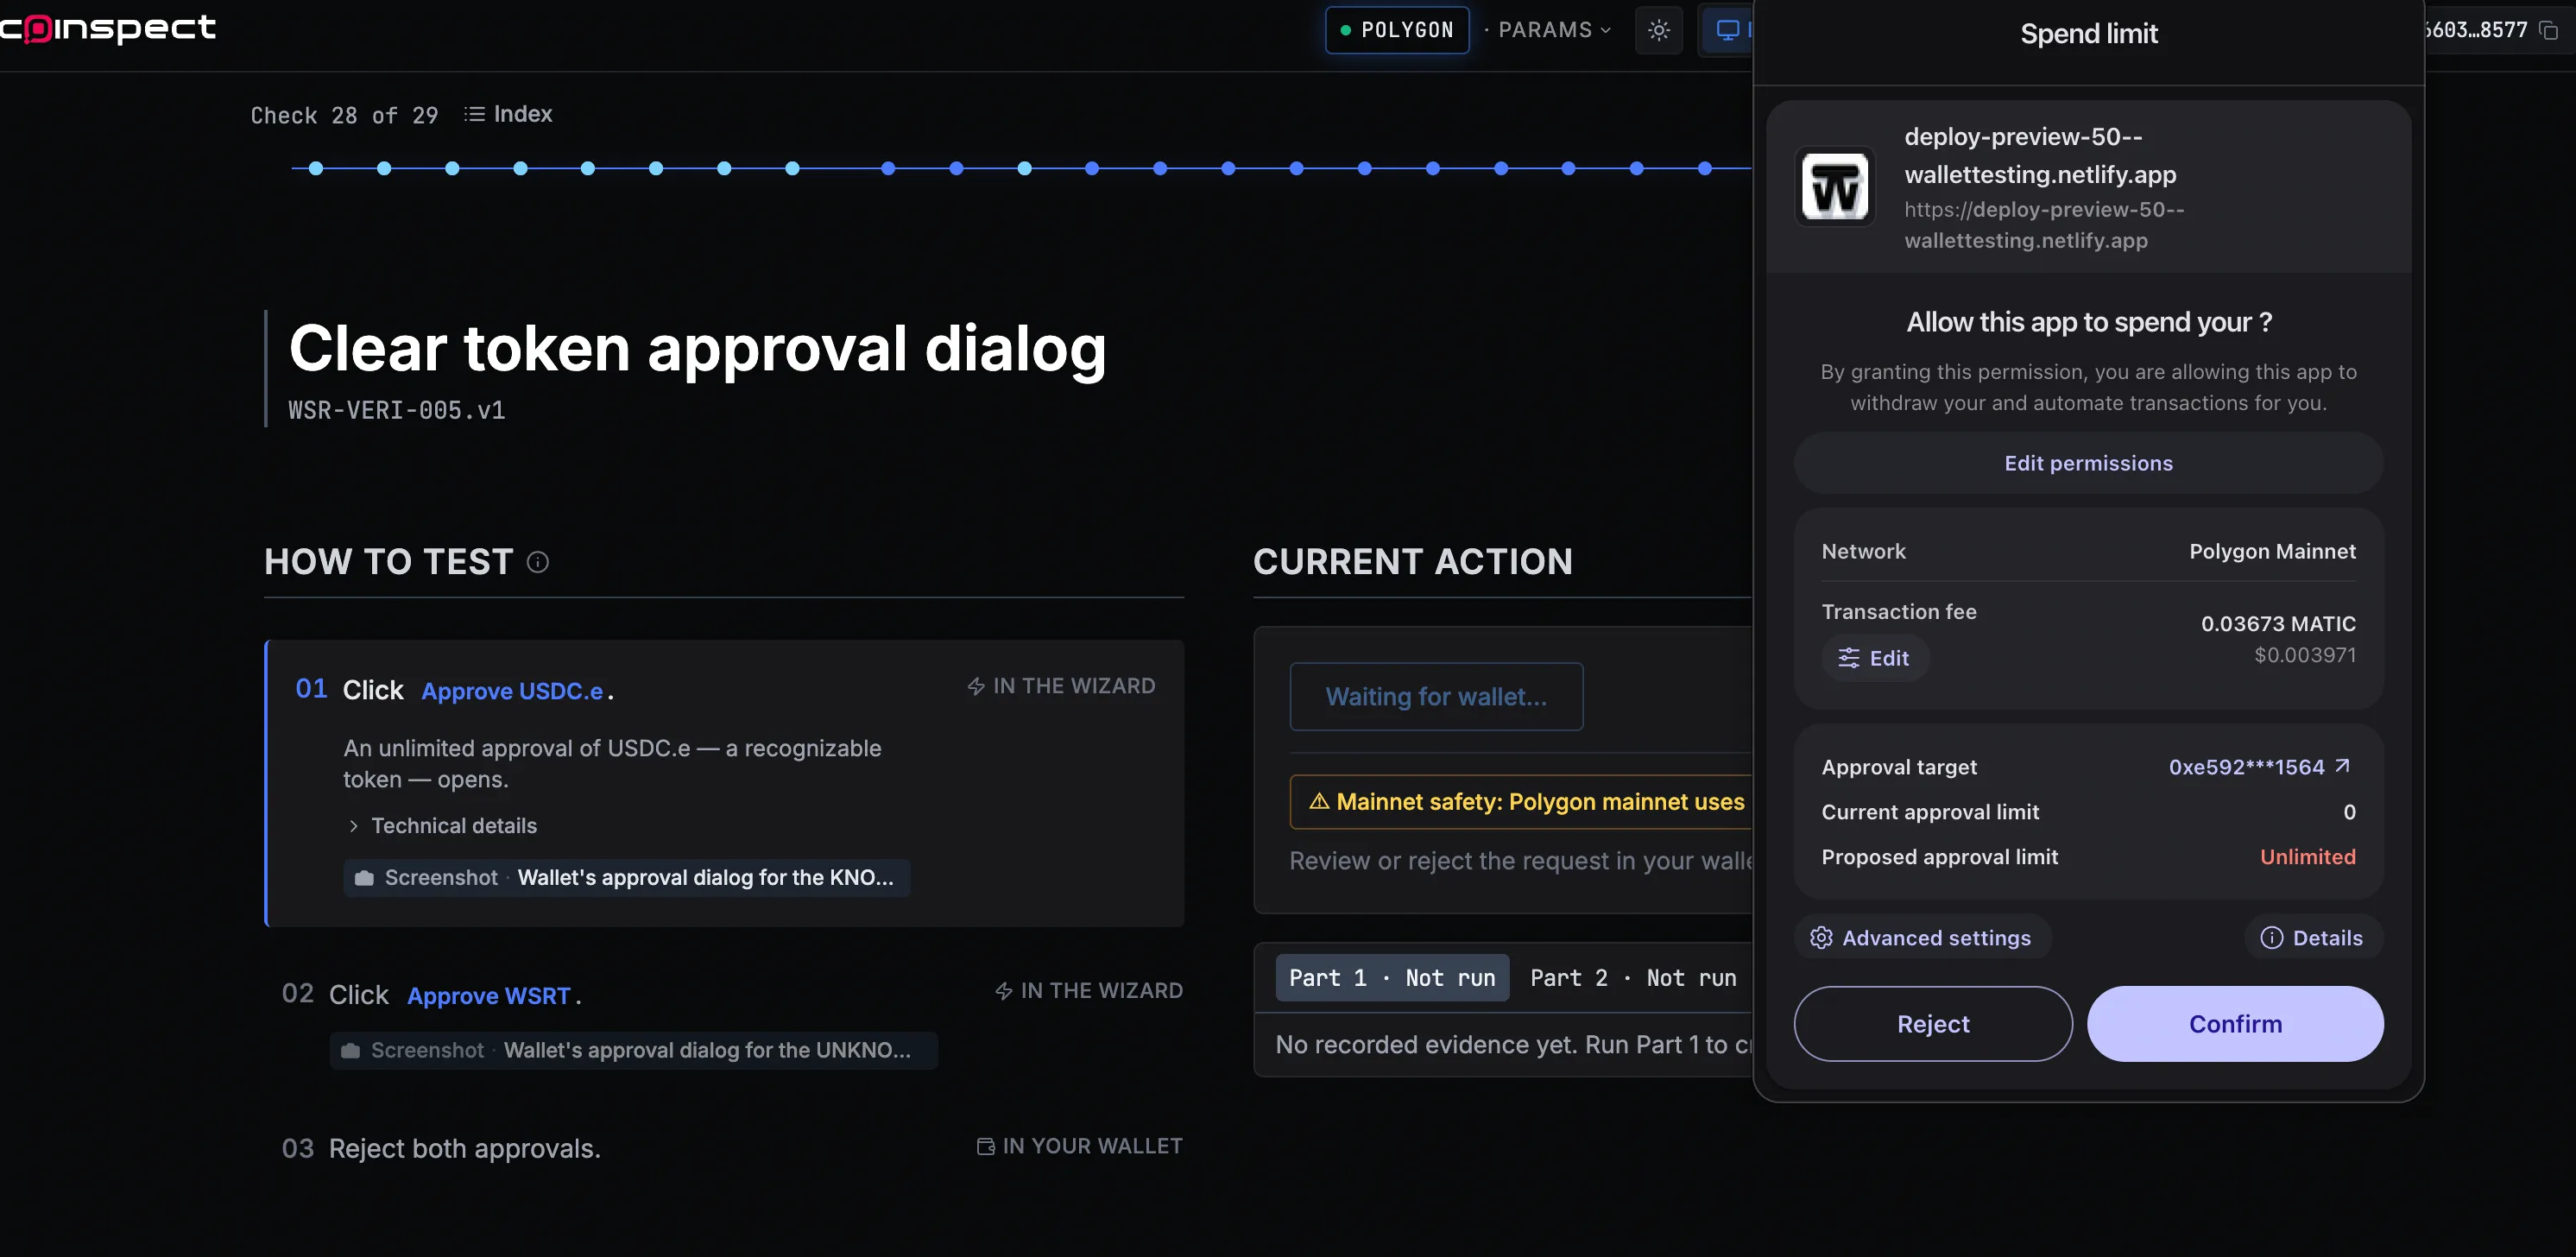
 Last updated on Sep 3, 2026Report an issue with this check
-
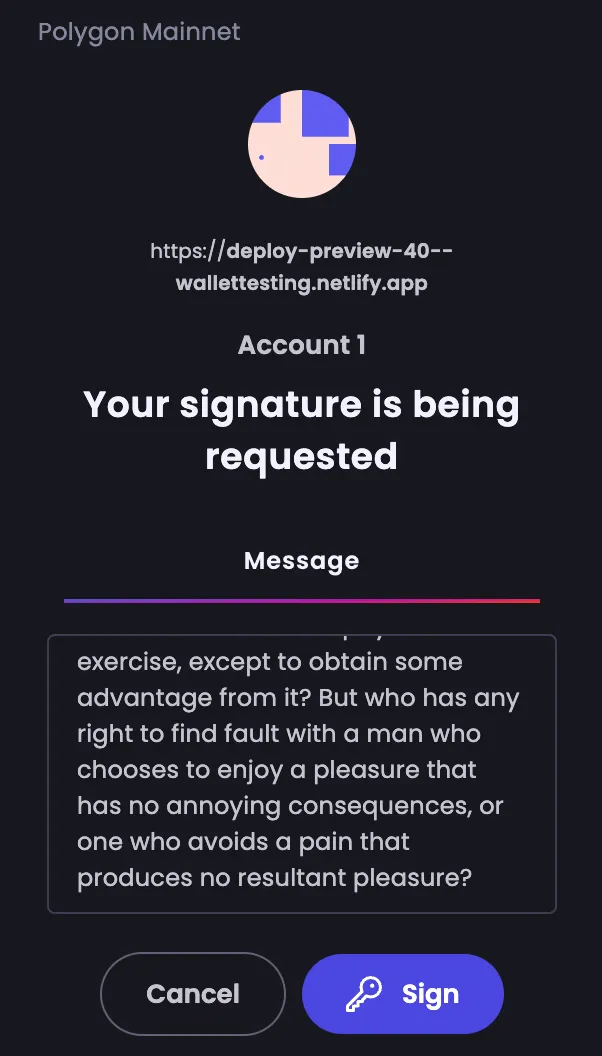
- Clear message signing dialog3.8 / 3.8Description
Clearly displays all message signature request details without truncating or hiding information.
-
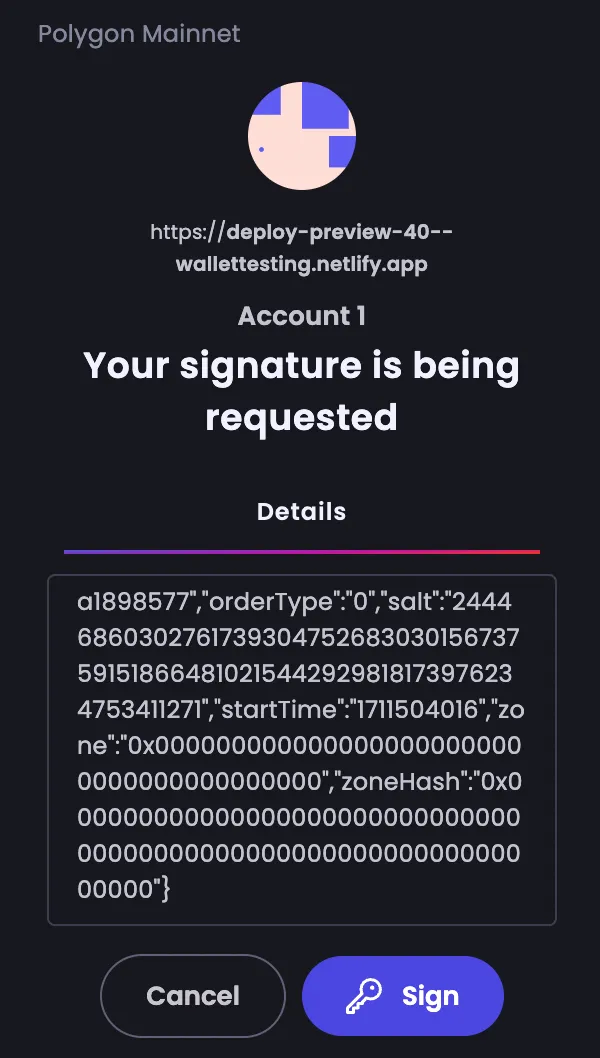
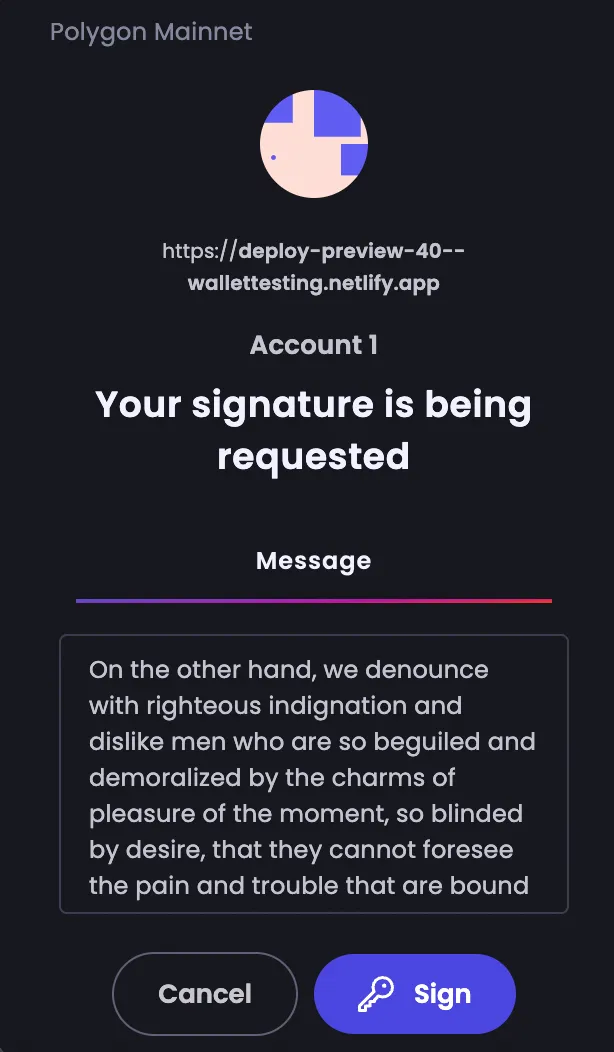
Large payloads for both `personal_sign` and `eth_signTypedData` are fully scrollable, and the `EIP712Domain`, including the `verifyingContract`.
— Verified by Sebastian Camia at Coinspect
Evidence · 4 screenshots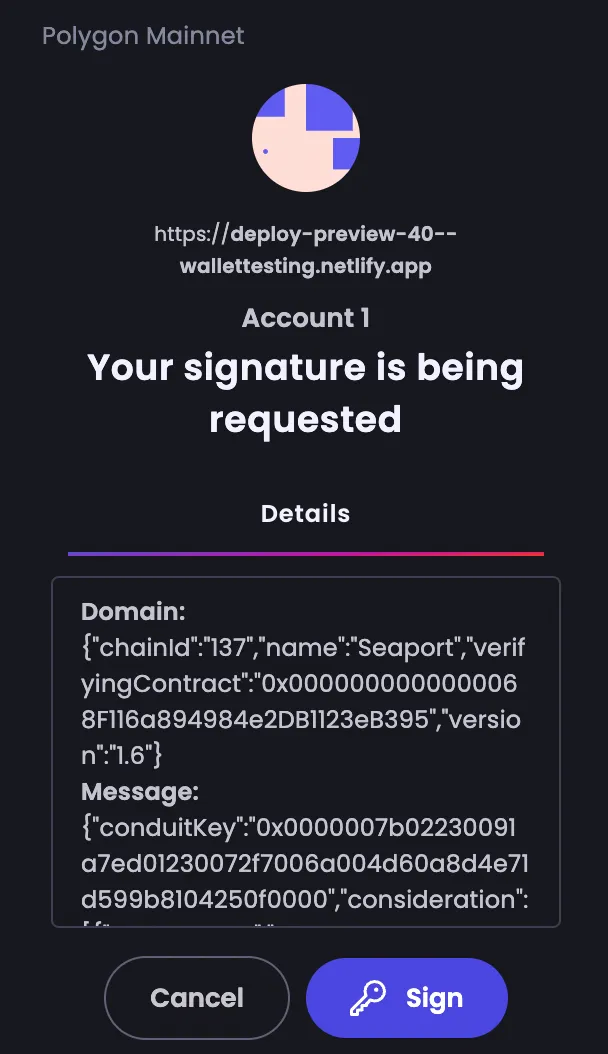
 Last updated on Sep 3, 2026Report an issue with this check
-
- EIP-712 message parsing0.0 / 2.4Description
Displays human-readable details for EIP-712 signature requests from well-known protocols.
-
The wallet renders raw JSON for the Seaport EIP-712 signature request, instead of structured human-readable details.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots Last updated on Sep 3, 2026Report an issue with this check -
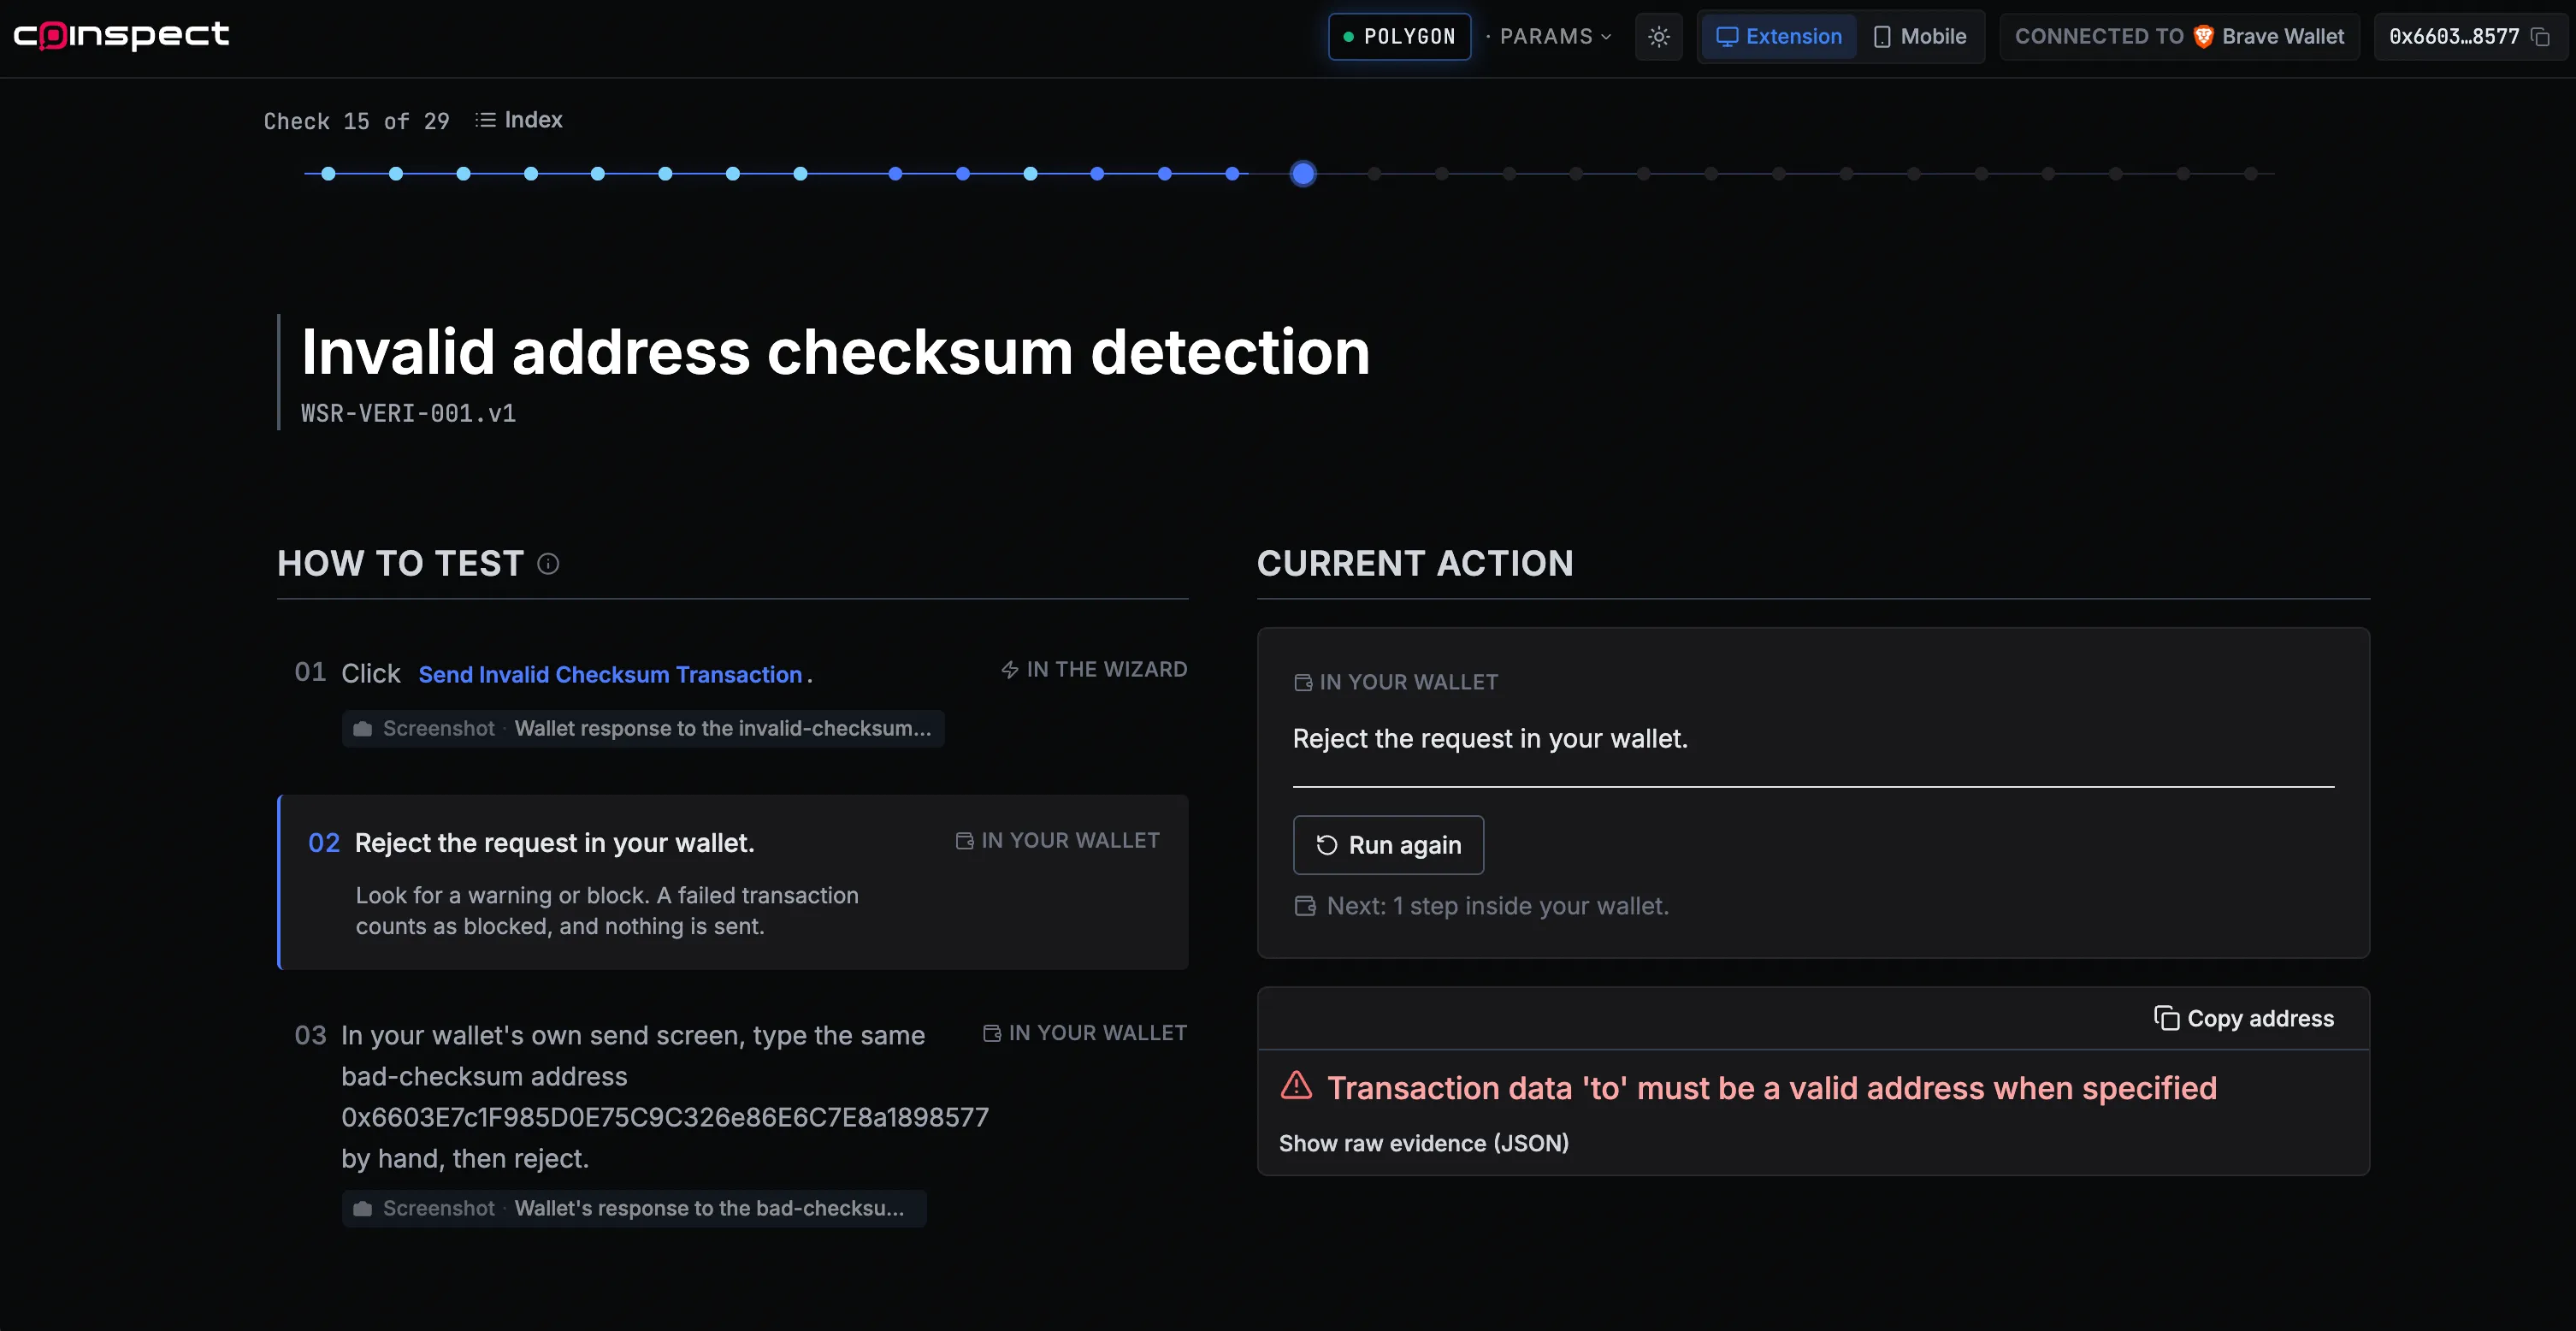
- Invalid address checksum detection2.2 / 2.2Description
Warns users when they input addresses with invalid EIP-55 checksums.
-
The wallet correctly identifies and warns the user about an incorrect EIP-55 checksum for manual transactions. For dApp transactions, the wallet blocks the transaction when an invalid address (due to incorrect checksum) is provided.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots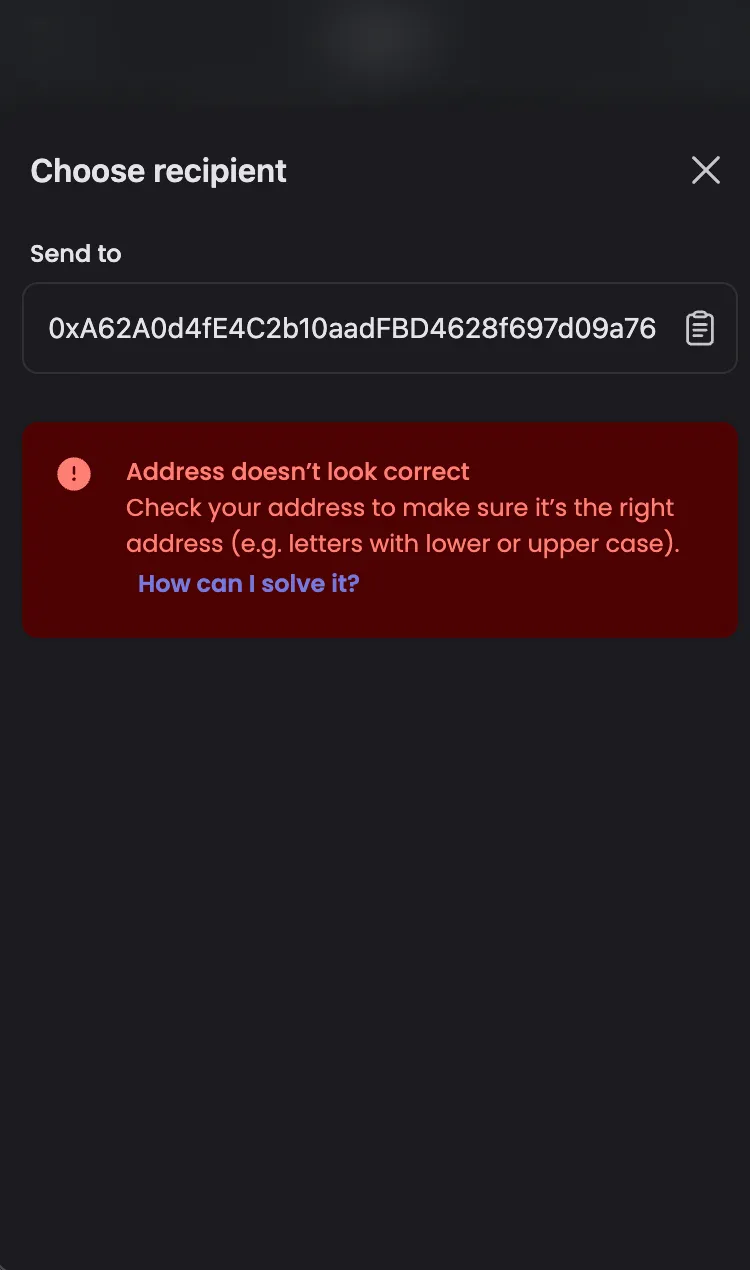
 Last updated on Sep 3, 2026Report an issue with this check
-
- Mandatory message review0.0 / 2.1Description
Requires users to review all the details before signing a message.
-
The Sign button is enabled before the user has scrolled through all the content, failing the acceptance criteria.
— Verified by Sebastian Camia at Coinspect
Evidence · 4 screenshots Last updated on Sep 3, 2026Report an issue with this check -
- Links to blockchain explorers1.2 / 1.2Description
Provides clickable links to block explorers for at least one key blockchain identifier.
-
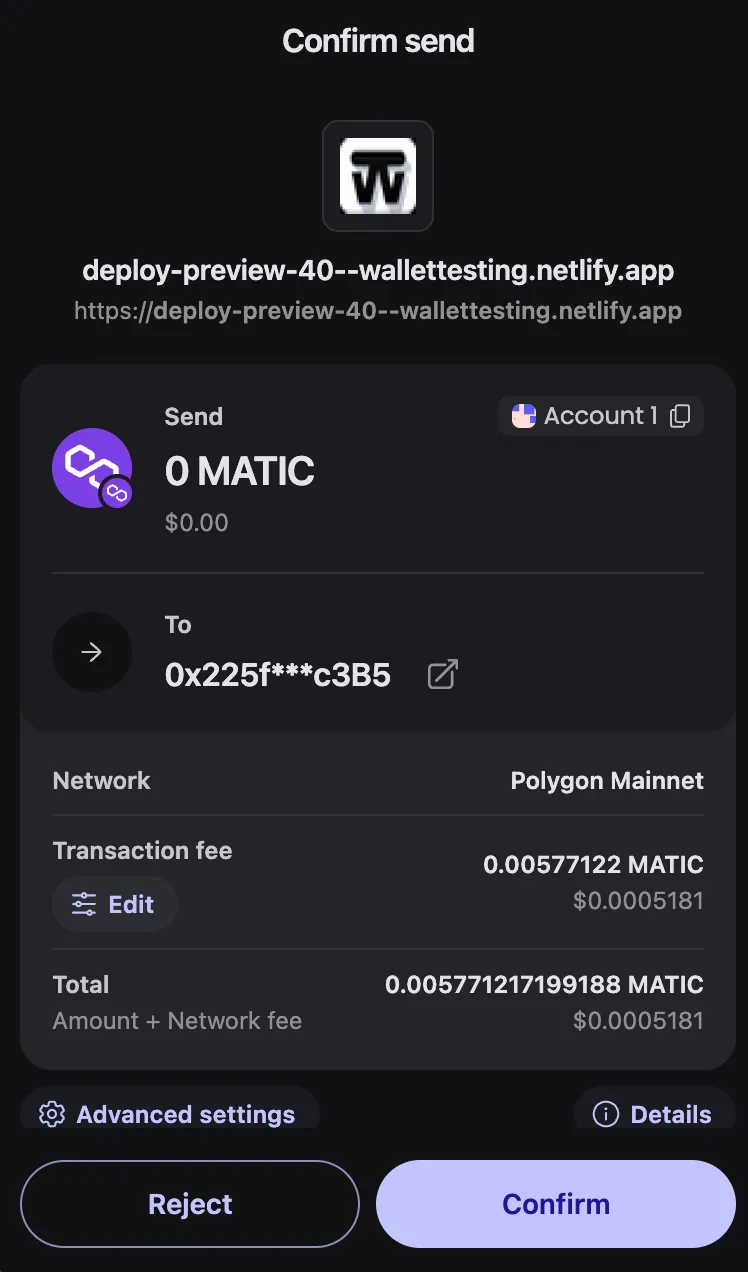
Addresses, contract addresses and transaction hashes are clickable and open a block explorer both when attempting to send a transaction and querying the wallet history.
— Verified by Sebastian Camia at Coinspect
Evidence · 2 screenshots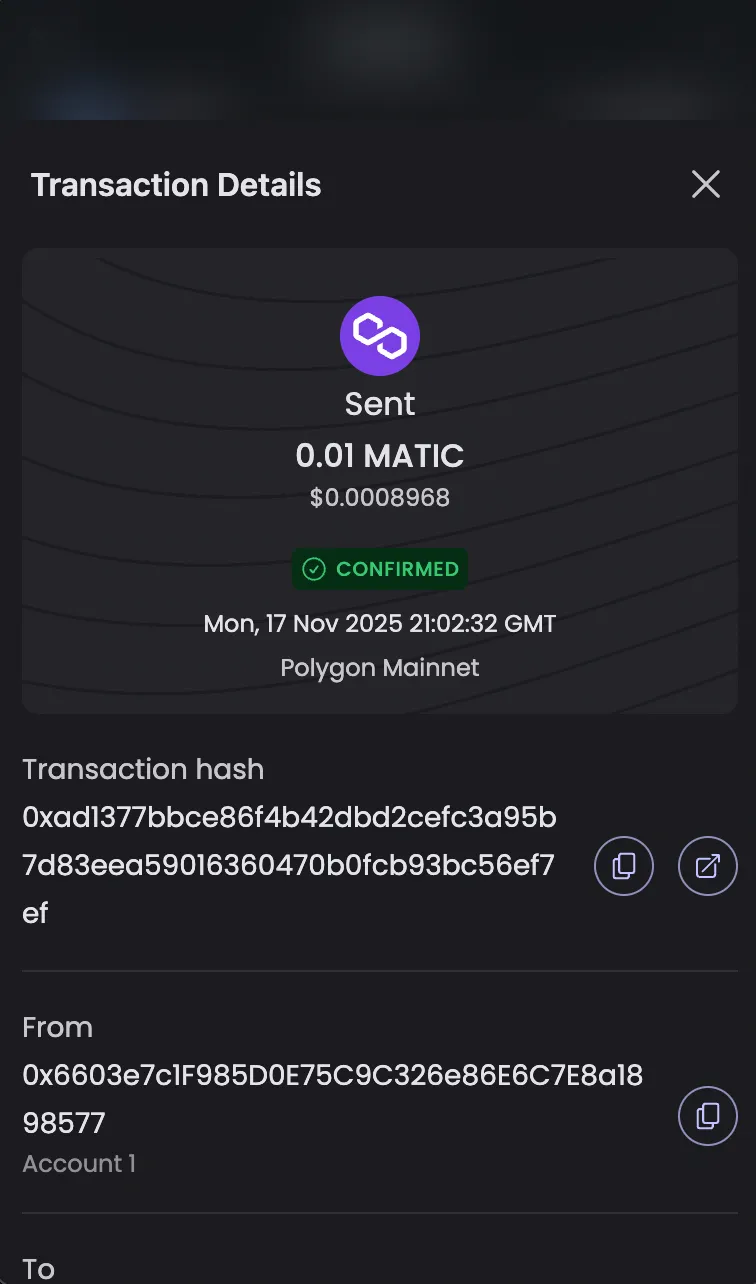
 Last updated on Sep 3, 2026Report an issue with this check
-
Physical Access
- Seed phrase access control6.6 / 6.6Description
Requires authentication to access seed phrases or private keys.
-
A password is required before the user can continue to back up their wallet.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot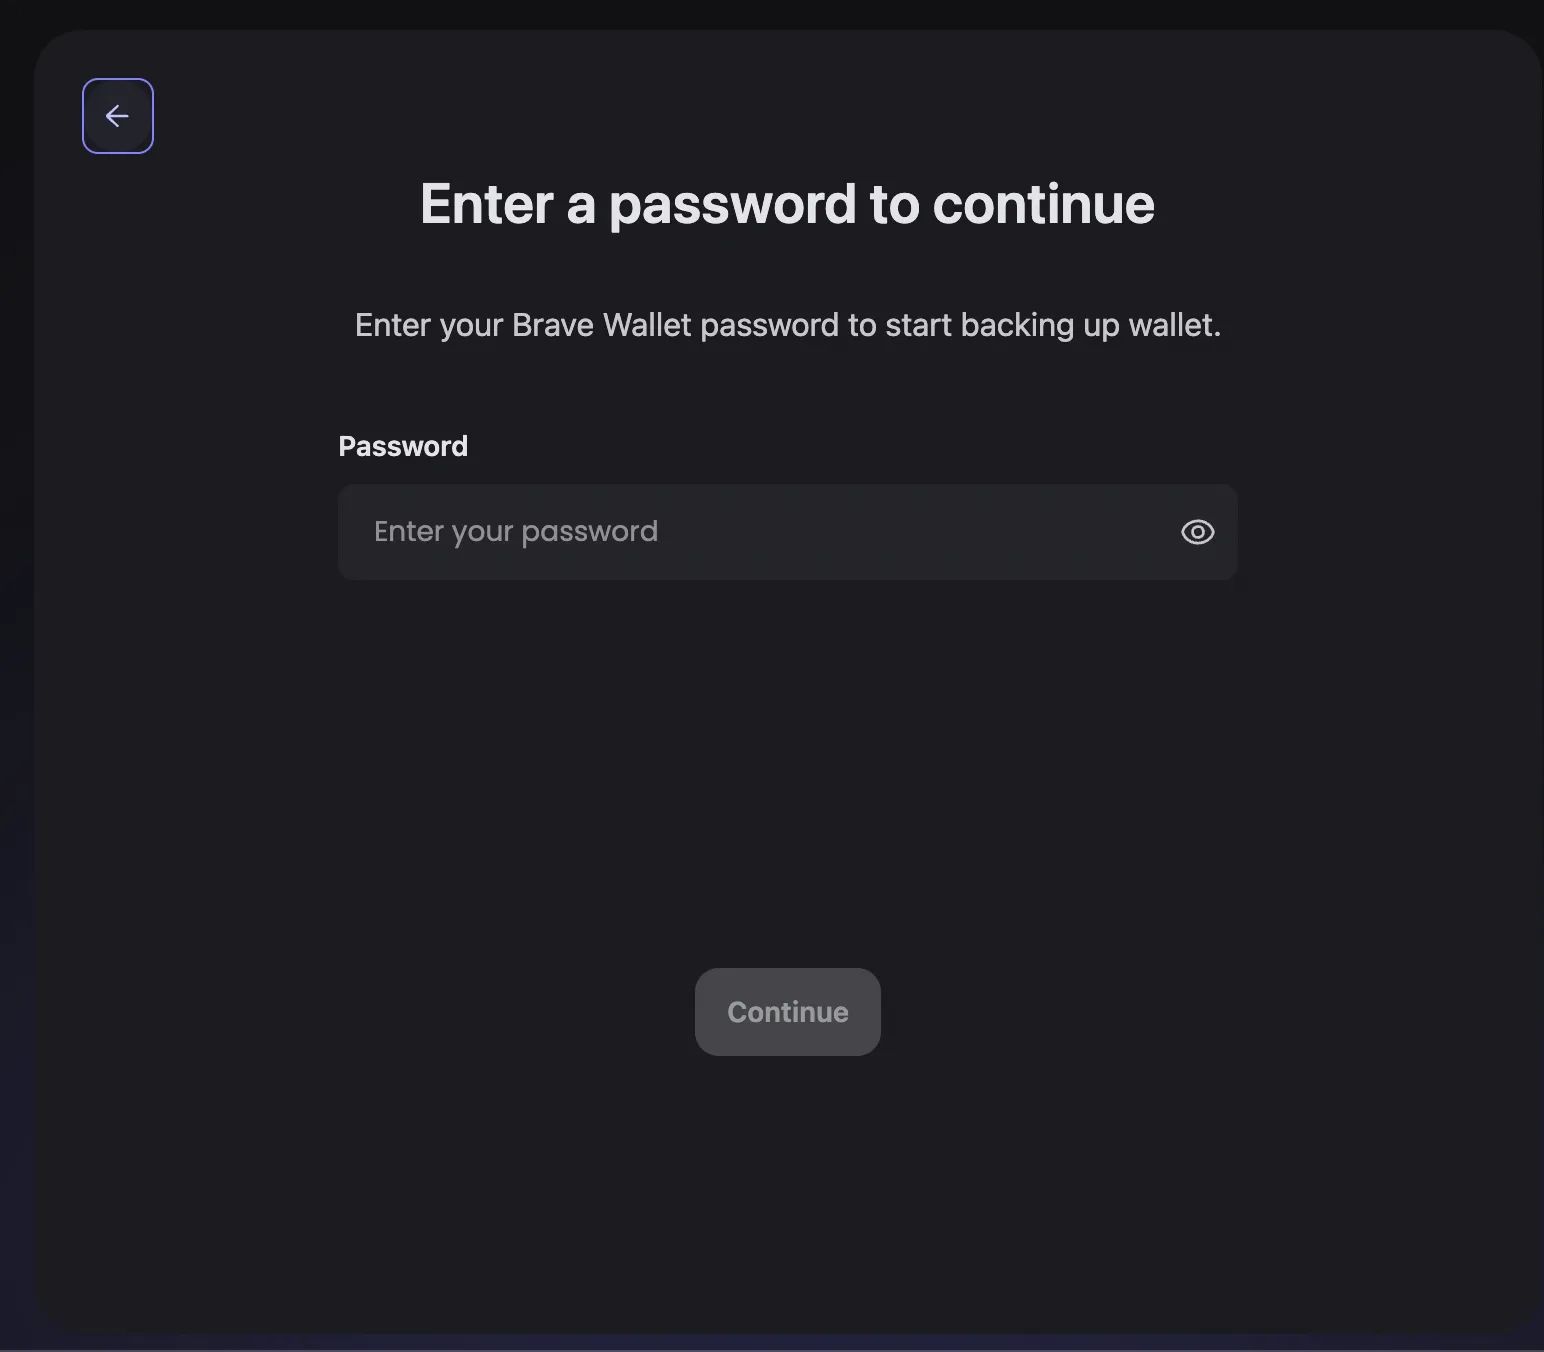 Last updated on Sep 3, 2026Report an issue with this check
-
- Manual wallet lock3.4 / 3.4Description
Allows users to lock it manually.
-
The wallet UI contains a "Lock wallet" button in the portfolio menu.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot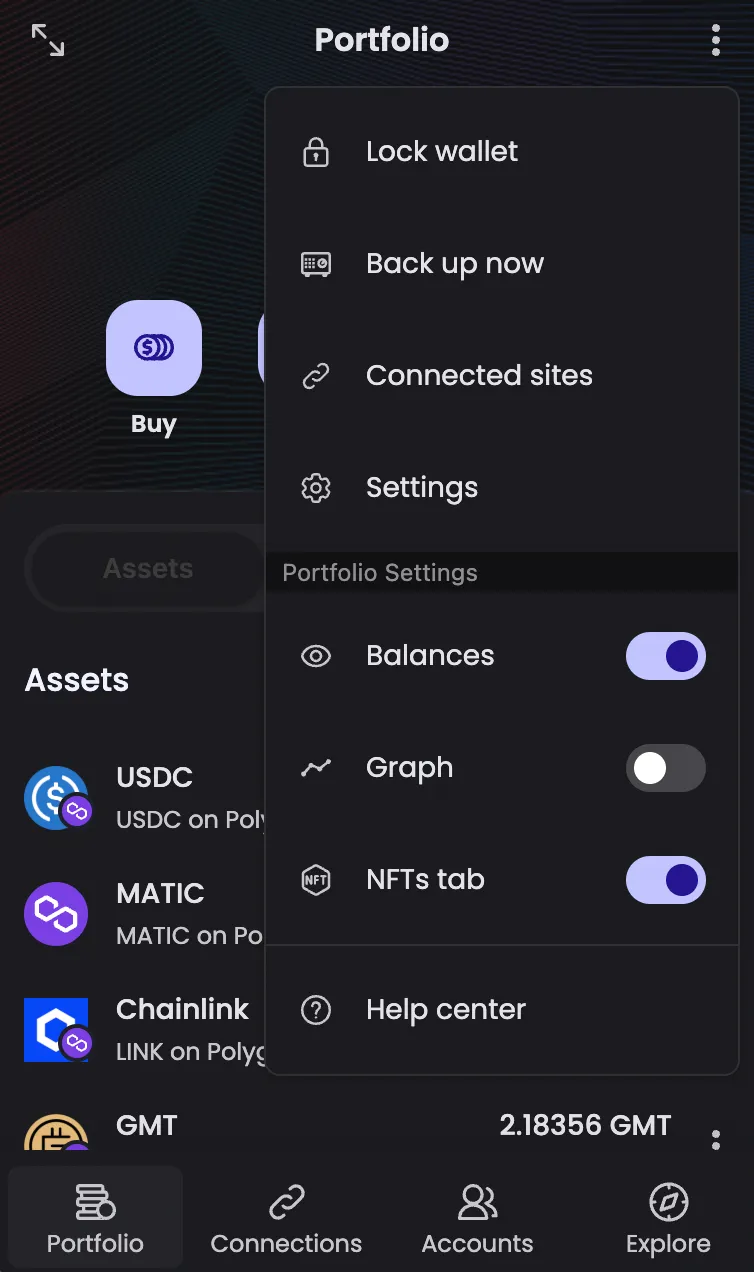 Last updated on Sep 3, 2026Report an issue with this check
-
- Automatic wallet lock3.4 / 3.4Description
Verifies wallet auto-locks on inactivity.
-
The wallet has an auto-lock setting that defaults to 5 minutes, as indicated by the screenshot. The wallet auto-locks after inactivity within 20 minutes.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot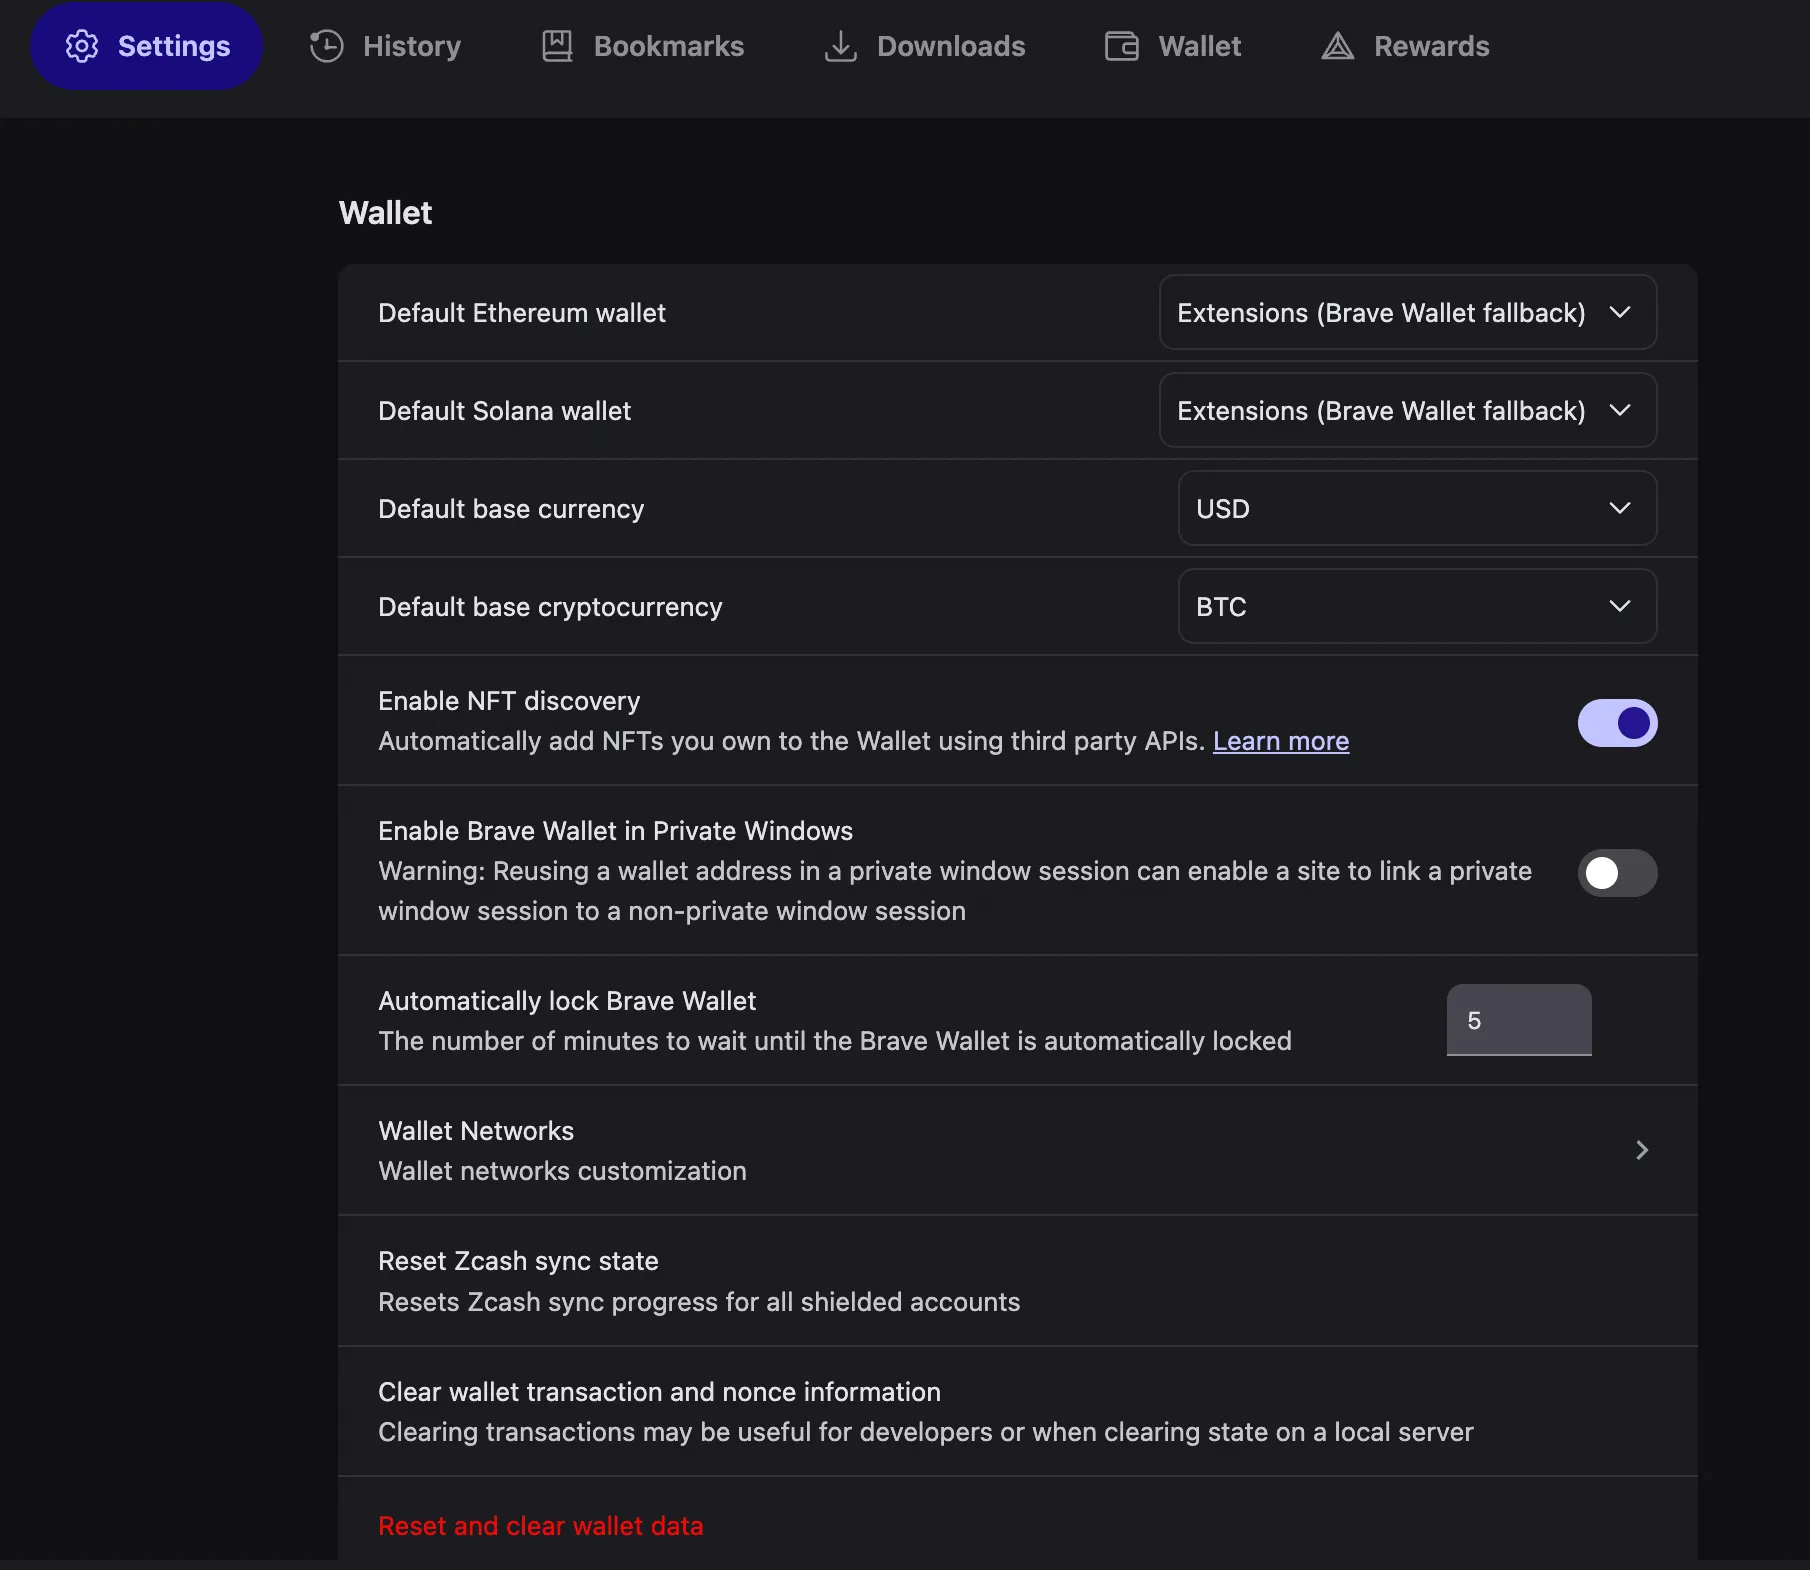 Last updated on Sep 3, 2026Report an issue with this check
-
- Robust Authentication0.0 / 3.2Description
Uses strong authentication, such as resistance to trivial or commonly-used passwords.
-
The wallet allows '11111111' as a valid password, which is considered a trivial password. The application should prevent users from using such passwords.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot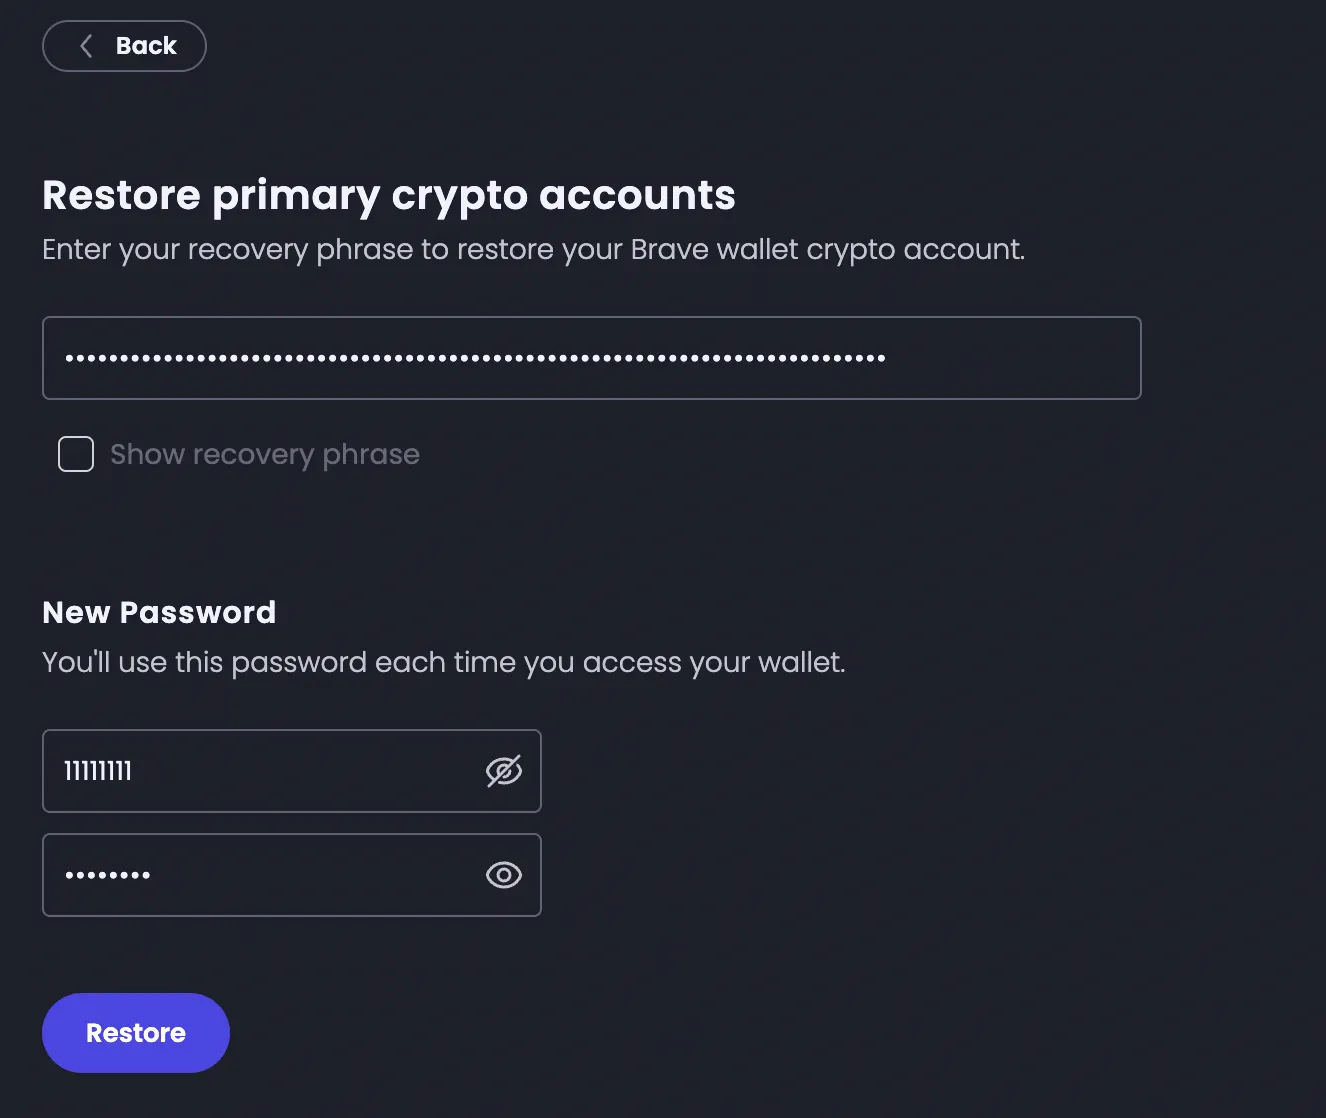 Last updated on Sep 3, 2026Report an issue with this check
-
- Seed phrase access warning1.8 / 1.8Description
Warns users of the risk before allowing access to seed phrases or private keys.
-
The risks of sharing the recovery phrase are clearly communicated before revealing it.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot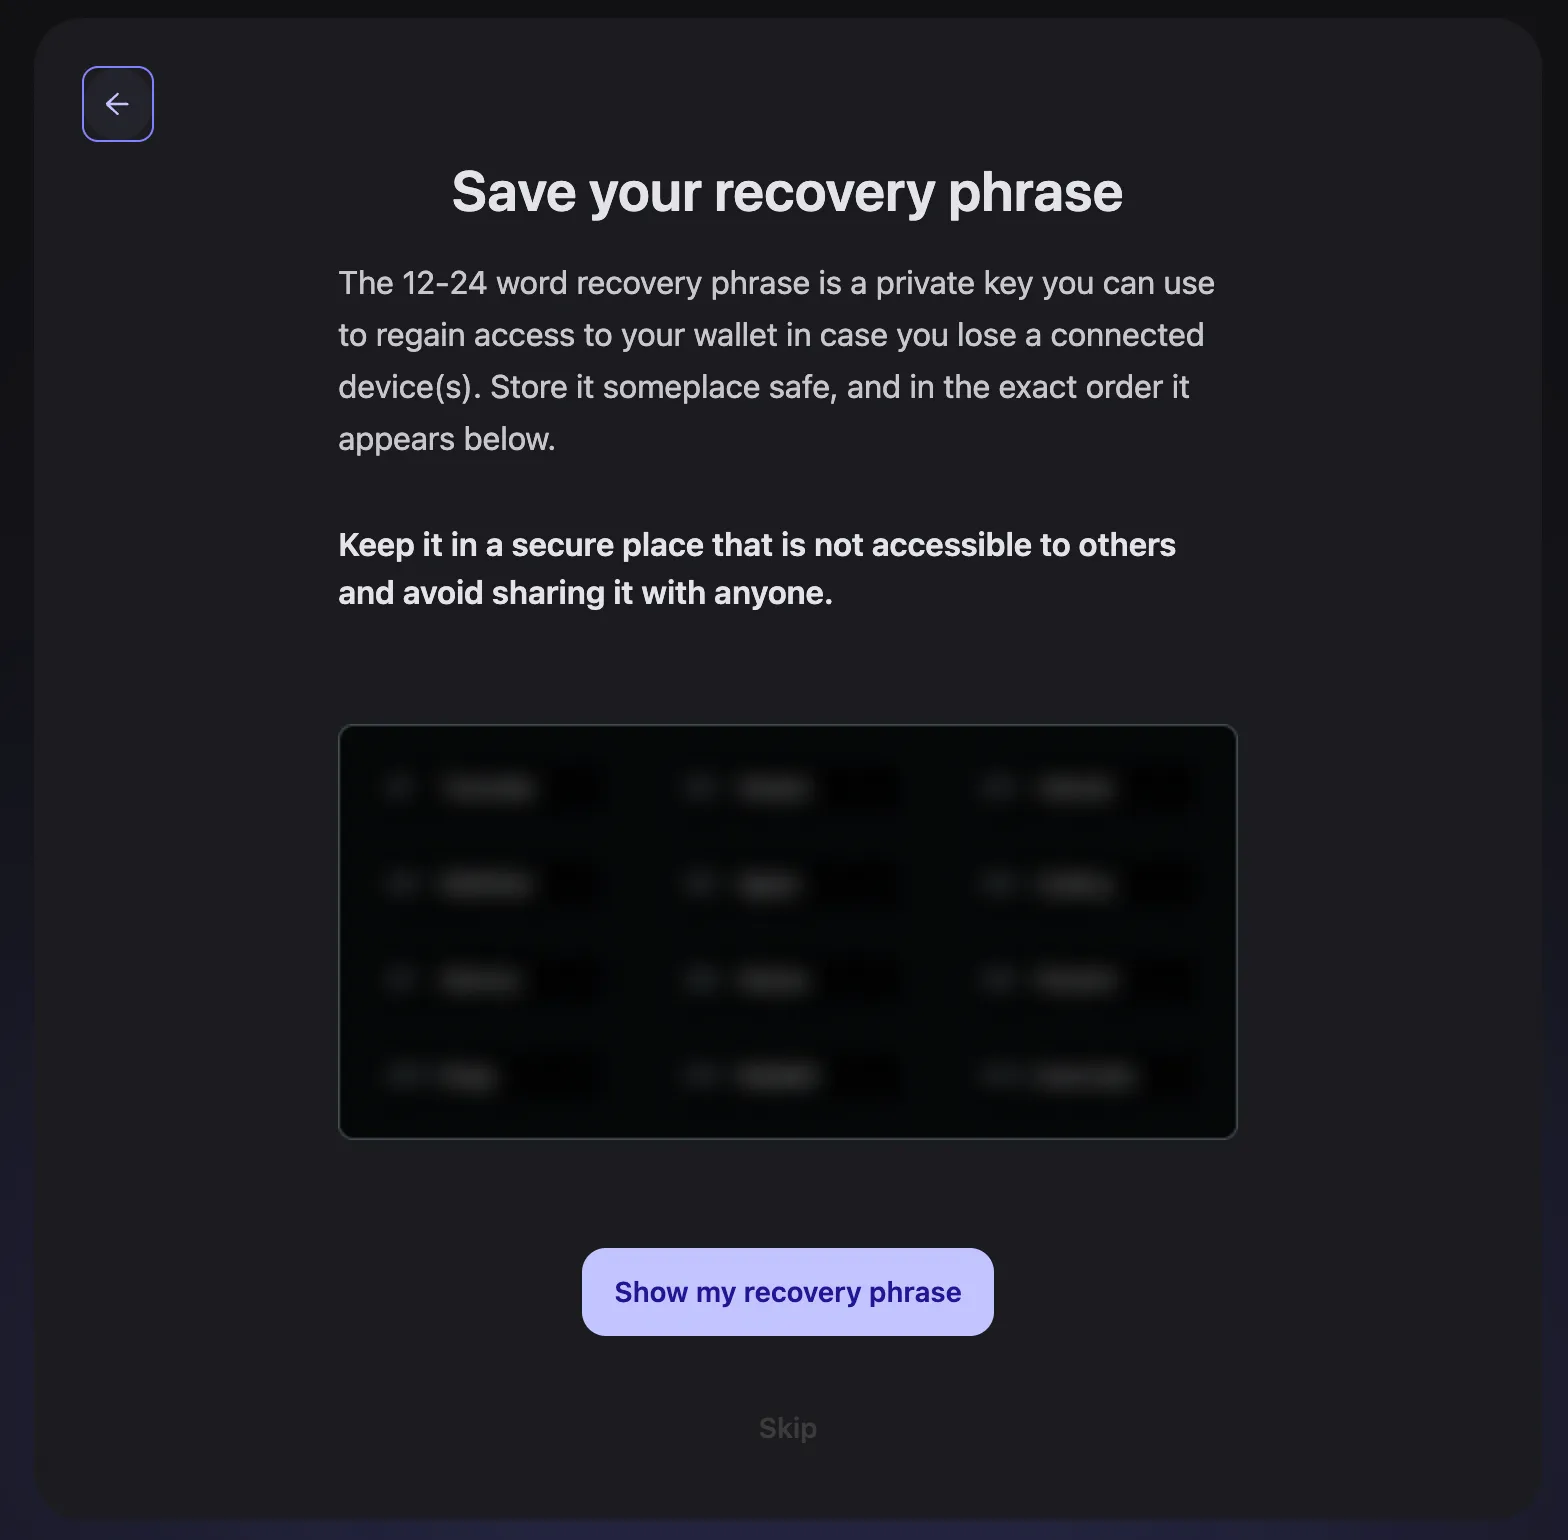 Last updated on Sep 3, 2026Report an issue with this check
-
- Clipboard seed phrase leak prevention1.8 / 1.8Description
Limits exposure of secrets by restricting or warning on copying seed phrases or taking screenshots.
-
The wallet allows copying mnemonics to the clipboard but these secrets are present for less than one minute (five seconds).
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot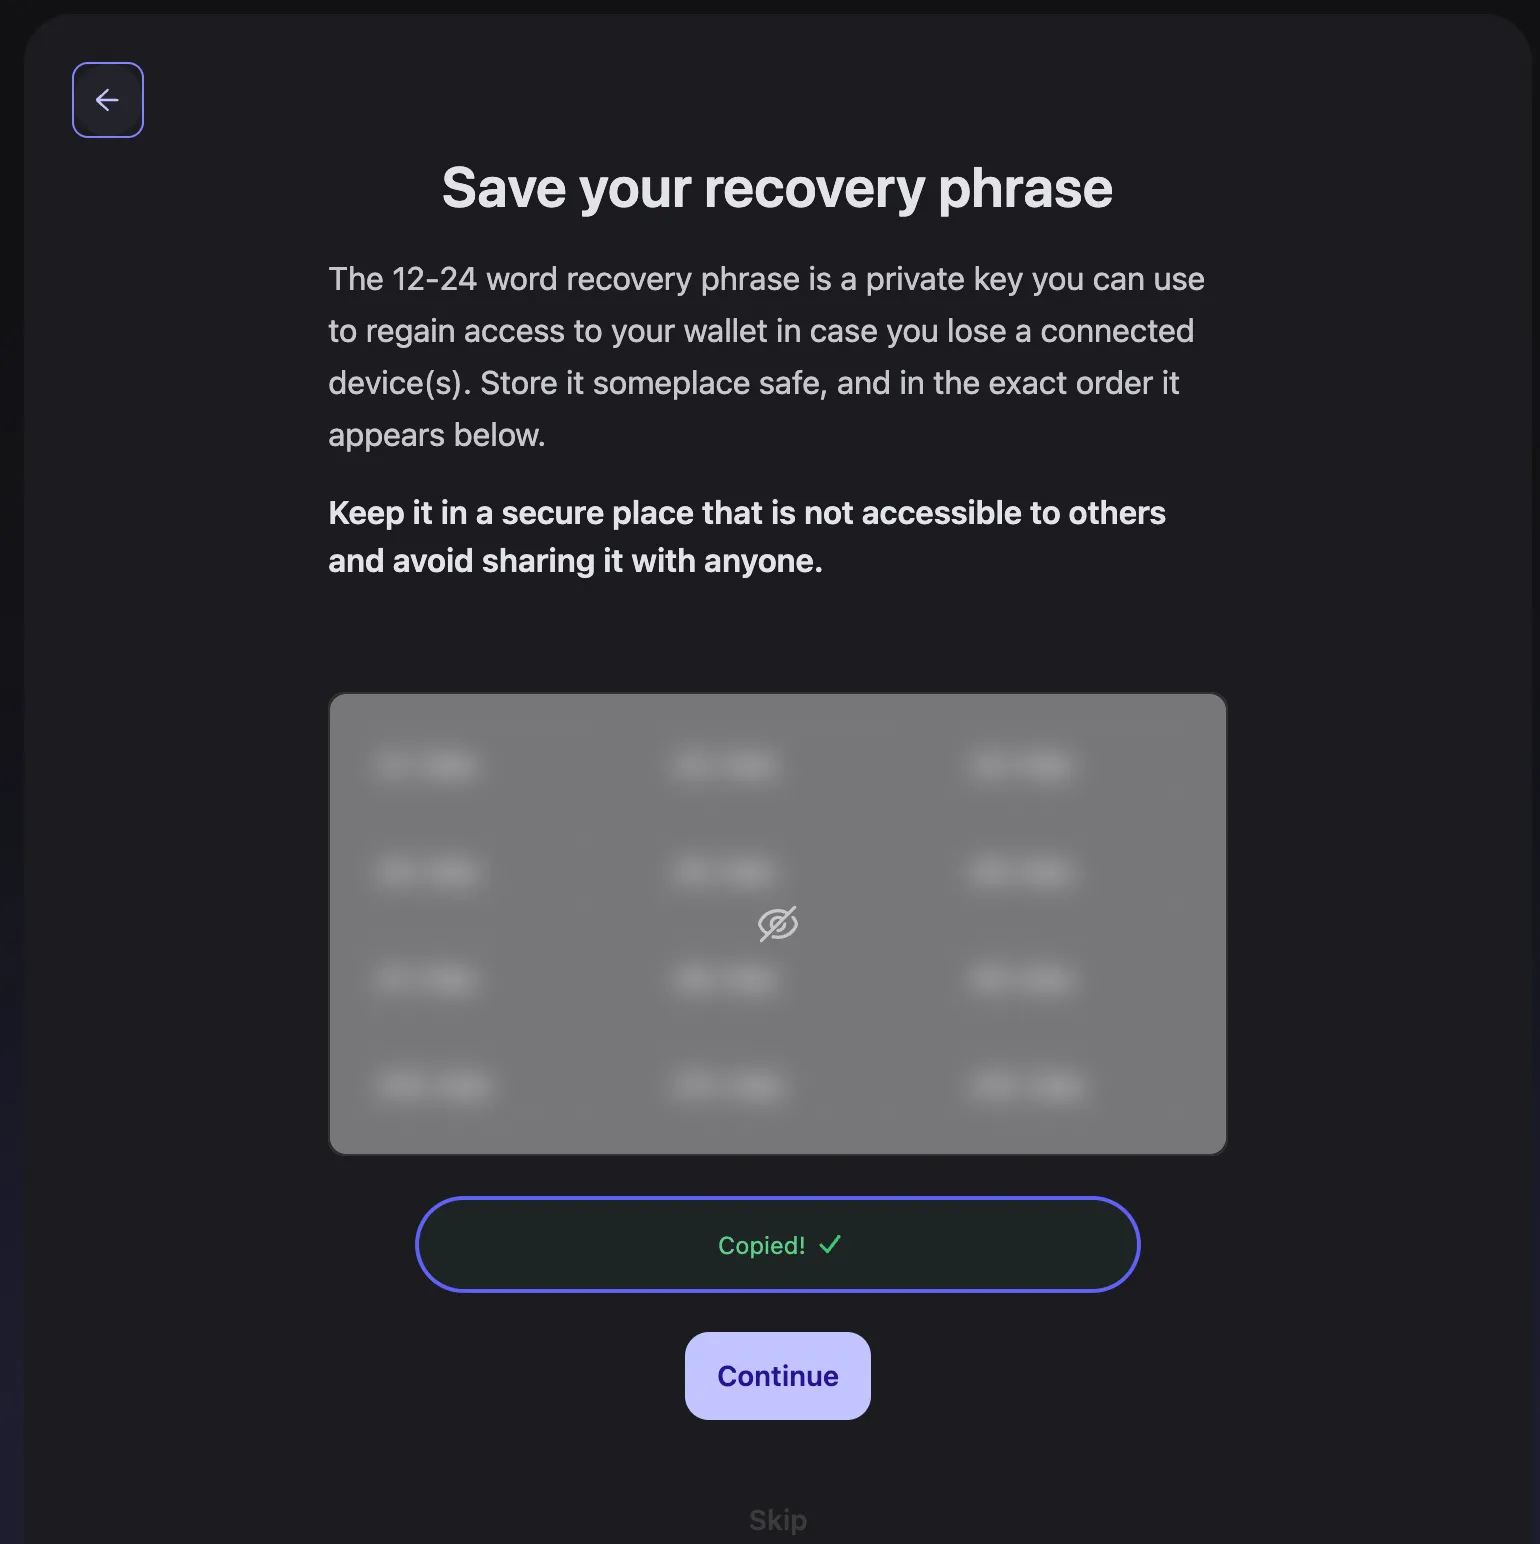 Last updated on Sep 3, 2026Report an issue with this check
-
Threat Prevention
- Malicious and poisoned address detection0.0 / 5.1Description
Prevents or alerts users about interactions with a known malicious address or a lookalike (poisoned) address.
-
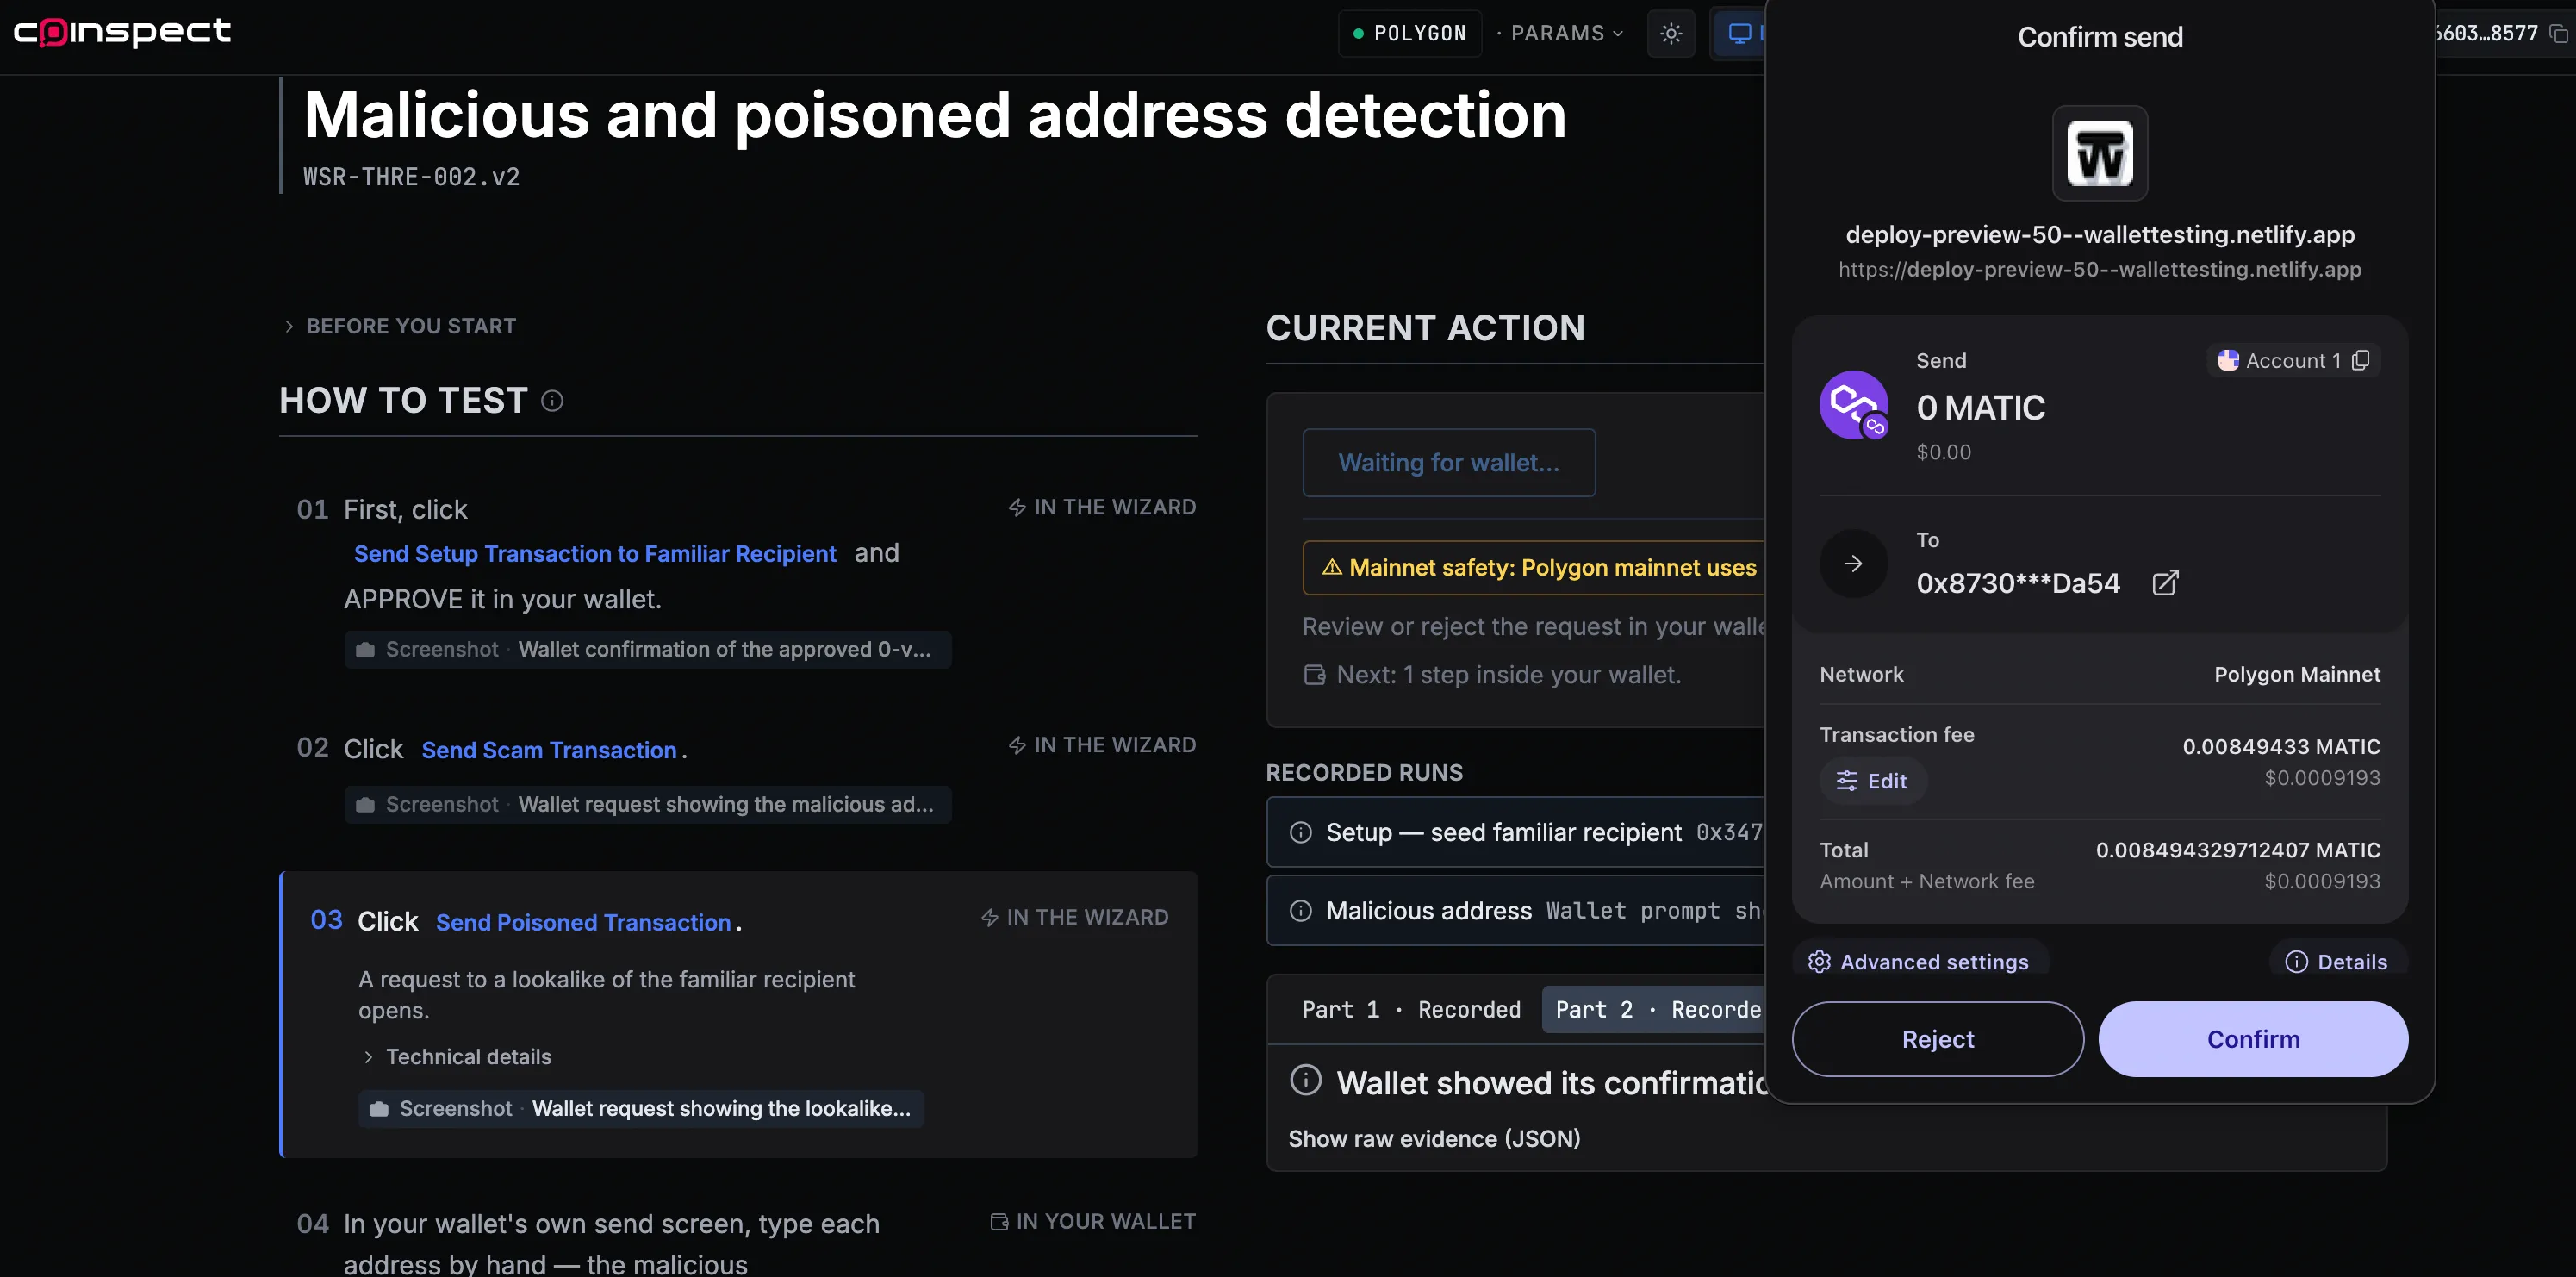
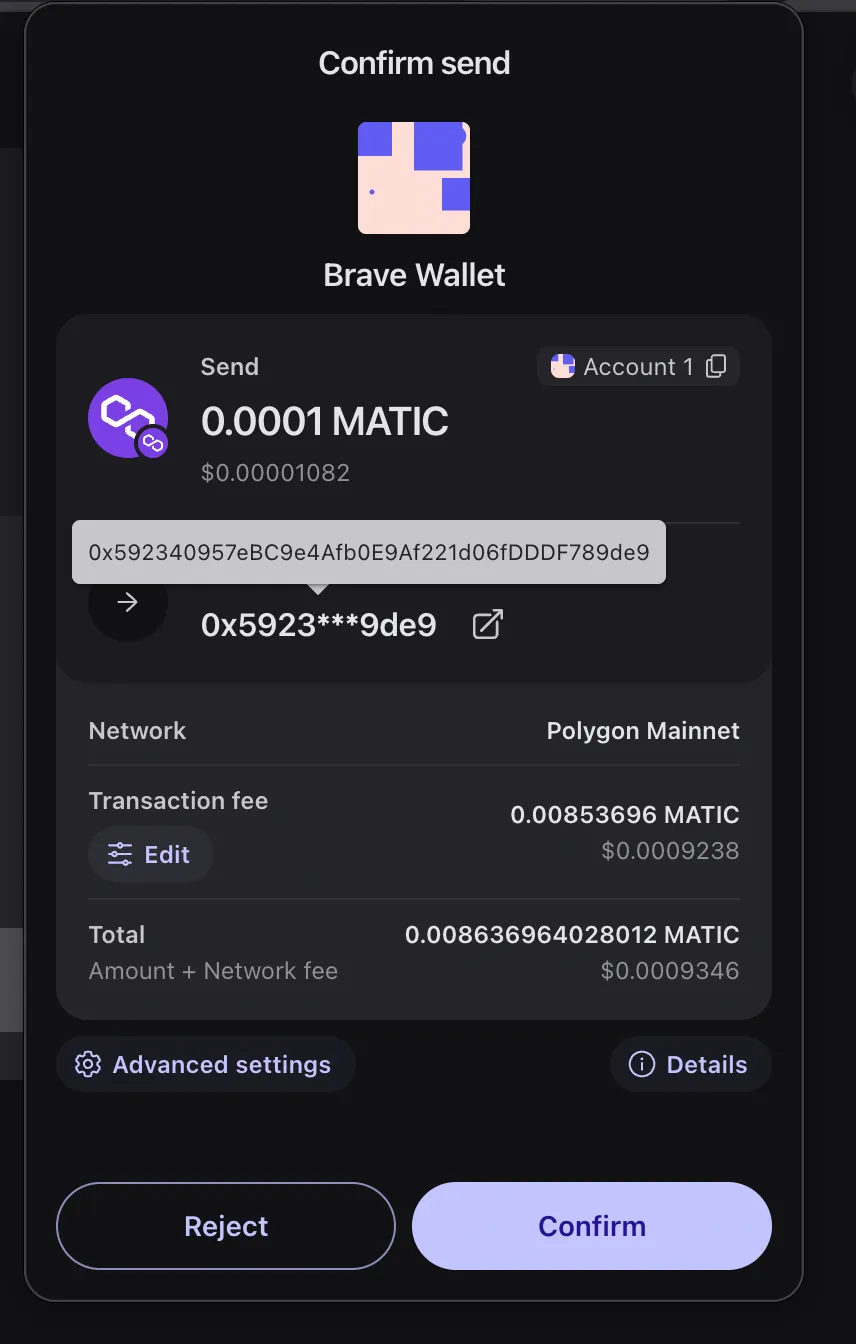
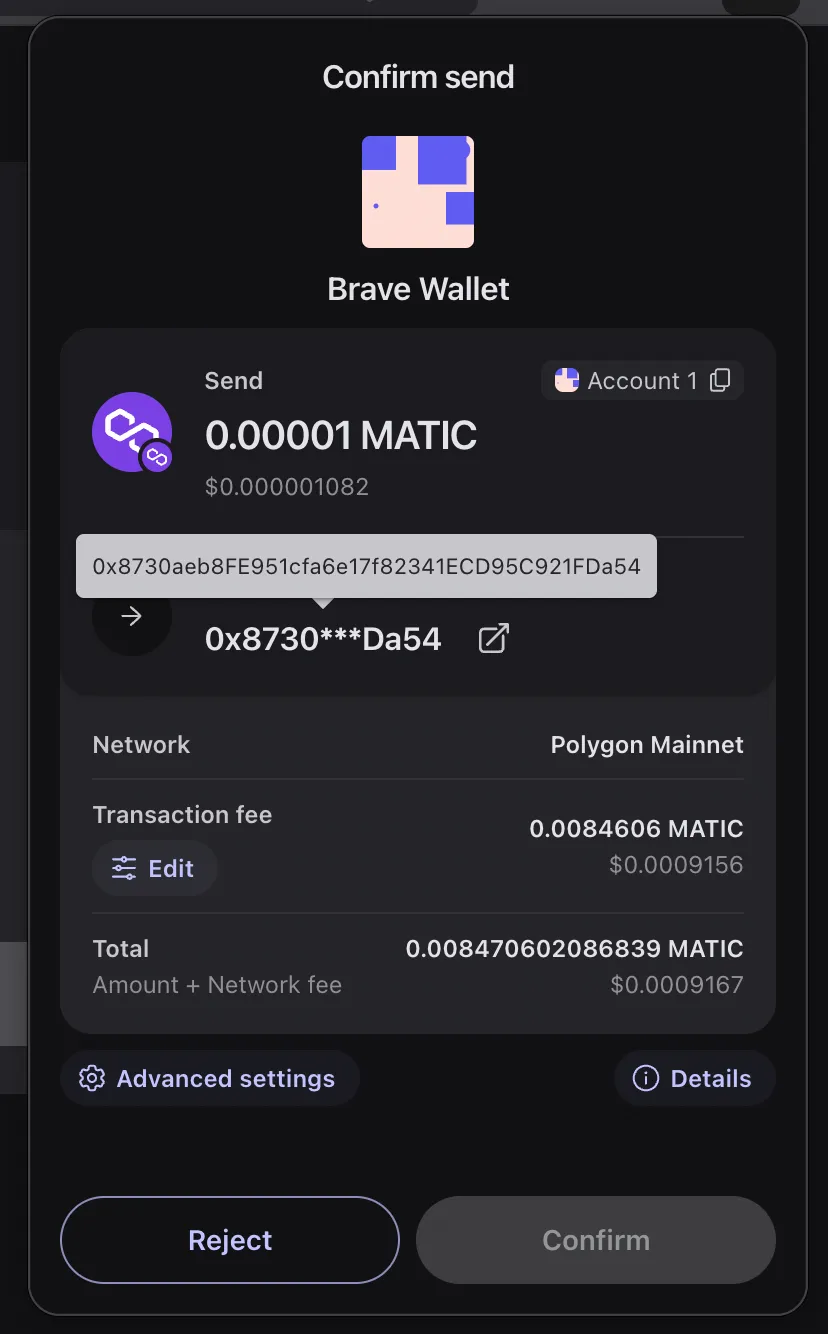
The wallet did not warn, flag, or block transactions to the known malicious address 0x592340957eBC9e4Afb0E9A221d06fDDF789de9 or the lookalike address 0x8730aeb8FE951cfa6e17f82341ECD95C921FDa54, whether entered manually or via the dApp.
— Verified by Sebastian Camia at Coinspect
Evidence · 4 screenshots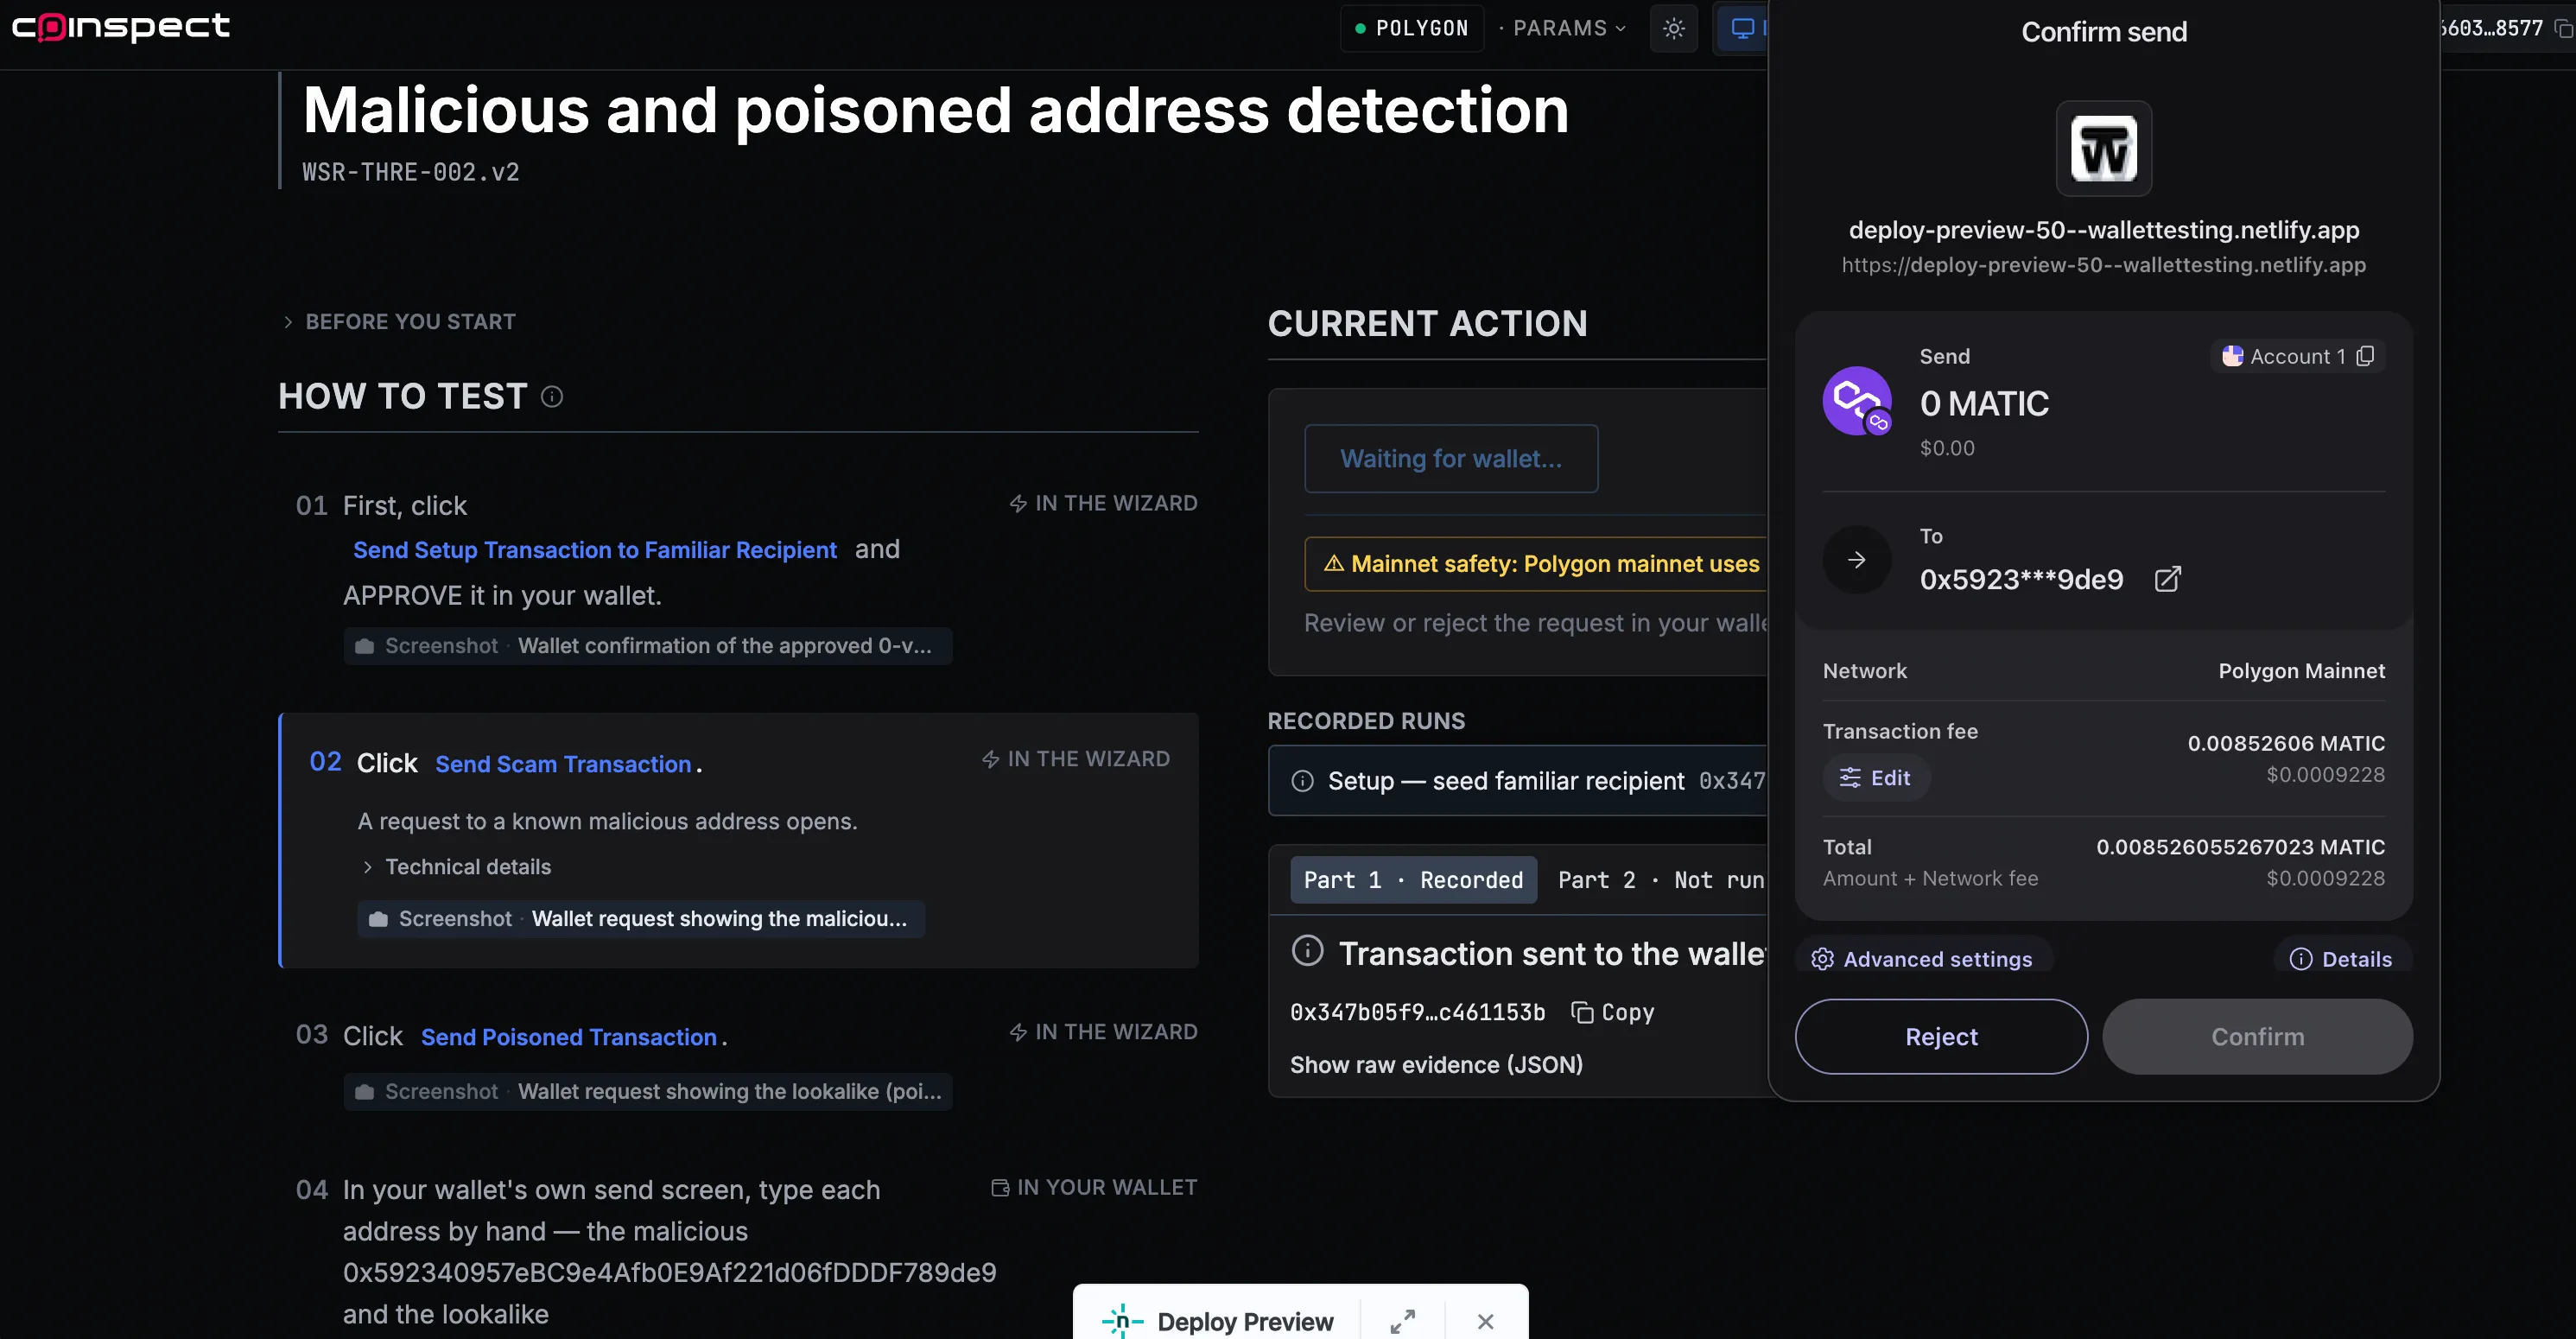
 Last updated on Sep 3, 2026Report an issue with this check
-
- Phishing dApp detection0.0 / 5.1Description
Prevents or alerts users about interactions with a known malicious URL.
-
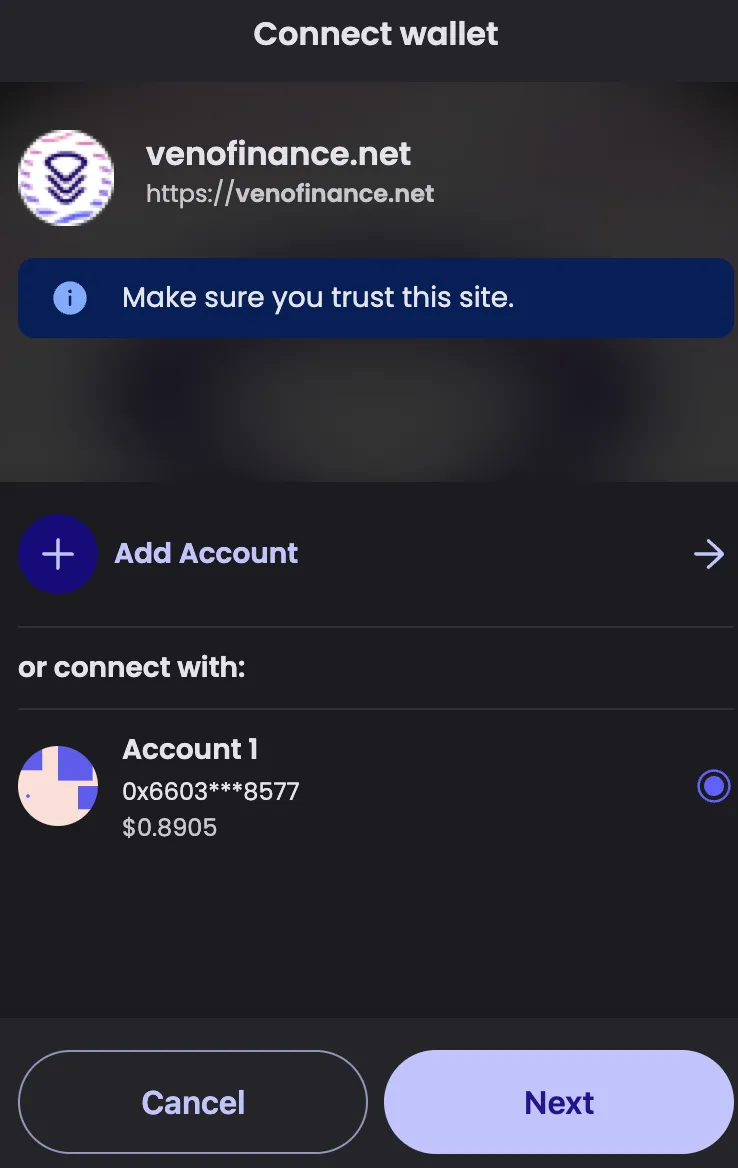
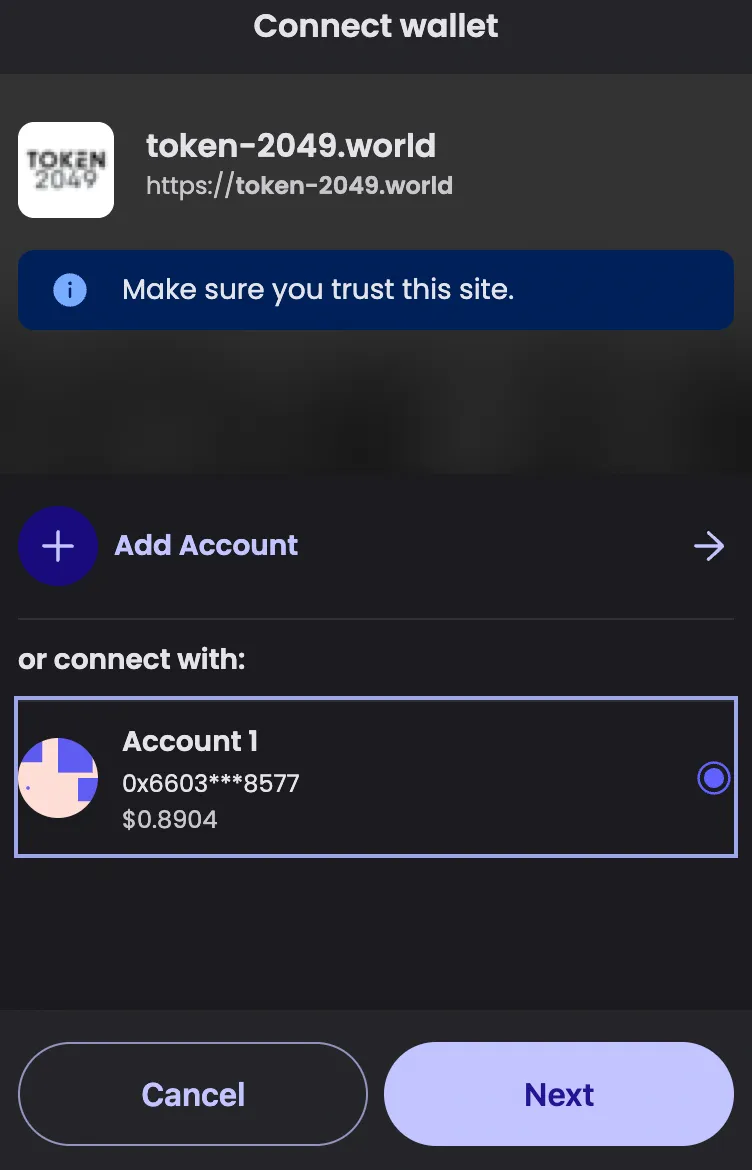
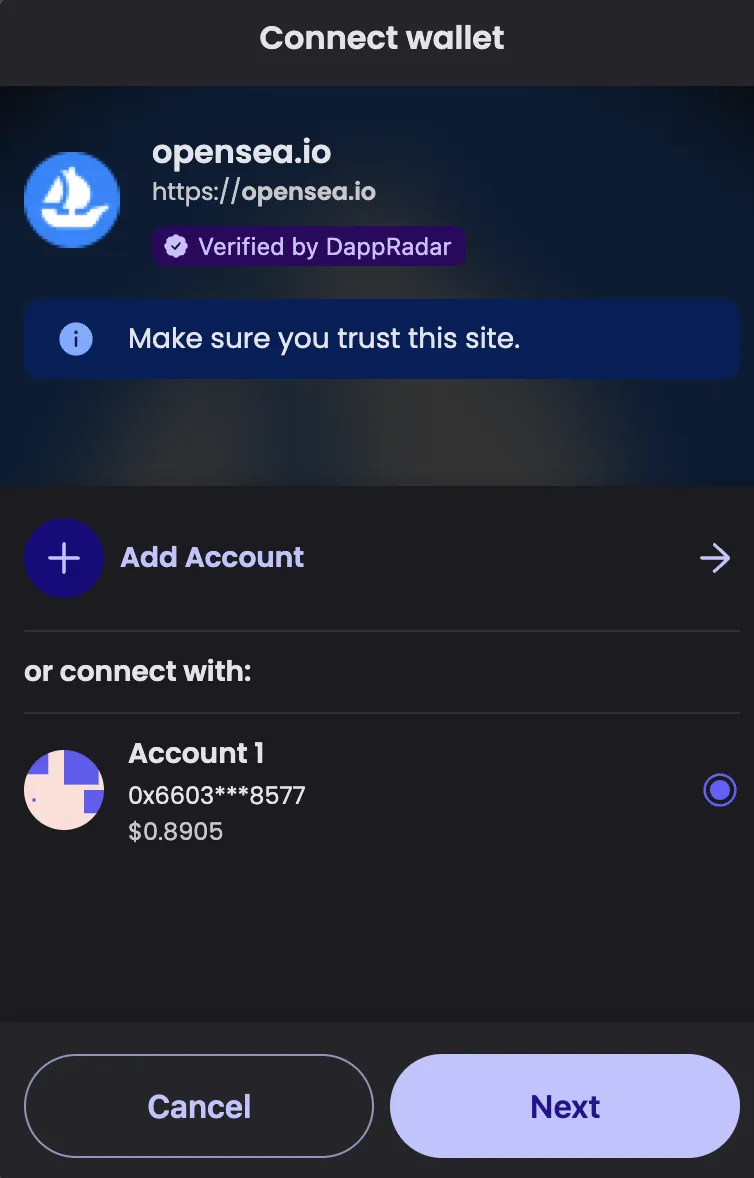
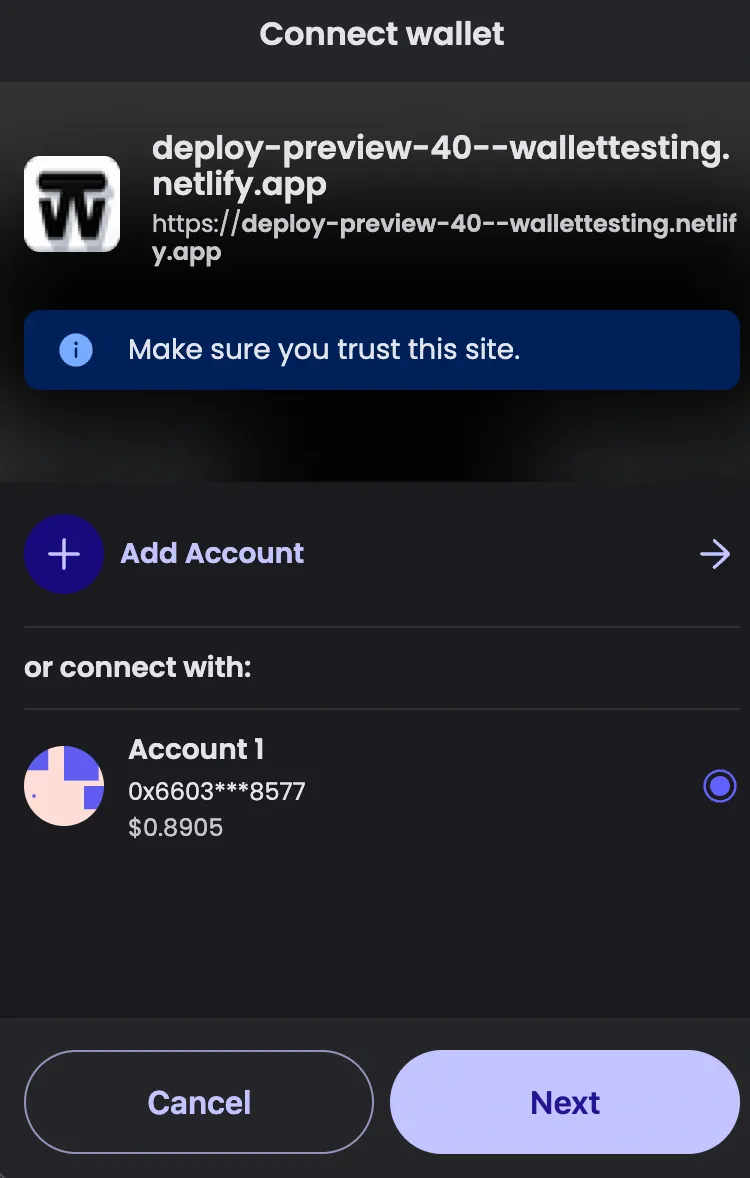
The wallet does not display any phishing warning for the listed URLs. It only displays 'Make sure you trust this site.'
— Verified by Sebastian Camia at Coinspect
Evidence · 3 screenshots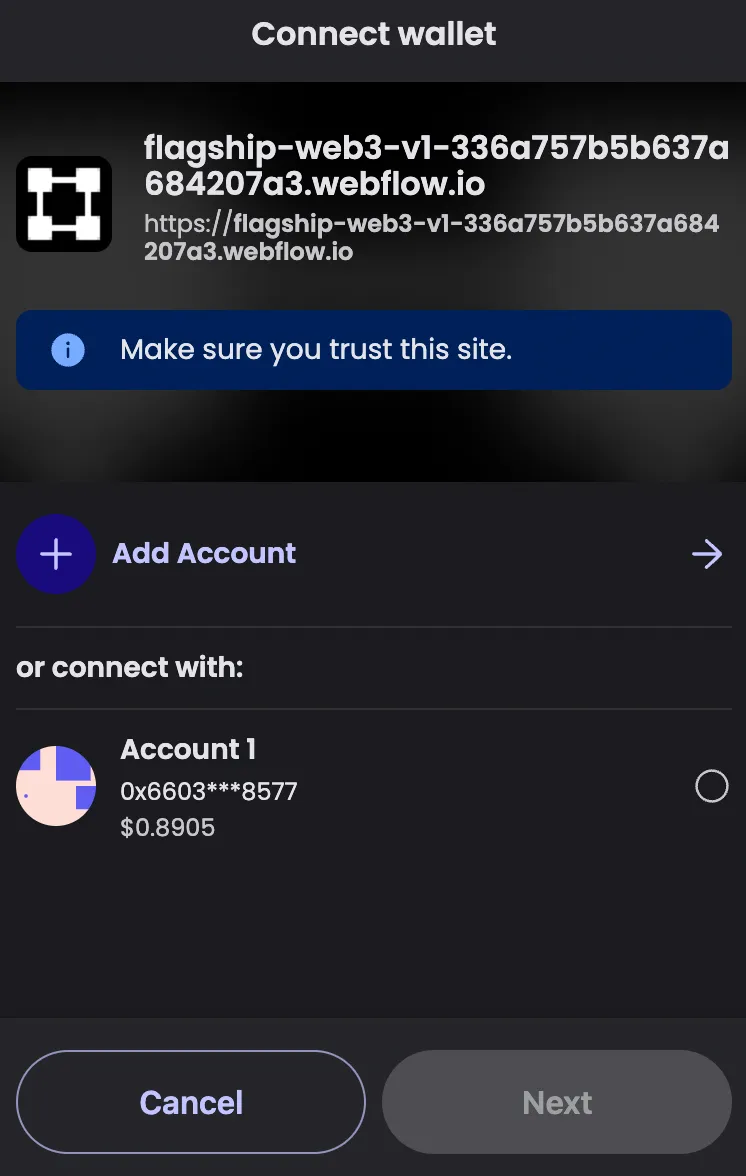
 Last updated on Sep 3, 2026Report an issue with this check
-
- Trusted dApp detection3.3 / 3.3Description
Informs users when interacting with a trusted dApp URL.
-
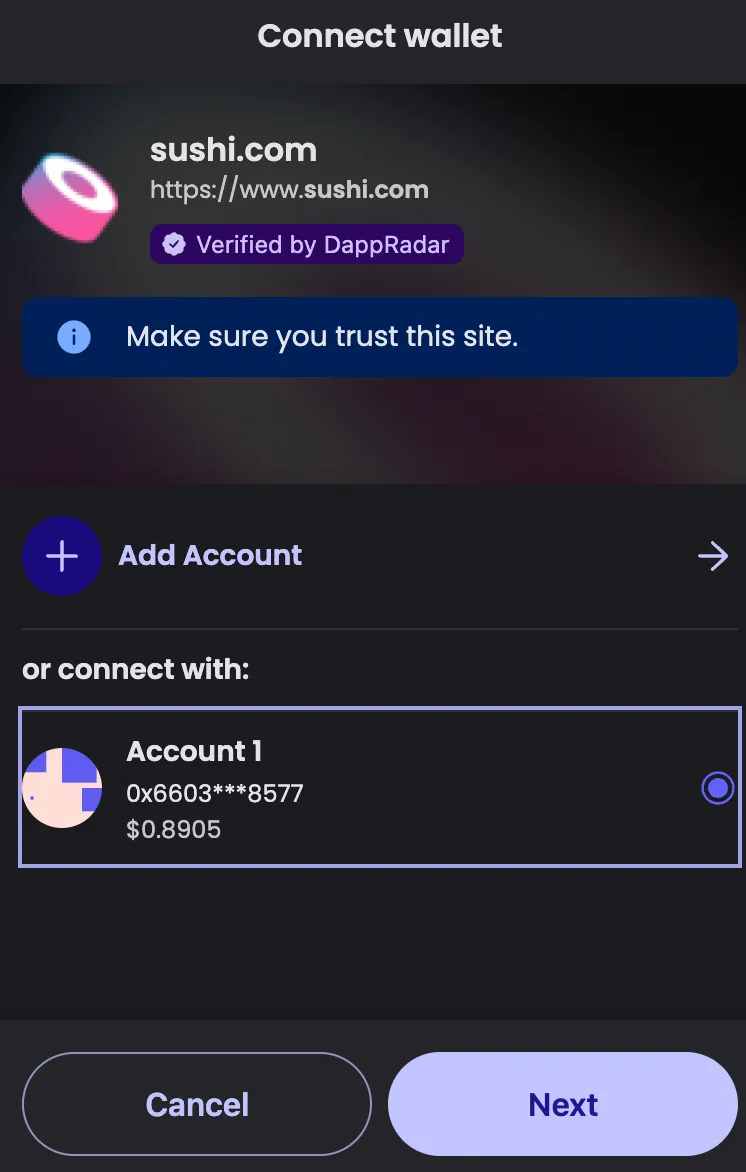
Verified dApps show the 'Verified by DappRadar' badge on the connection request screen, and unknown dApps don't show the badge.
— Verified by Sebastian Camia at Coinspect
Evidence · 4 screenshots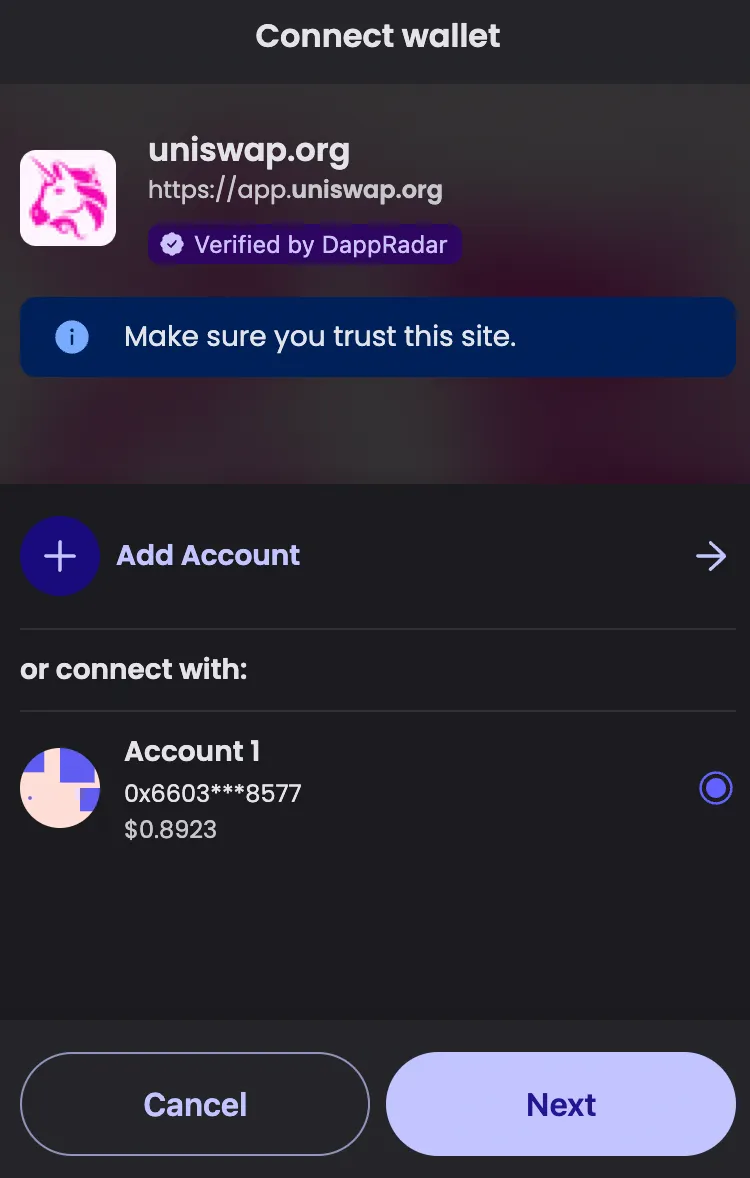
 Last updated on Sep 3, 2026Report an issue with this check
-
- Unknown address detection0.0 / 2.8Description
Warns users when interacting with an unknown address.
-
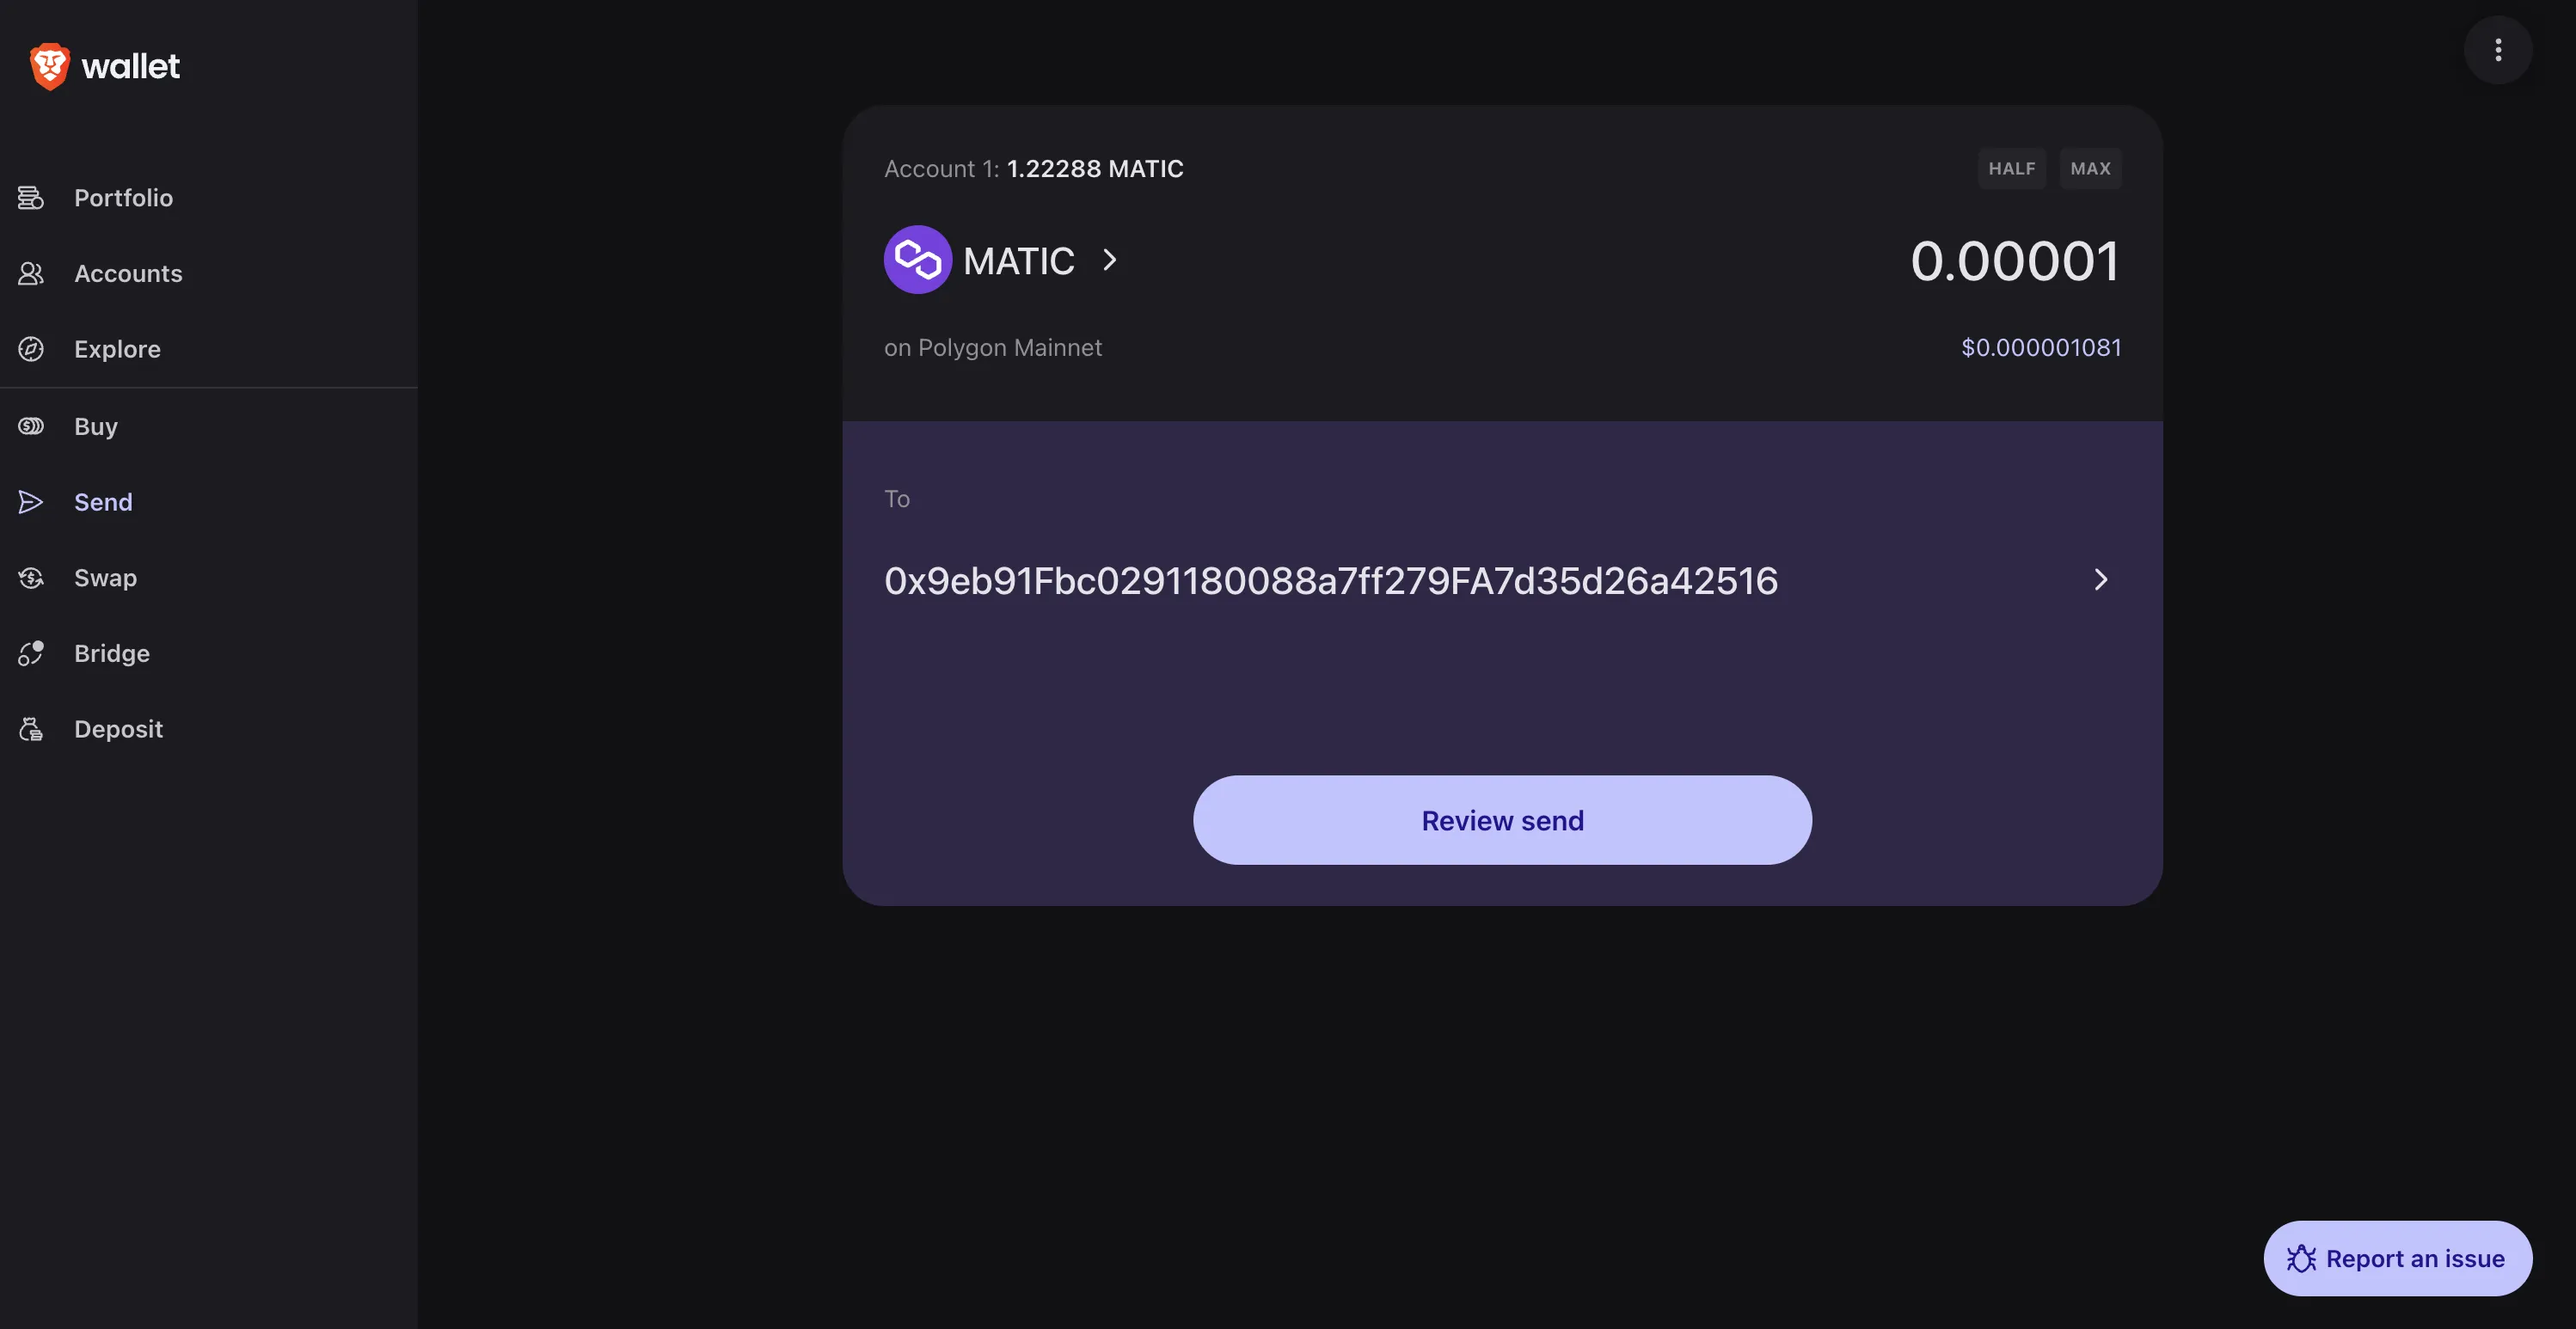
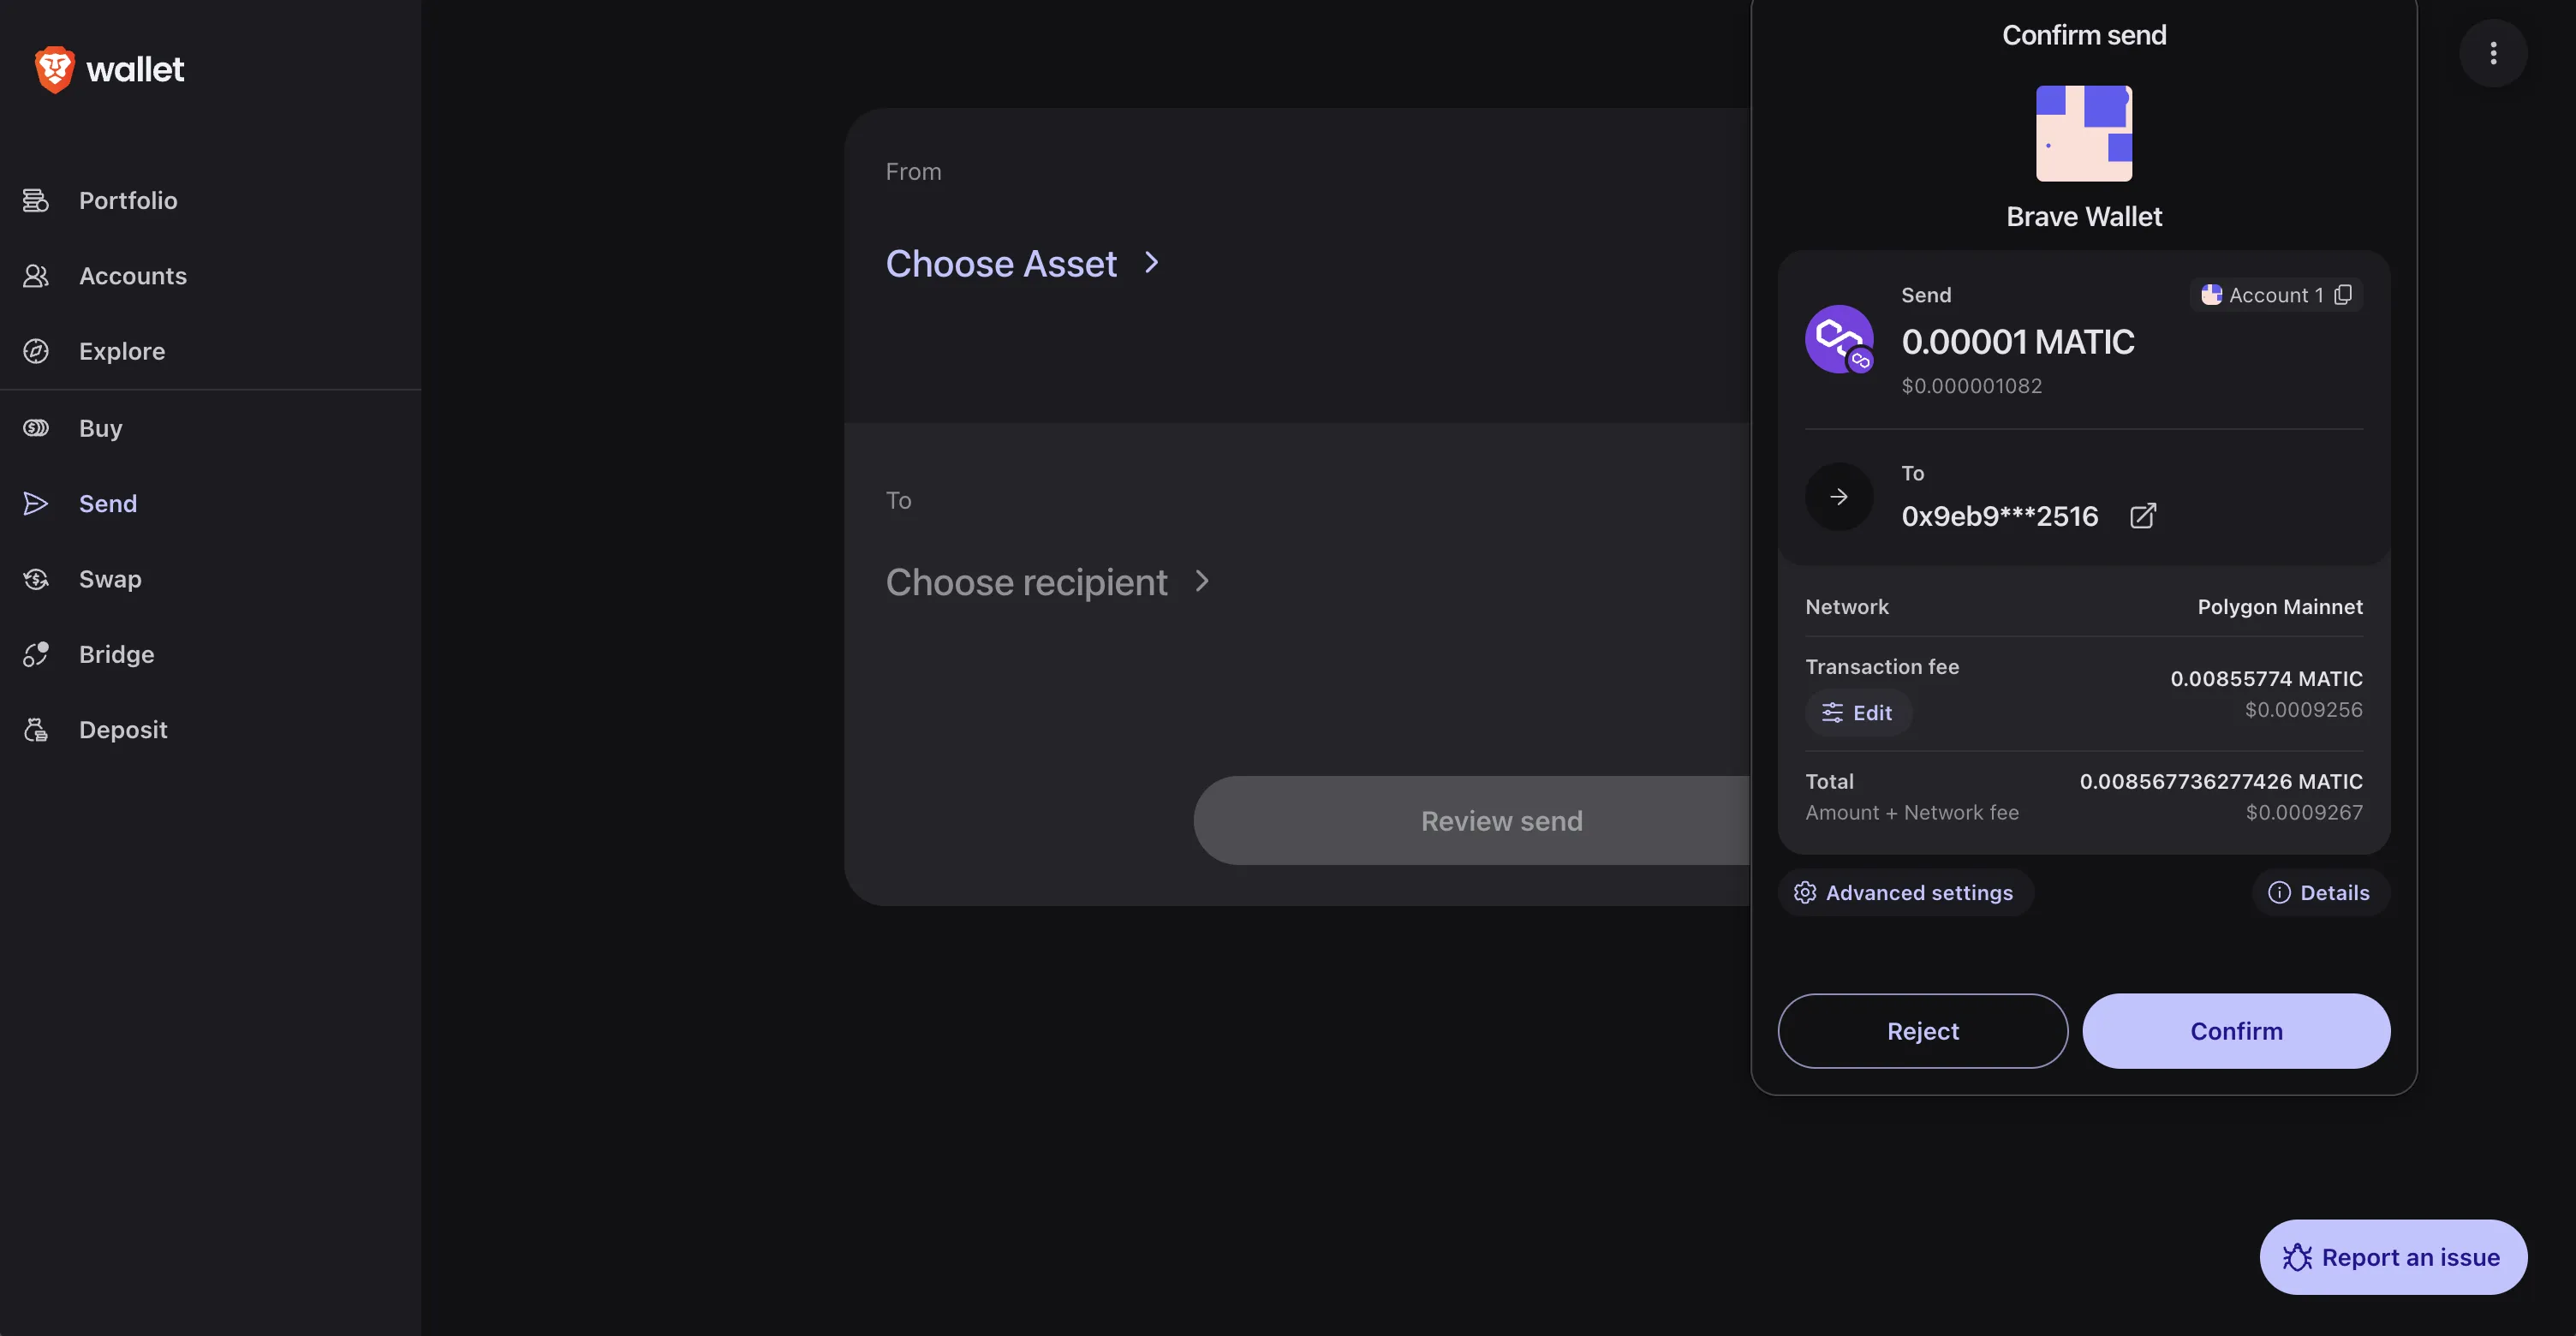
The wallet does not display any warning or indicator when sending to an unknown address, both when the address is provided by a dApp and when entered manually.
— Verified by Sebastian Camia at Coinspect
Evidence · 3 screenshots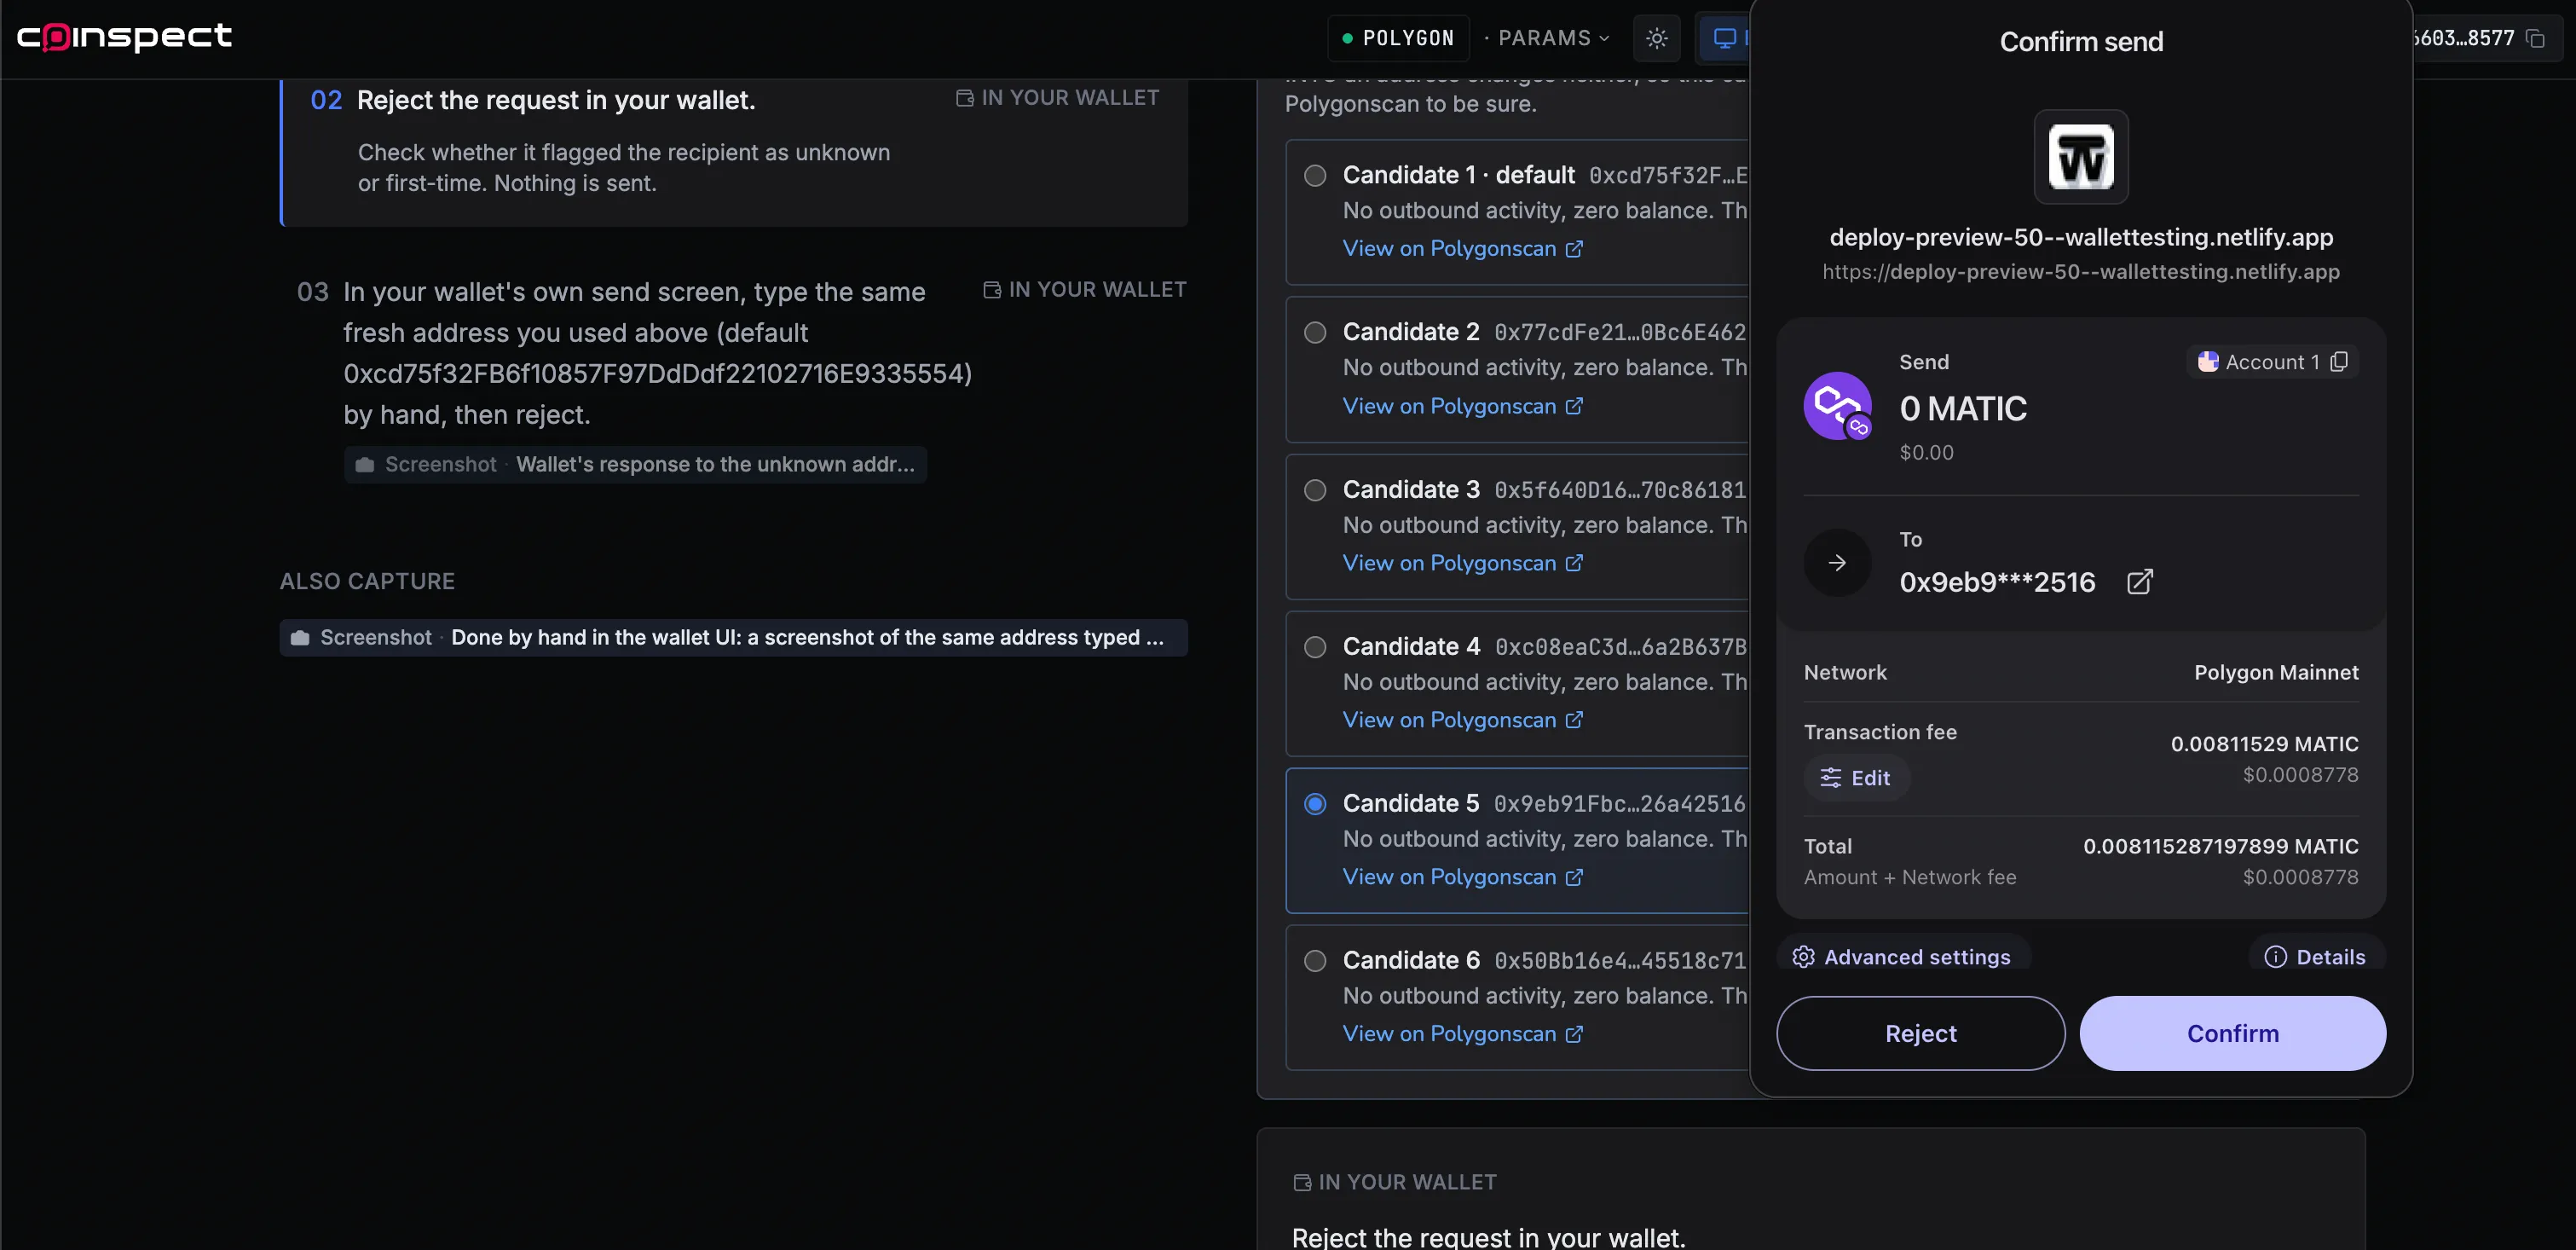
 Last updated on Sep 3, 2026Report an issue with this check
-
- Full dApp URL display1.5 / 1.5Description
Clearly displays the full dApp URL in the connection prompt.
-
The full dApp origin URL is shown without truncation.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot Last updated on Sep 3, 2026Report an issue with this check -
- Malicious or spam token filtering0.0 / 1.3Description
Hides malicious tokens and NFTs by default.
-
Spam tokens and NFTs are displayed by default in the portfolio view.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot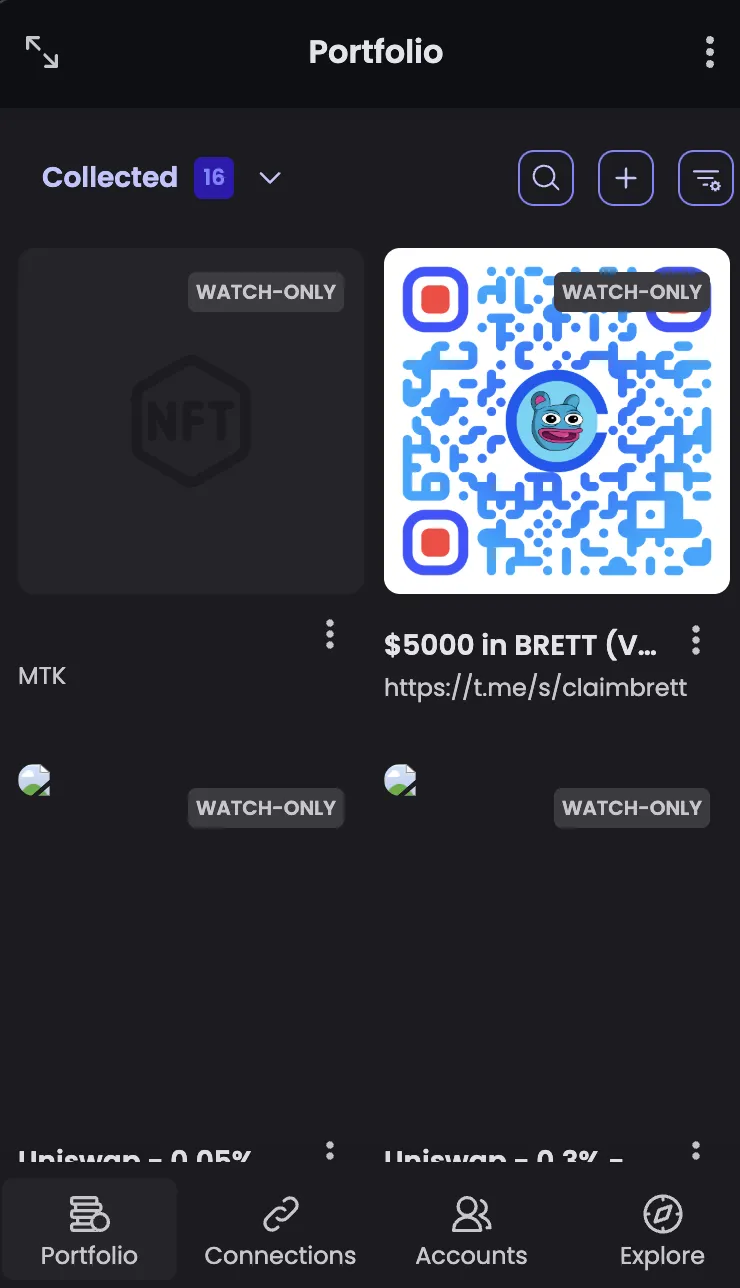 Last updated on Sep 3, 2026Report an issue with this check
-
- dApp access disclosure dialog1.0 / 1.0Description
Discloses the dApp's read access to the user's account and its ability to request signatures on connection.
-
The connection dialog clearly describes the permissions being granted, including the ability to check wallet balance and activity and request transaction approvals, satisfying the acceptance criteria.
— Verified by Sebastian Camia at Coinspect
Evidence · 1 screenshot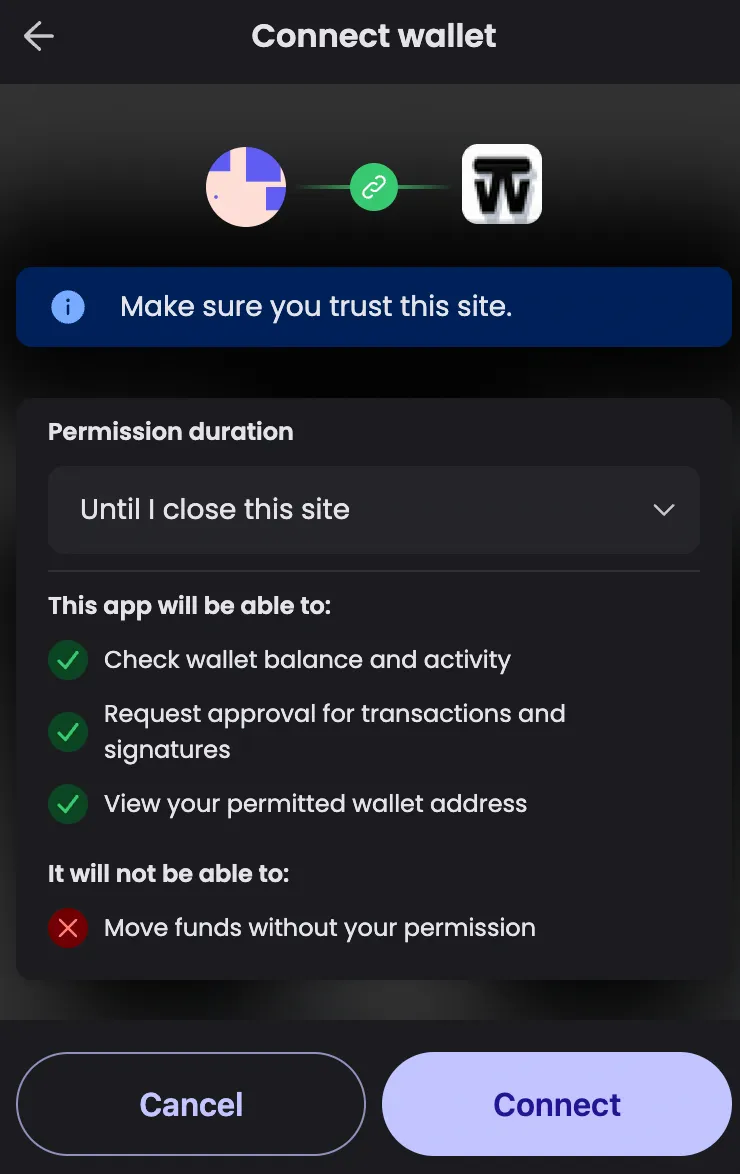 Last updated on Sep 3, 2026Report an issue with this check
-
This ranking is for informational purposes only. It should not be relied on to provide legal, tax, financial, investment, or other types of advice. Coinspect does not guarantee or warrant the accuracy, completeness, timeliness, suitability, or validity of the information provided and will not be responsible for any claim attributable to reliance on errors, omissions, or other inaccuracies of any part of such information.